
Archived
purpleteam-s2-containers
 purpleteam-labs/purpleteam-s2-containers
Stage two containers
cloud-securitycontainer-securitydevsecops+5
purpleteam-labs/purpleteam-s2-containersStage two containers
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
 purpleteam-labs/purpleteam
CLI component of purpleteam
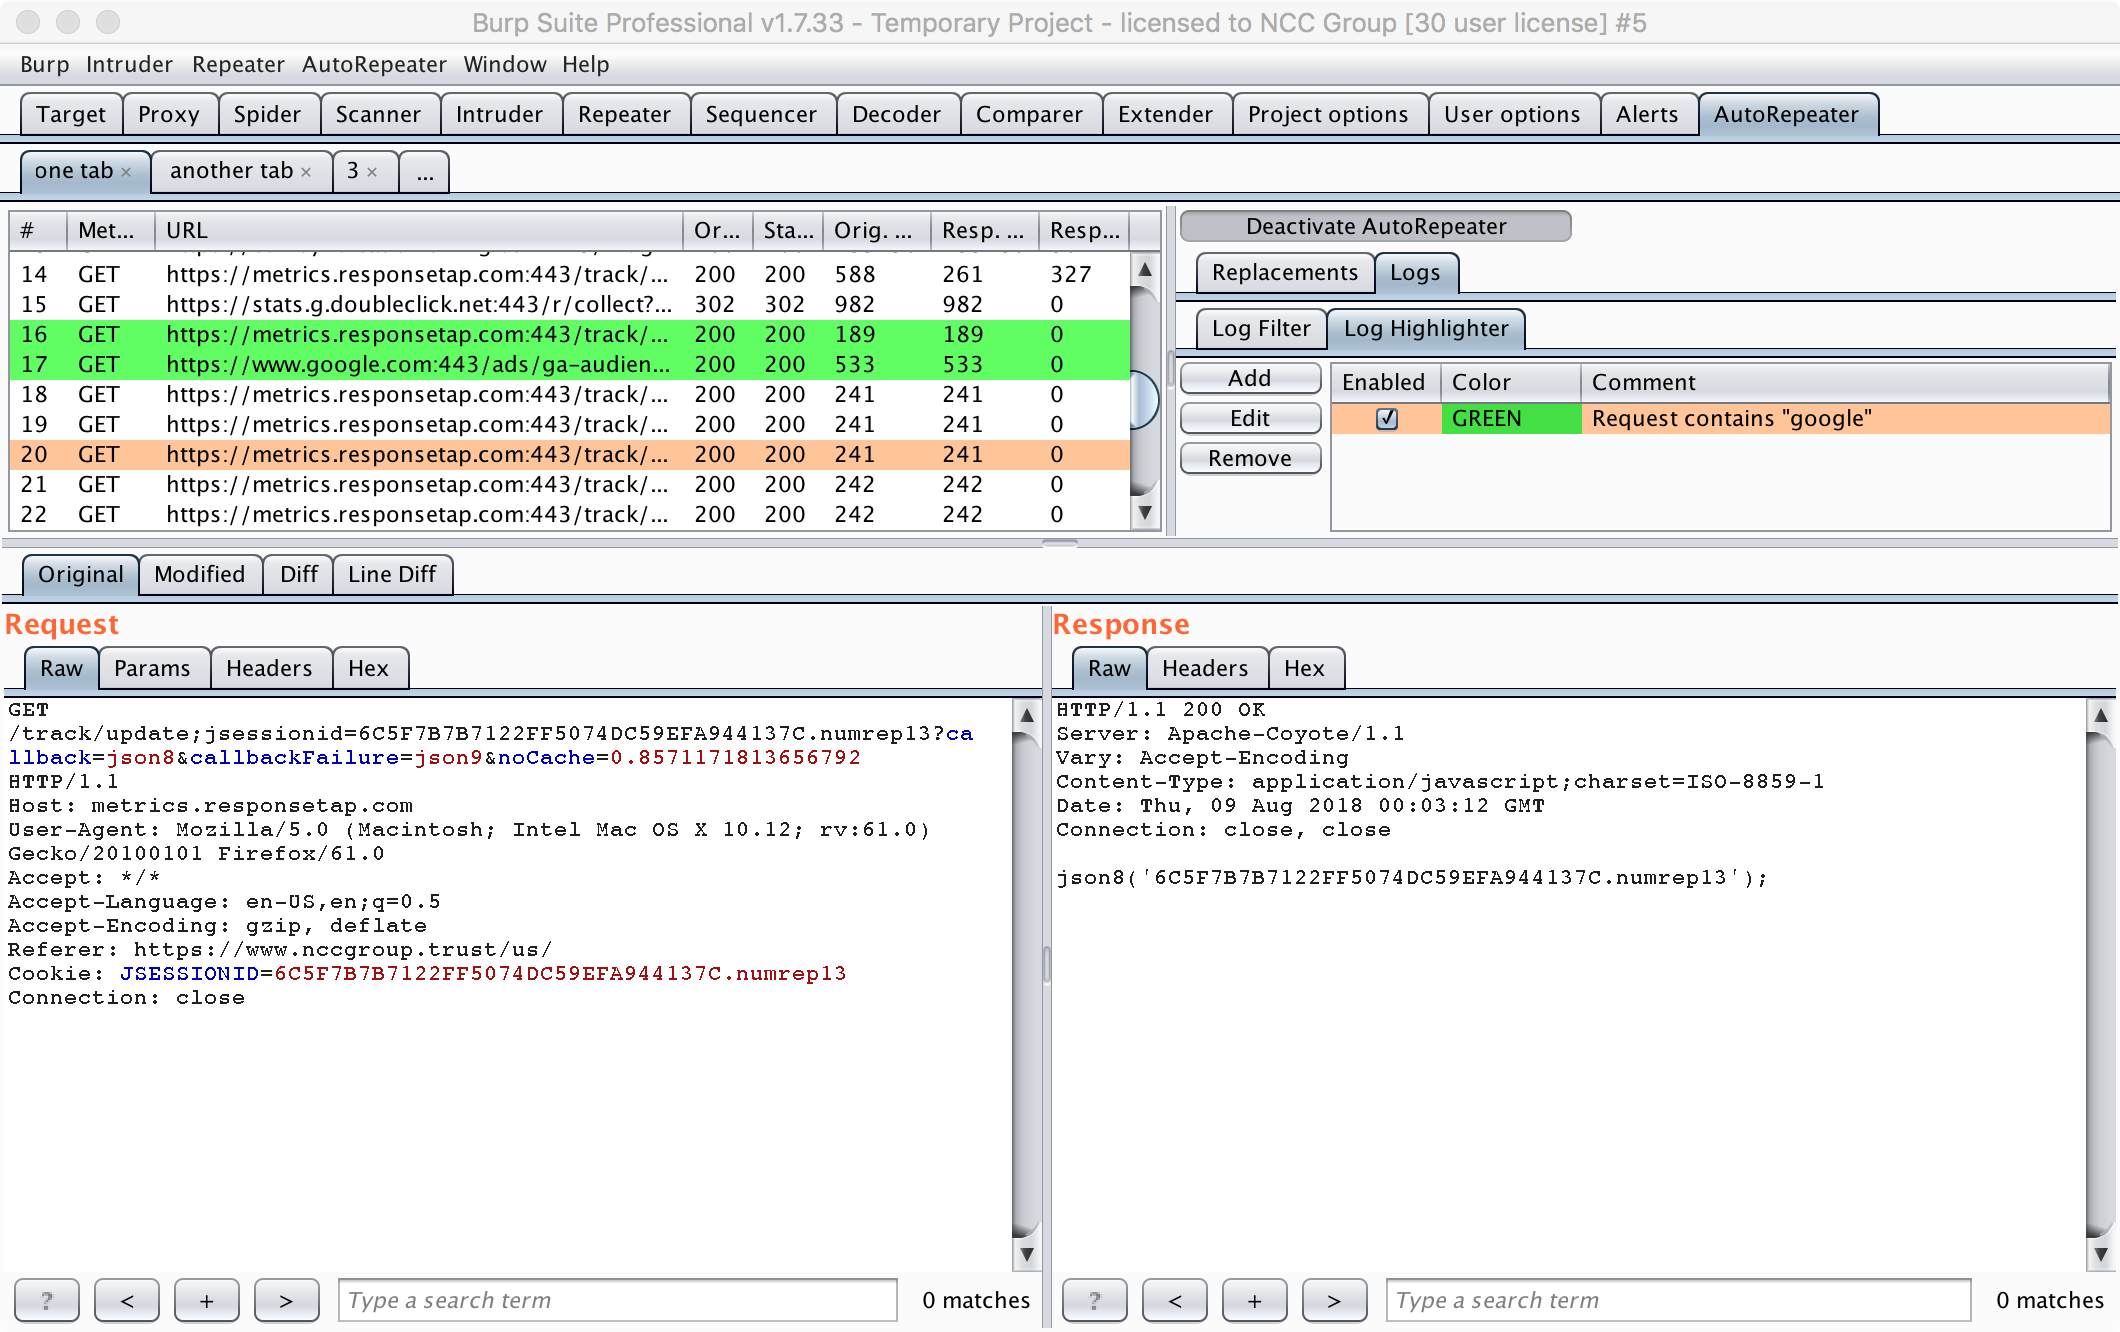
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
 murataydemir/cve-2016-4014
[CVE-2016-4014] SAP Netweaver AS JAVA UDDI Component XML External Entity (XXE)
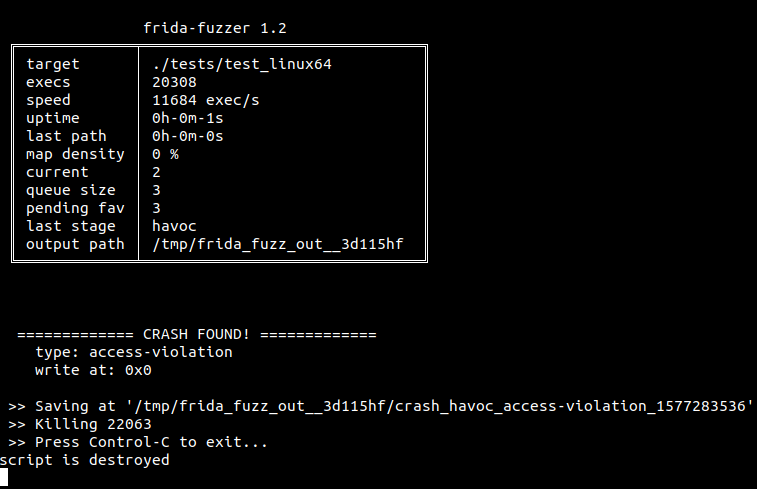 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
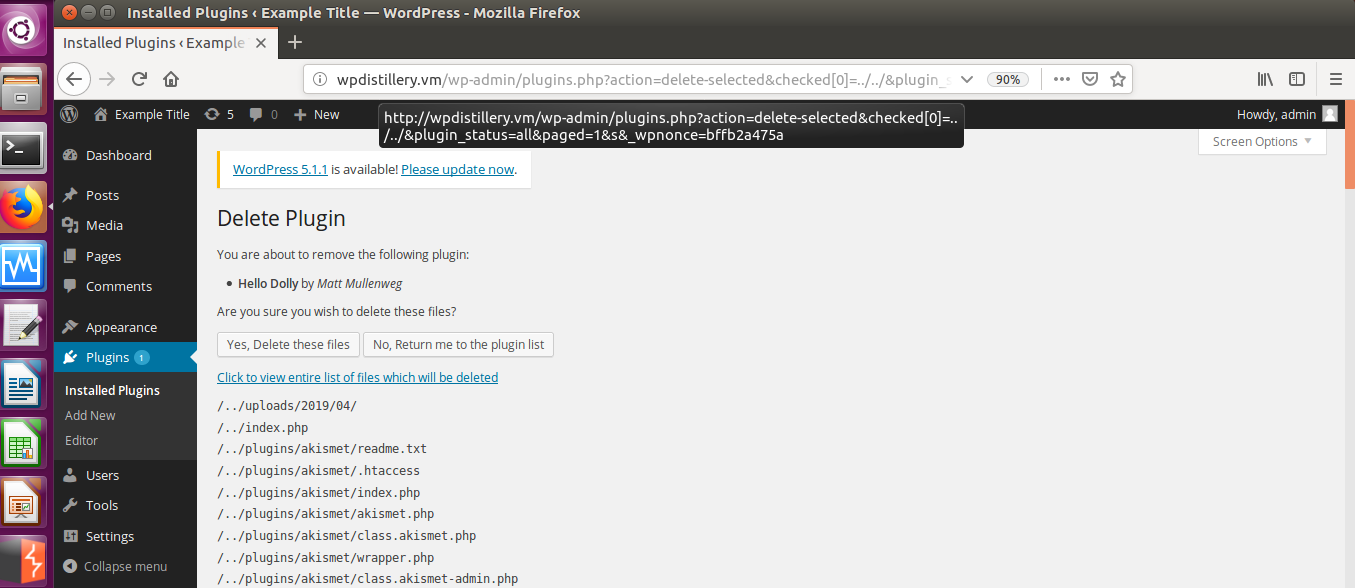 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API
 infobyte/alexafaraday
Alexa skill example for Faraday API
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 joanbono/gurp
Burp Commander written in Go
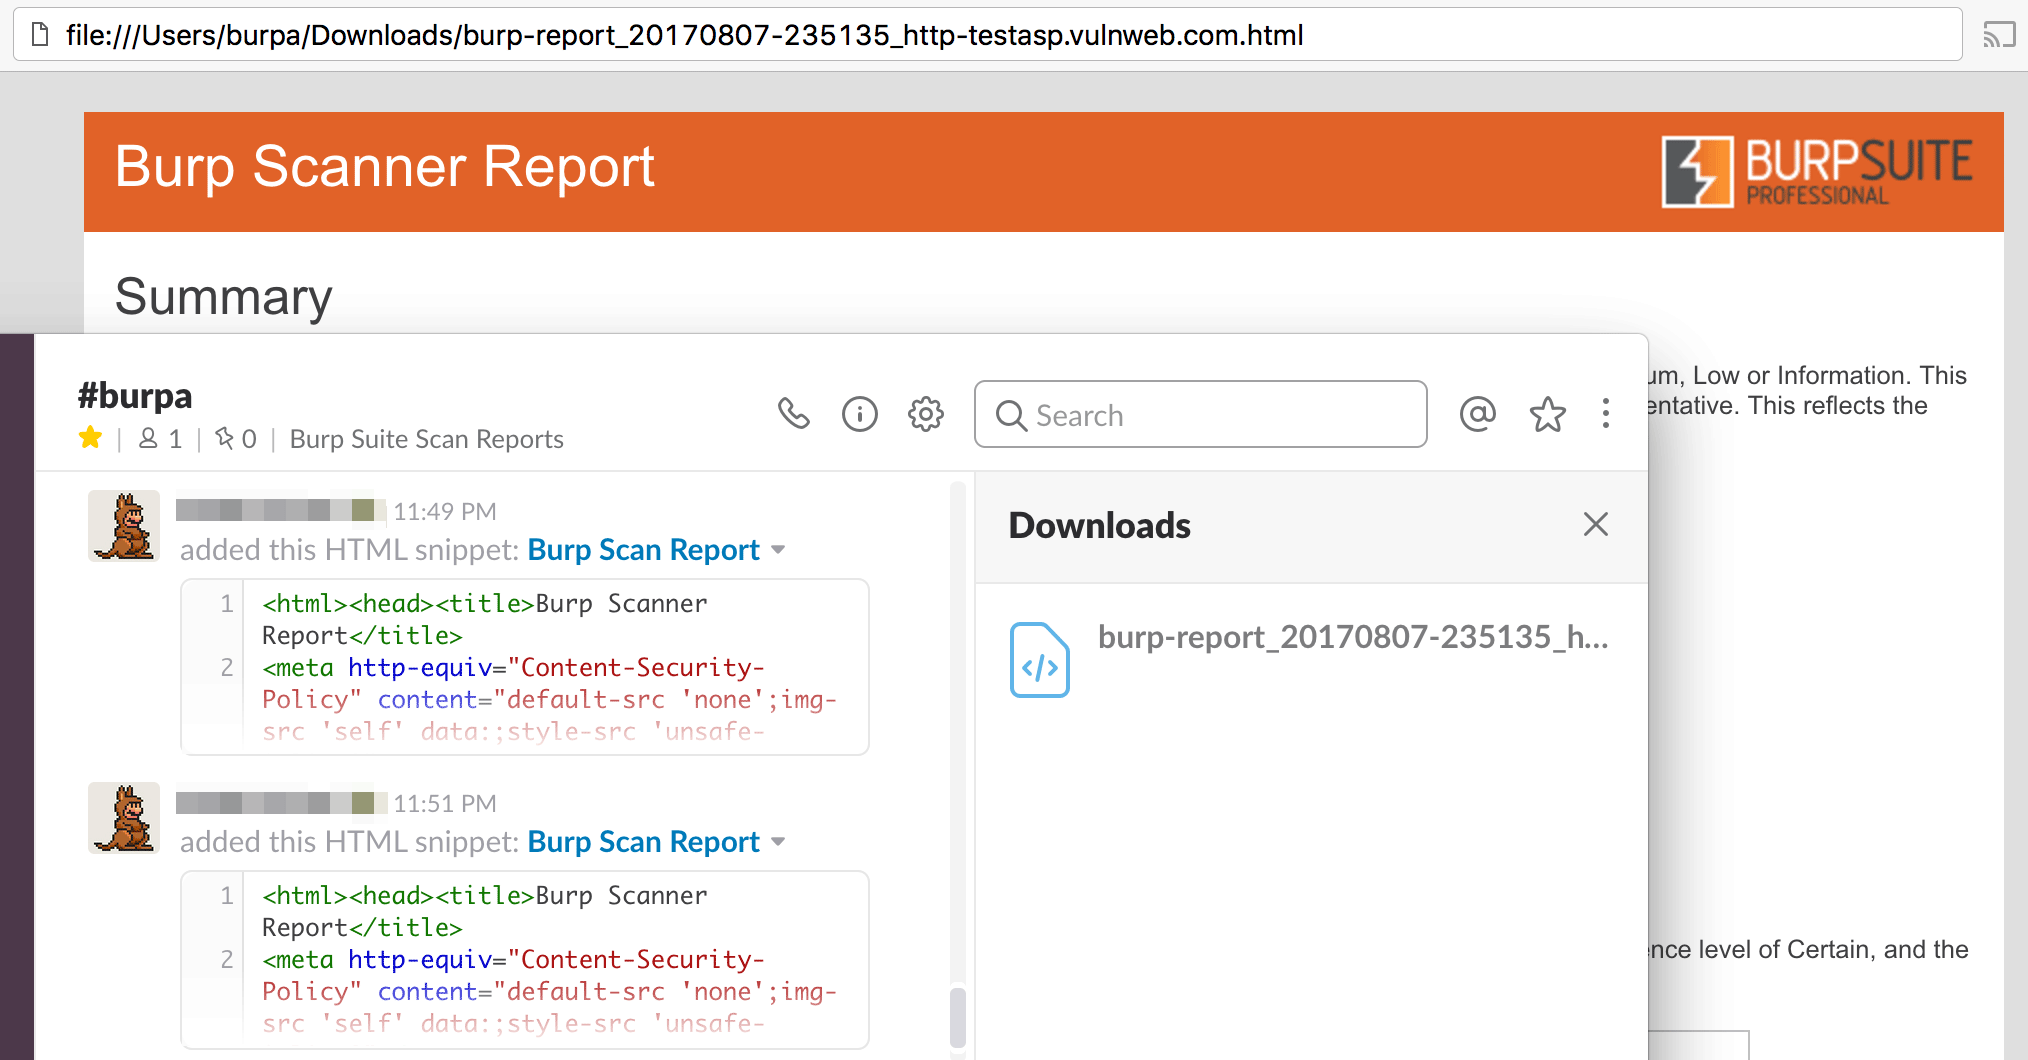 0x4d31/burpa
Burp-Automator: A Burp Suite Automation Tool with Slack Integration. It can be used with Jenkins and Selenium to automate Dynamic Application…
 deepseasred/autonessus
This script communicates with the Nessus API in an attempt to help with automating scans. Depending on the flag issued with the script, you can list…

 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library