CVE-2026-75429_PowerJob_friend_process_RCE

Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…

Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…

This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.

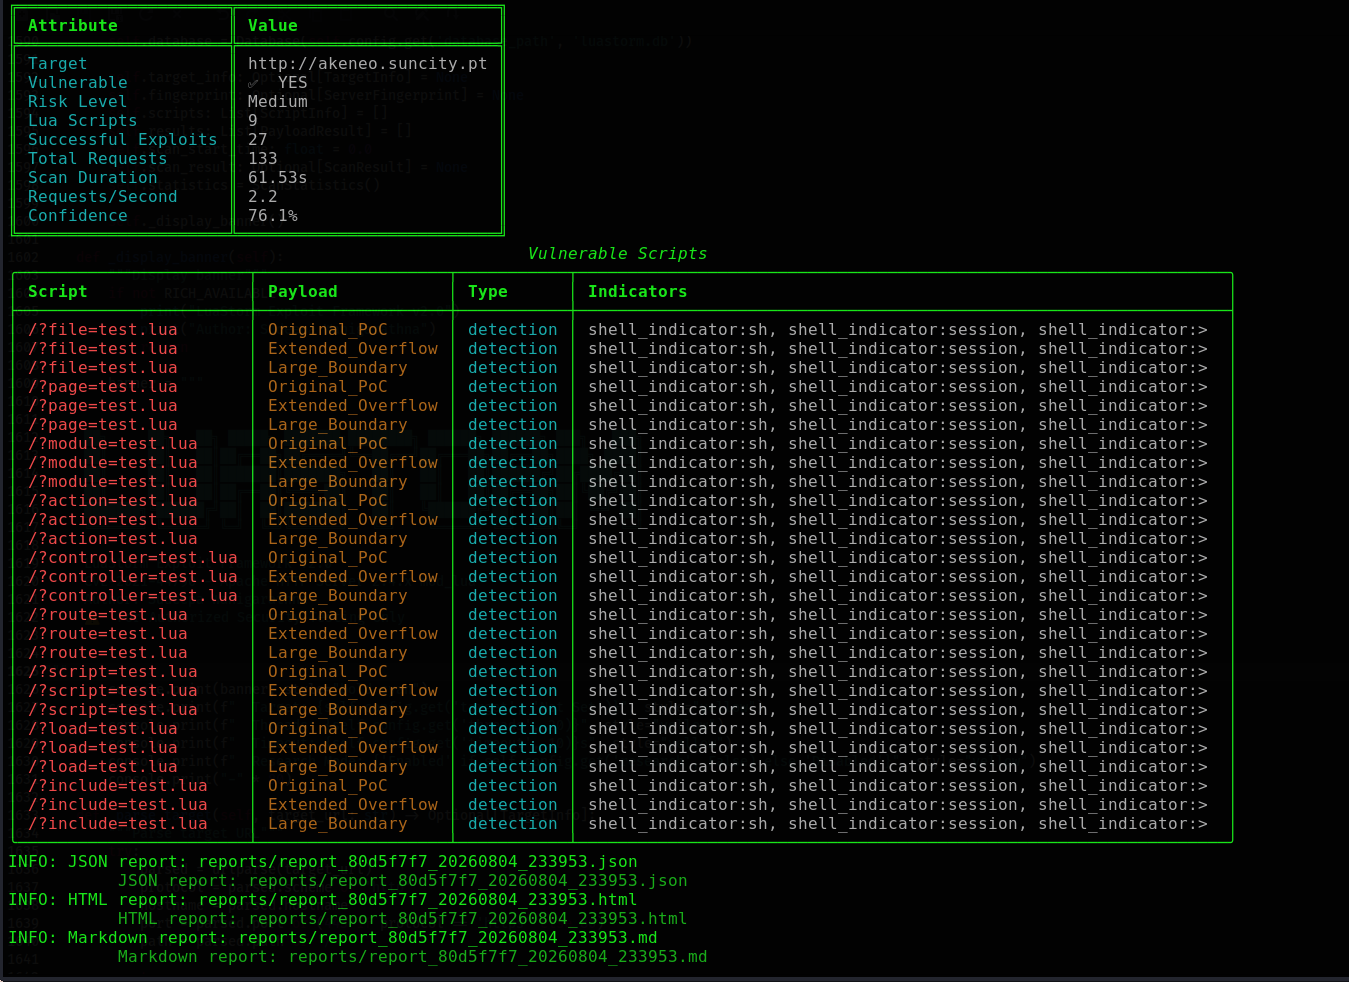
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…

CVE-2026-32941 PoC - Sliver Remote OOM

Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…

Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…

Vulnerability Research

Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…

CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)

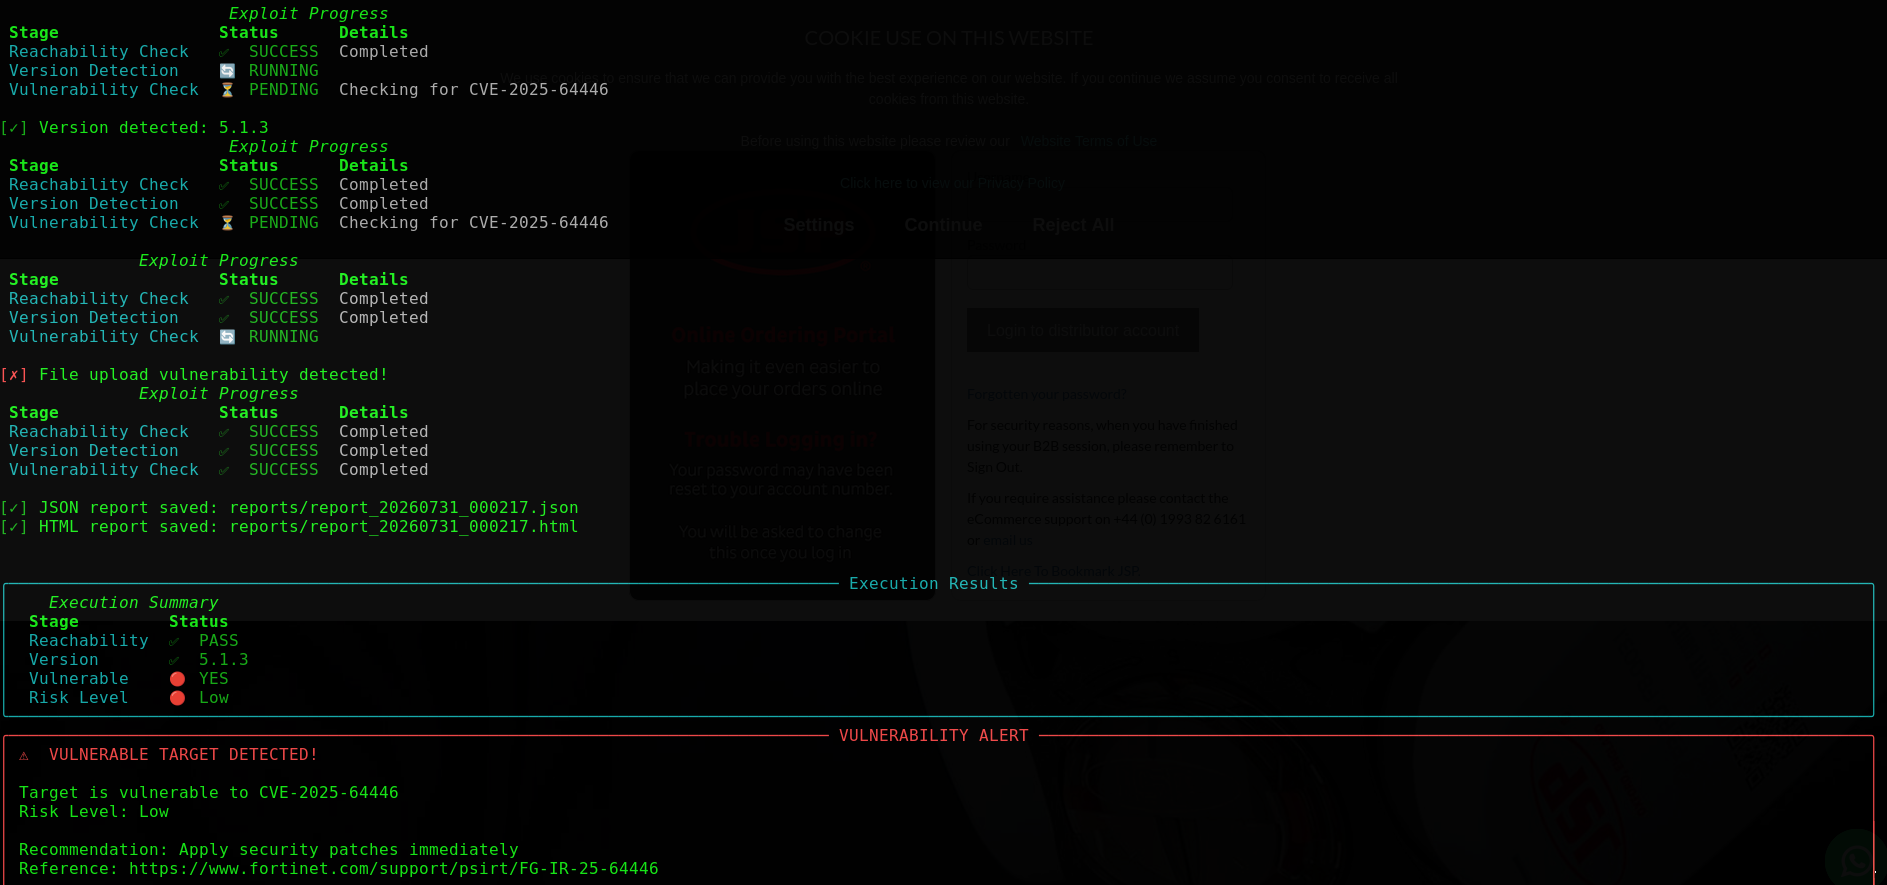
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…

JavaScript for Automation (JXA) macOS agent

CVE-2026-8206: Kirki Customizer Framework - Unauthenticated Account Takeover (CVSS 9.8)

AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…

Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.