
ad_attack_architecture
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
curated-resourceseducationidentity-management+7
36
kypvas/ad_attack_architectureActive Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
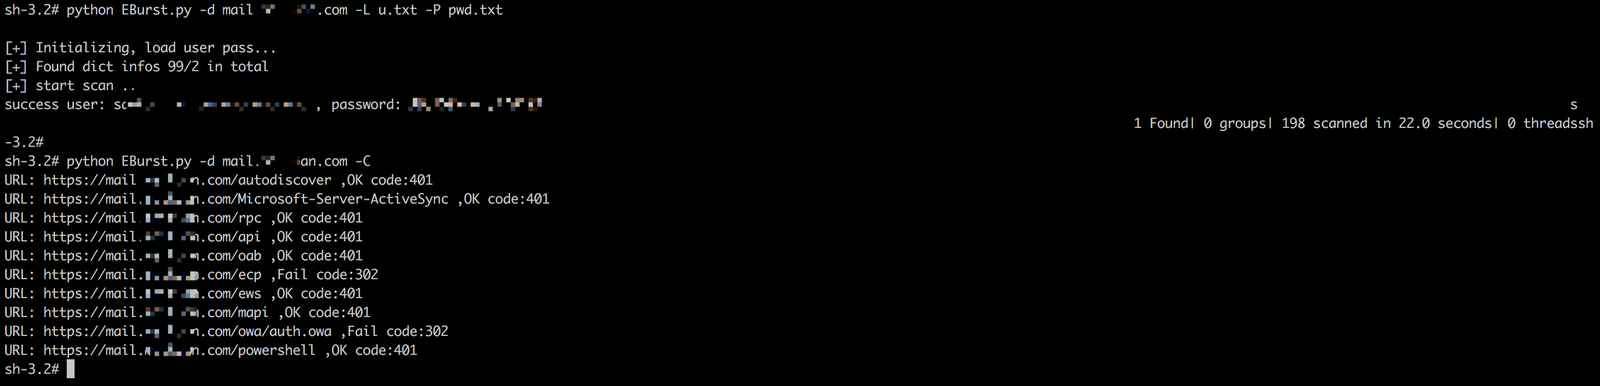 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
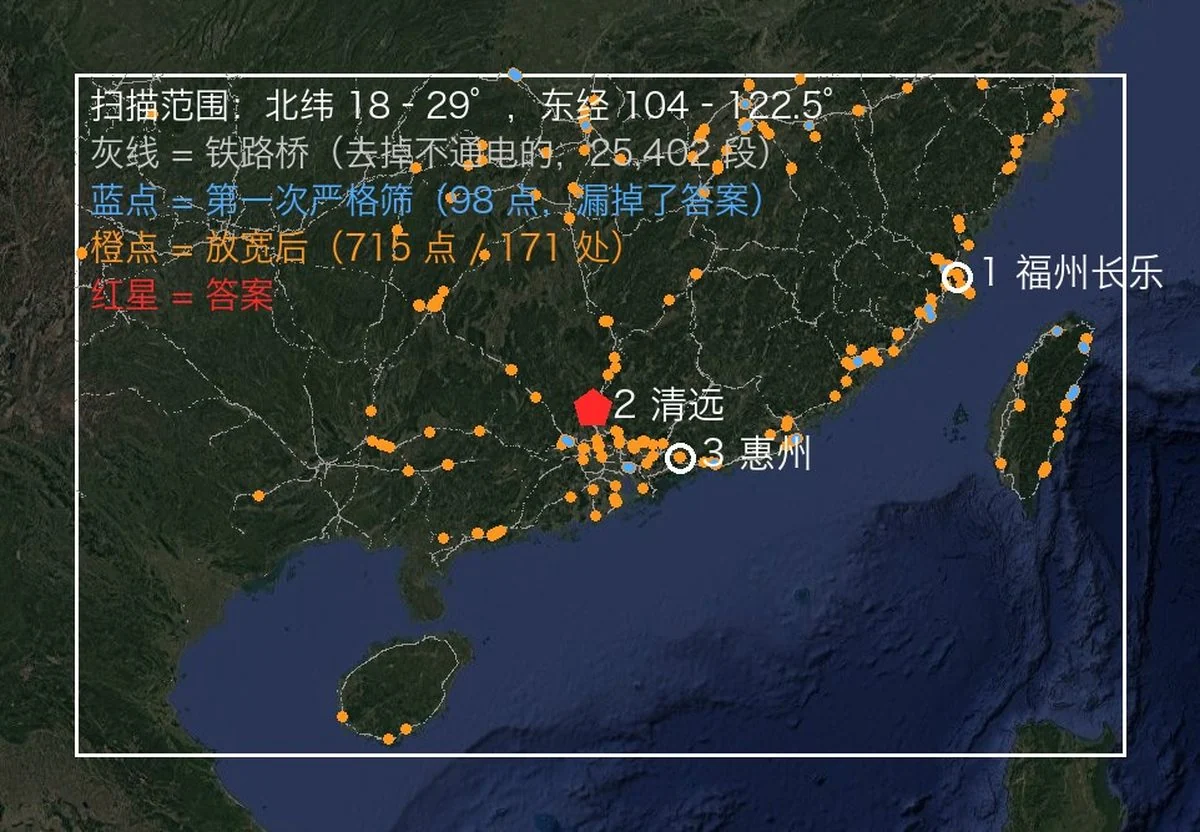 oldcircle/geo-sleuth
An agent skill that finds where a photo was taken — OpenStreetMap geometry, elevation skylines, satellite imagery and street view — and shows its…
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
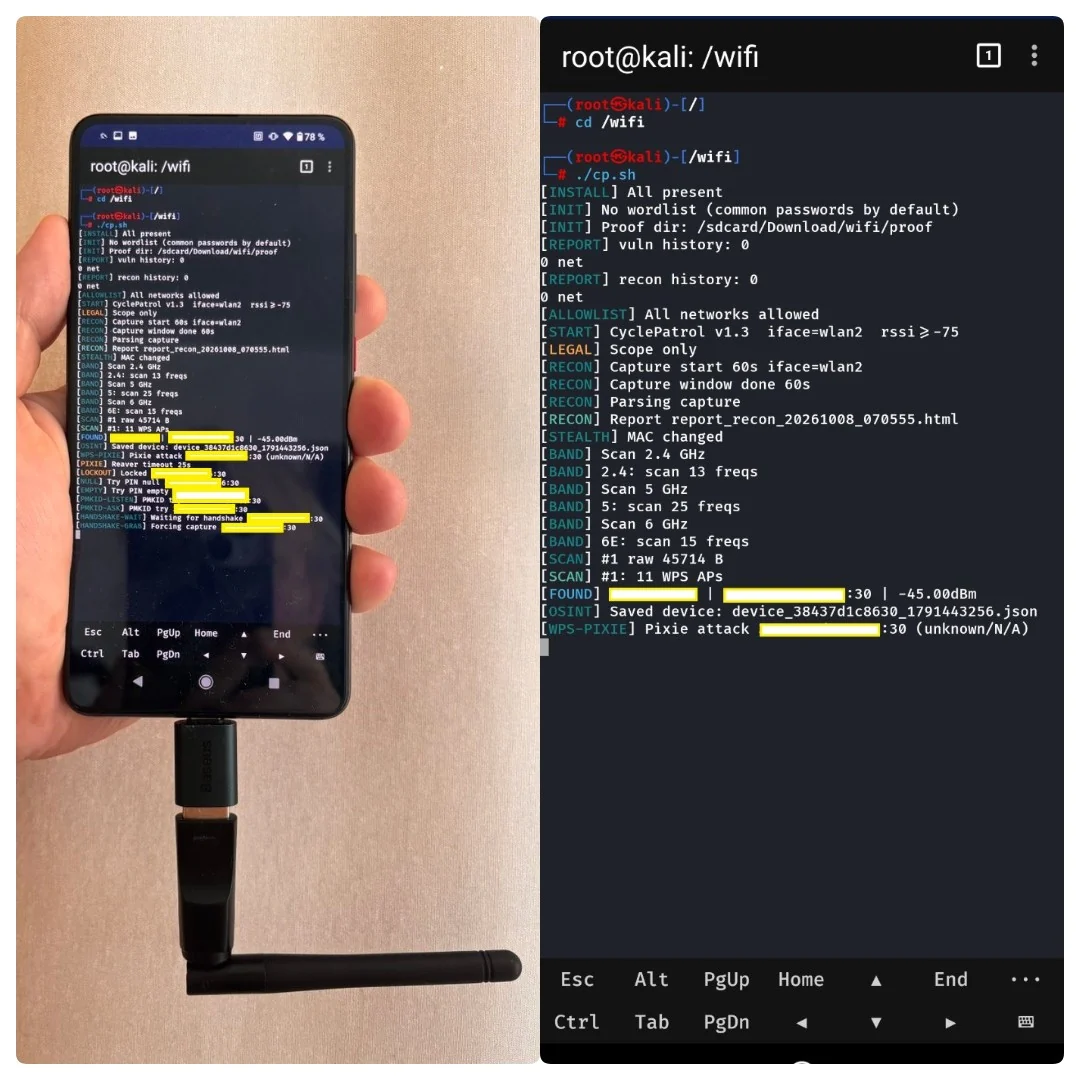 buybitart/cyclepatrol
Bash tool for on-foot Wi-Fi security checks in a loop, with evidence reports.
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 vulncheck-oss/cli
VulnCheck's official command line tool
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 cyber-courses/cyber-library
Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence,…
 vulncheck-oss/go-exploit-cache
A utility for producing an HTTP cache database to use with go-exploit
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.