
realm
 spellshift/realm
Cross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
command-and-controlexploit-frameworkslateral-movement+9
641
spellshift/realmCross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 guila95/cve-2026-86426
Proof-of-concept and recon framework for CVE-2026-86426, a LibreNMS API authentication bypass via type confusion, extracting SNMP credentials and…
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
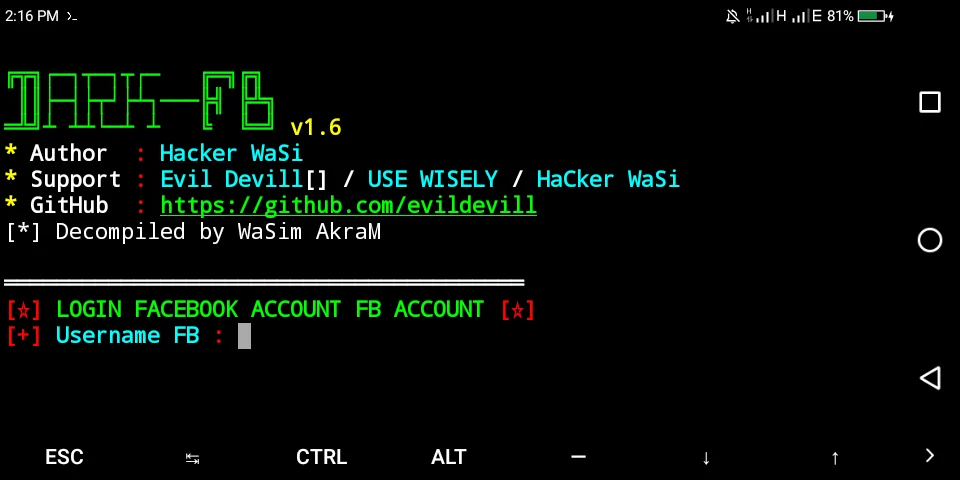 evildevill/devil
Menu-driven shell framework bundling brute-force login attacks, friendlist and profile data harvesting, and automated Facebook account-grabbing…
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 mrphrazer/msynth
Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads