
SharpRelay
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
lateral-movementpacket-sniffing-analysispenetration-testing+1
180
pkb1s/sharprelayC# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 bee-san/pywhat
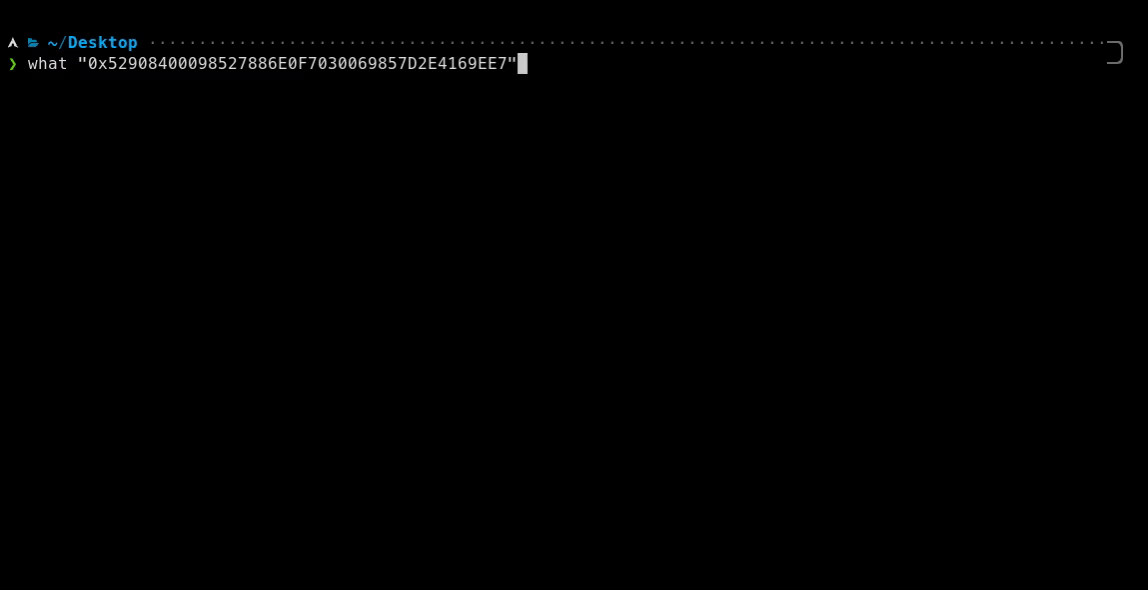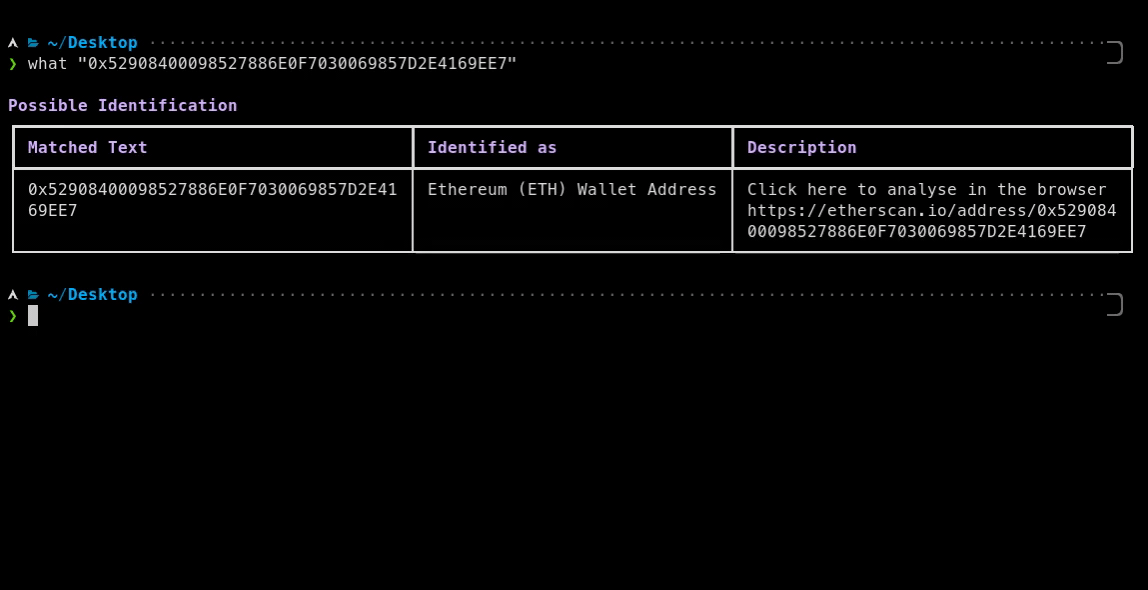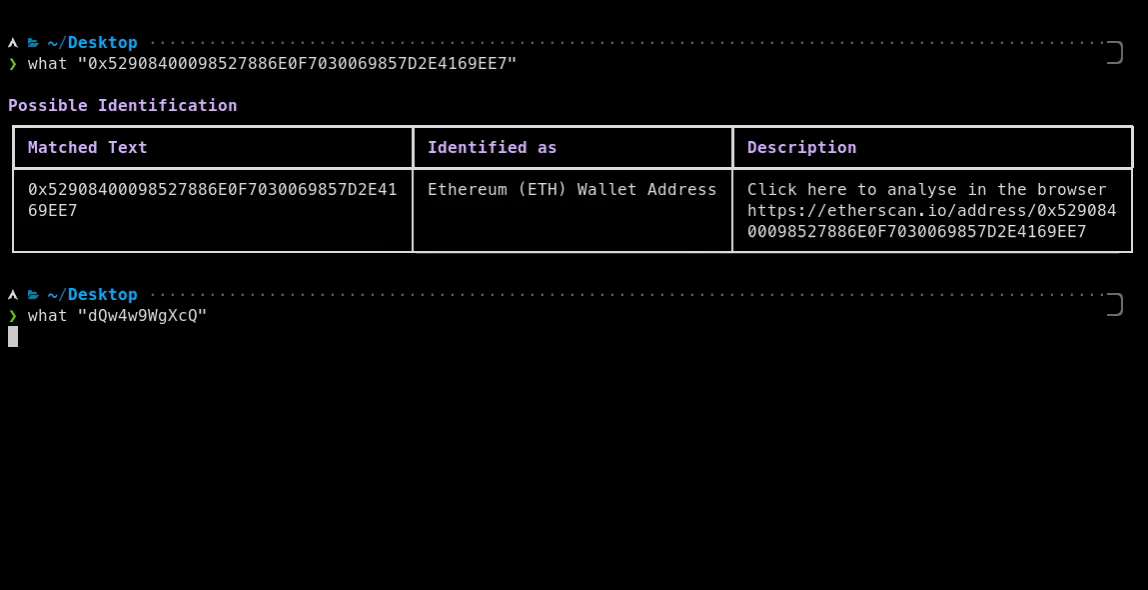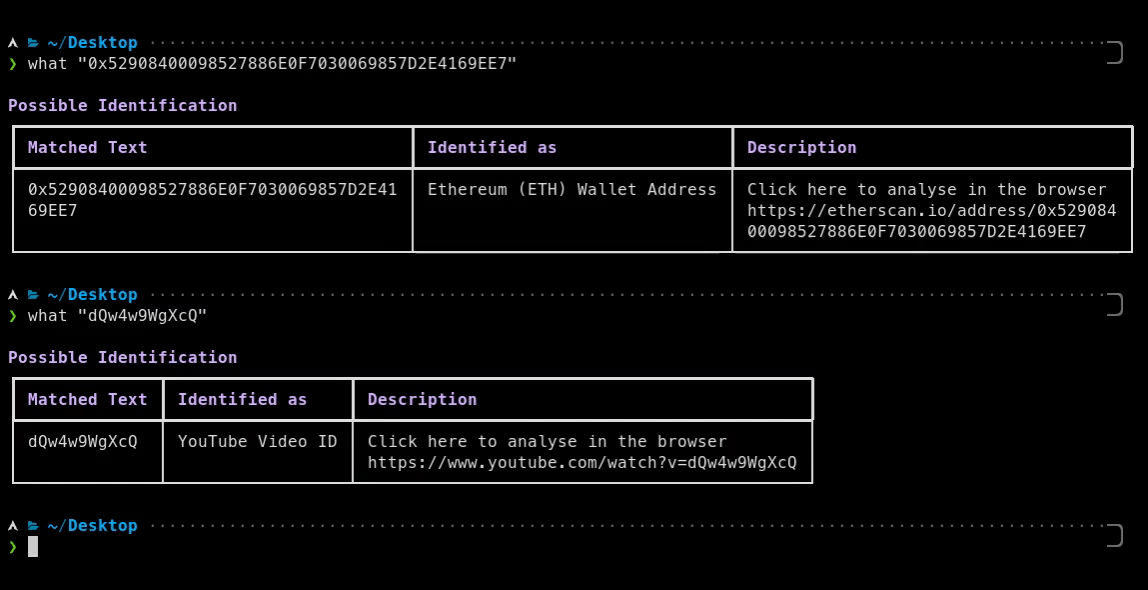
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
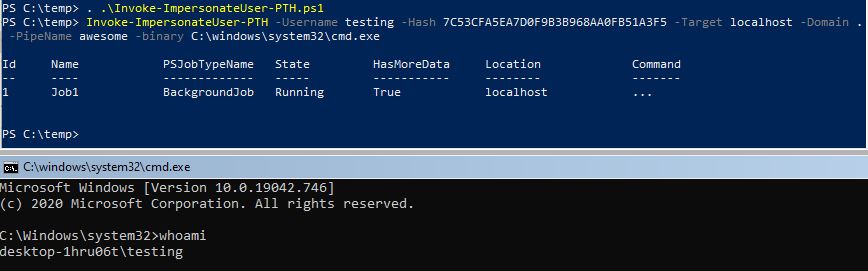 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
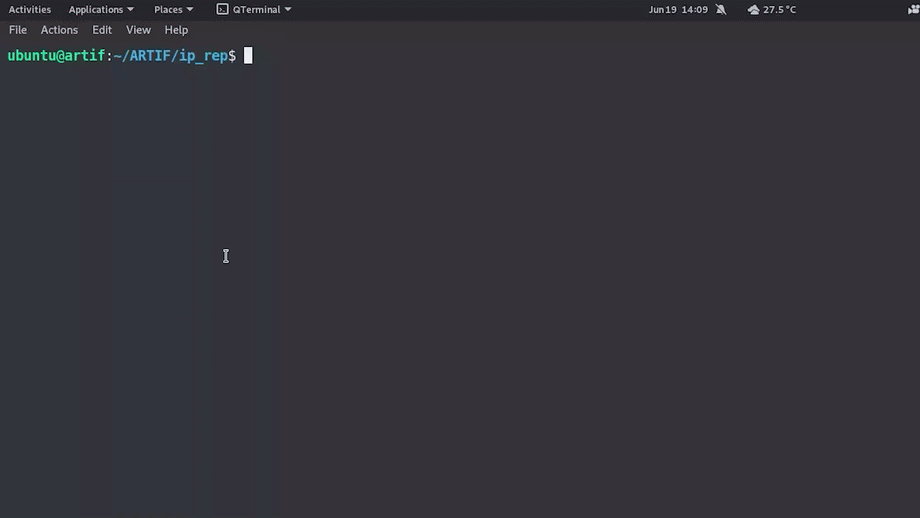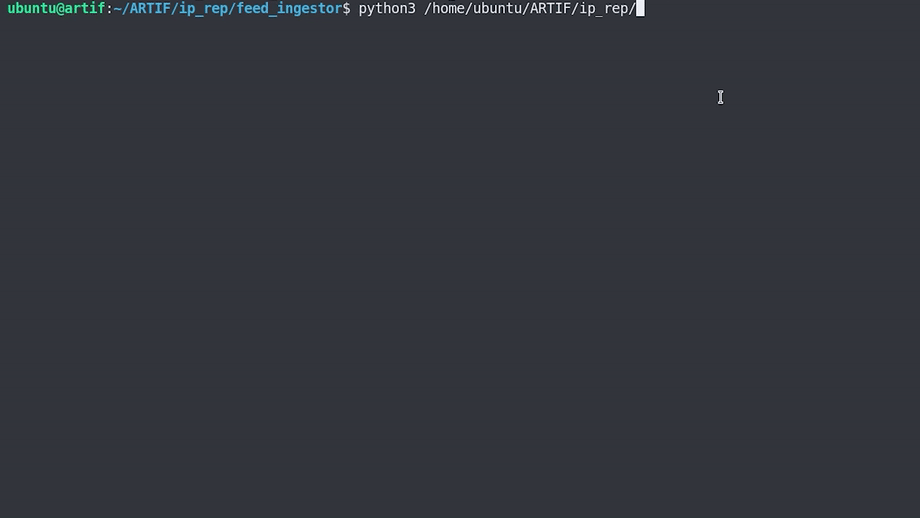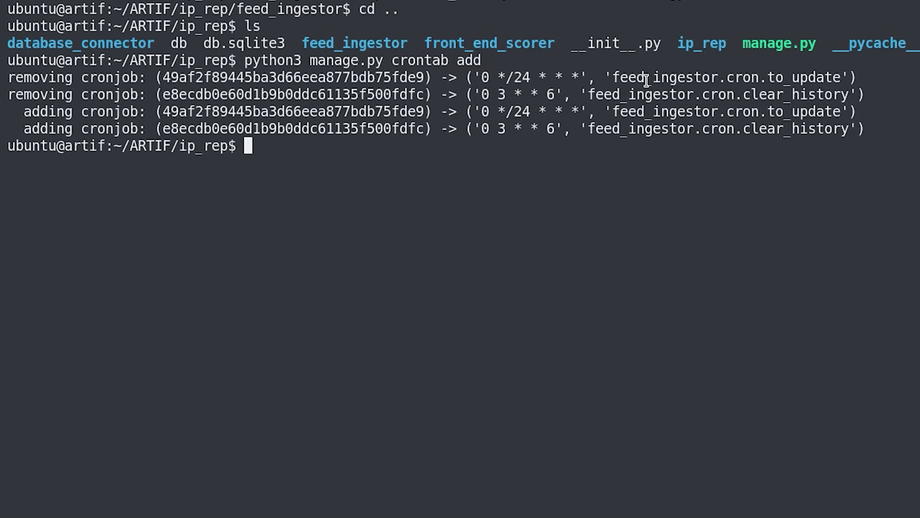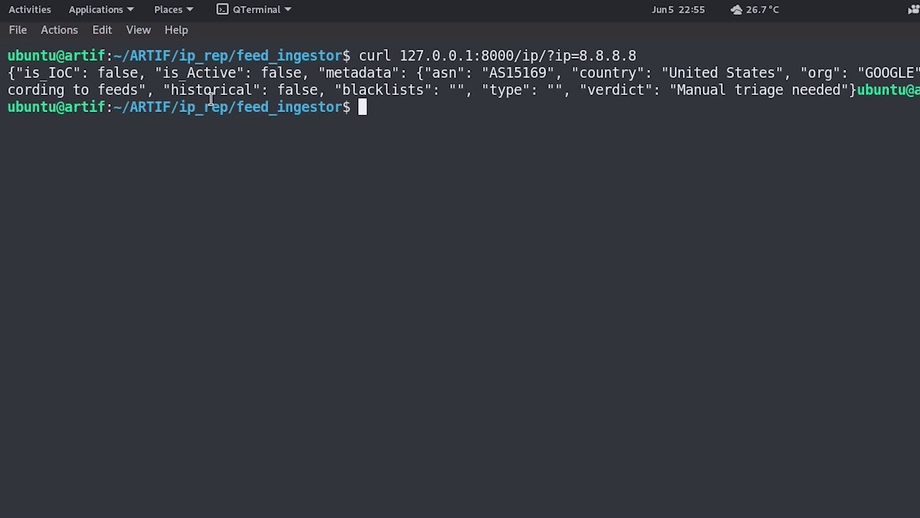 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 libnet/nemesis
A command-line network packet crafting and injection utility
 nccgroup/keimpx
Check for valid credentials across a network over SMB
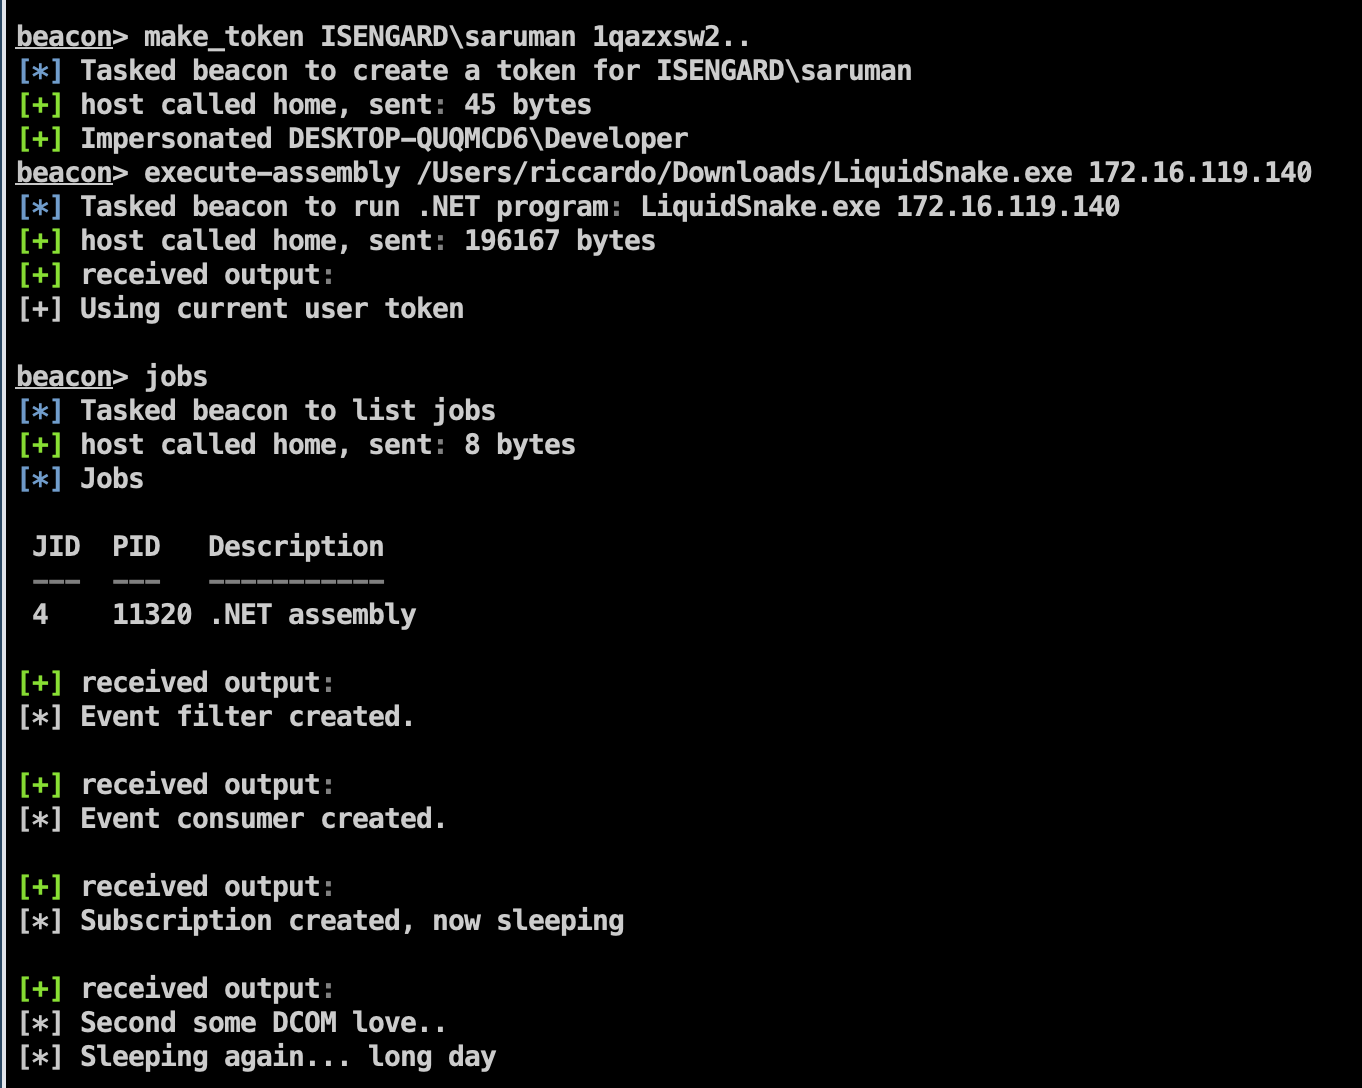 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 matamorphosis/scrummage
A Holistic OSINT and Threat Hunting Platform
 awesom3alex/osint-menace
Passive OSINT triage console for email, username, domain, IP, and crypto wallet reconnaissance. Features case management, curated resource links, and…
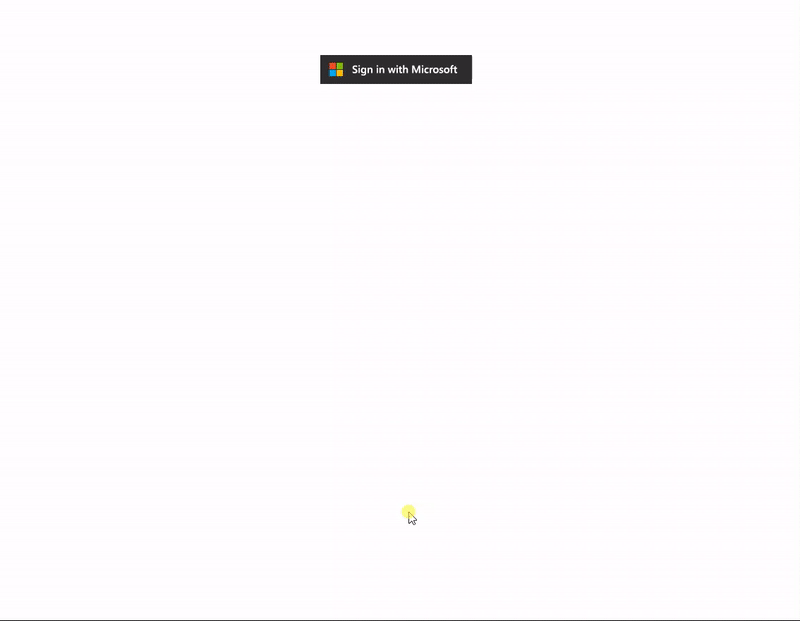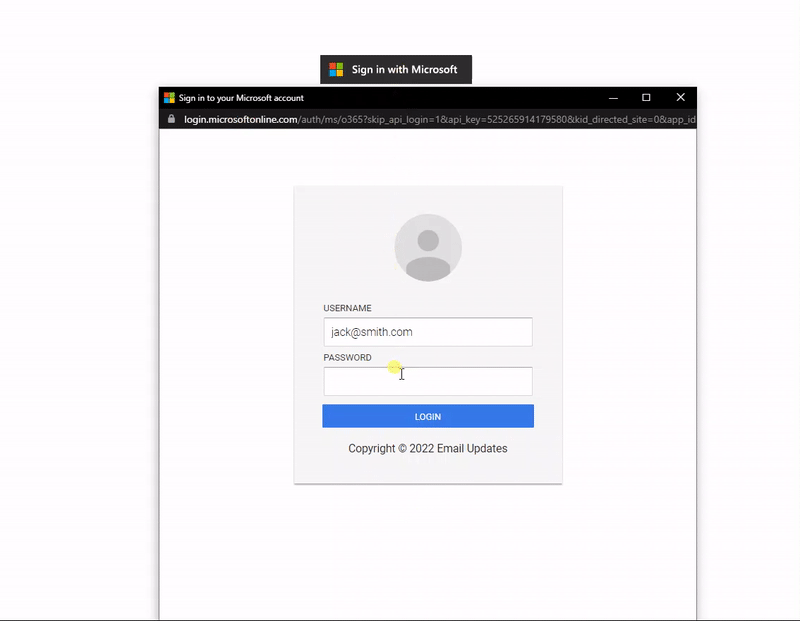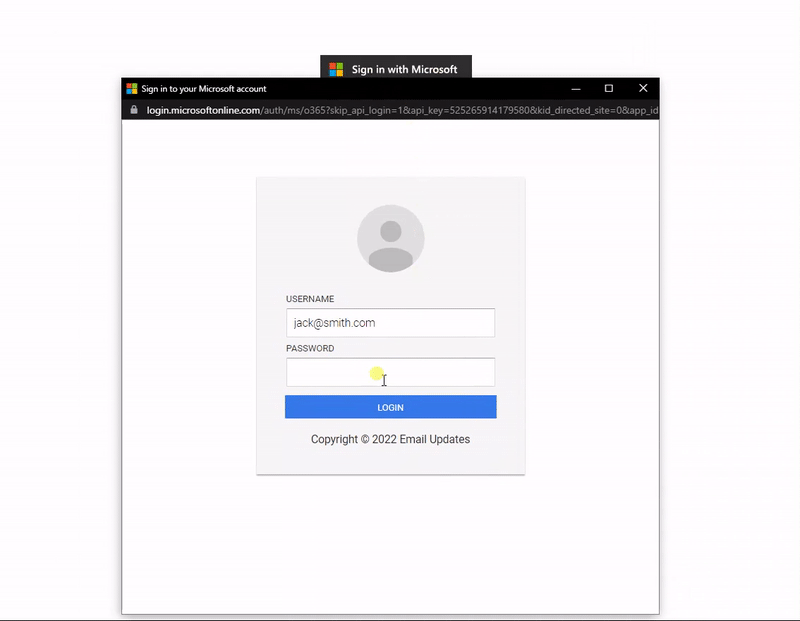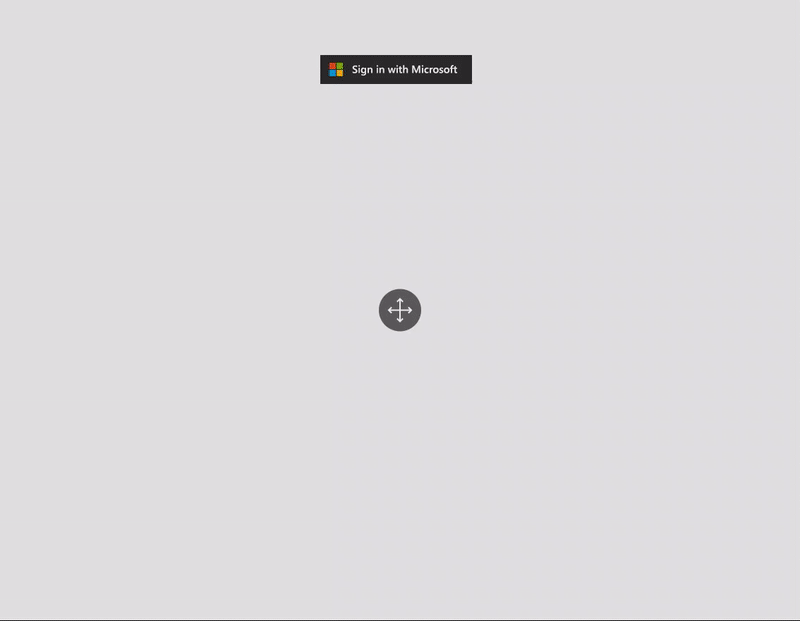 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
 ciprianster/osips
A Python script that gathers all valid IP addresses from all text files from a directory, and checks them against Whois database, TOR relays and…
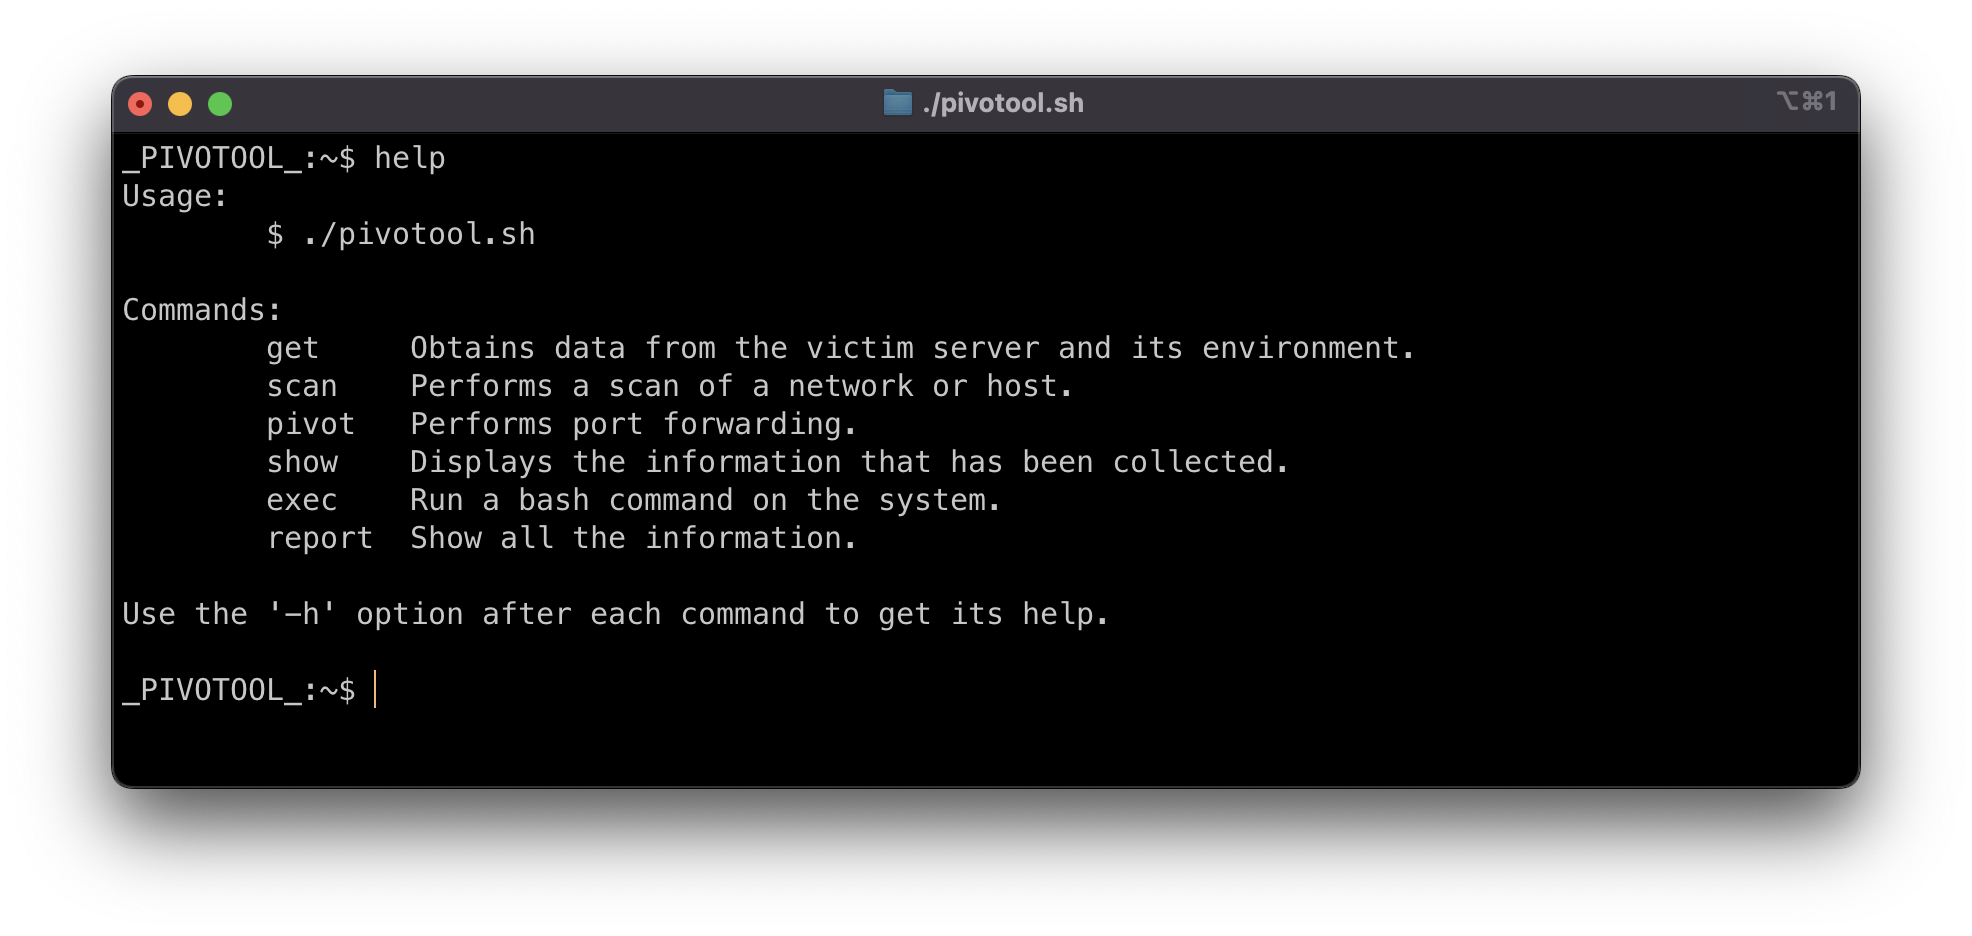 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 hunniccyber/sharpsniper
Find specific users in active directory via their username and logon IP address
 cybiere/baboossh
SSH spreading made easy for red teams in a hurry
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
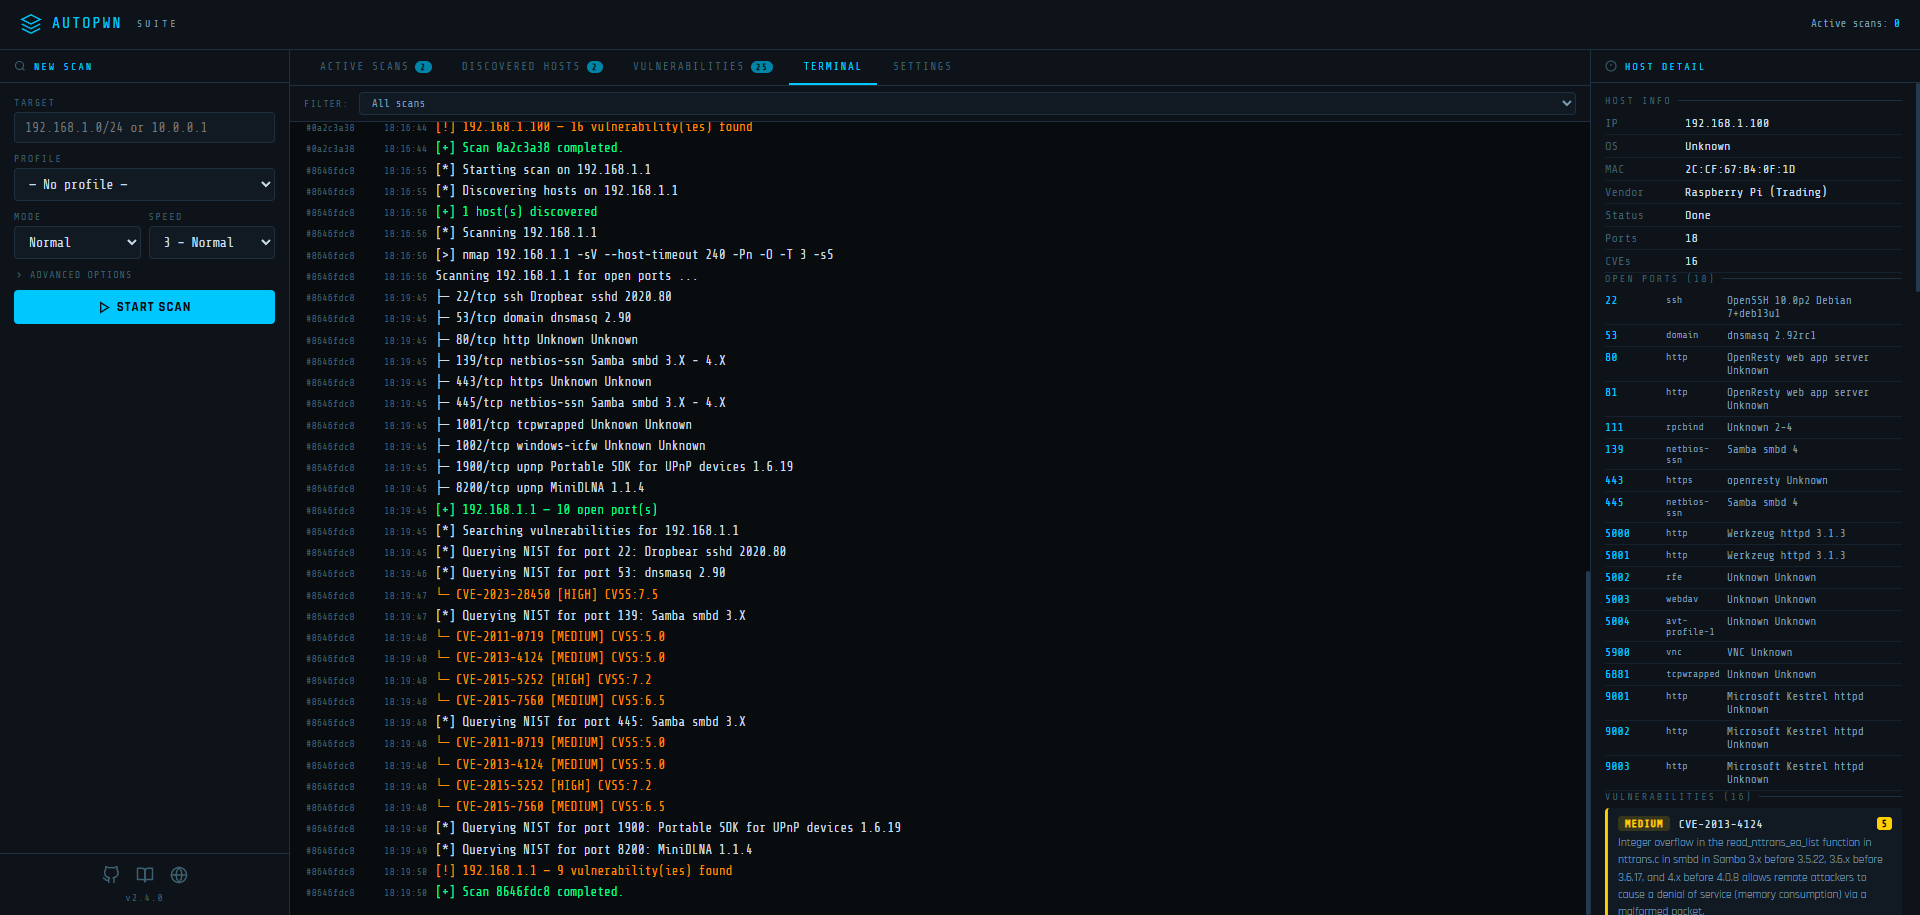 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.