Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
2866 results
CVE-2026-28695-craft-rce-bypass preview

CVE-2026-28695-craft-rce-bypass

GitHubgbuyssens/cve-2026-28695-craft-rce-bypass

Authenticated, **blind** remote code execution in Craft CMS. Fix for CVE-2026-28695
exploitationpayload-developmentpenetration-testing+5
1
1 month ago
ps-ppl-bypass preview

ps-ppl-bypass

GitHubr41n3rzuf477/ps-ppl-bypass

Process Explorer vulnerable driver PPL Bypass
binary-exploitationdefensive-toolsexploitation+5
2829 days ago
CVE-2026-31857 preview

CVE-2026-31857

GitHub0xtatsuki/cve-2026-31857

Craft CMS RCE via relational conditionals in the control panel
exploitationpayload-developmentpenetration-testing+6
28 days ago
CVE-2026-34990-poc preview

CVE-2026-34990-poc

GitHubdennisdgr/cve-2026-34990-poc

LPE PoC for CVE-2026-34990 using a CUPS root file write vulnerability.
exploitationpayload-developmentpenetration-testing+2
21 month ago
CVE-2026-34990 preview

CVE-2026-34990

GitHubgbuyssens/cve-2026-34990

Local privilege escalation against a root `cupsd`.
exploitationpayload-developmentpenetration-testing+3
1 month ago
CVE-2026-34990-poc preview

CVE-2026-34990-poc

GitHubkhush-613/cve-2026-34990-poc

Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
exploitationpayload-developmentpenetration-testing+4
21 month ago
cups-2.4.16-lpe preview

cups-2.4.16-lpe

GitHubmrdebora/cups-2.4.16-lpe

CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)

exploitationpayload-generationpenetration-testing+4
1 month ago
Koi preview

Koi

GitHubb3rt1ng/koi

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
371 day ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
4 years ago
CVE-2026-44011-craft-rce-poc preview

CVE-2026-44011-craft-rce-poc

GitHubcyberuser-hash/cve-2026-44011-craft-rce-poc

Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…
exploitationpayload-generationpenetration-testing+4
21 month ago
watchTowr-vs-Citrix-Netscaler-CVE-2026-88771 preview

watchTowr-vs-Citrix-Netscaler-CVE-2026-88771

GitHubwatchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88771

Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…

exploitationpapers-researchpayload-generation+5
221 month ago
blindxss-lite preview

blindxss-lite

GitHubyuyudhn/blindxss-lite

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
command-and-controldata-exfiltrationinformation-gathering+7
310 days ago
CVE-2026-48356 preview

CVE-2026-48356

GitHubabraxas/cve-2026-48356

Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
exploitationlabs-practicepayload-generation+5
1 day ago
CVE-2026-63030-CVE-2026-60137 preview

CVE-2026-63030-CVE-2026-60137

GitHubz3rodayhacks/cve-2026-63030-cve-2026-60137

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
exploitationpayload-developmentpenetration-testing+6
2 months ago
CVE-2026-63030 preview

CVE-2026-63030

GitHublangz337/cve-2026-63030

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
command-and-controlexploitationpayload-development+8
11 month ago
CVE-2026-60004 preview

CVE-2026-60004

GitHubyym8538/cve-2026-60004

Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
exploitationpayload-developmentpenetration-testing+6
12 months ago
polychrome-rs preview

polychrome-rs

GitHubdovelus/polychrome-rs

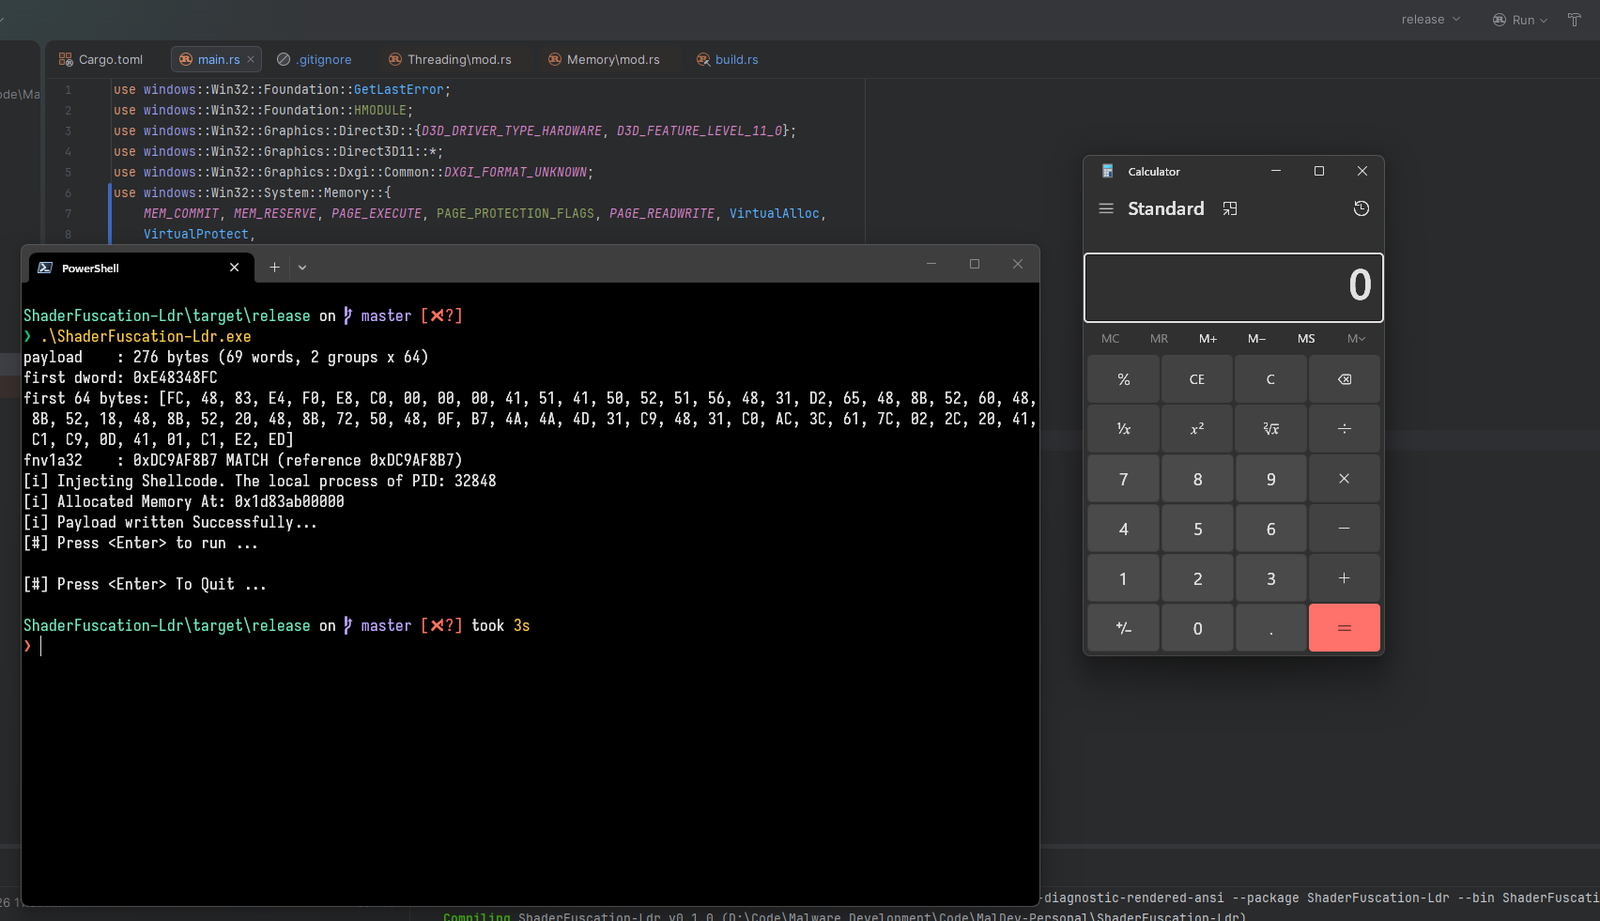
A PoC on how to use a Compute Shader as Payload
defensive-toolsencryption-decryption-toolsexploitation+5
101 month ago
waybend preview

waybend

GitHubprinciplebreach/waybend

Self-hosted SSRF redirect, payload, callback, and DNS workbench

command-and-controldns-analysisinformation-gathering+9
51 month ago
Previous1234…100Next