

PocketPentester
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
dns-analysisfuzzinghash-analysis+9
8
tegal1337/pocketpentesterOffline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 slaptat/copyfail30
copyFail for python pre 3.10, without os.splice()
 mrechofi/greedos_v2
A Multi-vector DoS tool for Cybersecurity Red Teamers' .
 fulxey/cve-2022-0543
Redis RCE through Lua Sandbox Escape vulnerability
 shadowforge-cyber/cve-2026-104286-poc
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team…
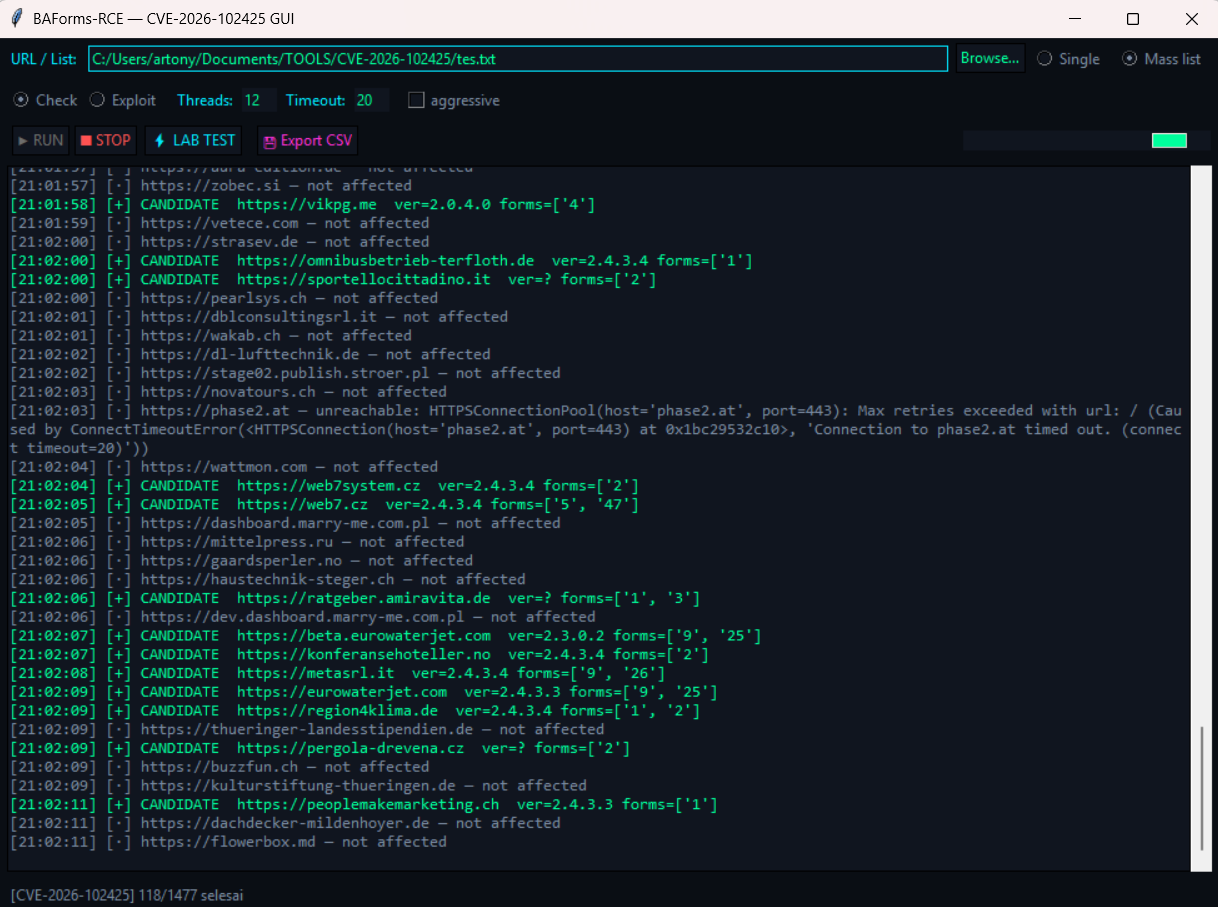 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 yym8538/cve-2026-16723
Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…