

Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
111
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
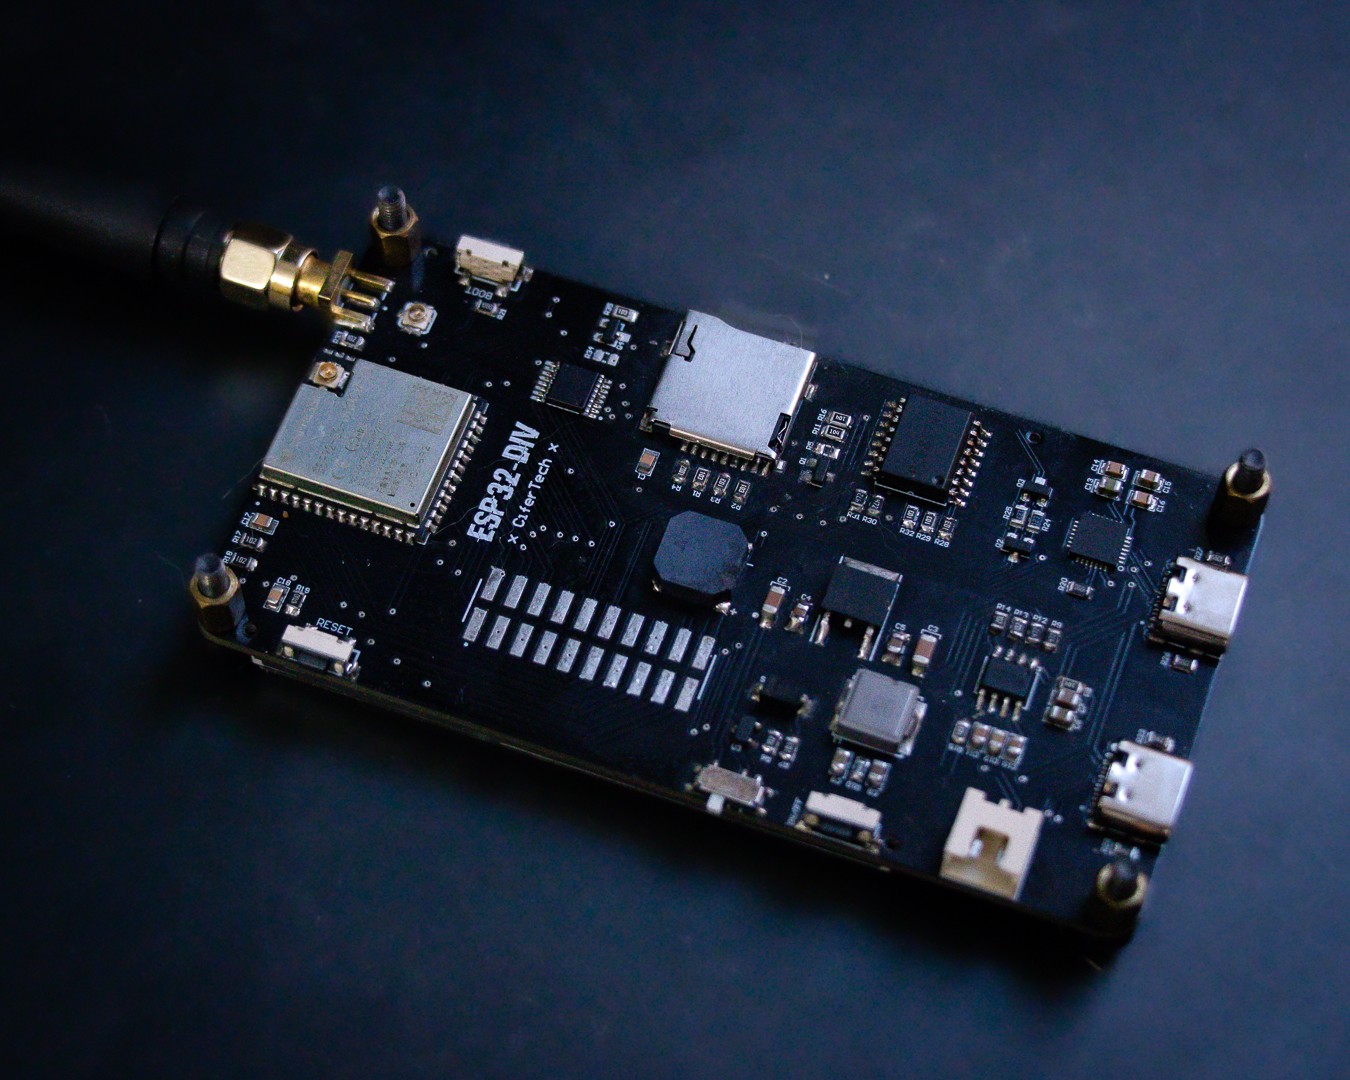 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32

 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 cisc0-gif/kitt
Python-Based Pentesting Framework
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…