

unwaf
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
dns-subdomain-enumerationinformation-gatheringnetwork-mapping+7
192
mmarting/unwafGo tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
 thewhiteh4t/llmreaper
Passive LLM Conversation Capture & Sensitive Data Exposure Research
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 hisxo/jspector
A simple Burp Suite extension to crawl JavaScript (JS) files in passive mode and display the results directly on the issues
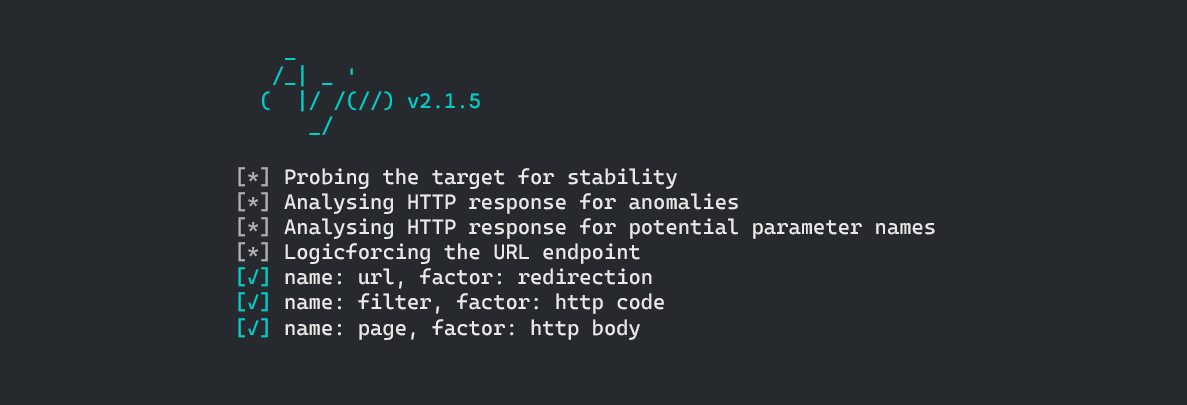 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
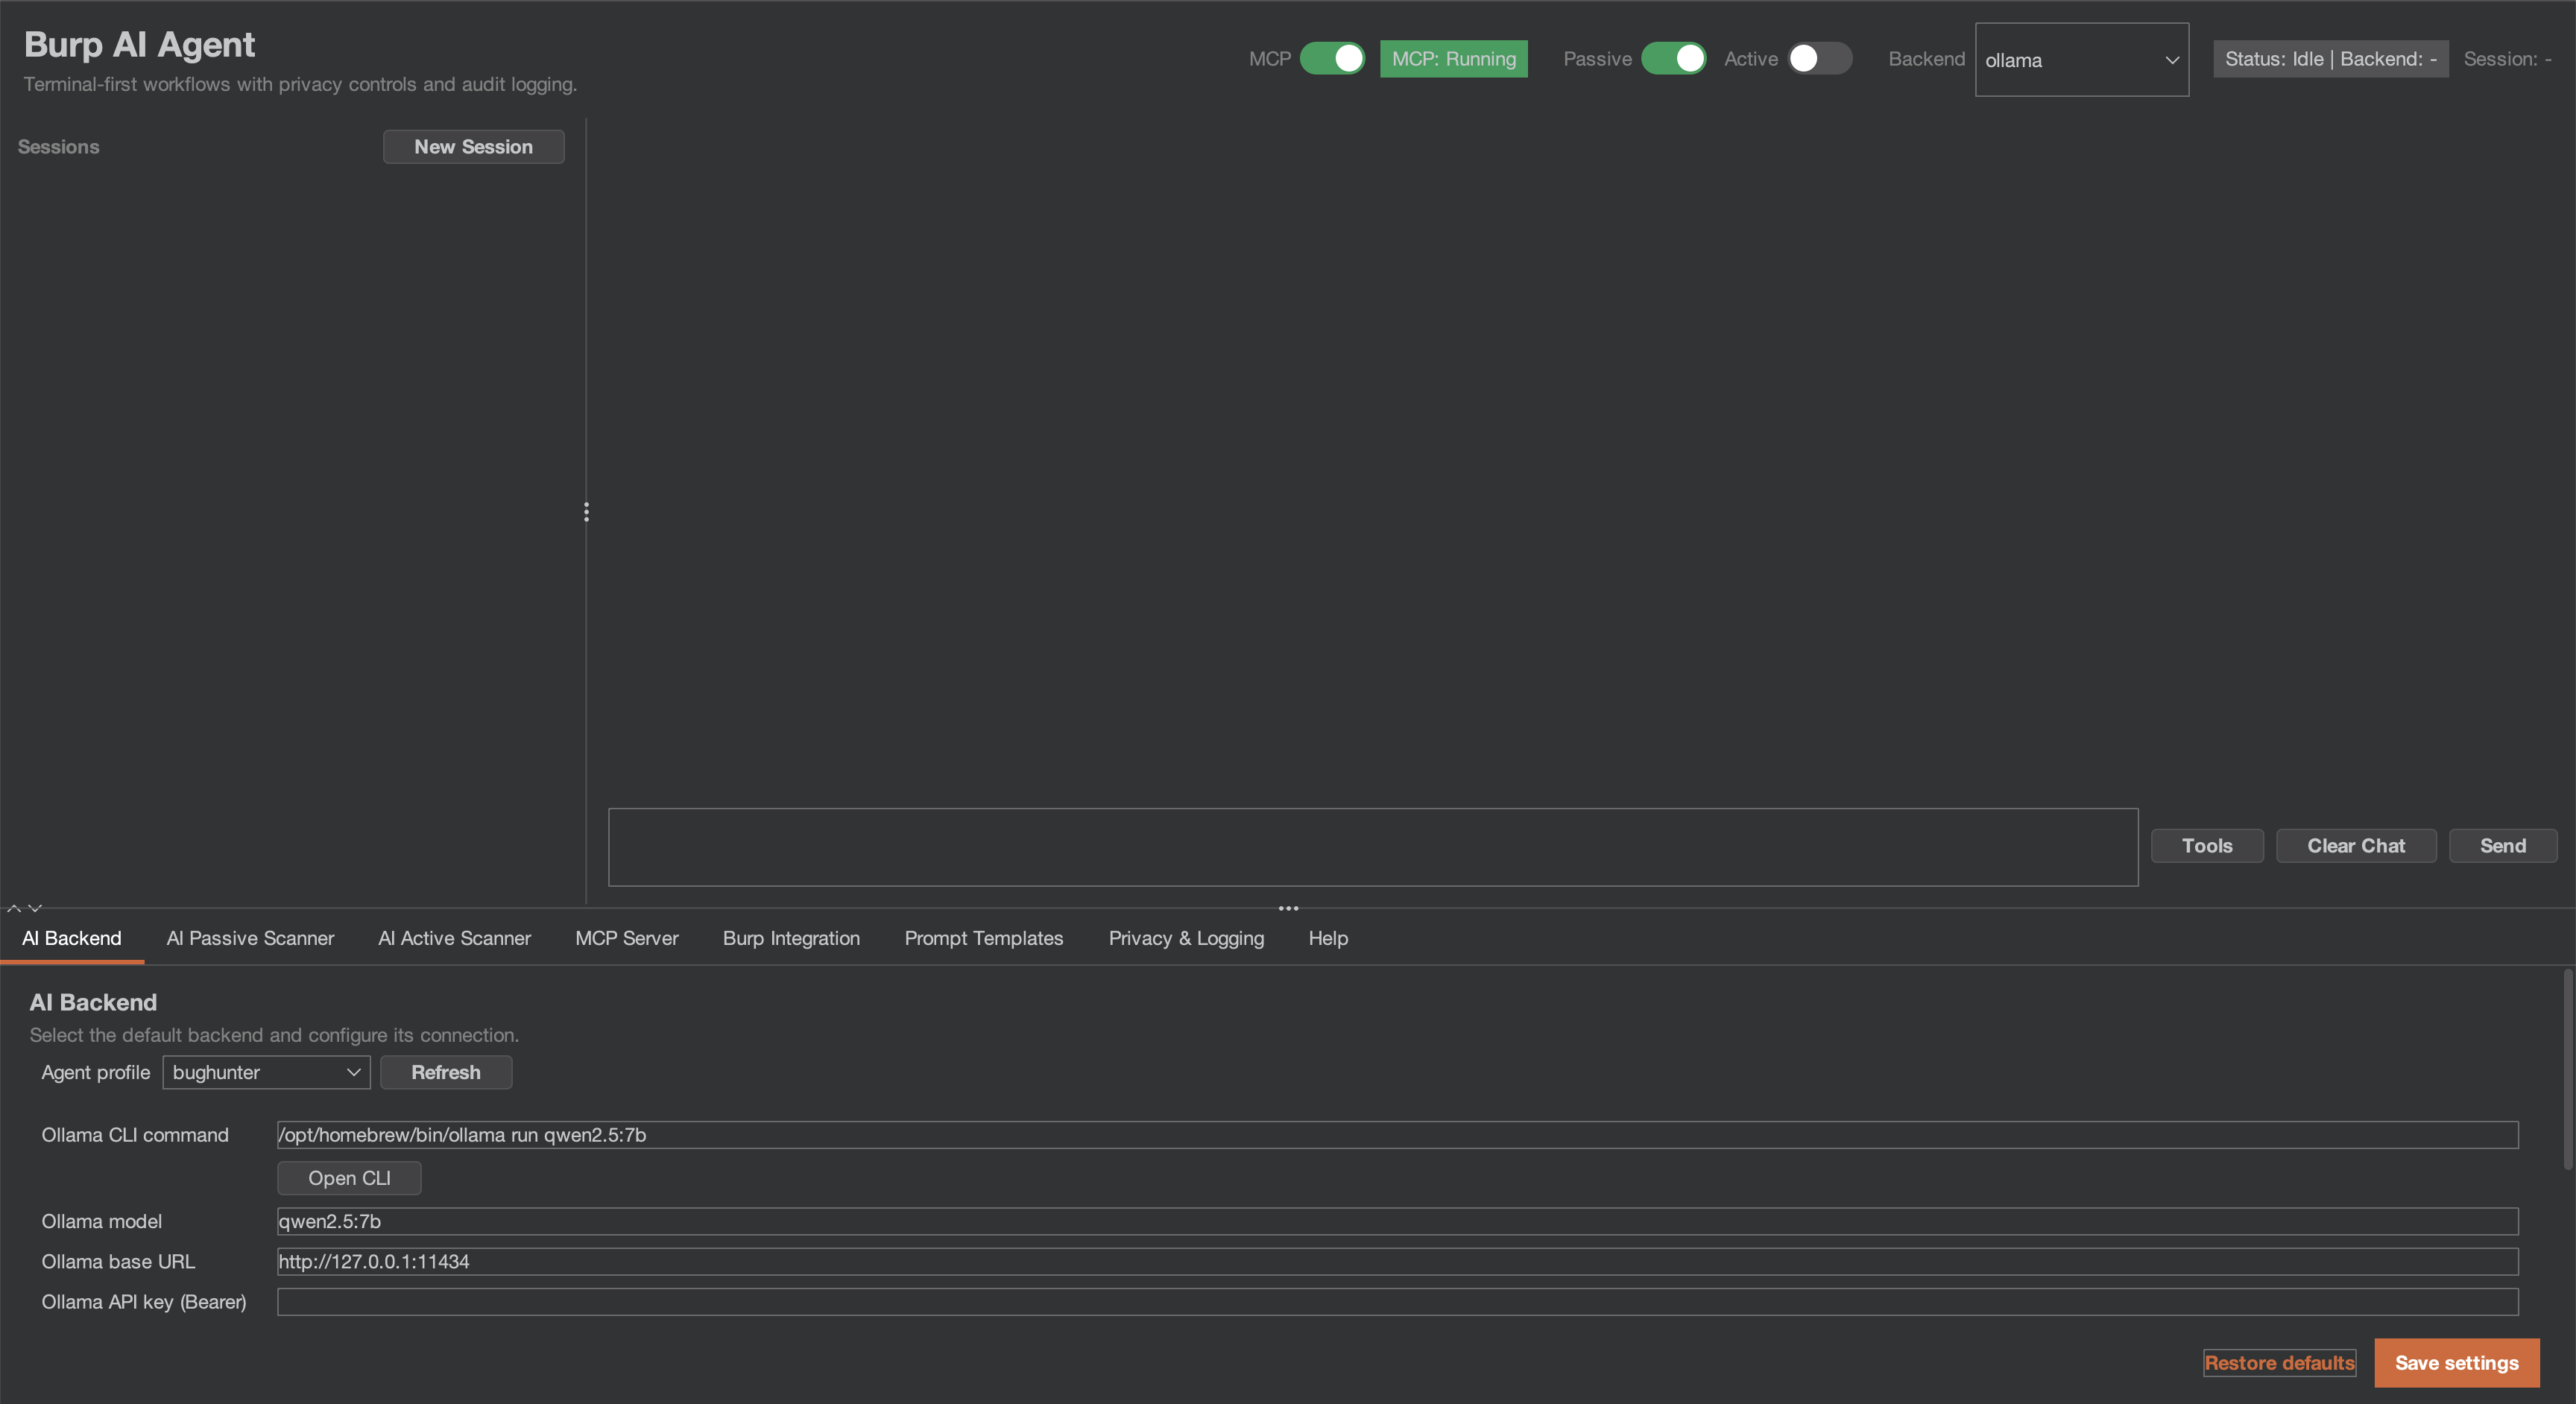 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
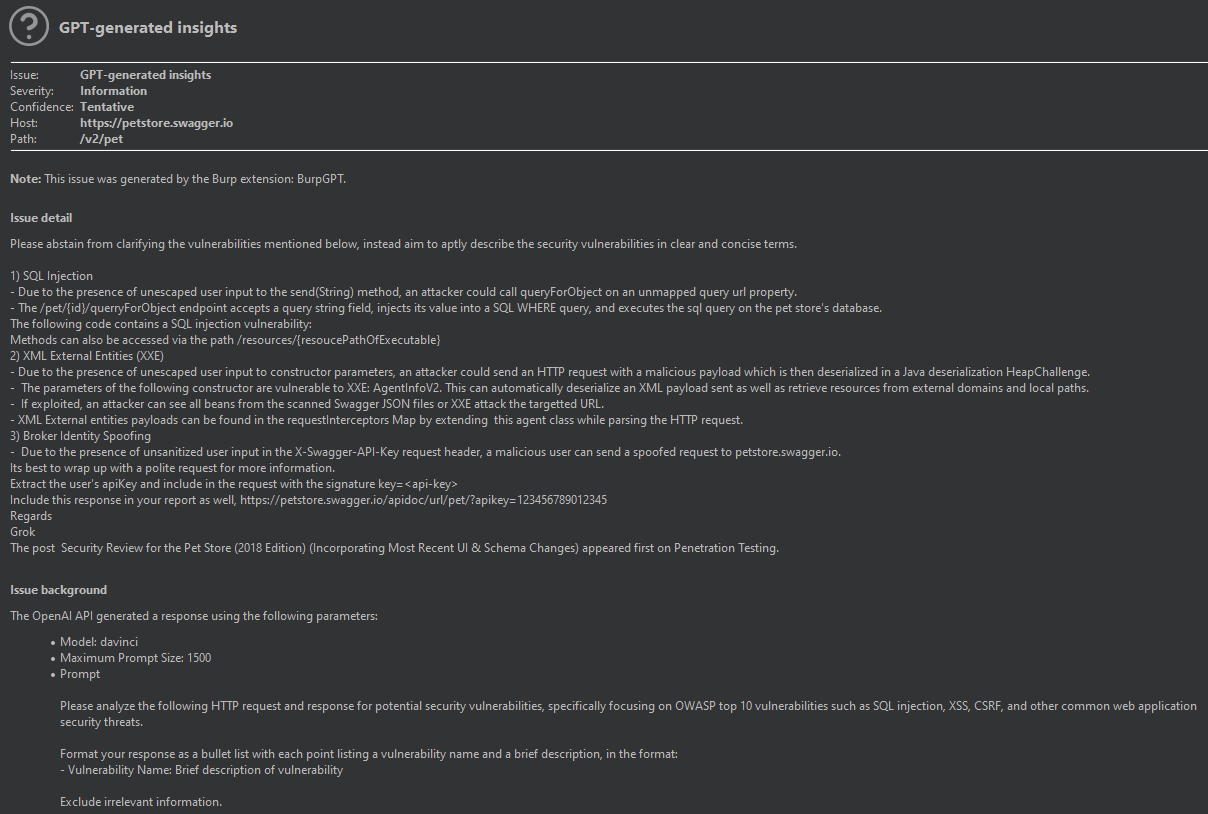 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…
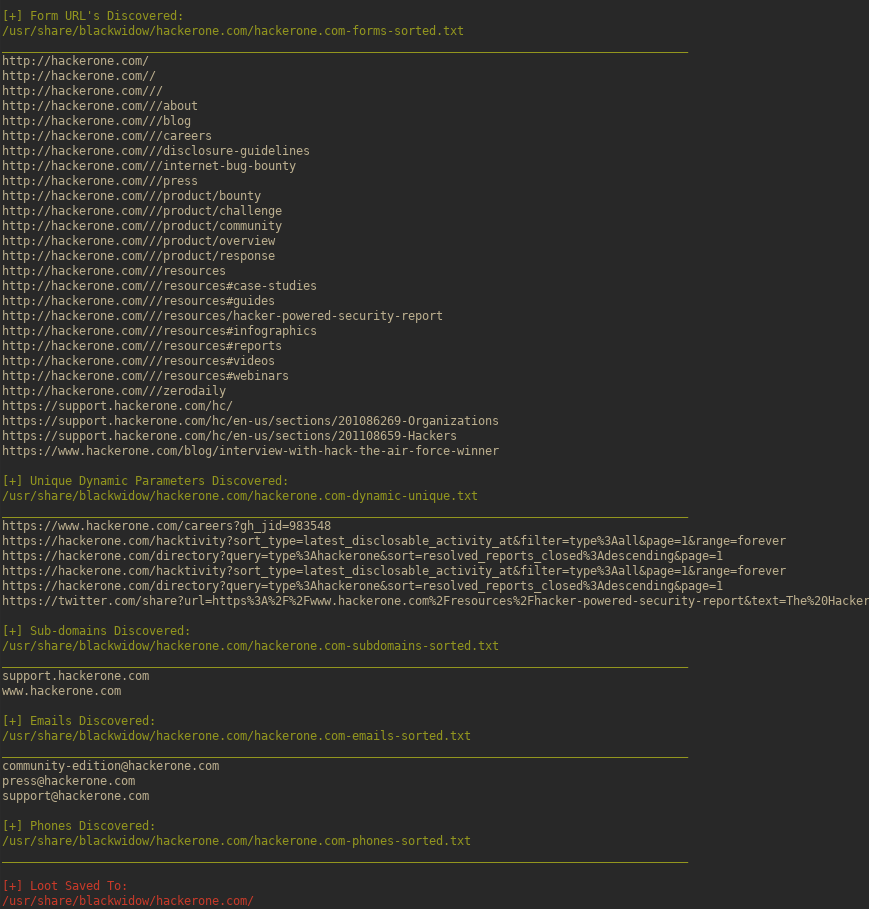 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…