
xyntia
 binsec/xyntia
Xyntia, the black-box deobfuscator
binary-analysiscode-analysisdynamic-code-analysis+1
binsec/xyntiaXyntia, the black-box deobfuscator
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
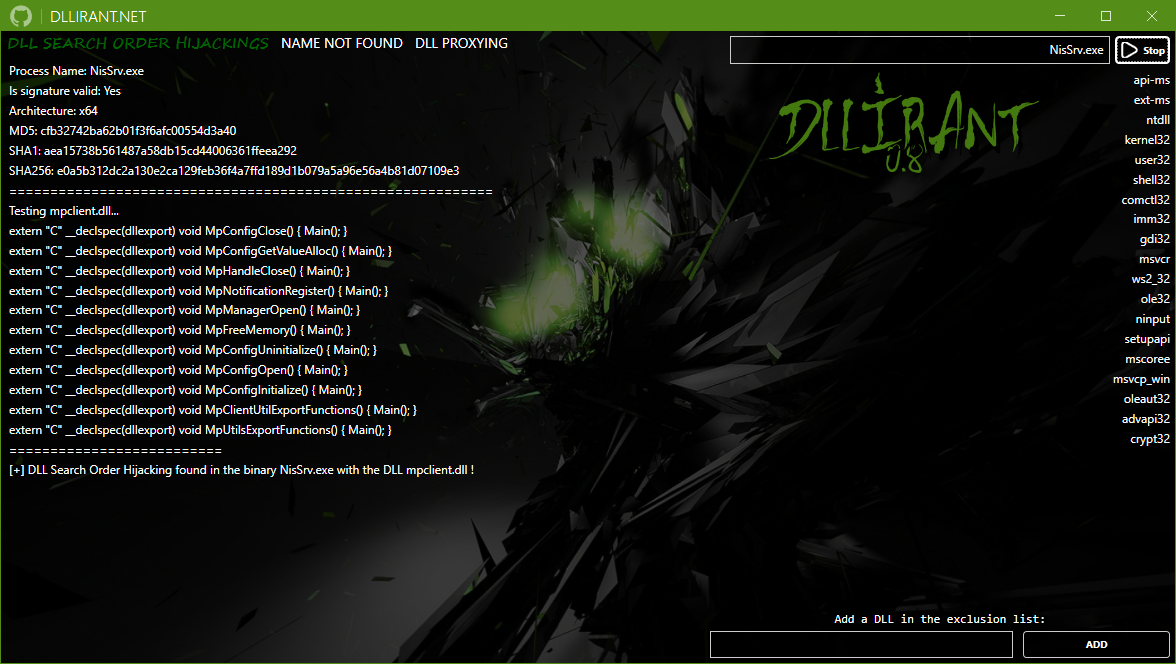 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
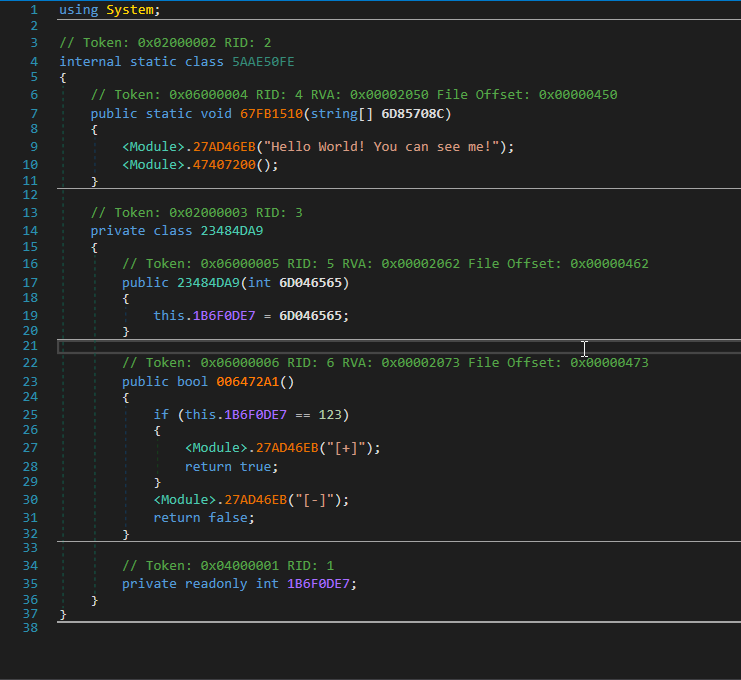 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
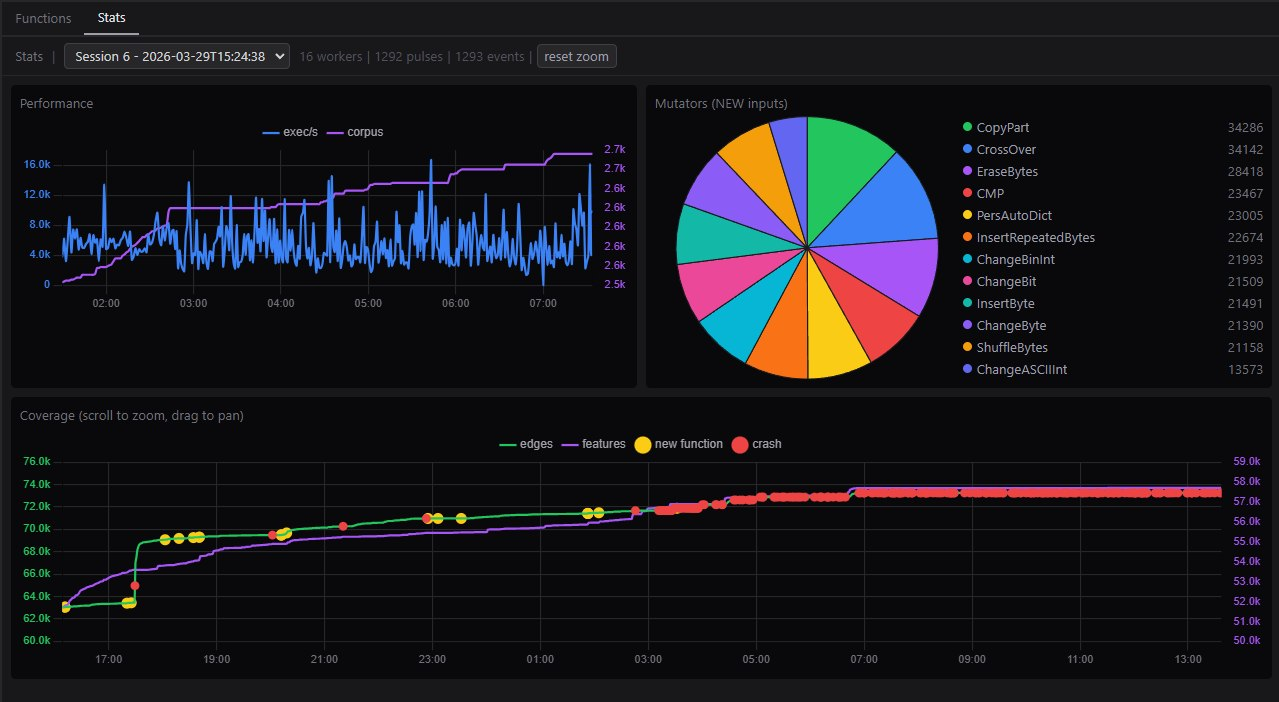 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
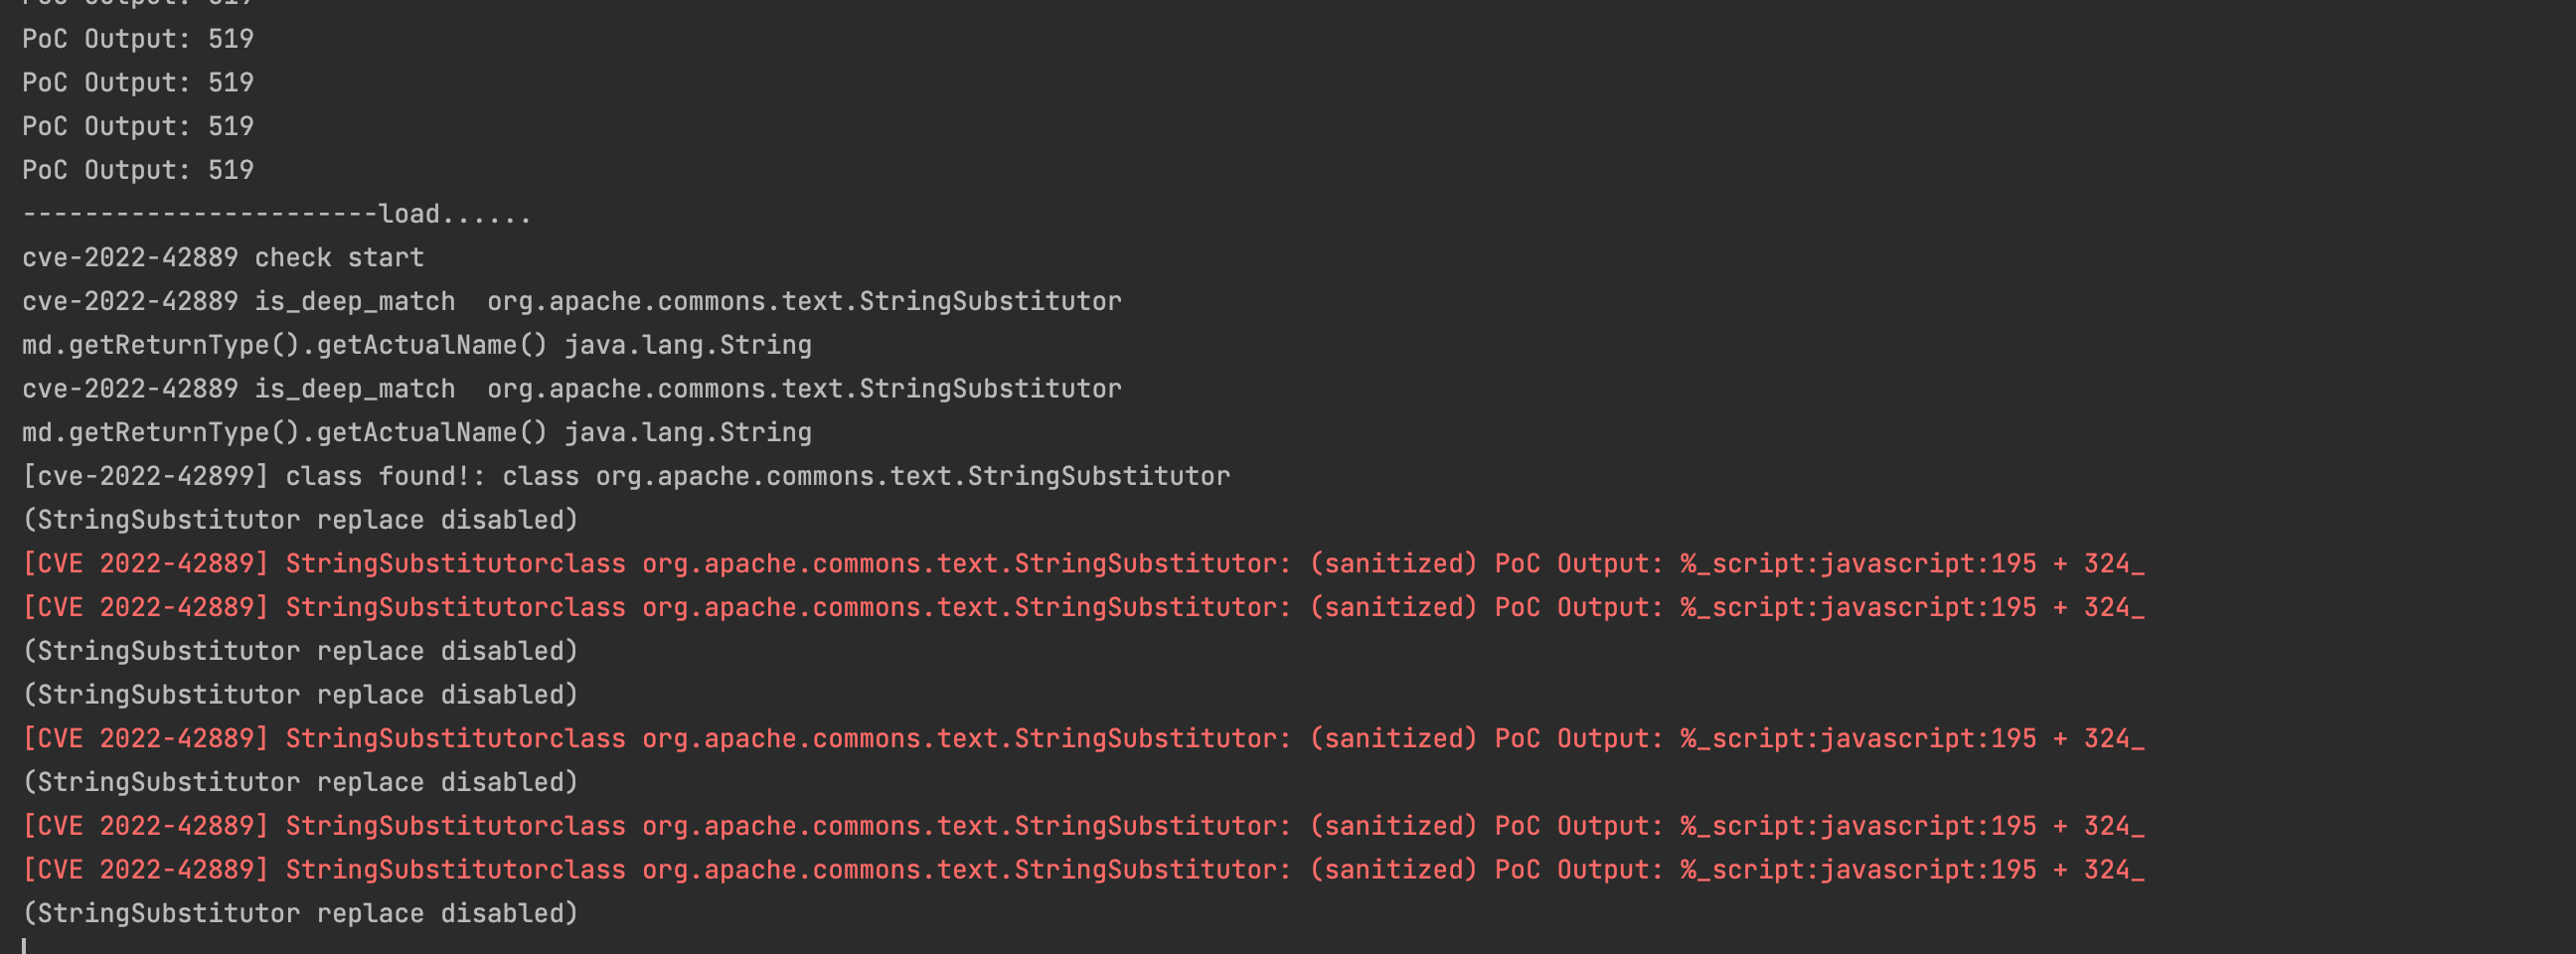 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 gbrindisi/xsssniper
An automatic XSS discovery tool
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU