reDOM
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.

Burp extension for wordpress security scanning

A proxy for net.tcp-based WCF traffic.

A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…

PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)

Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…

Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

Scanner: CVE-2026-42208 LiteLLM SQL Injection — Python scanner for BerriAI LiteLLM proxy instances

Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.

Orchestration component of purpleteam

Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…

Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…

Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…

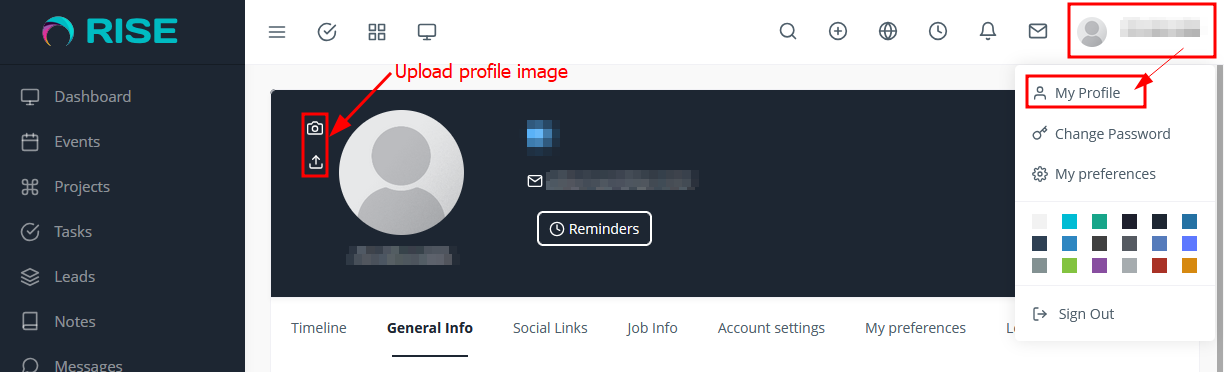
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR

Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…

Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…