
OmniScan
 d3ckx1/omniscan
Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
dynamic-analysis-sandboxingexploit-frameworksfuzzing+6
9
d3ckx1/omniscanMulti-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 withsecureopensource/see
Sandboxed Execution Environment
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
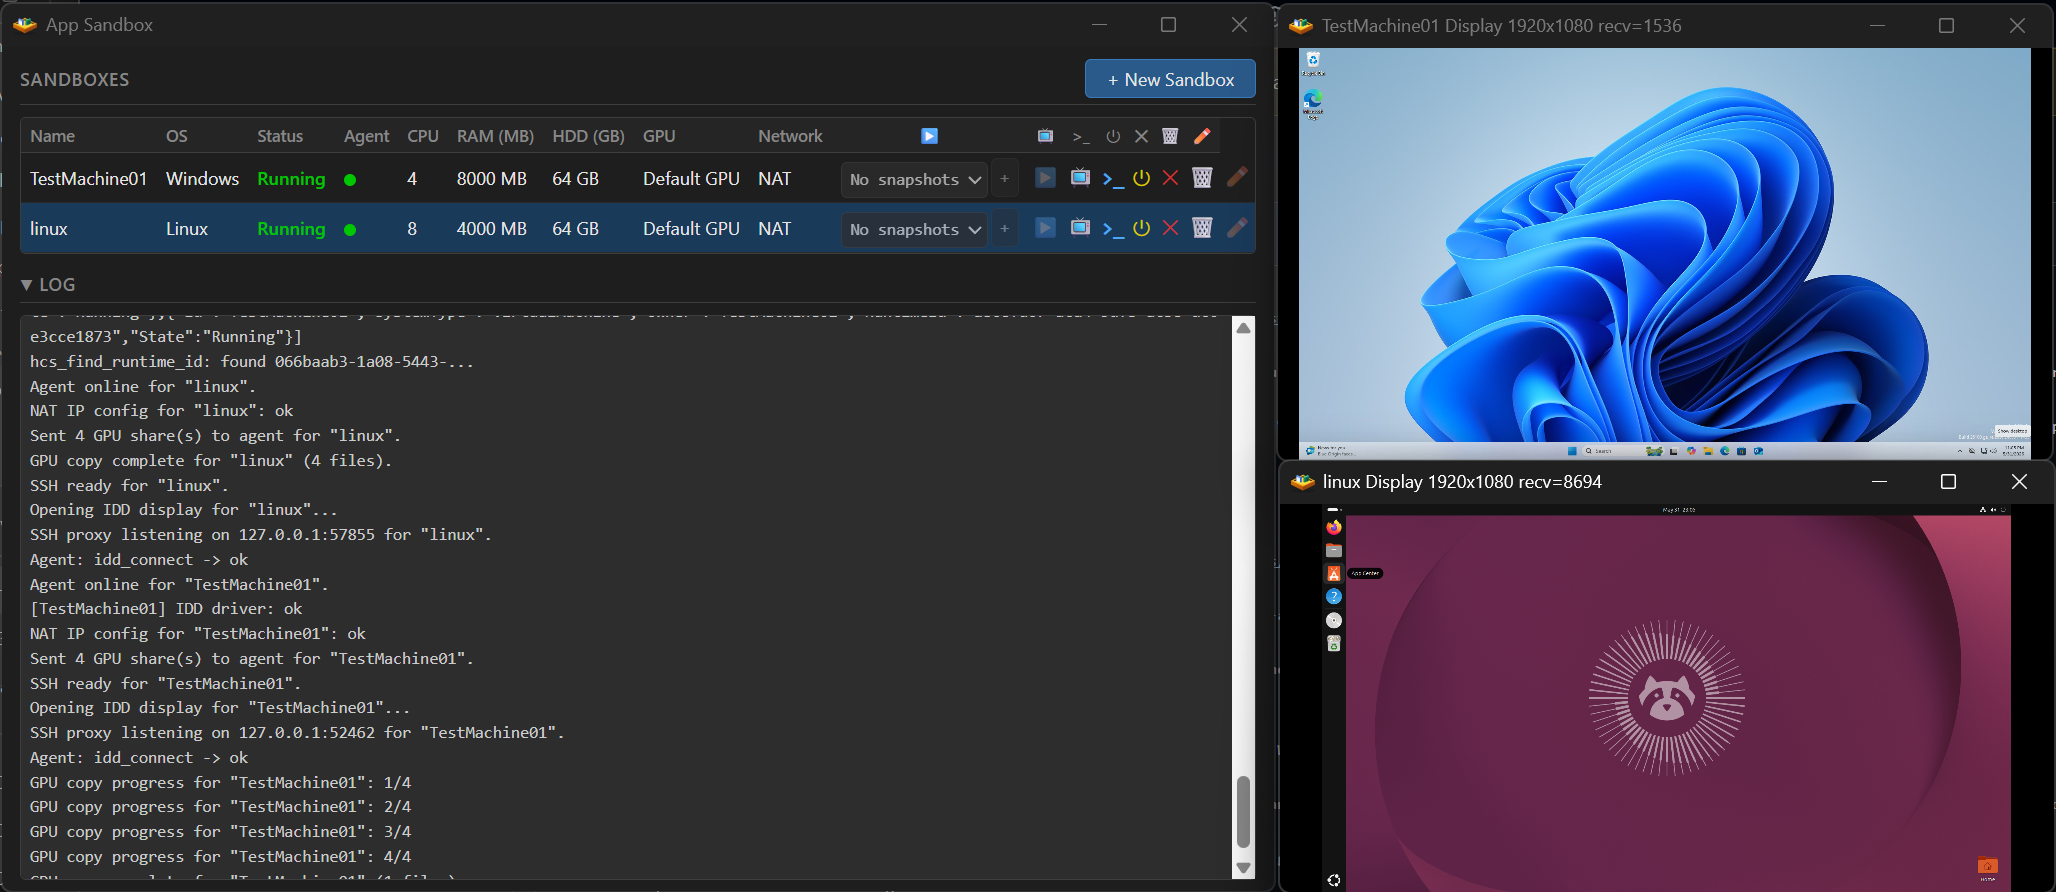 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 takahiroharuyama/ida_haru
scripts/plugins for IDA Pro
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
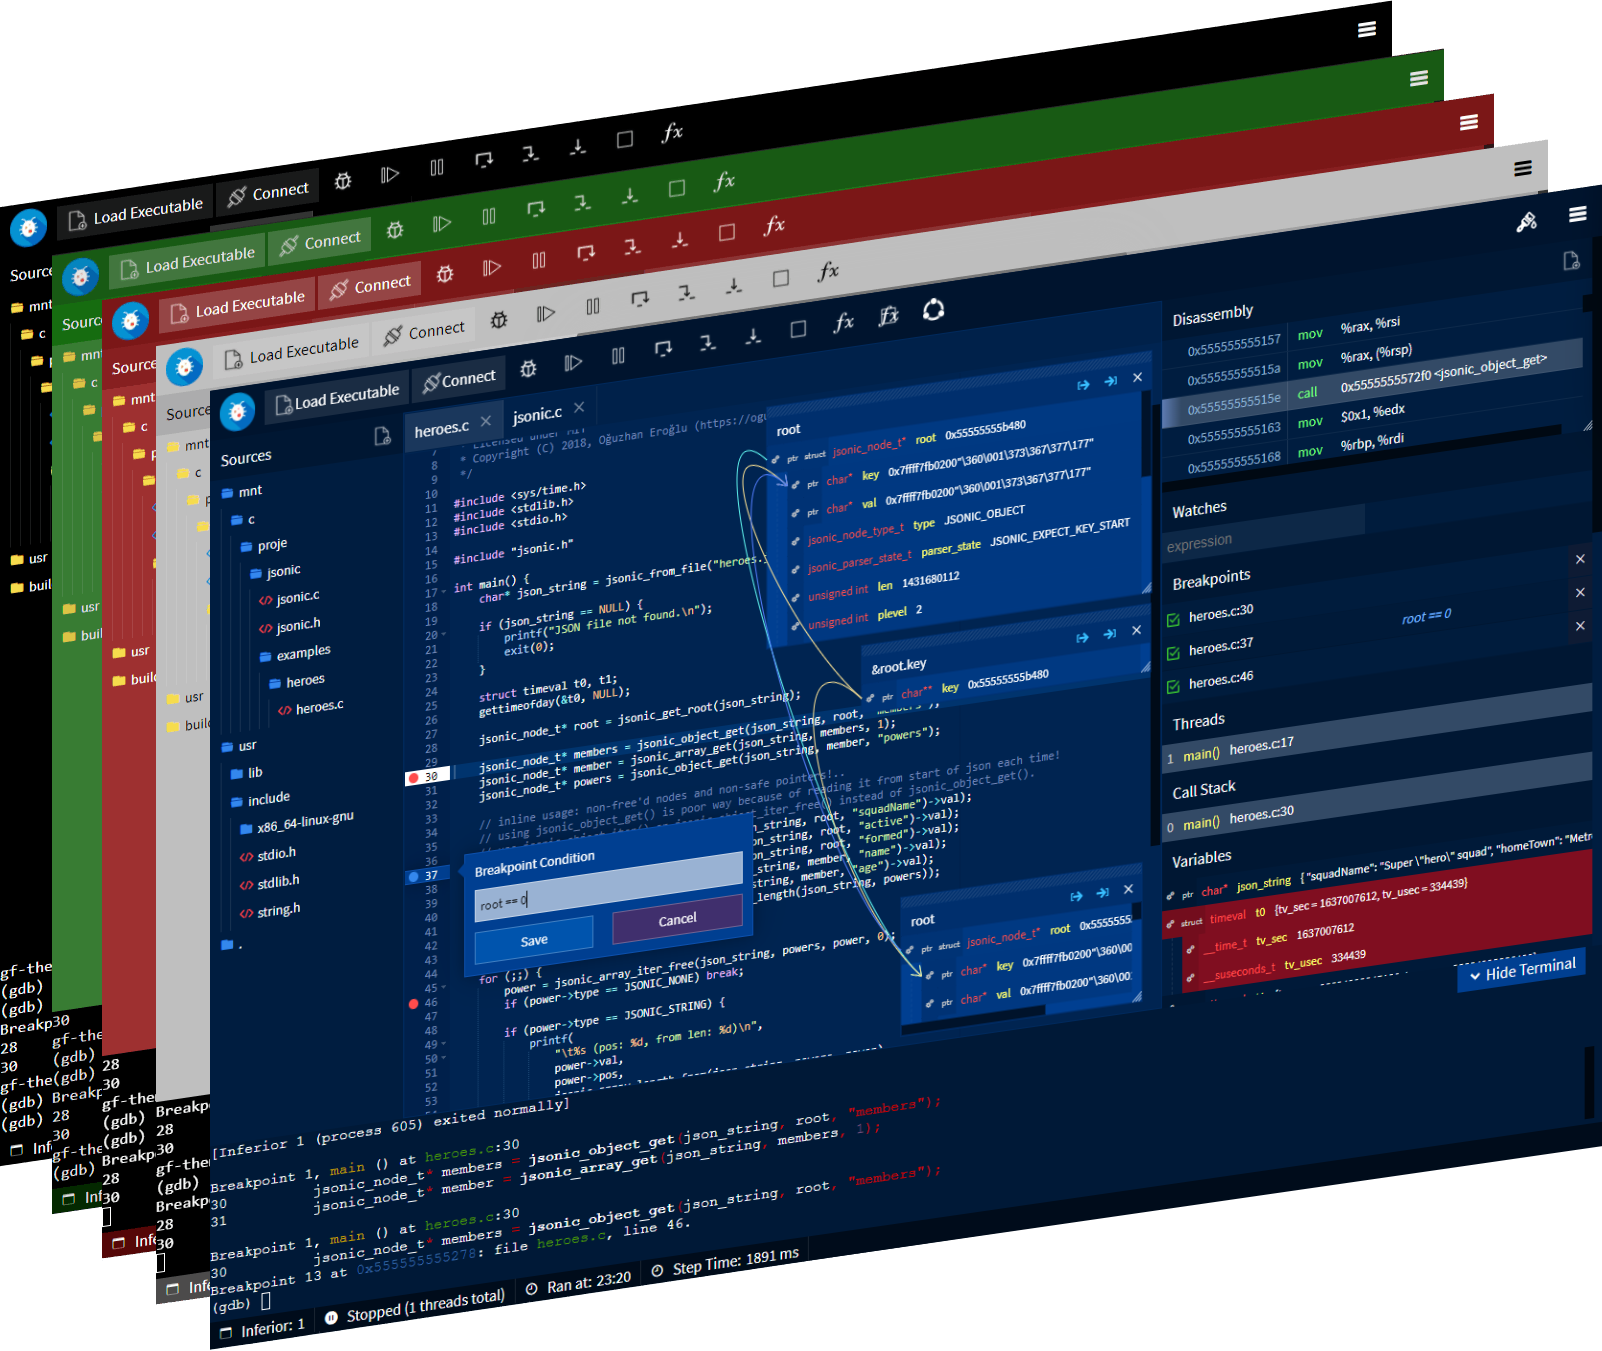 rohanrhu/gdb-frontend
☕ GDBFrontend is an easy, flexible and extensible gui debugger.
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
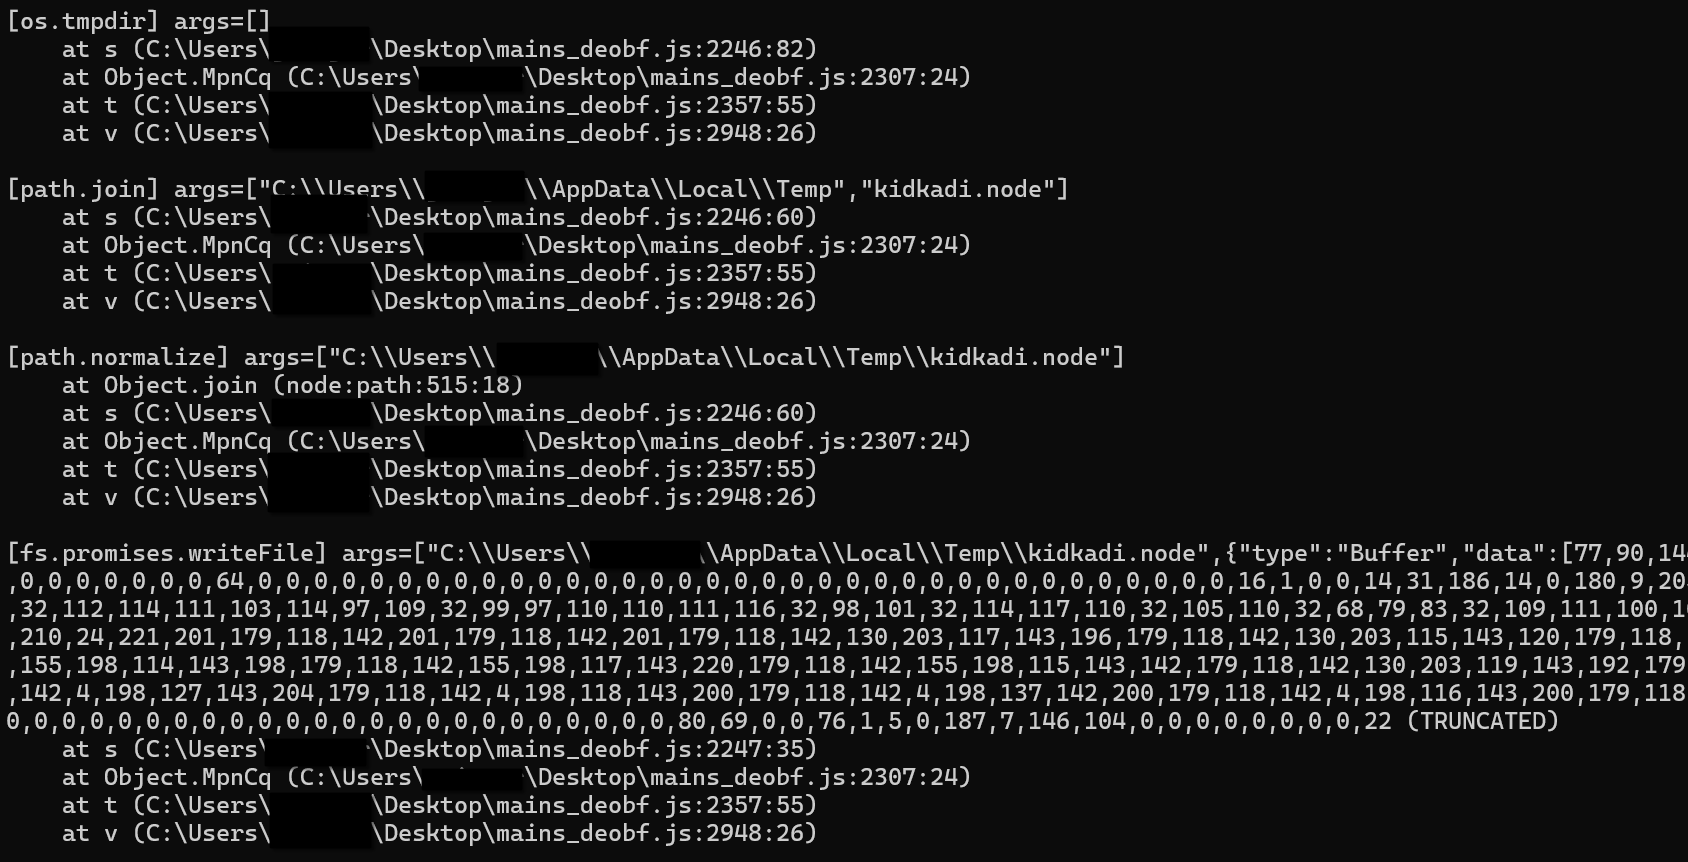 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
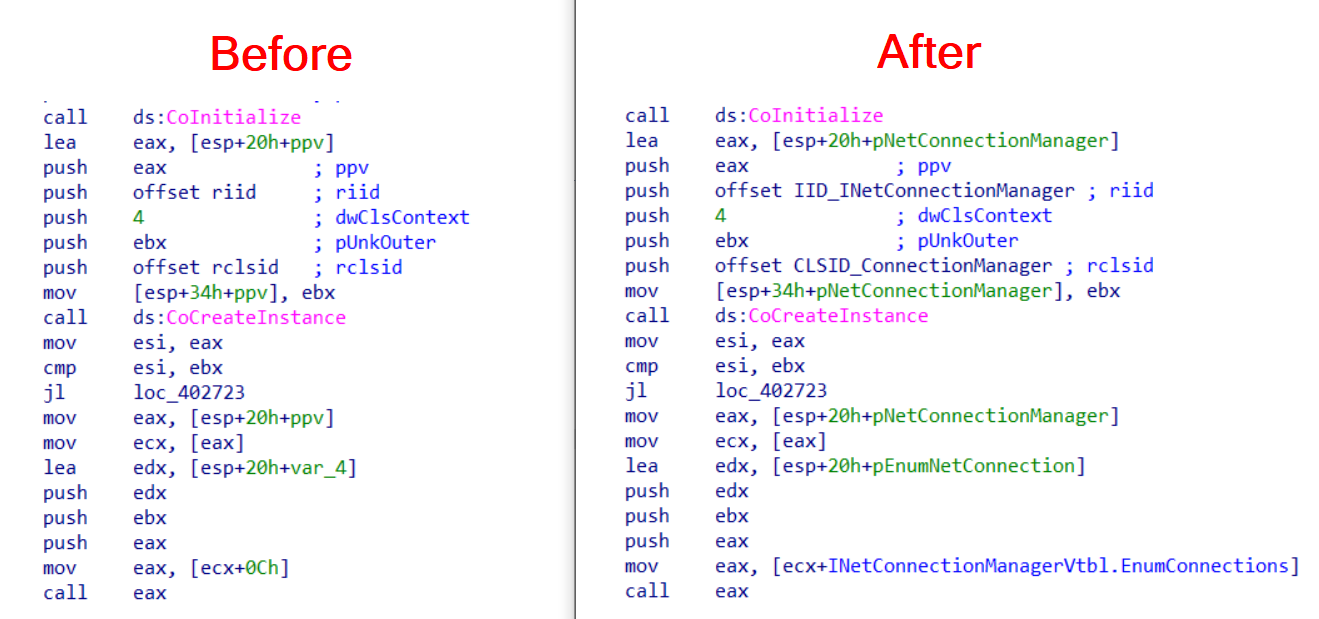 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
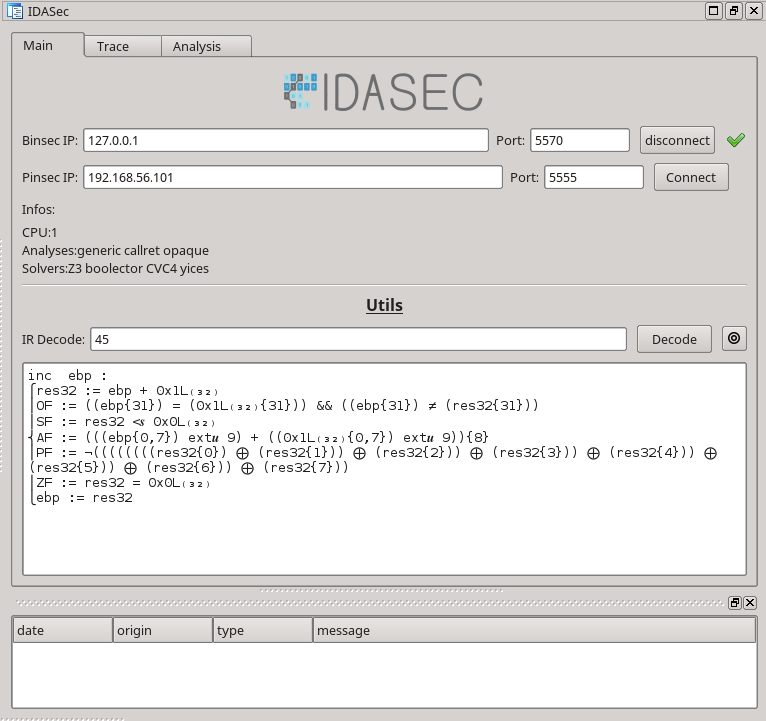 robindavid/idasec
IDA plugin for reverse-engineering and dynamic interactions with the Binsec platform