

vapi
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
api-securityapi-security-testingeducation+4
1.4k1 year ago
roottusk/vapivAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
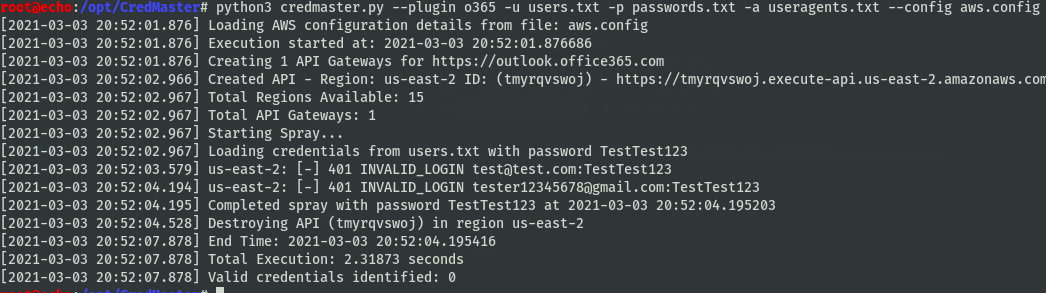 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 owasp/owasp-vwad
⚠️ This repo is no longer in use. Please refer to https://github.com/OWASP/www-project-vulnerable-web-applications-directory
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
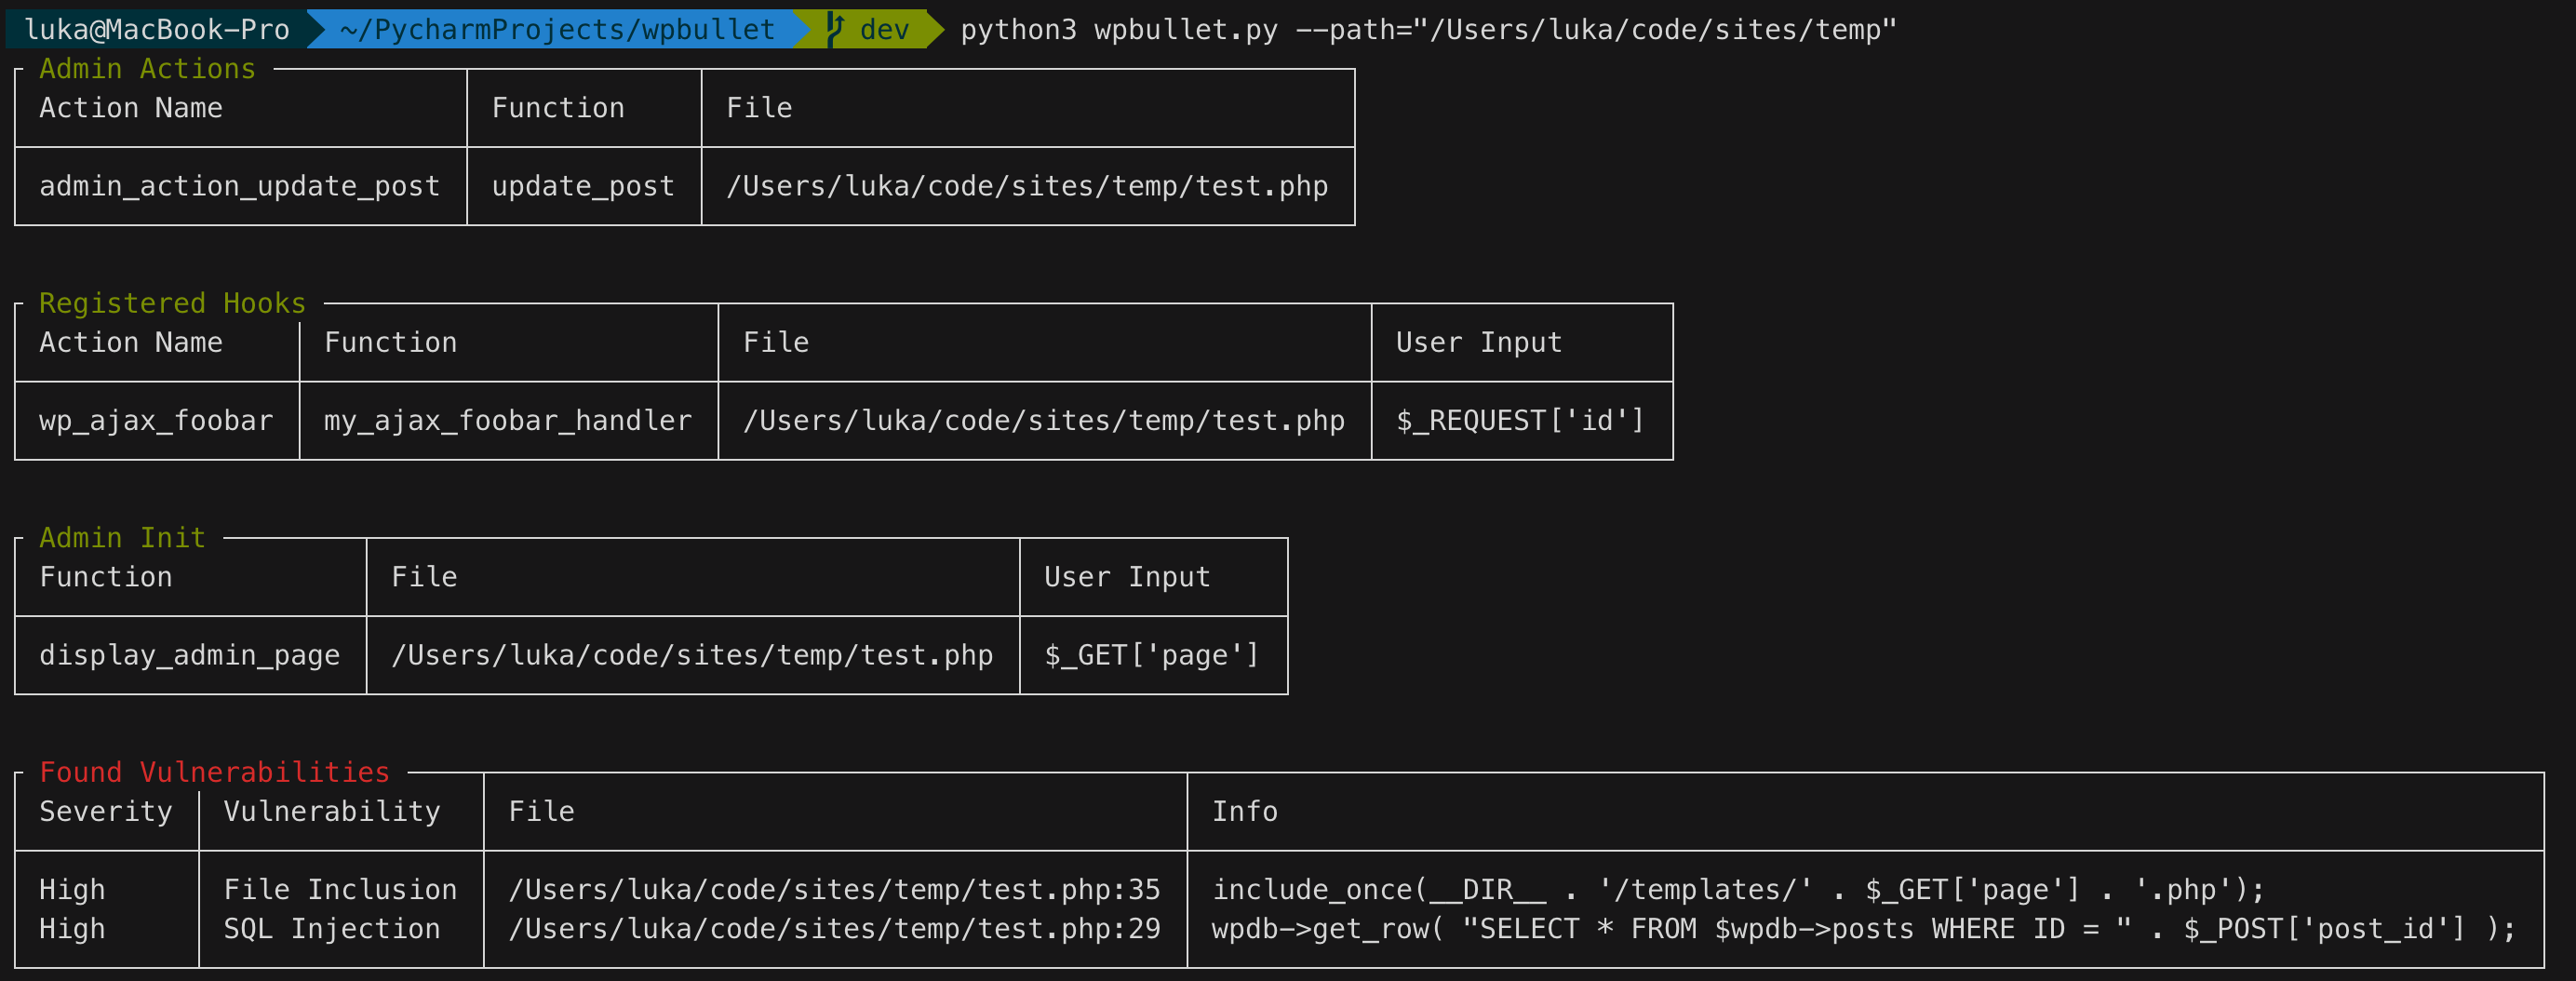 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
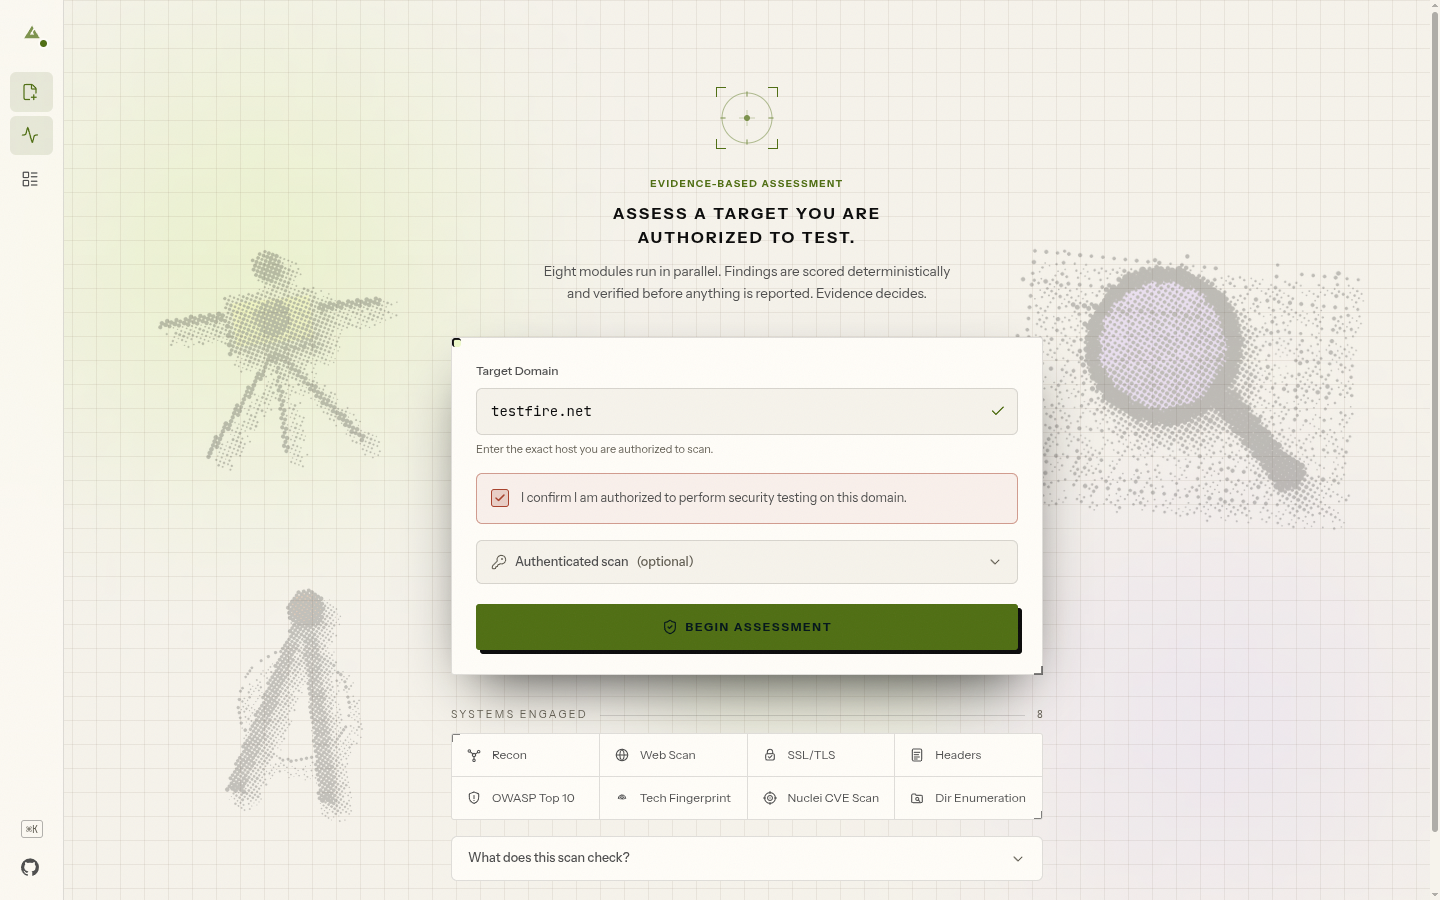 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 ajinabraham/oauth-request-crafter
OAuth Request Crafter