
eWeLink-QR-Code
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
cryptographyexploitationhardware-iot-security+3
1
salgio/ewelink-qr-codeThis repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 xtr4nge/fruitywifi
FruityWiFi is a wireless network auditing tool. The application can be installed in any Debian based system (Jessie) adding the extra packages.…
 nfcgate/nfcgate
An NFC research toolkit application for Android
 nfc-tools/libnfc
Platform independent Near Field Communication (NFC) library
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
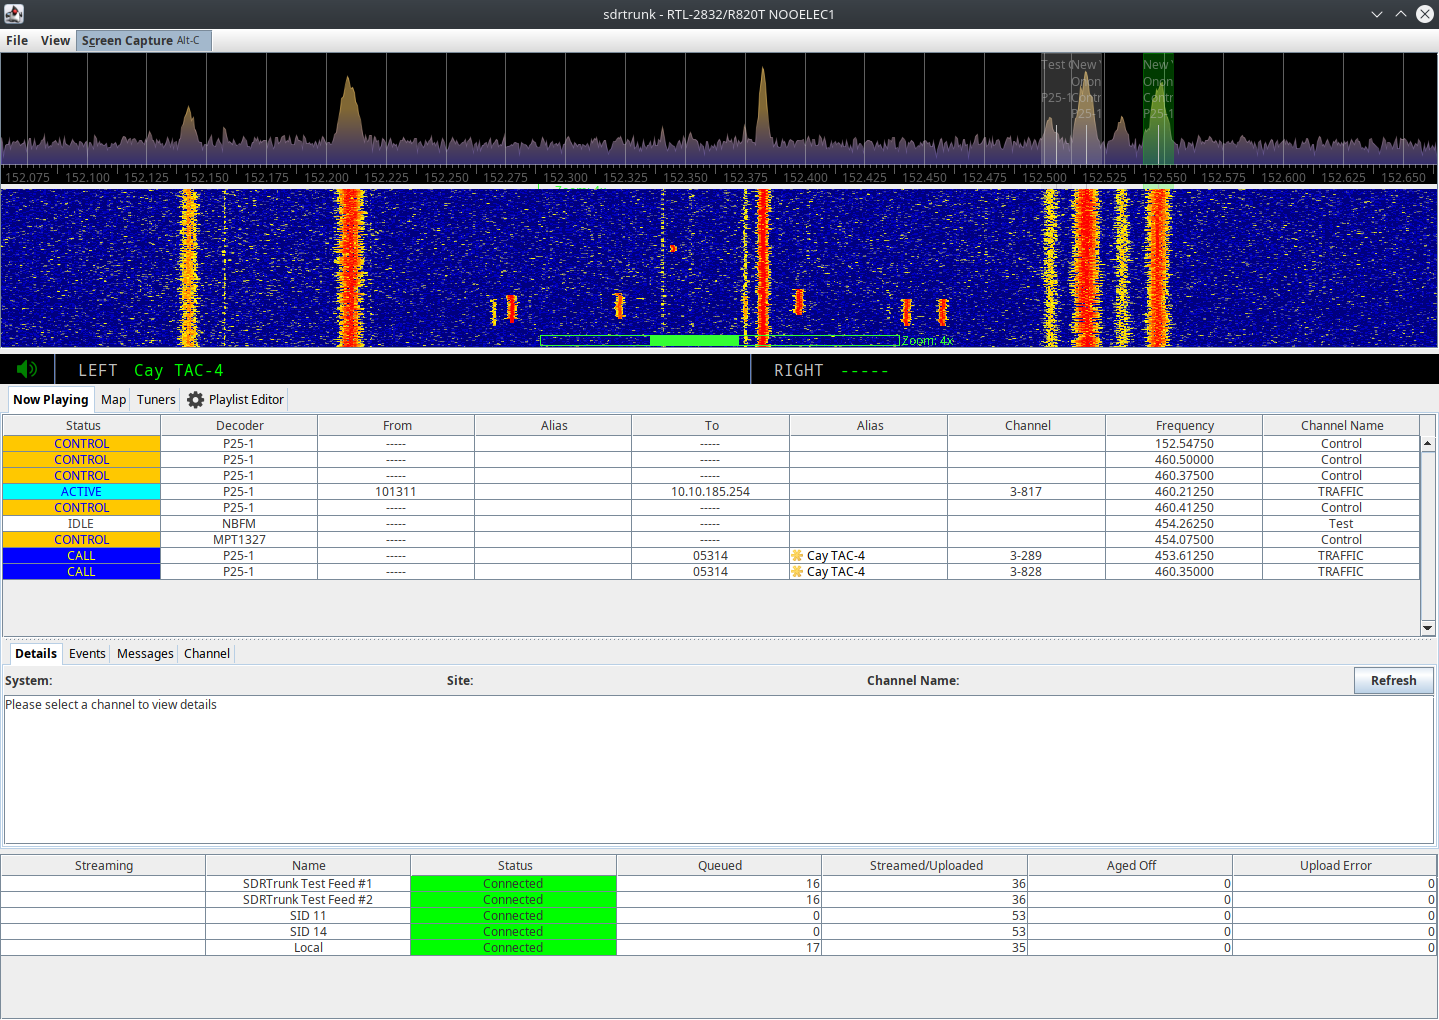 dsheirer/sdrtrunk
A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
 salgio/esptouchcatcher
eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…
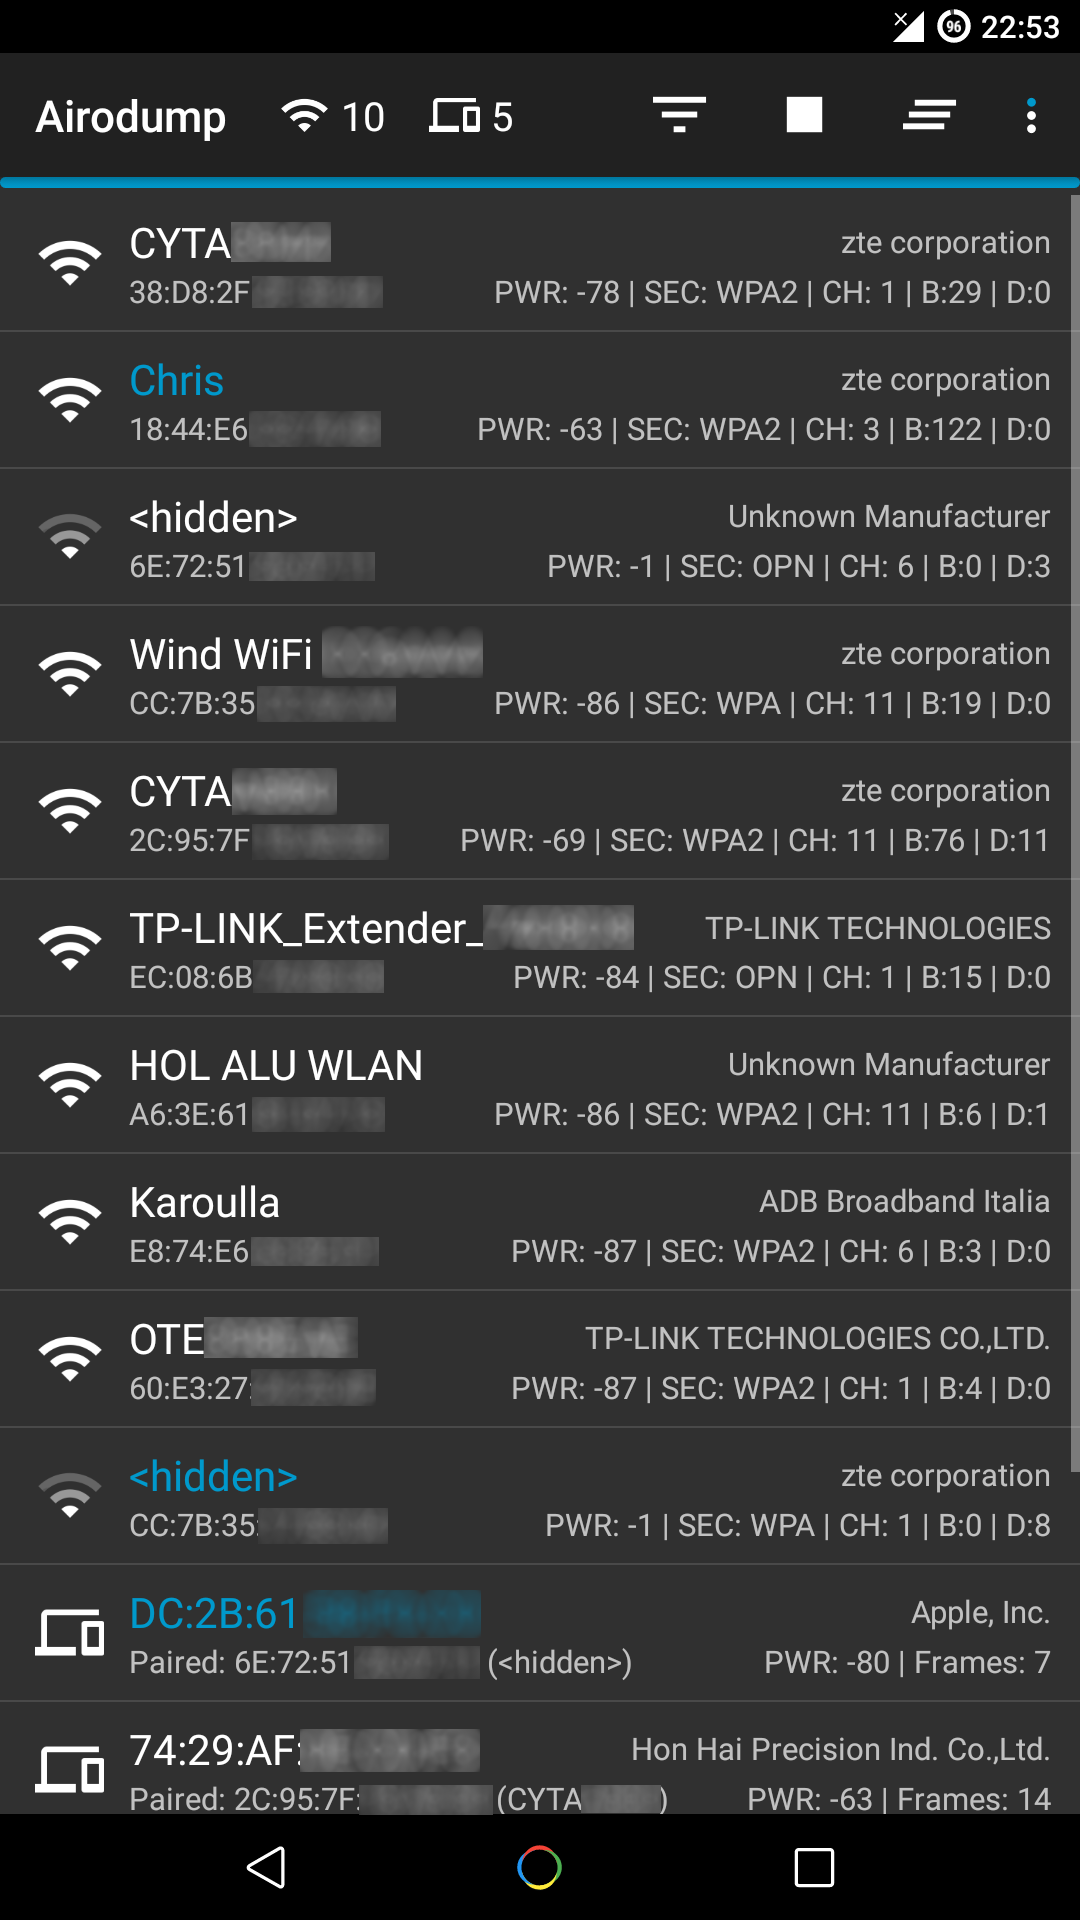 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
 alwentiu/cve-2020-14292
Details of CVE-2020-14292