
Whisper_Bully
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
bluetooth-securityexploitationinformation-gathering+4
34
ymsniper/whisper_bullyThree-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 m4rm0k/cve-2020-10135-bias
CVE 2020-10135 a.k.a BIAS (Bluetooth Impersonation Attack)
 dsheirer/sdrtrunk
A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…
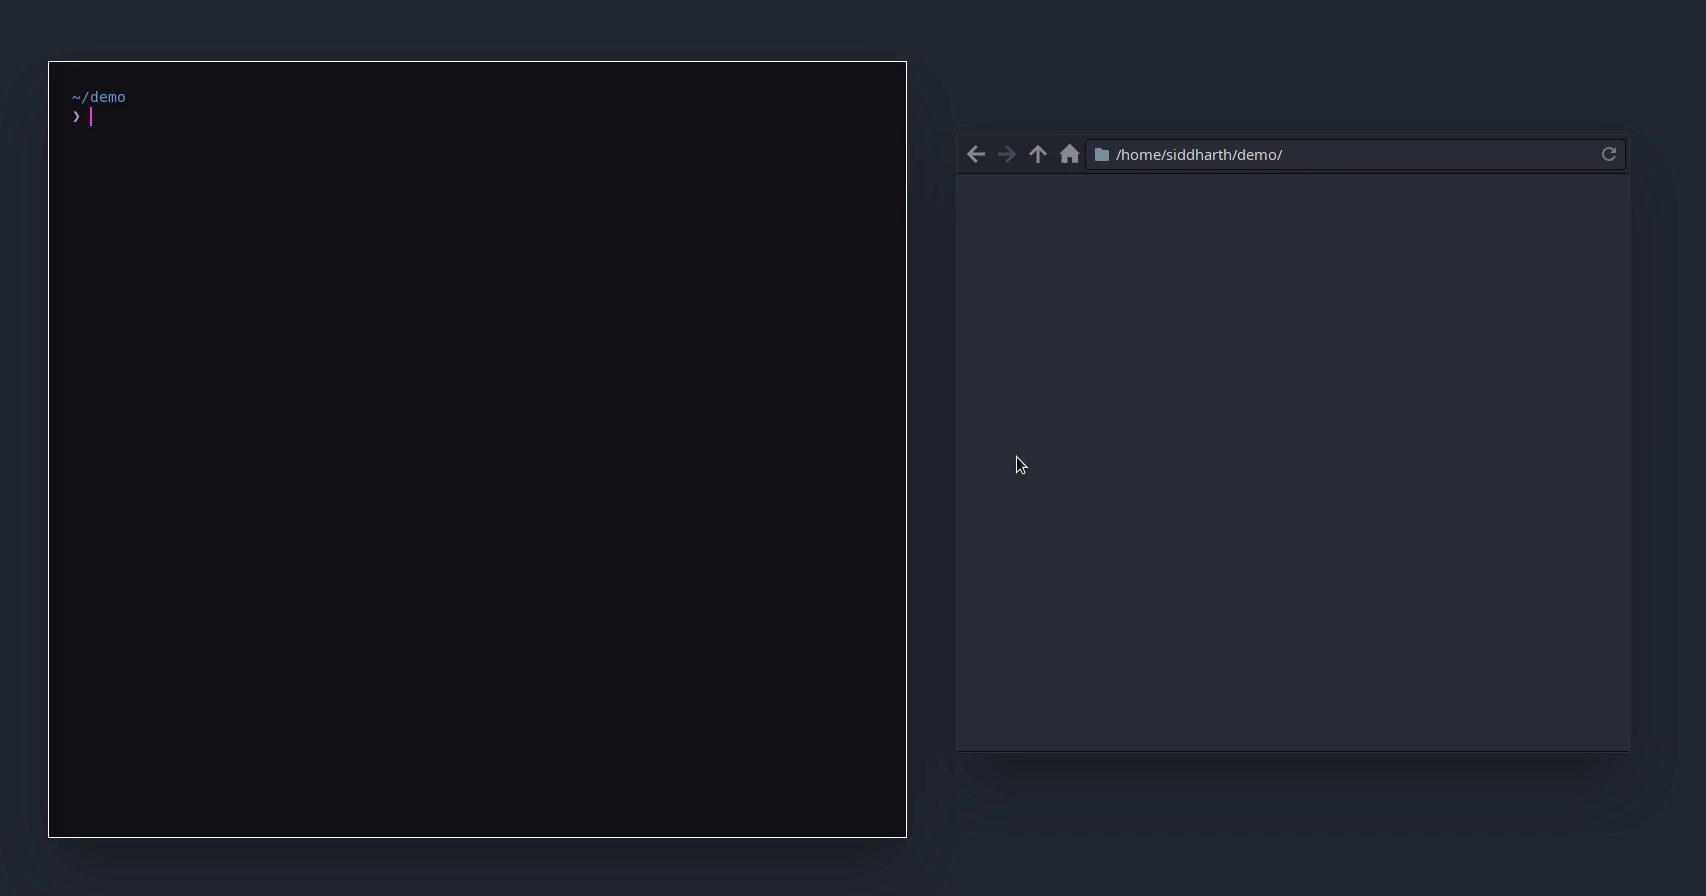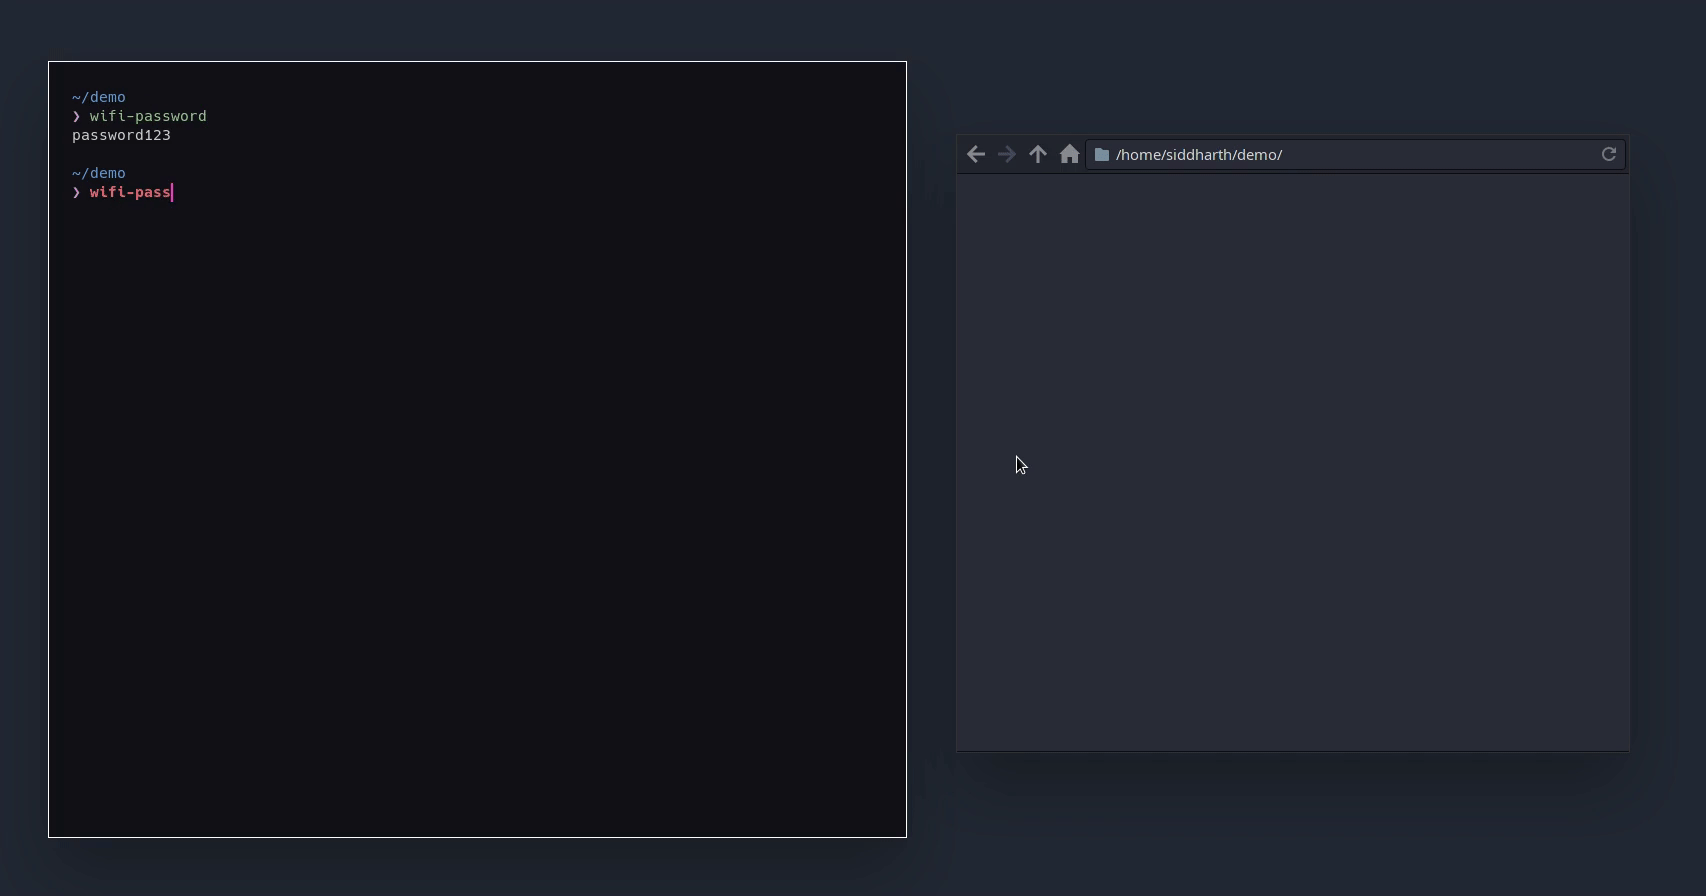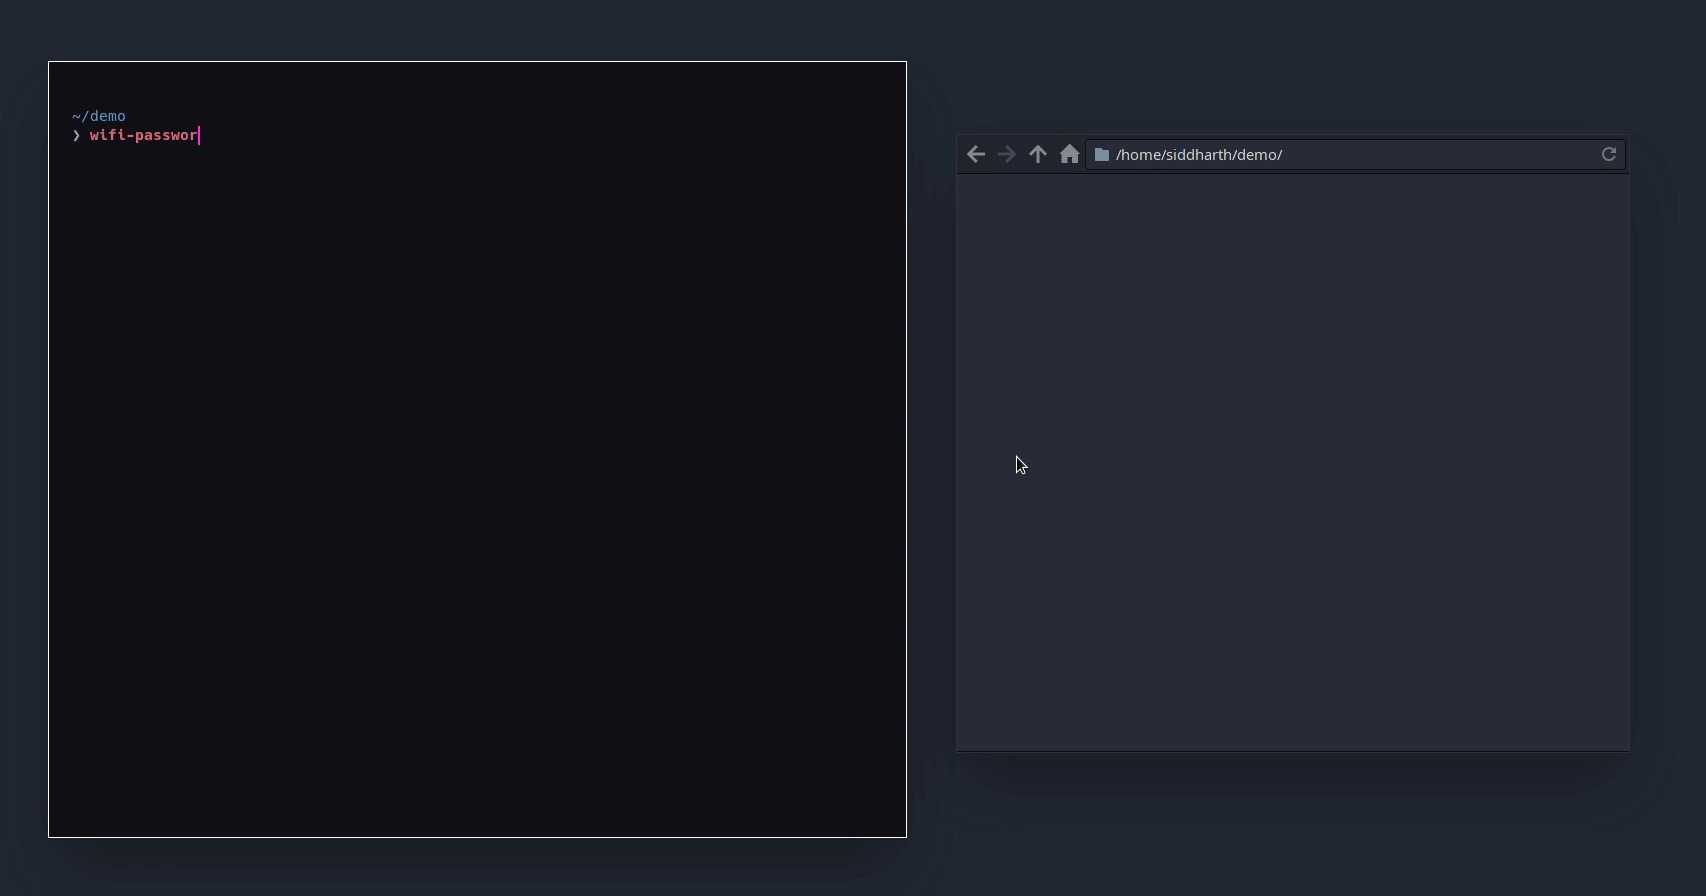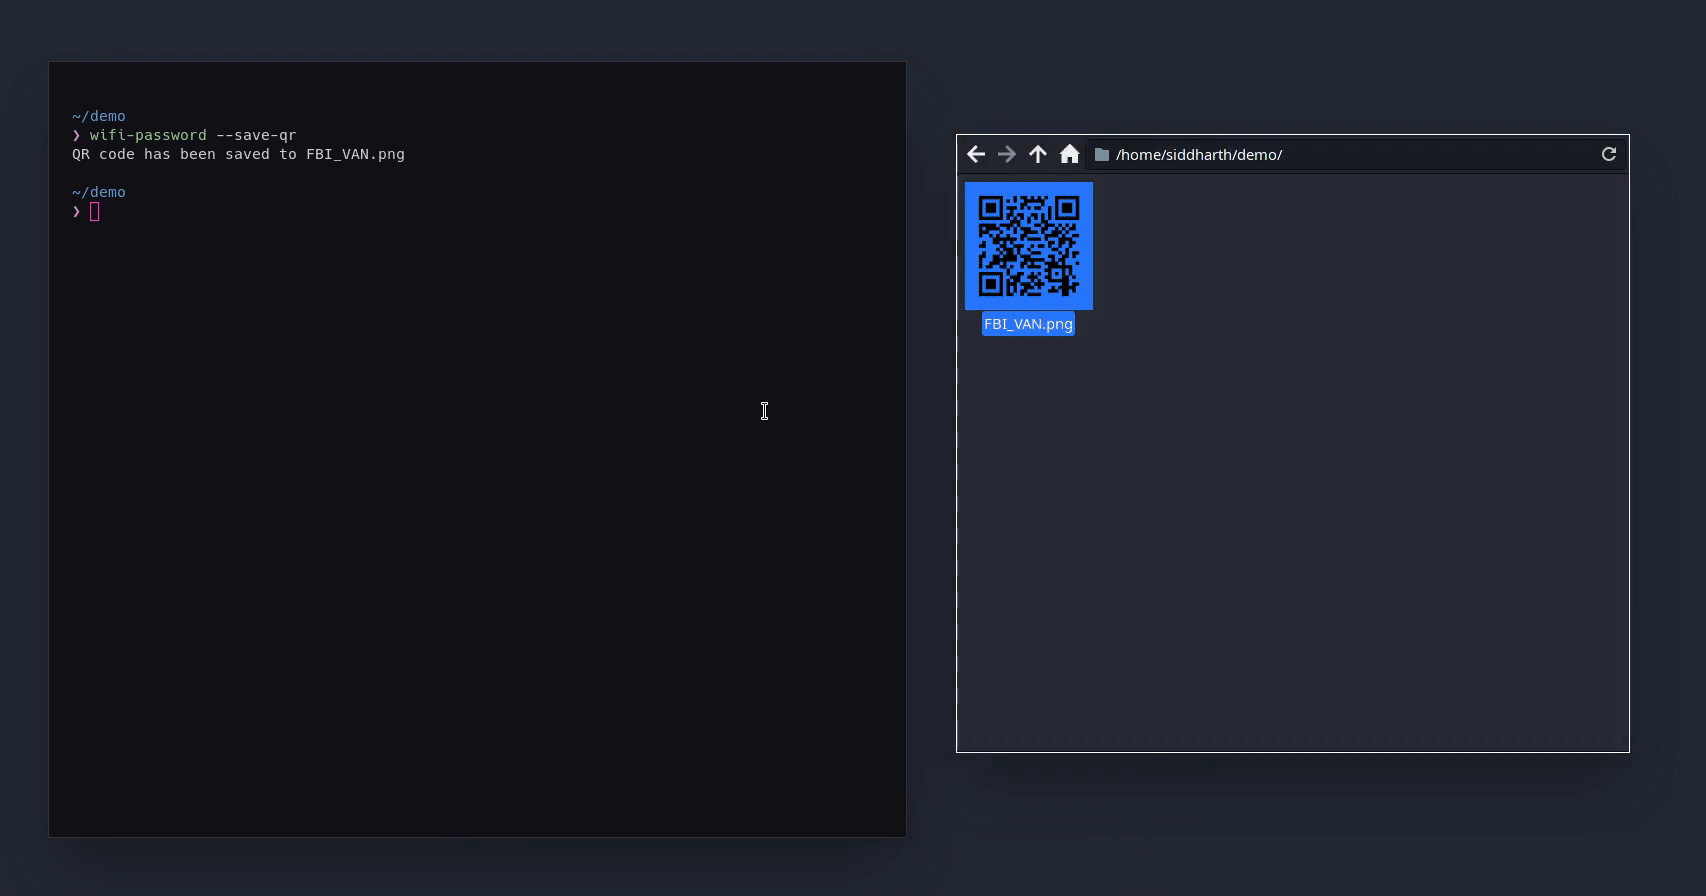 sdushantha/wifi-password
Quickly fetch your WiFi password and if needed, generate a QR code of your WiFi to allow phones to easily connect
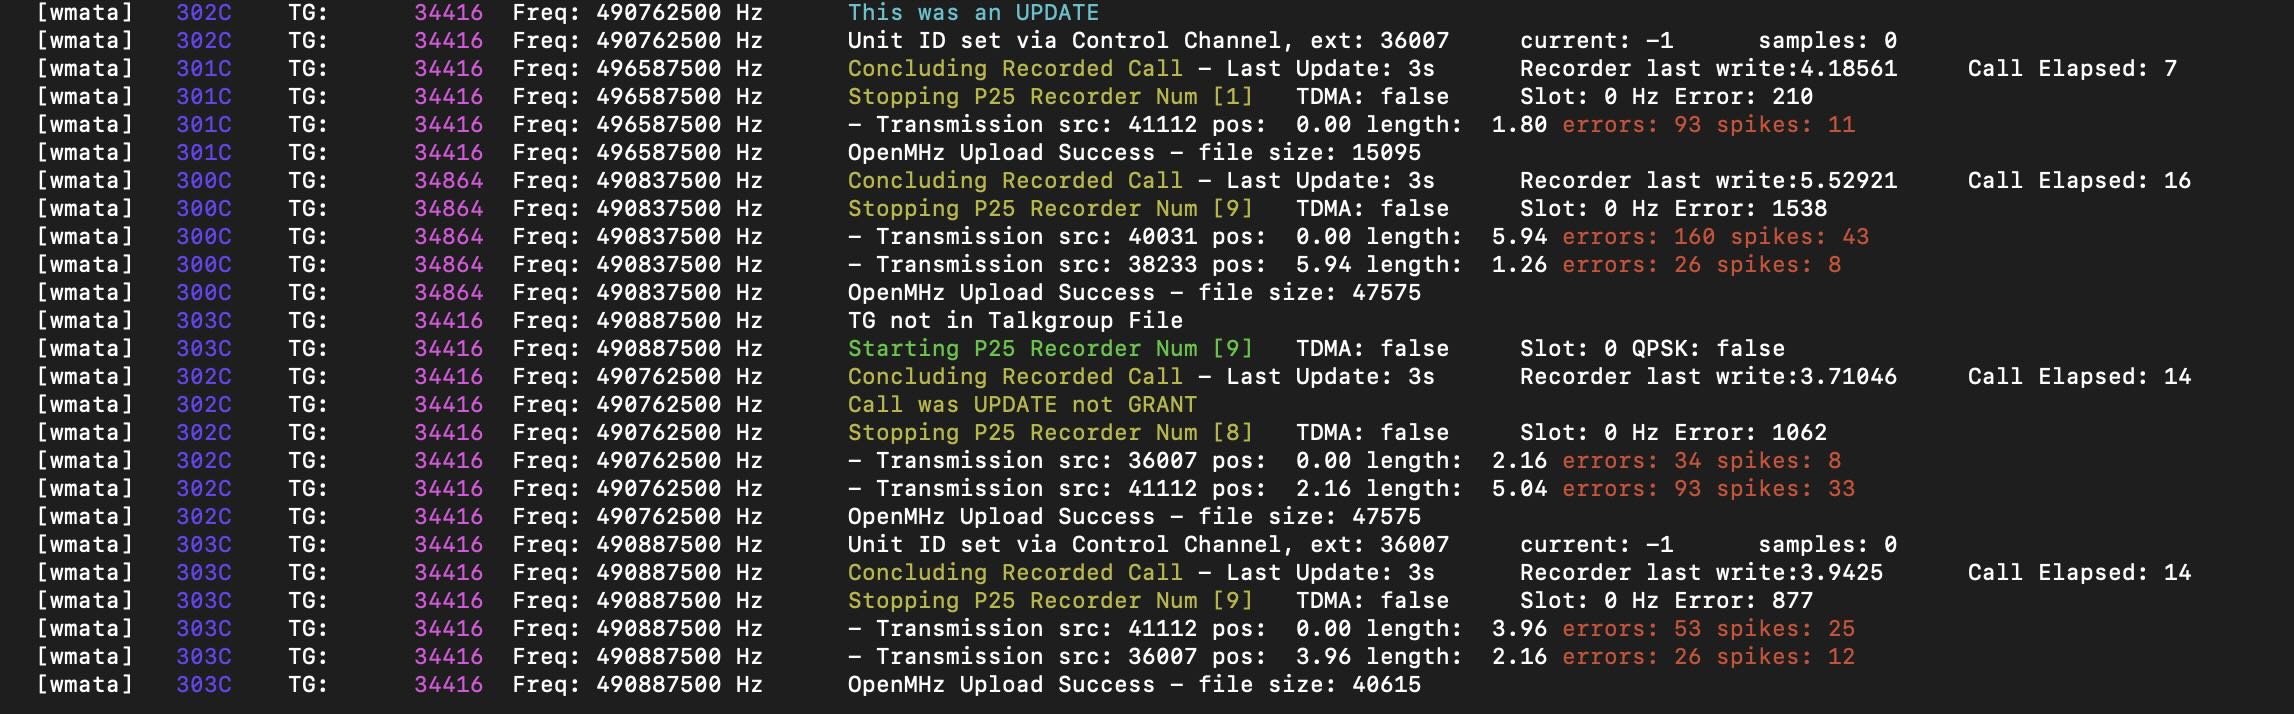 trunkrecorder/trunk-recorder
Records calls from a Trunked Radio System (P25 & SmartNet)
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
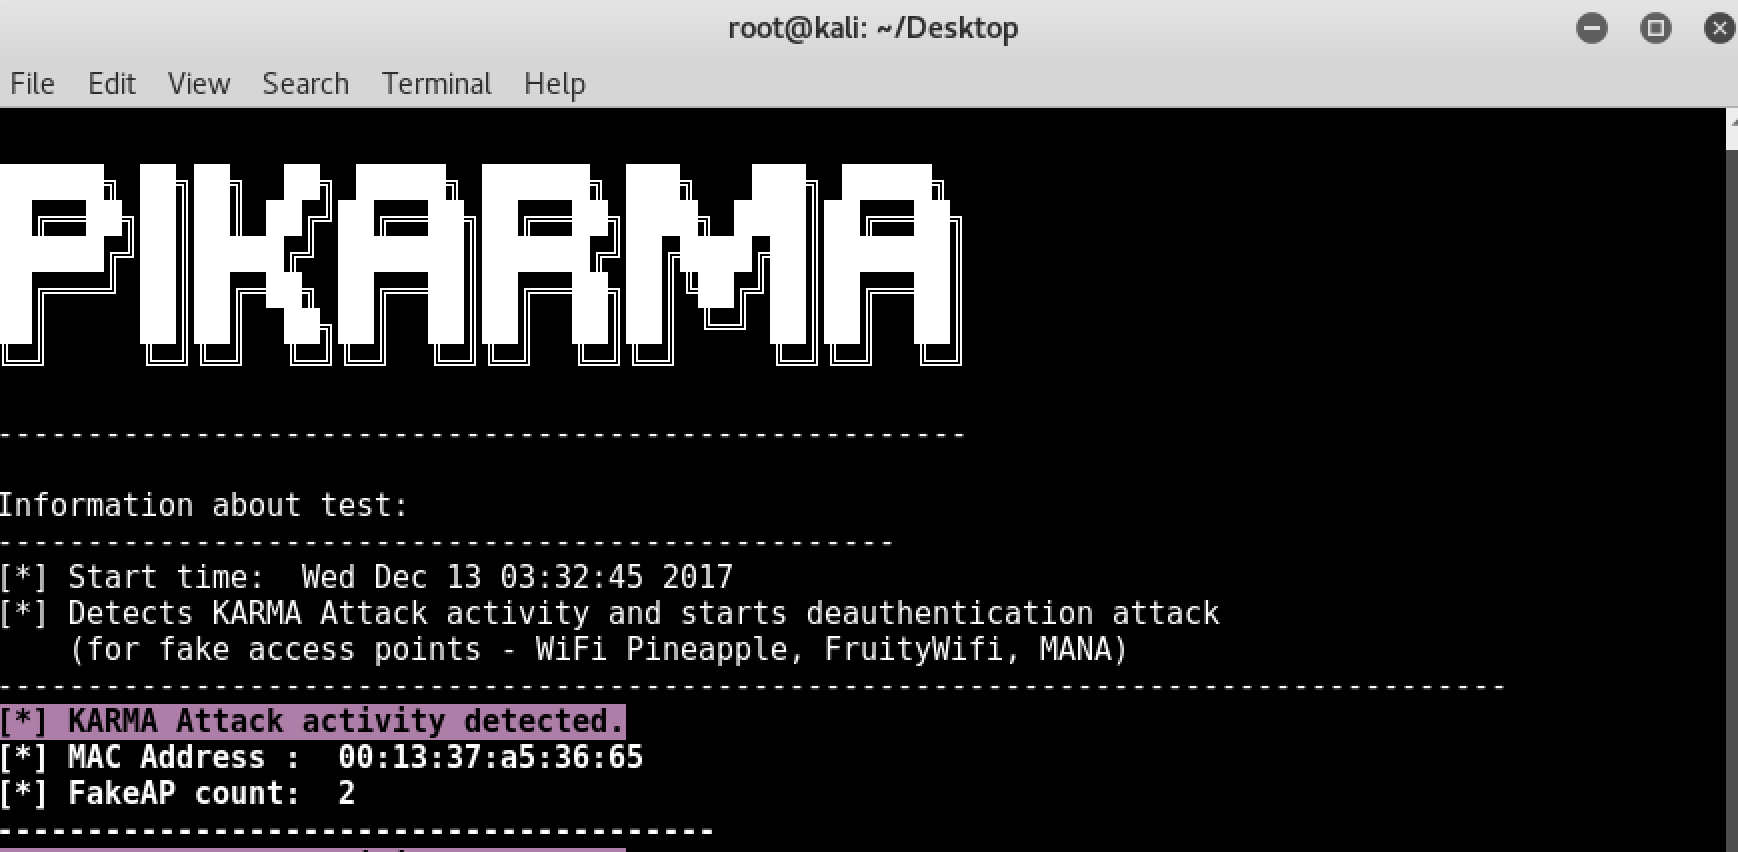 wipi-hunter/pikarma
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)
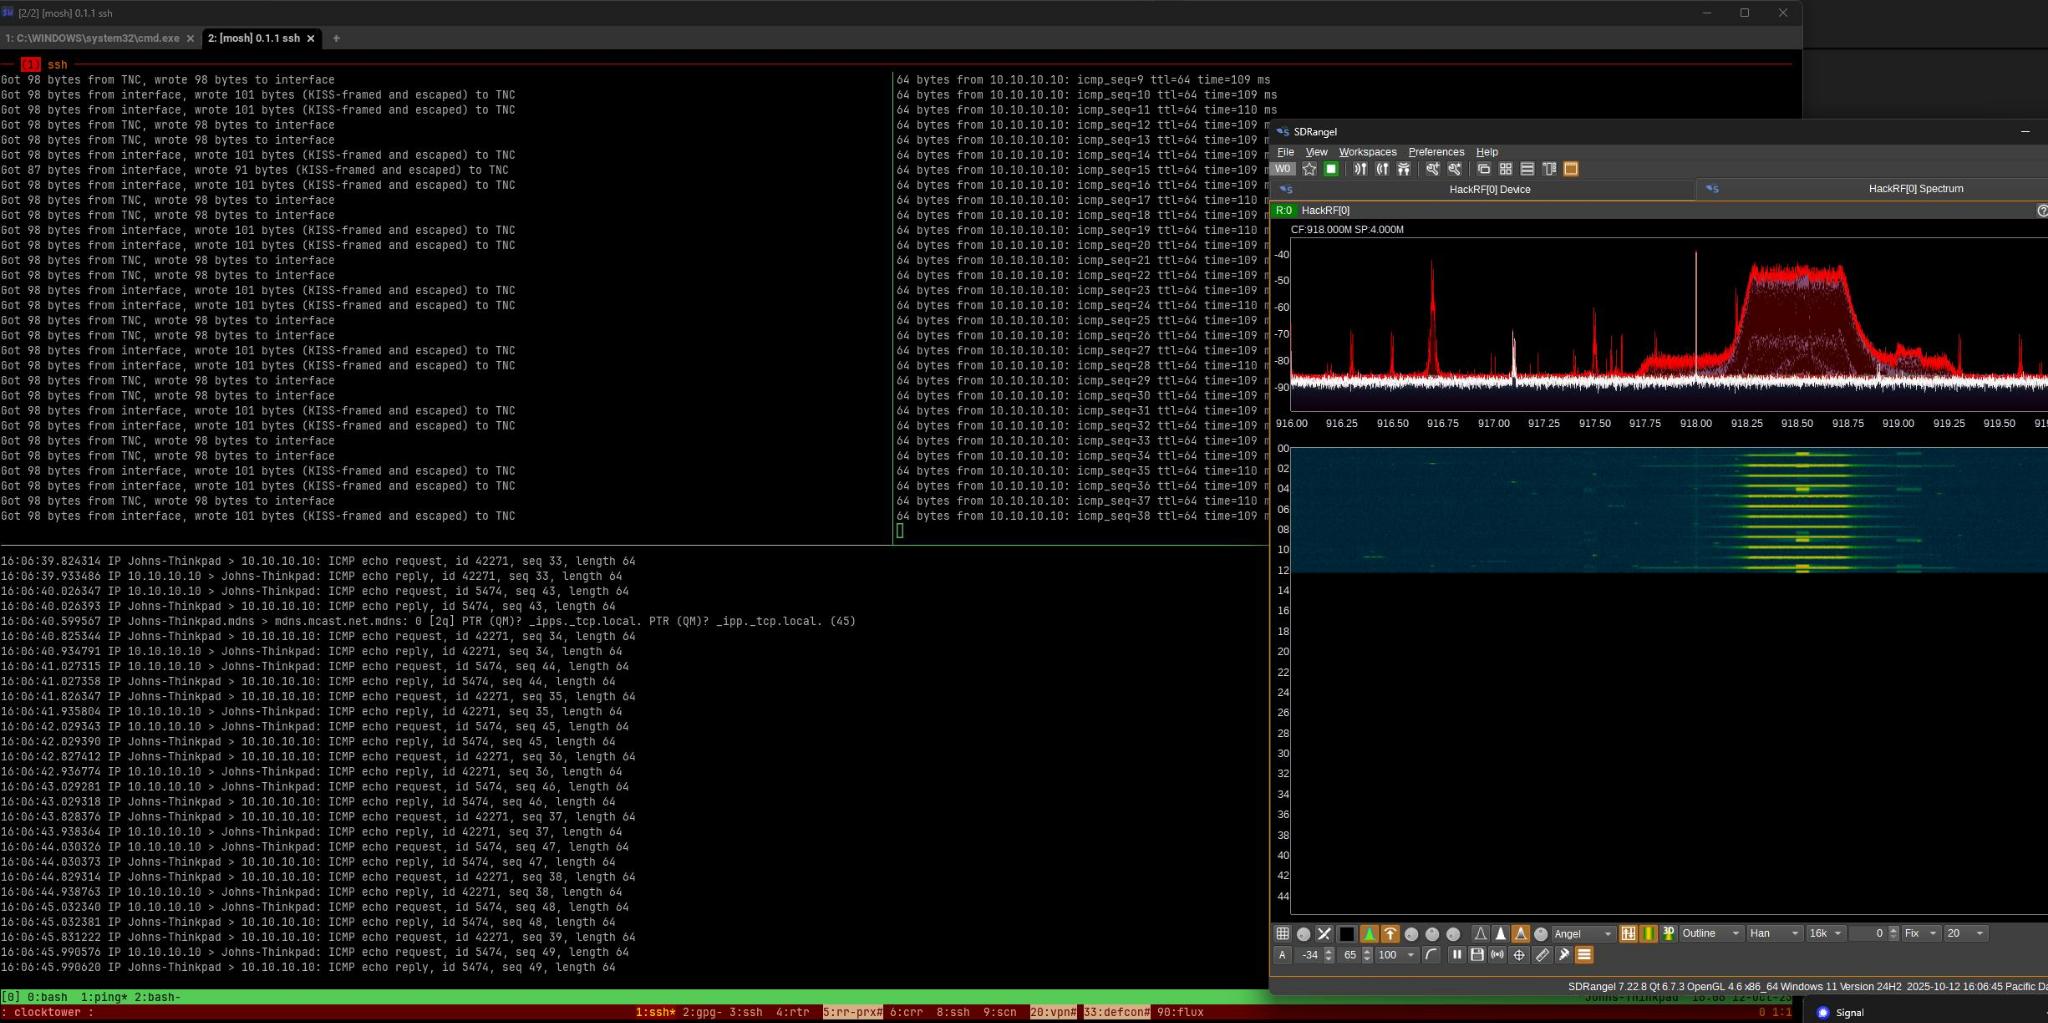 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 osqzss/bladegps
Real-time GPS signal simulator for bladeRF
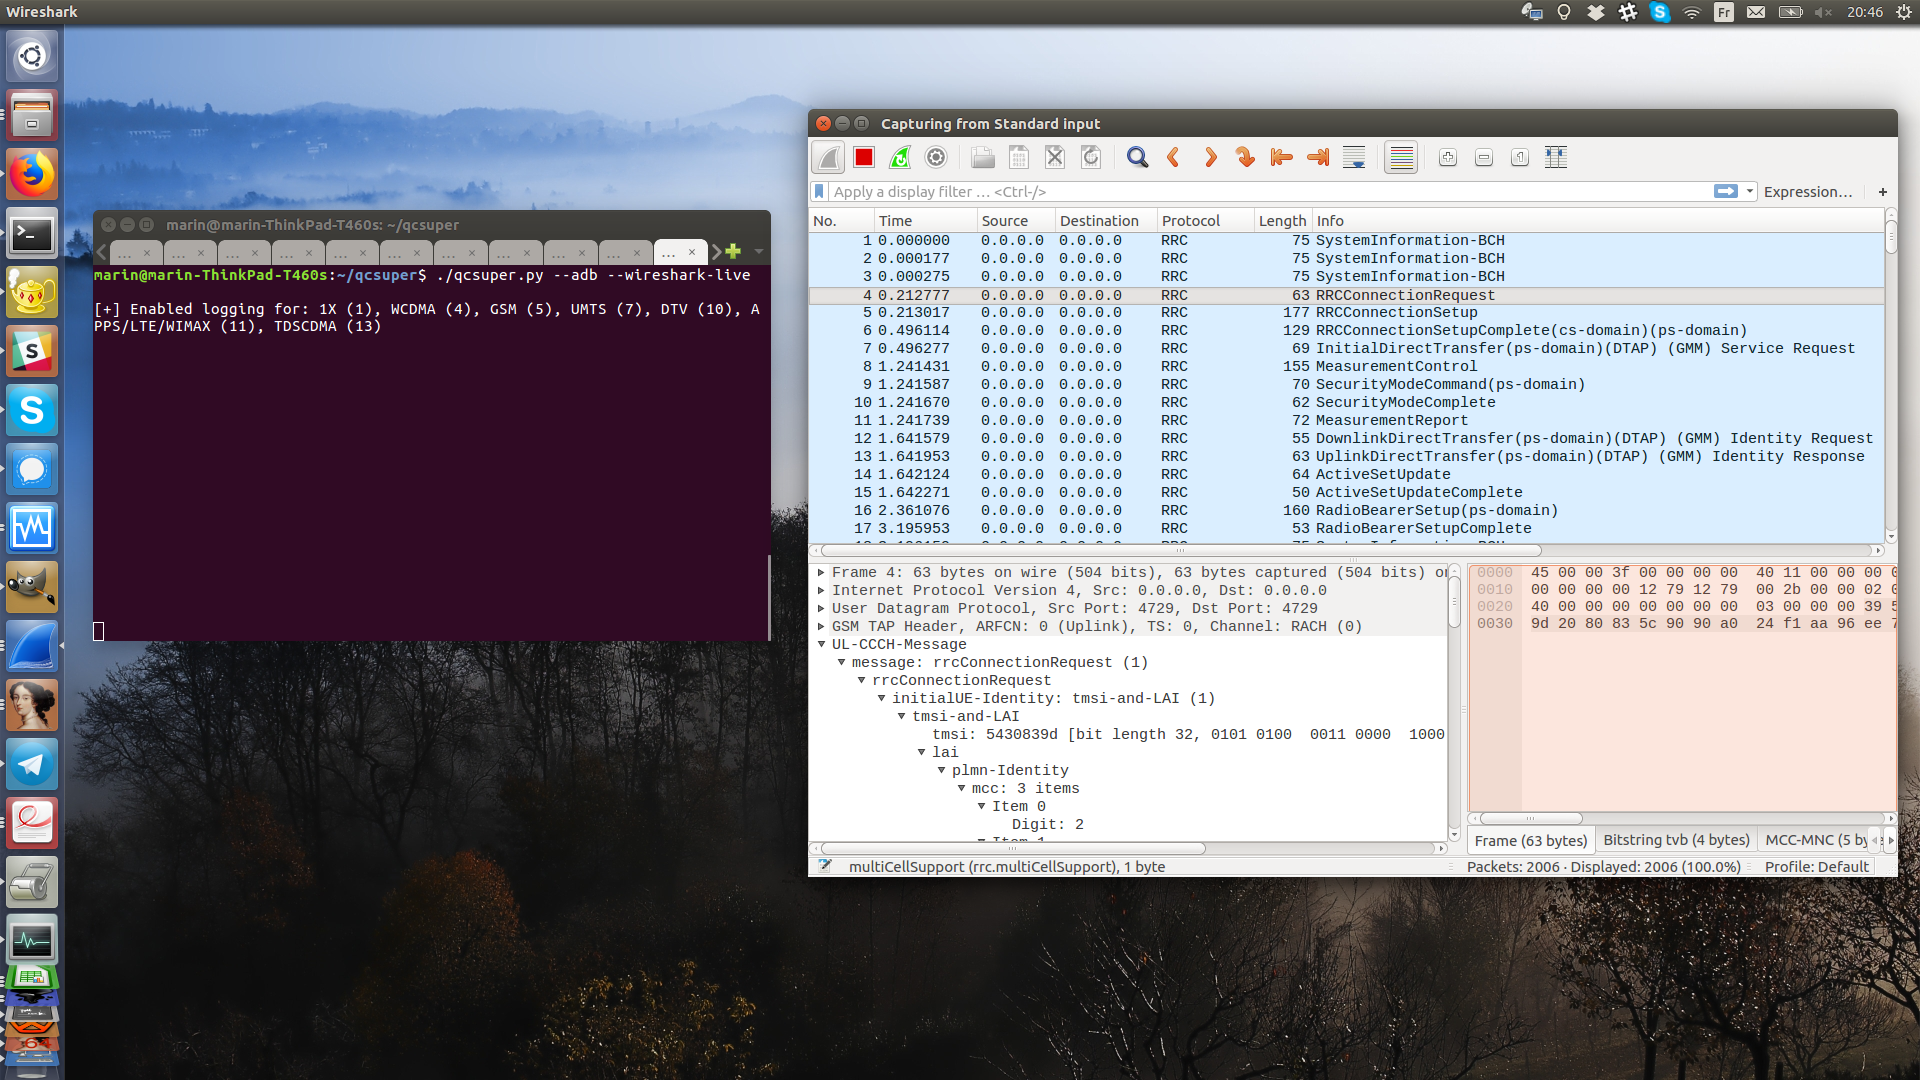 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32
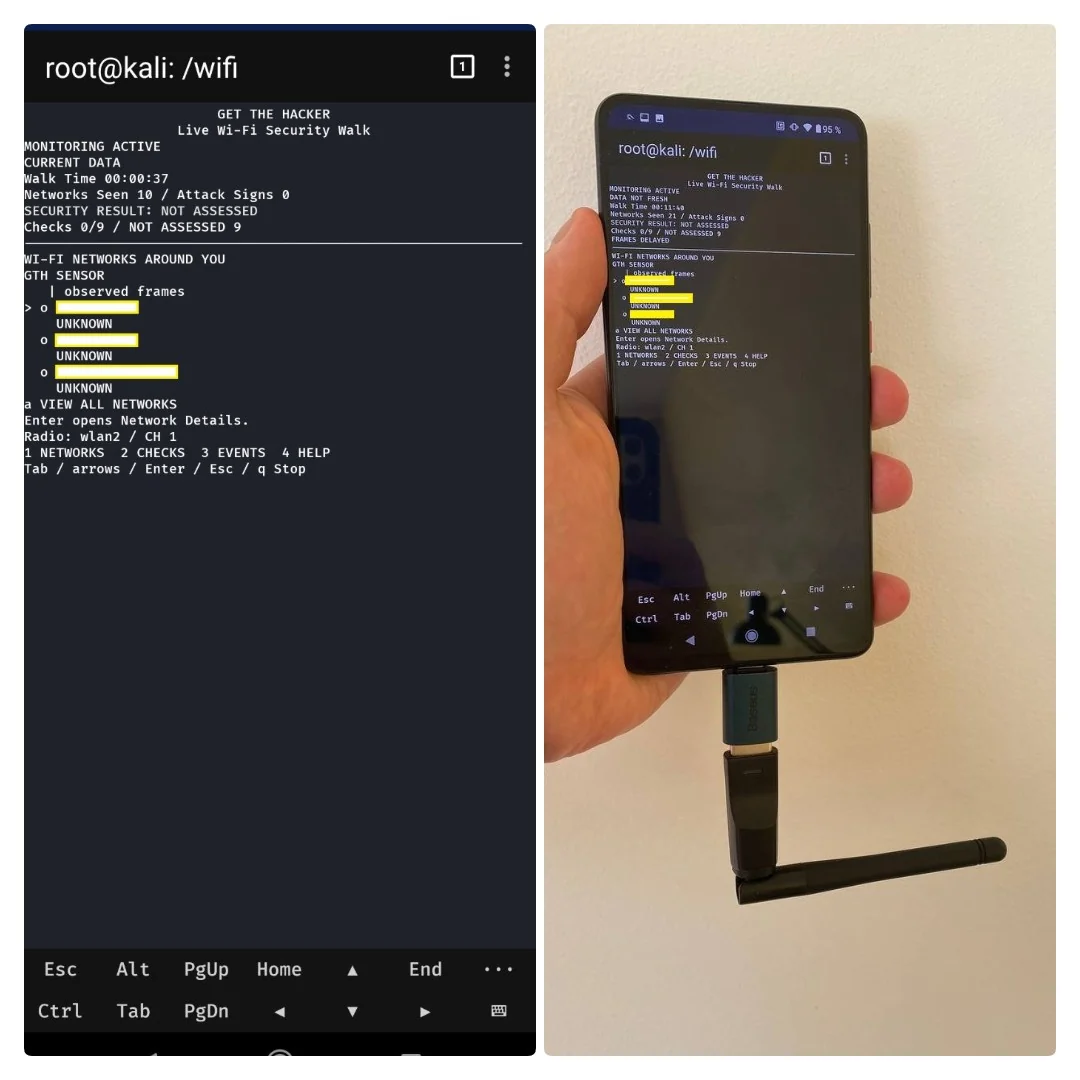 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
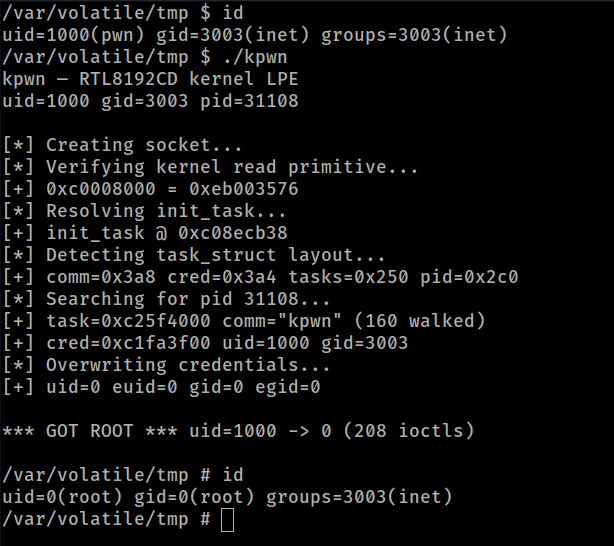 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls