

Evil_Twin_Attack
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
educationintrusion-detectionnetwork-security+5
yashubitra/evil_twin_attackRogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…

 manaswijaiswal/reproducing-connman-1.34
CVE-2017-12865 exploit
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0326
Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…
 web-logs2/hostapd_mirror
mirror of https://w1.fi/cgit/hostap/ till 30/01/2023 for CVE-2022-23303/4 - c22
 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 nanopathi/packages_wpa_supplicant8_cve-2021-0326
Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 amirasaiyad/ble-tpms
CVE-2024-39081. BLE TPMS data manipulation over bluetooth communication.
 lukejenkins/cve-2021-34767
Cisco IOS XE Software for Catalyst 9800 Series Wireless Controllers IPv6 Denial of Service Vulnerability
 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.
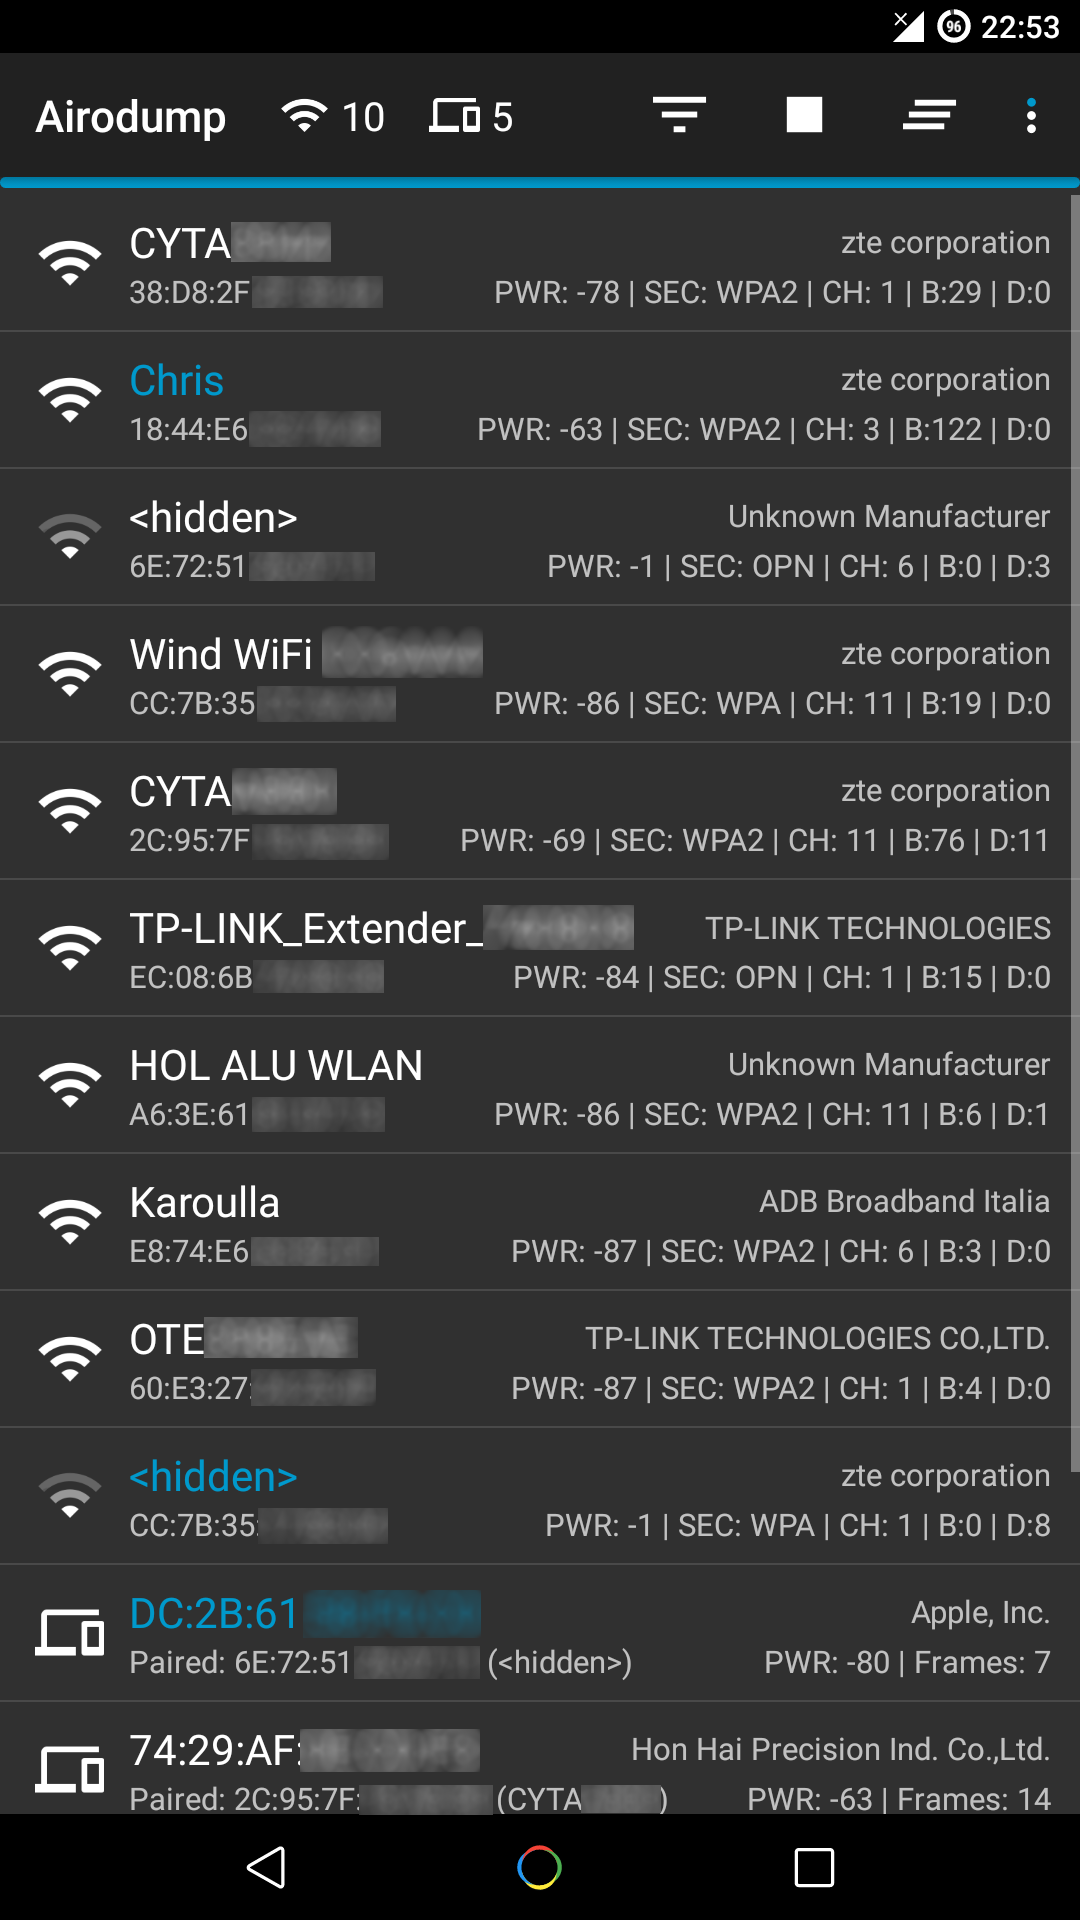 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
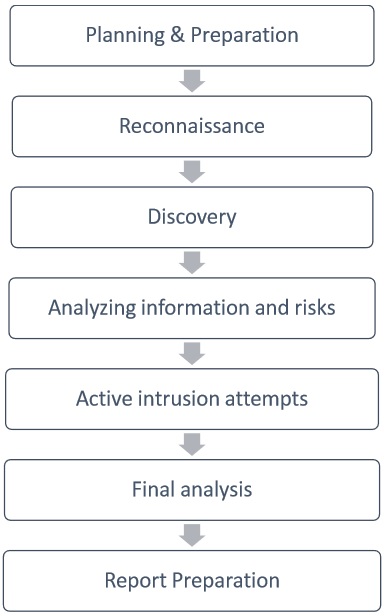 sundowndev/hacker-roadmap
A collection of hacking tools, resources and references to practice ethical hacking.
 xdavidhu/probesniffer
🔍 A tool for sniffing unencrypted wireless probe requests from devices.
 oblique/create_ap
[NOT MAINTAINED] This script creates a NATed or Bridged WiFi Access Point.
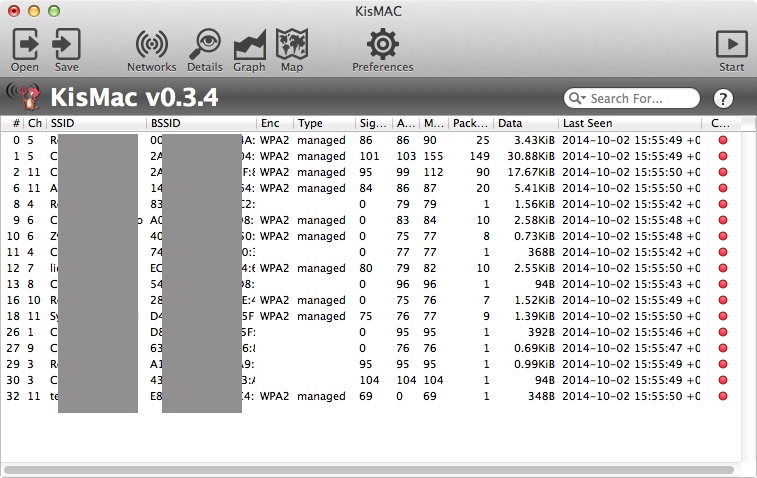 agnidia/kismac2
KisMAC is a free, open source wireless stumbling and security tool for Mac OS X.
 tmpertor/raven-storm
Python DDoS and stress-testing toolkit with L3/L4/L7, ARP, WiFi and Bluetooth attack modules plus a server mode for coordinating distributed attacks.