

Evil_Twin_Attack
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
educationintrusion-detectionnetwork-security+5
yashubitra/evil_twin_attackRogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
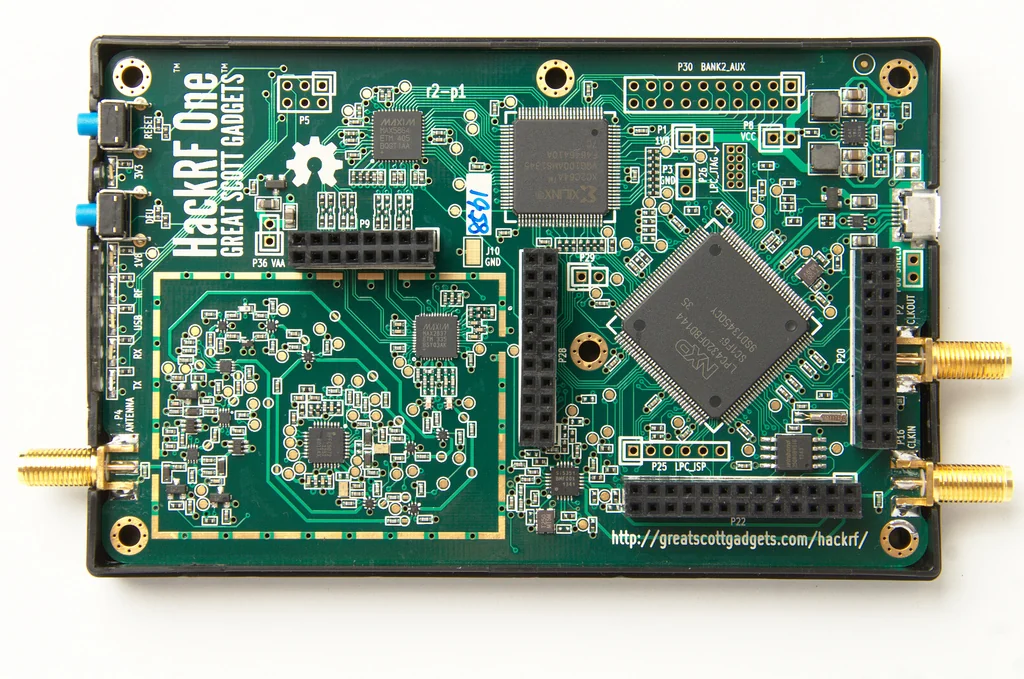 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 george0papasotiriou/cve-2026-11117-wpa2-4-way-handshake-reinstallation-krack-sim-
Python simulation of CVE-2026-11117 demonstrating WPA2 4-way handshake PTK reinstallation and nonce reuse to illustrate the KRACK attack.
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 martinmarinov/tempestsdr
Remote video eavesdropping using a software-defined radio platform
 rtlsdrblog/tempestsdr
Remote video eavesdropping using a software-defined radio platform
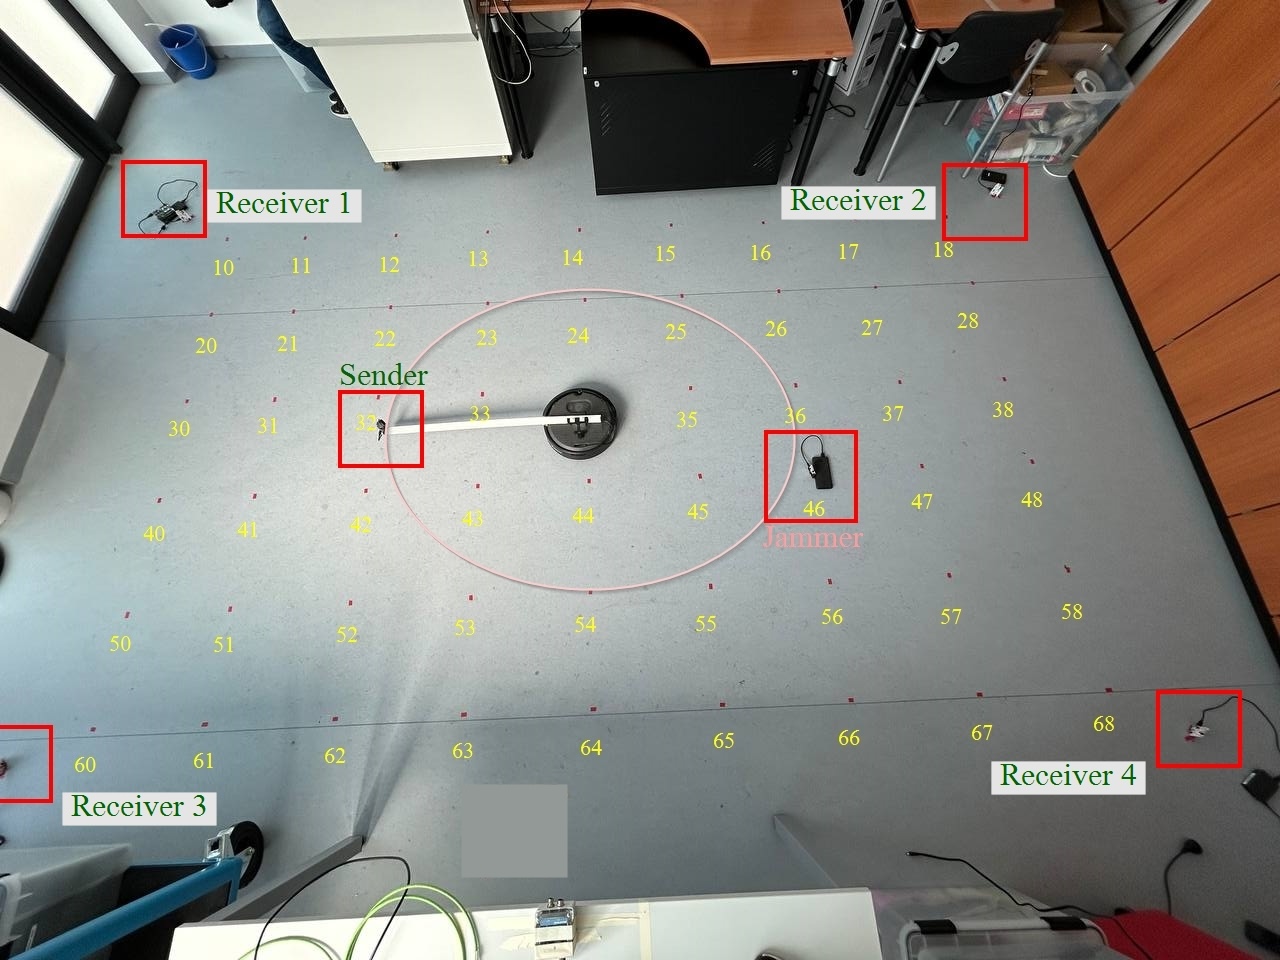 afbf4c8996f/jammer-loc
Implements machine and deep learning methods for indoor UWB jammer localization, including hyperparameter optimization, classification, and…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 eartoearoak/rtlsdr-scanner
A cross platform Python frequency scanning GUI for the OsmoSDR rtl-sdr library