

ESP32-DIV
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
bluetooth-securityeducationembedded-systems-security+8
3.7k
cifertech/esp32-divESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 cisc0-gif/kitt
Python-Based Pentesting Framework
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
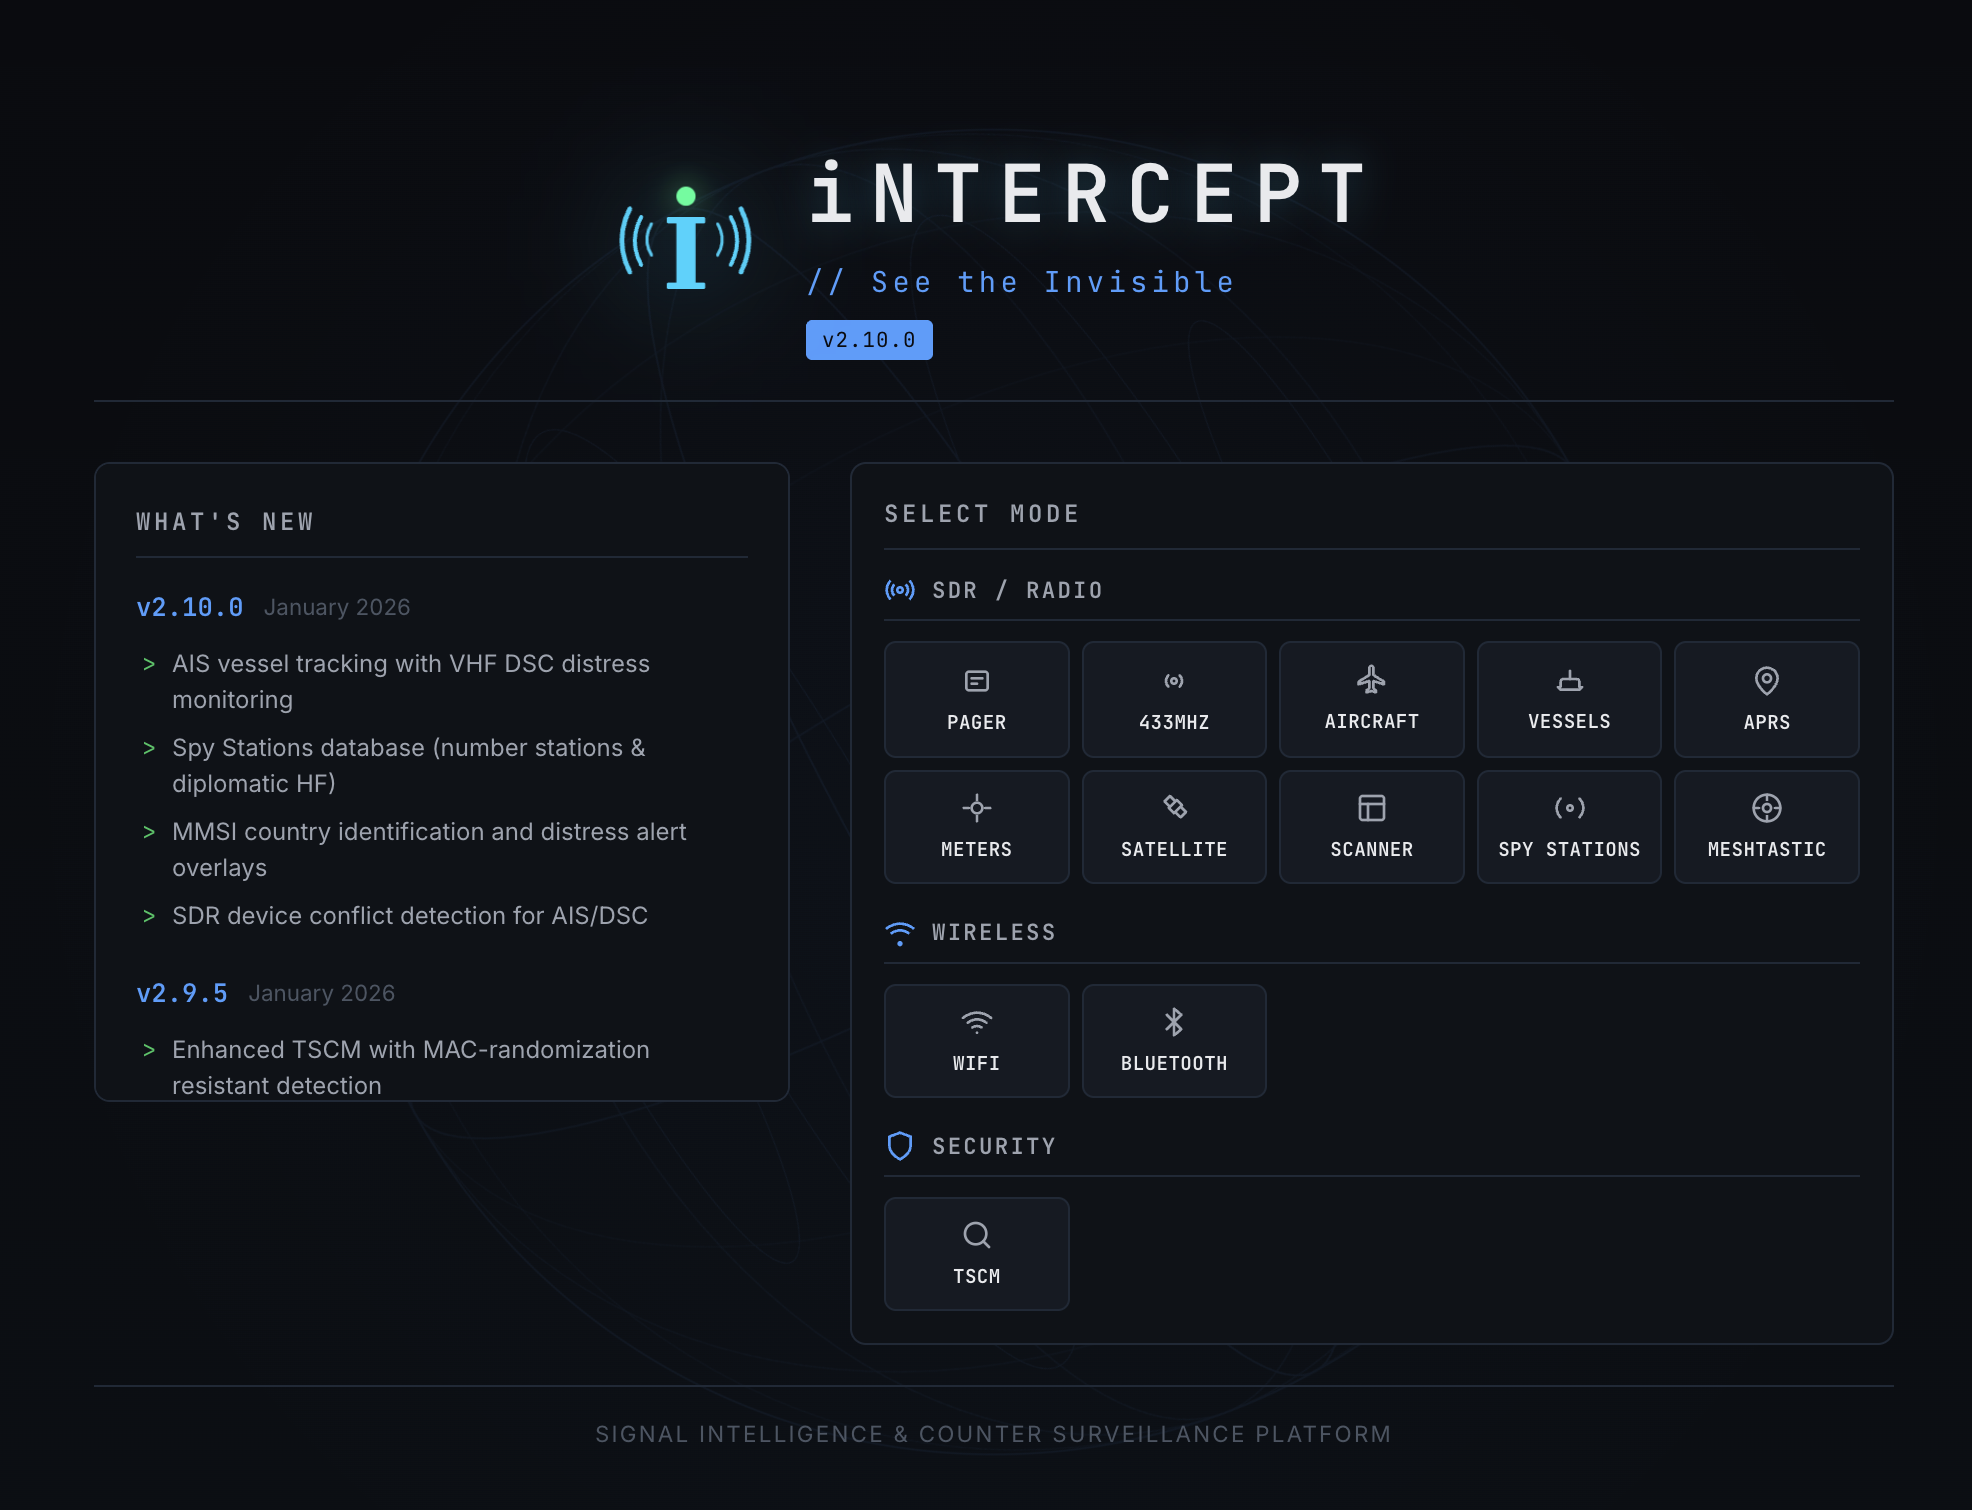 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
 rianhanft/marauderbox
A fork of the marauder firmware with Nyan box capabilities
 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 faizann24/wifi-bruteforcer-fsecurify
Android application to brute force WiFi passwords without requiring a rooted device.
 yashubitra/evil_twin_attack
Rogue access point attack and defense on Kali Linux: deauth with aireplay-ng, an airbase-ng evil twin with a captive portal, plus real-time…
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
 morpheuslord/winfihack
A windows Wifi Brute forcing utility which is an extremely old method but still works without the requirement of external dependencies.
 pulkin/esp8266-injection-example
Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 wipi-hunter/pifinger
📡🔍Searches for wifi-pineapple traces and calculate wireless network security score 🍍
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 marcrowproject/bramble
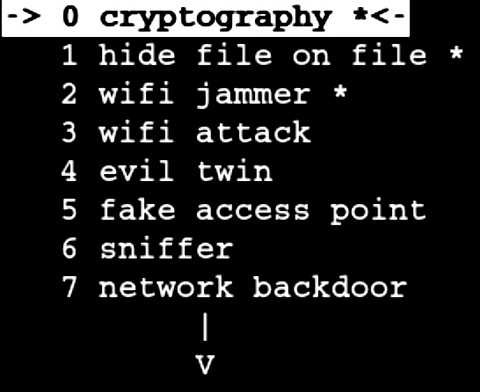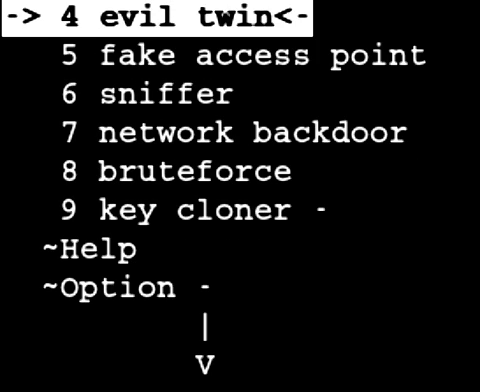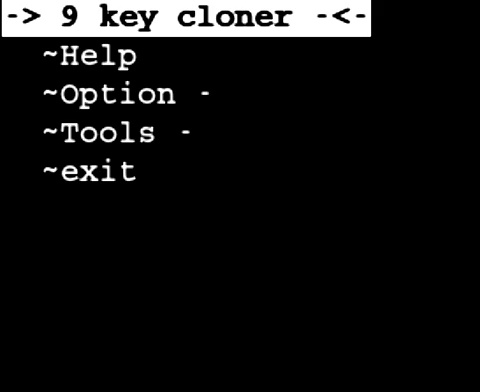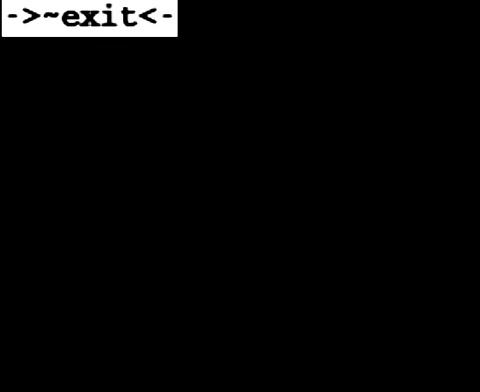
Bramble is a hacking Open source suite.