
traxss
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
penetration-testingvulnerability-analysisweb-security+1
1827 years ago
m4cs/traxsstraxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
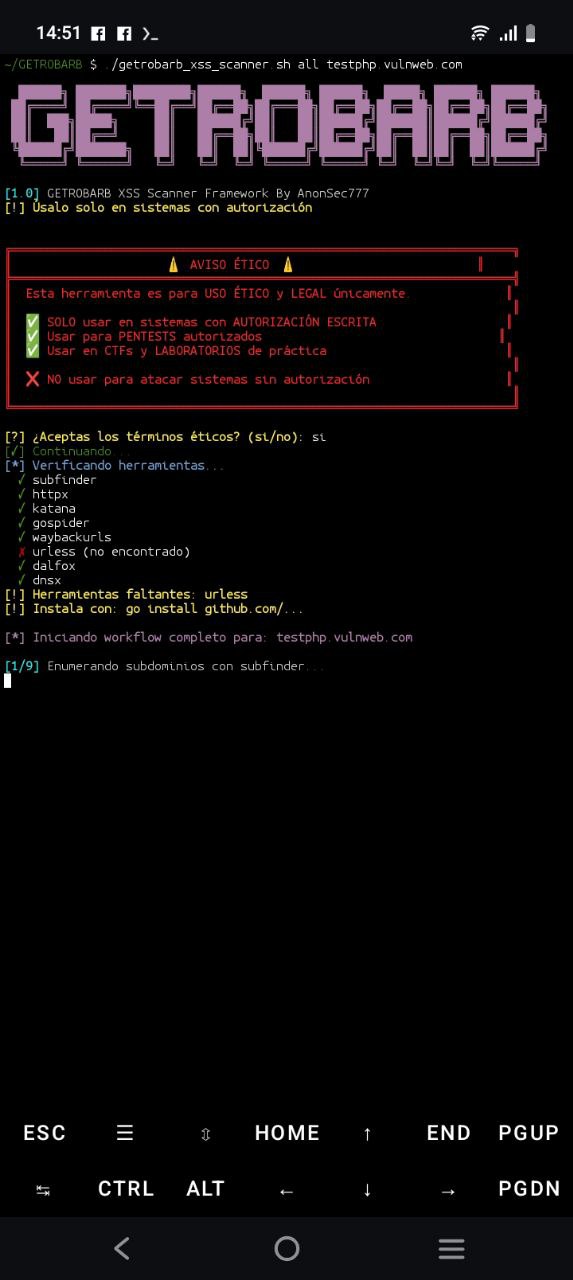 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
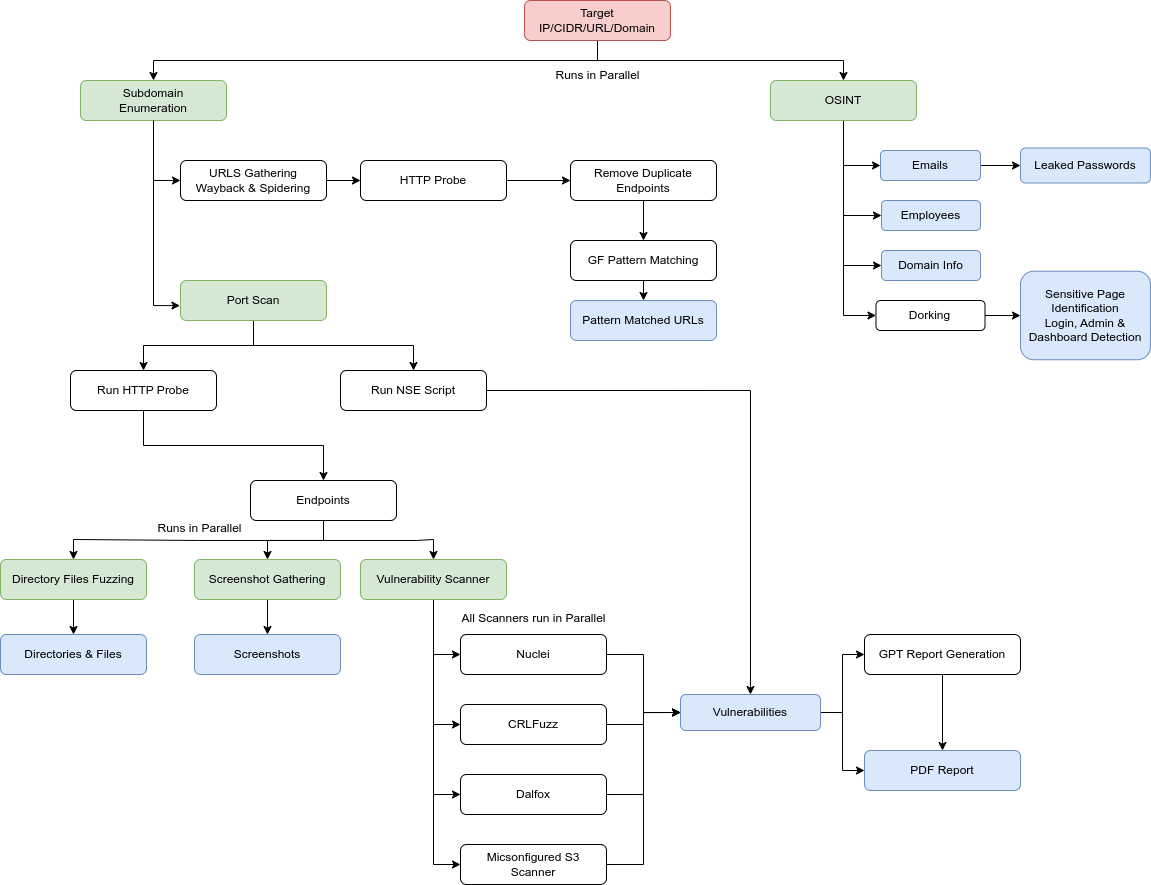 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
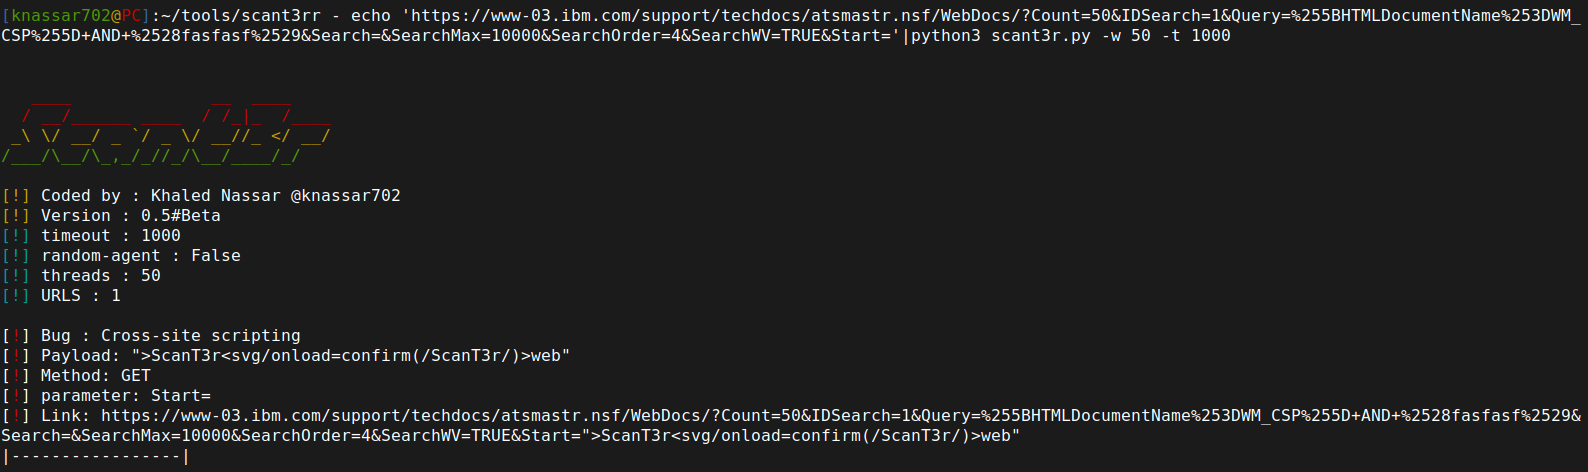 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 shenril/sitadel
Web Application Security Scanner
 jenderal92/cve-2026-49049
Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…
 projectdiscovery/katana
A next-generation crawling and spidering framework.
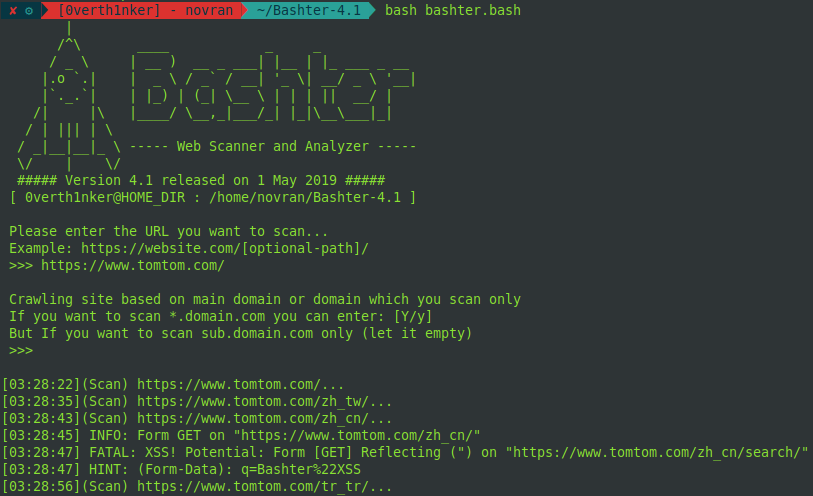 zerobyte-id/bashter
Web Vulnerability Scanner using Shell Script
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 arachni/arachni
Web Application Security Scanner Framework
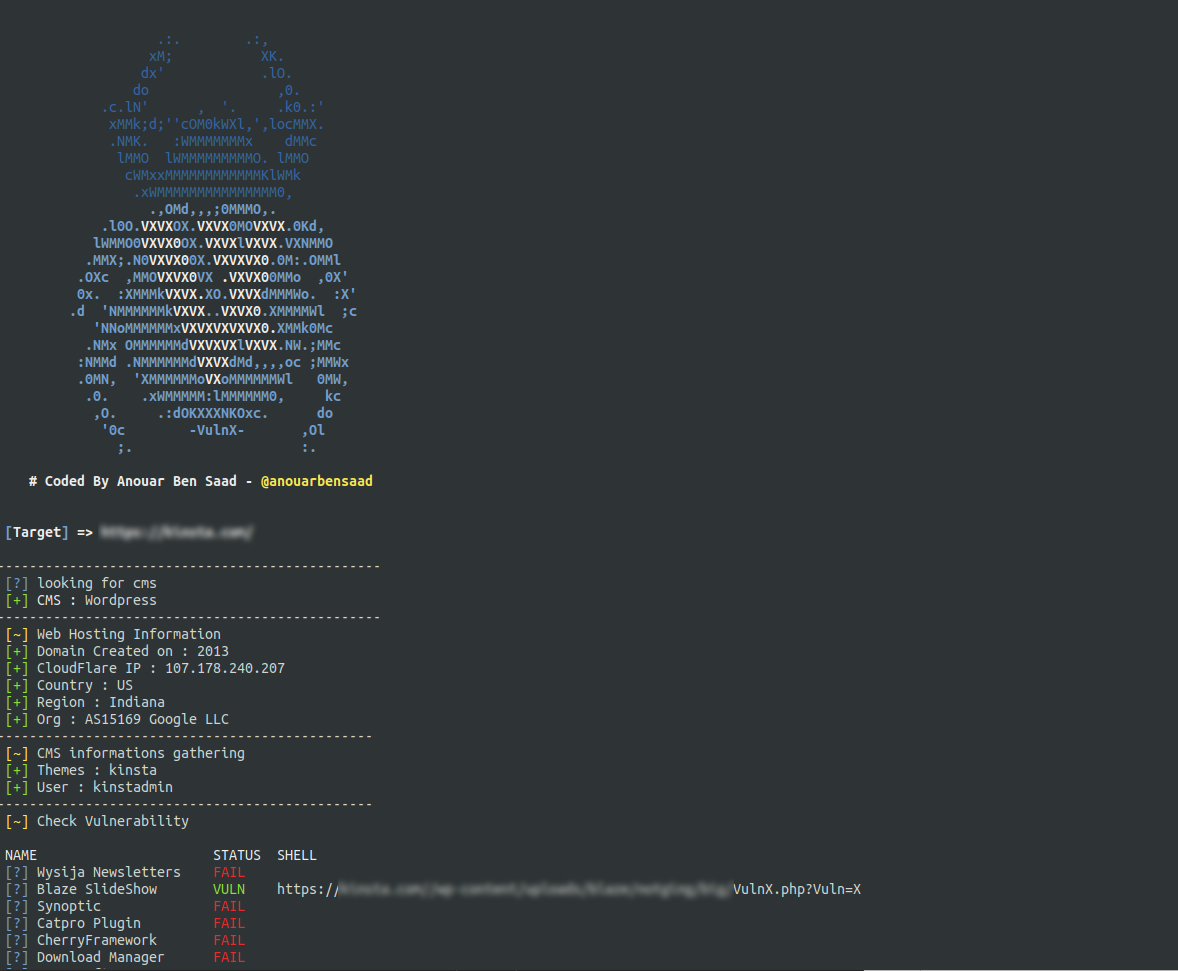 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
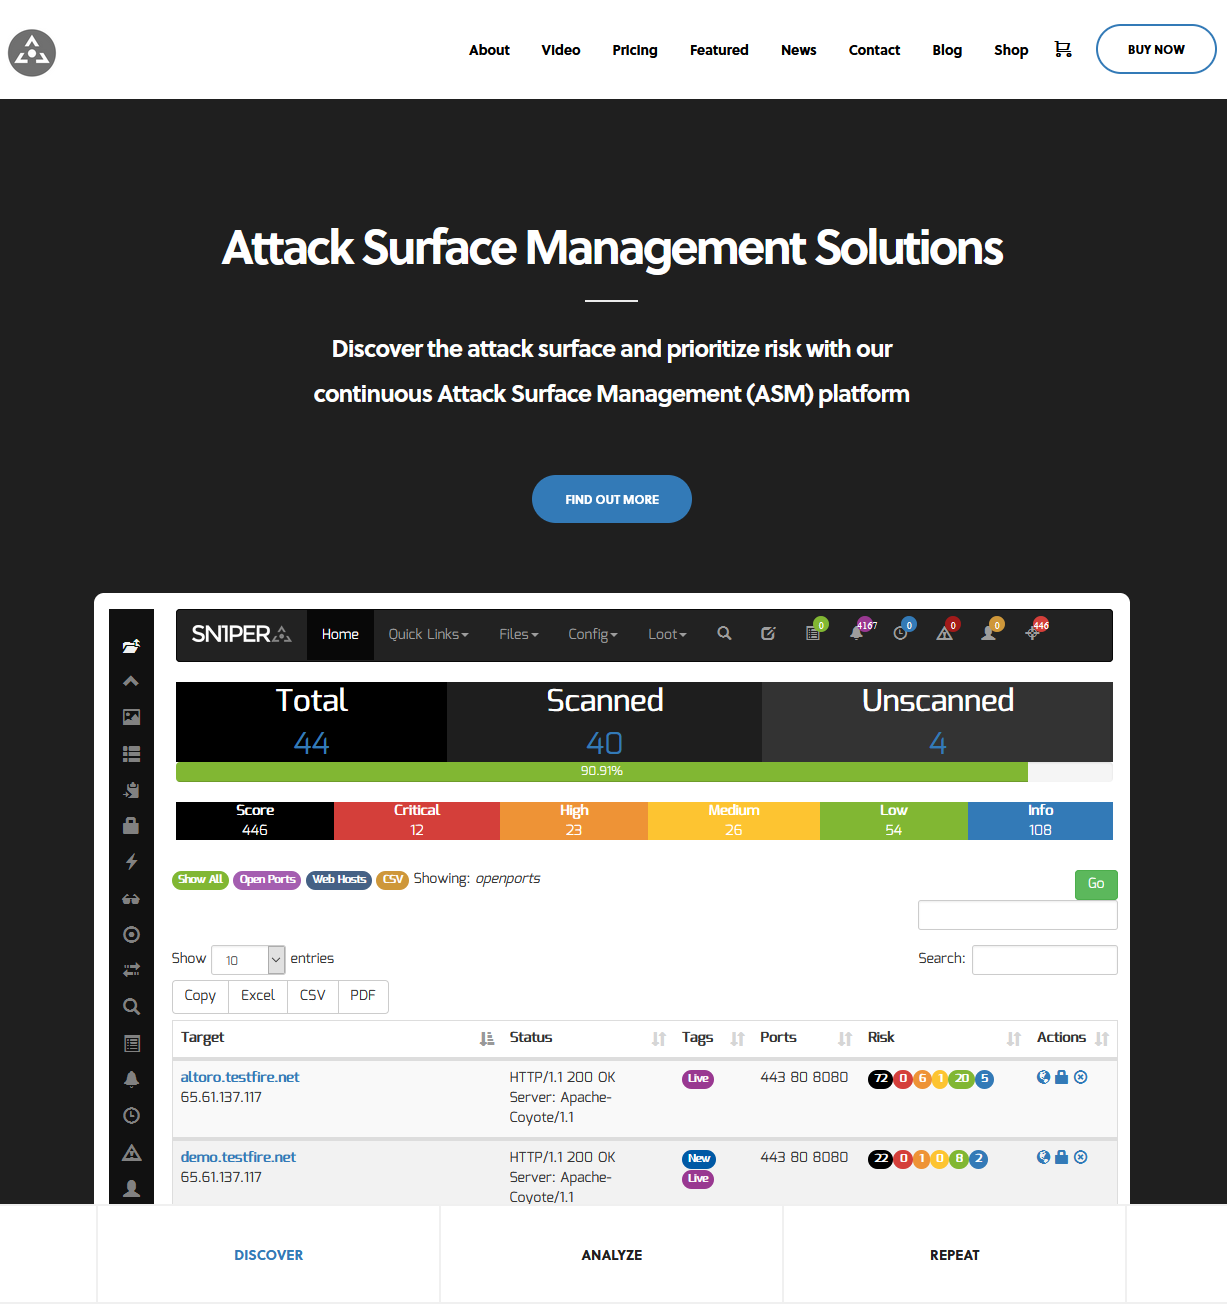 1n3/attacksurfacemanagement
Discover the attack surface and prioritize risks with our continuous Attack Surface Management (ASM) platform - Sn1per Professional #pentest #redteam…
 flyingllama87/p4wned
Perforce security research and tools - CVE-2026-6043
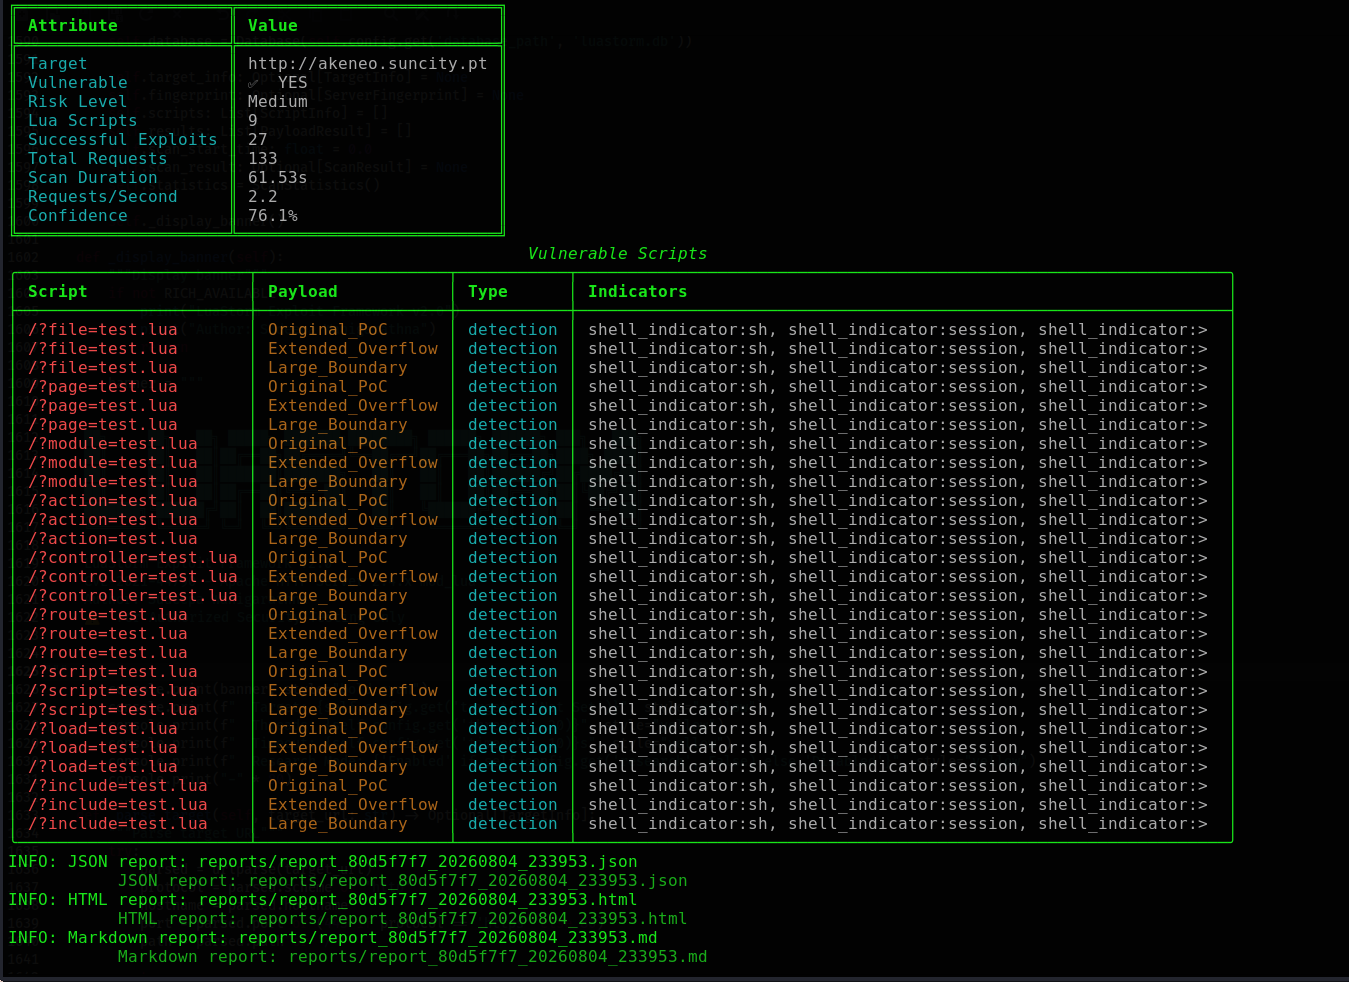 cerberusmrxi/apache-lua-buffer-overflow-exploit-cve-2021-44790
Apache HTTP Server 2.4.x mod_lua Buffer Overflow (CVE-2021-44790) - Advanced exploitation framework with fingerprinting, multi-stage scanning, plugin…
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.