
detectXSSlib
 gwroblew/detectxsslib
C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
code-analysispenetration-testingstatic-analysis+3
31
gwroblew/detectxsslibC++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
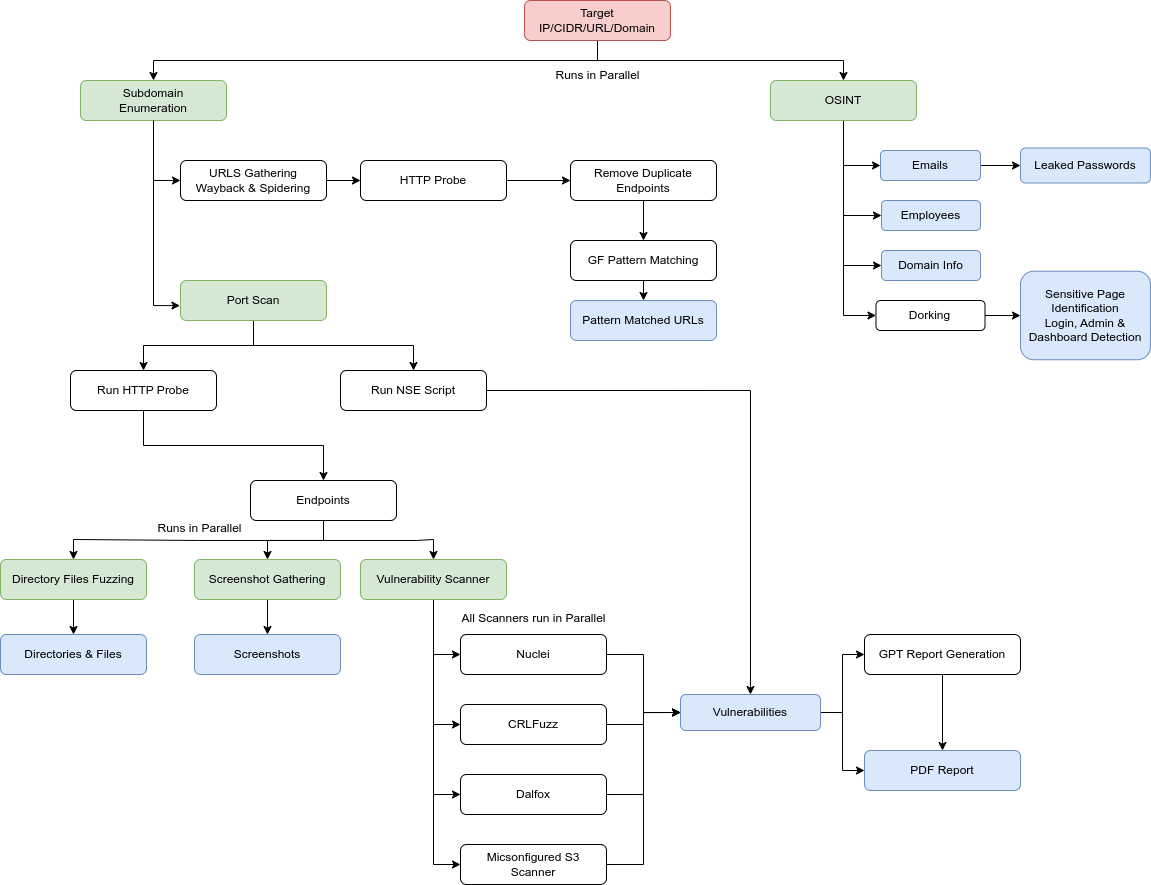 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 tomnomnom/gf
A wrapper around grep, to help you grep for things
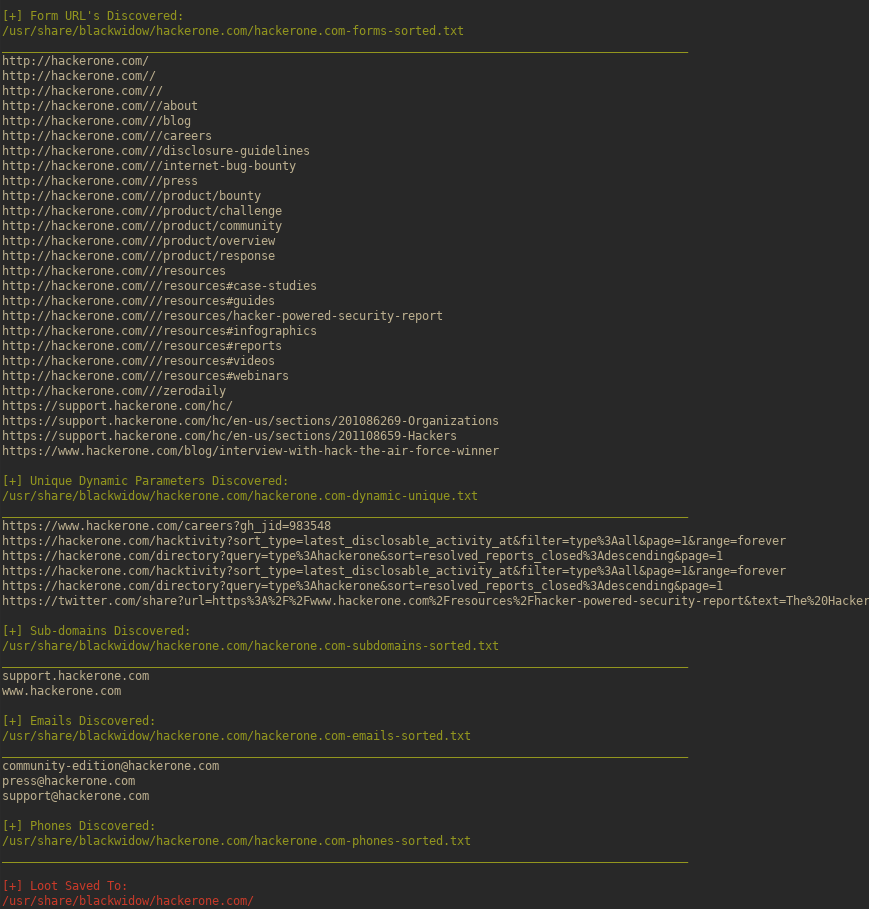 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
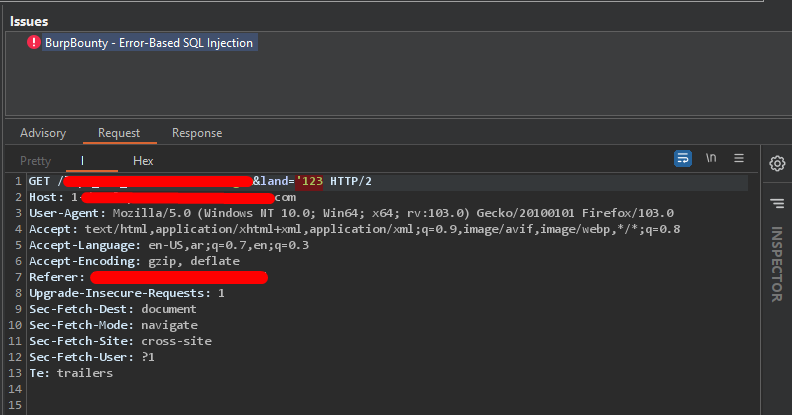 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
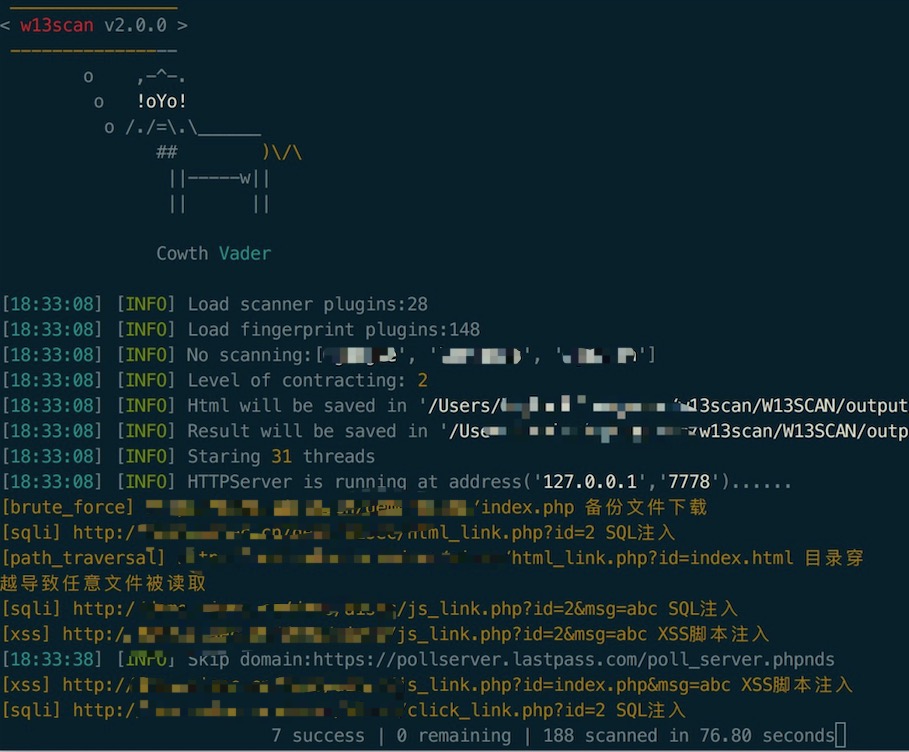 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…