
goWAPT
 dzonerzy/gowapt
Go Web Application Penetration Test
fuzzingpenetration-testingscripting-automation+4
dzonerzy/gowaptGo Web Application Penetration Test
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
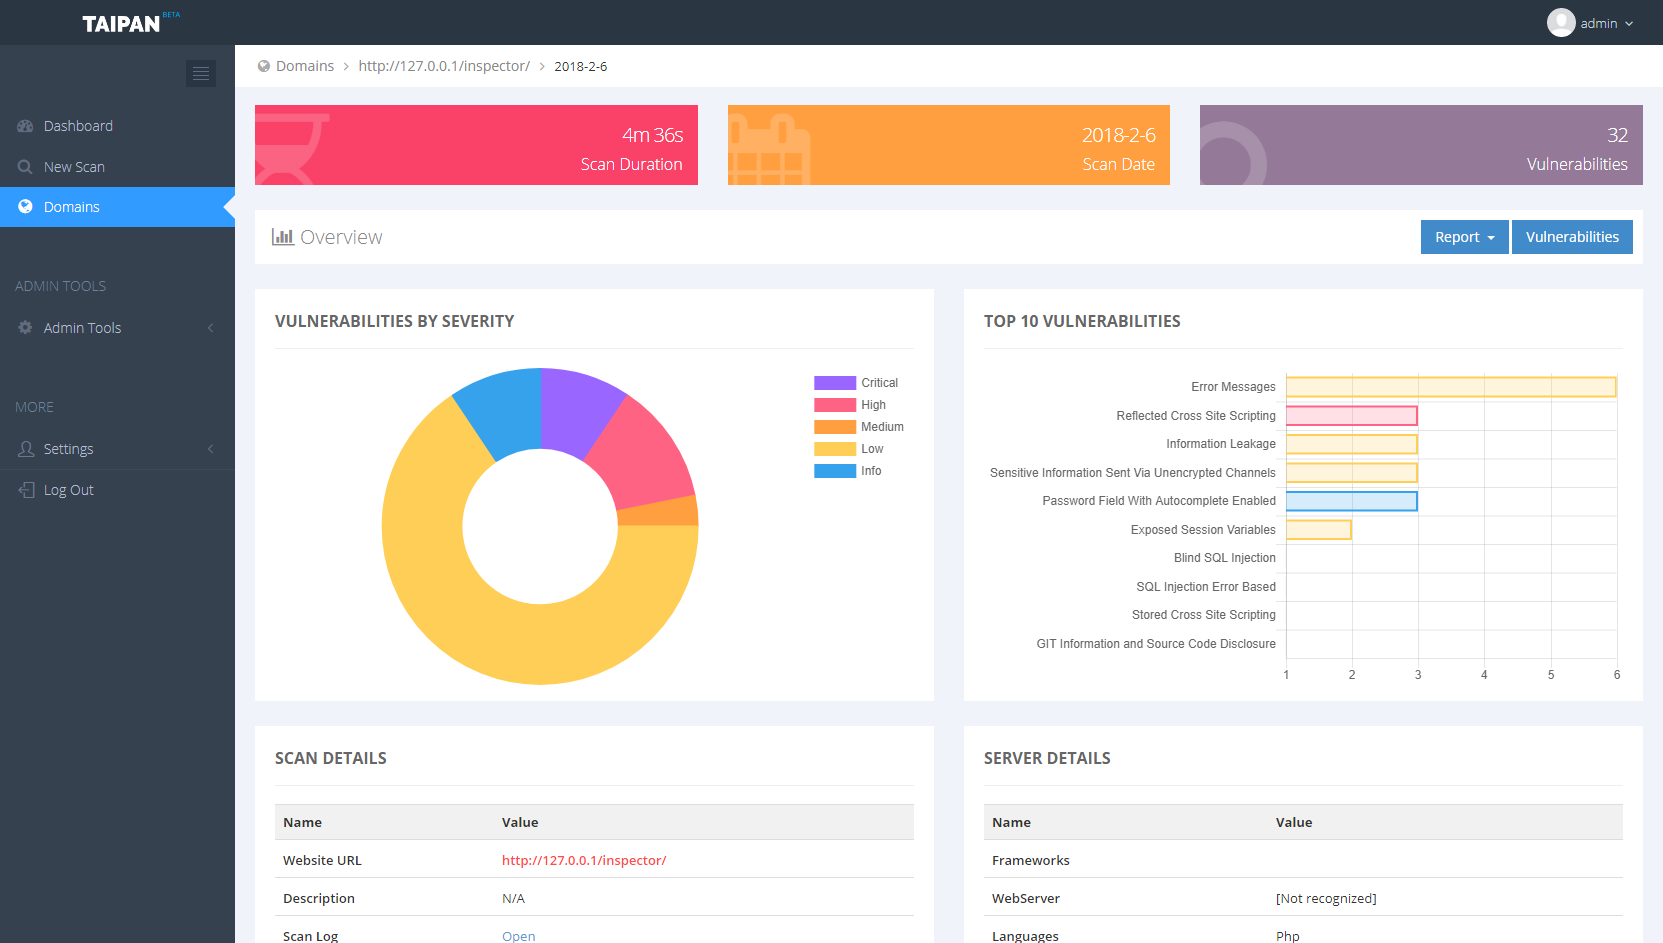 enkomio/taipan
Web application vulnerability scanner
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
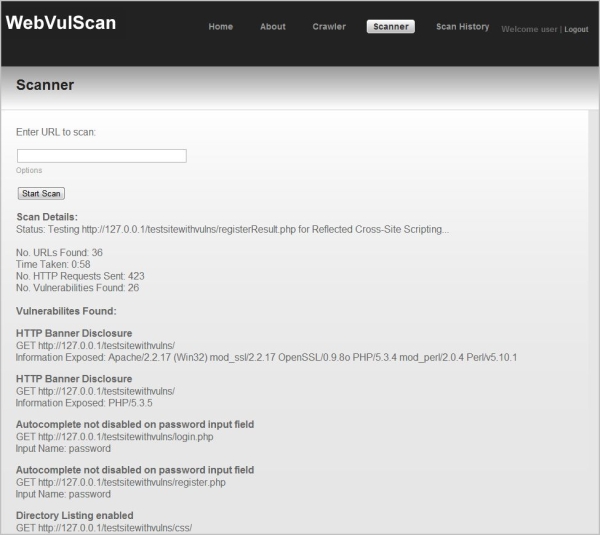 dermotblair/webvulscan
Web Application Vulnerability Scanner.
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
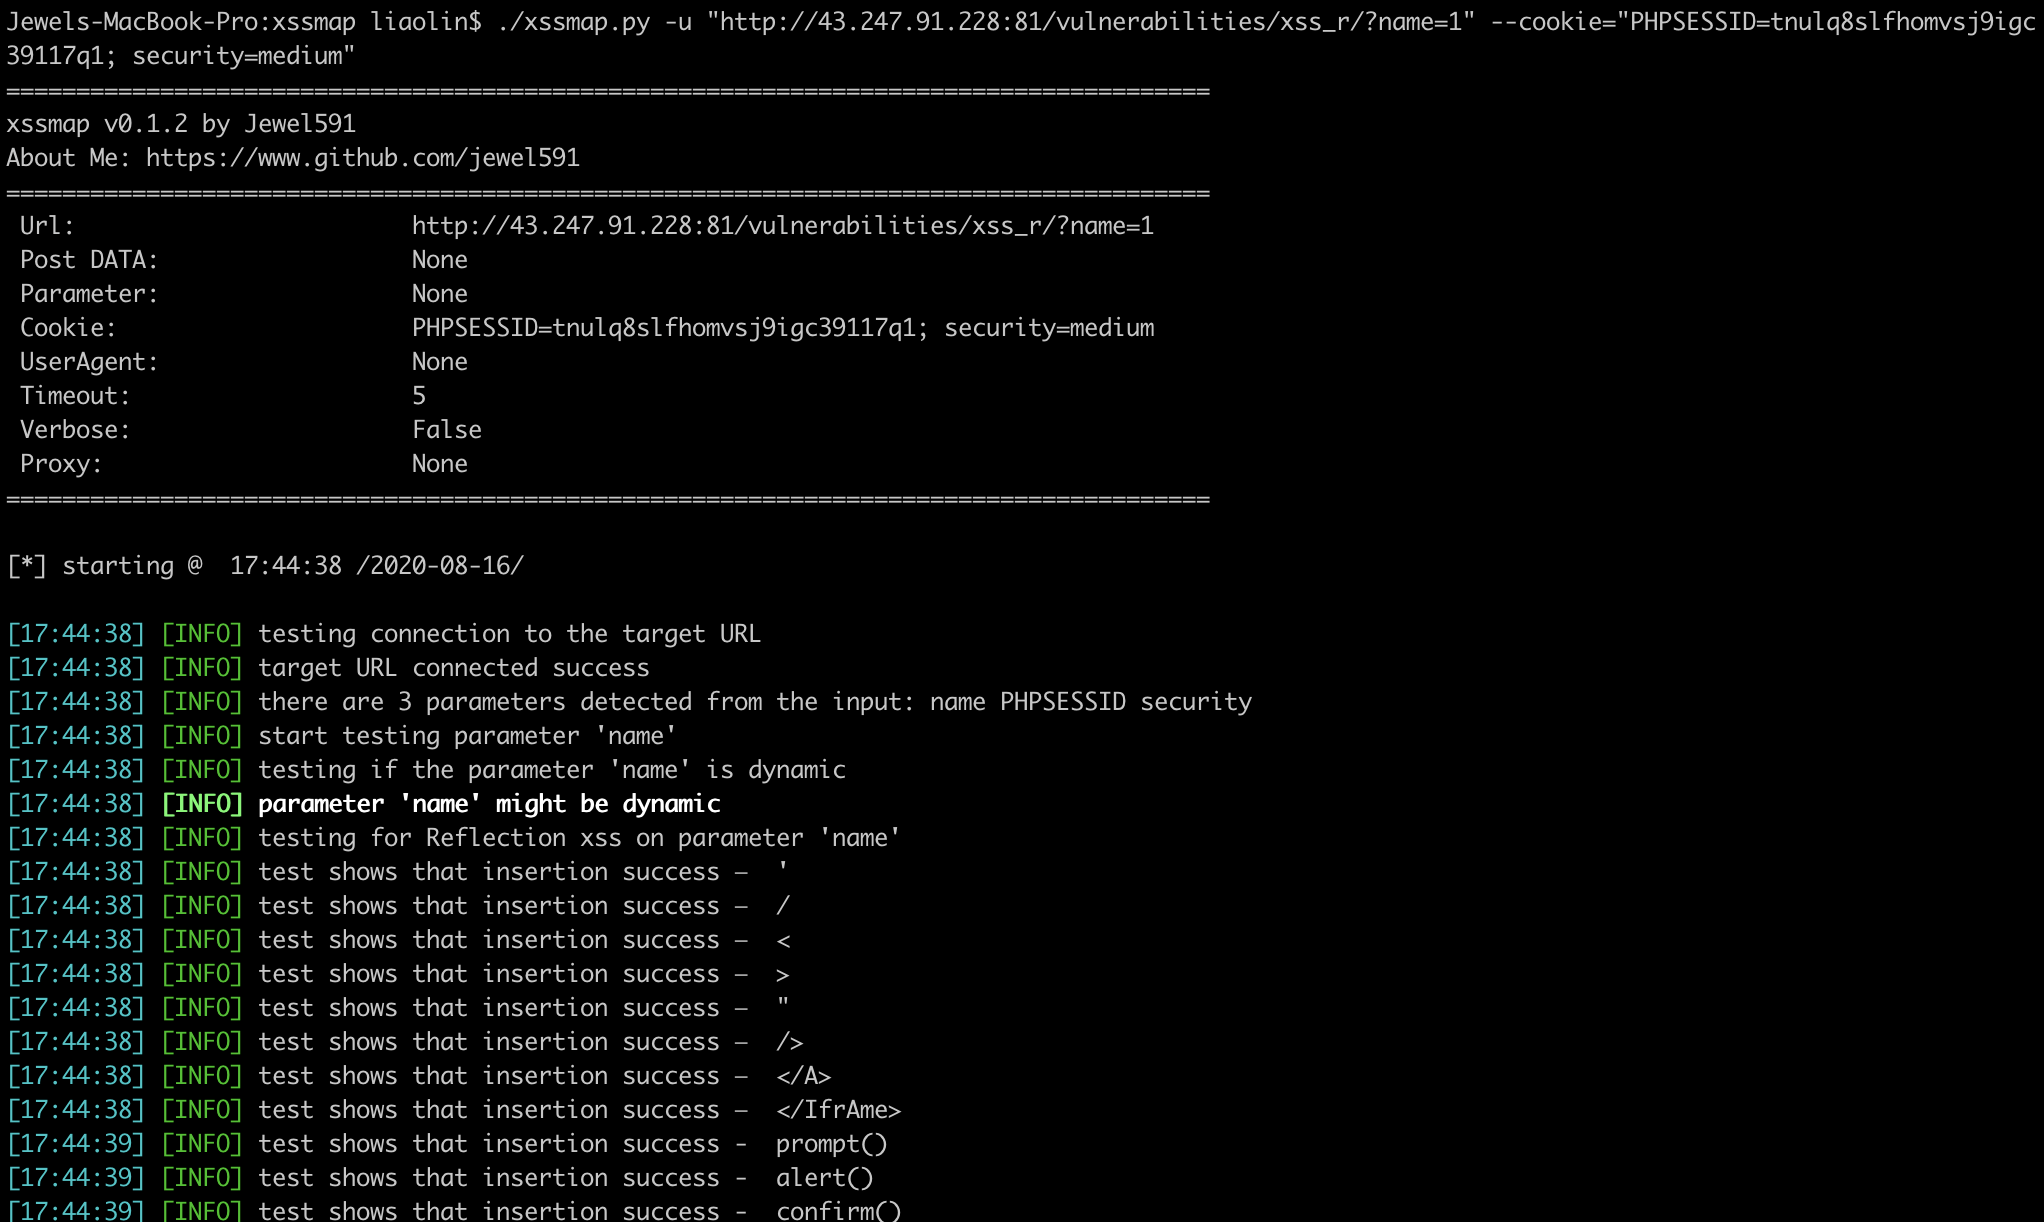 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…
 evilsocket/altair
Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…
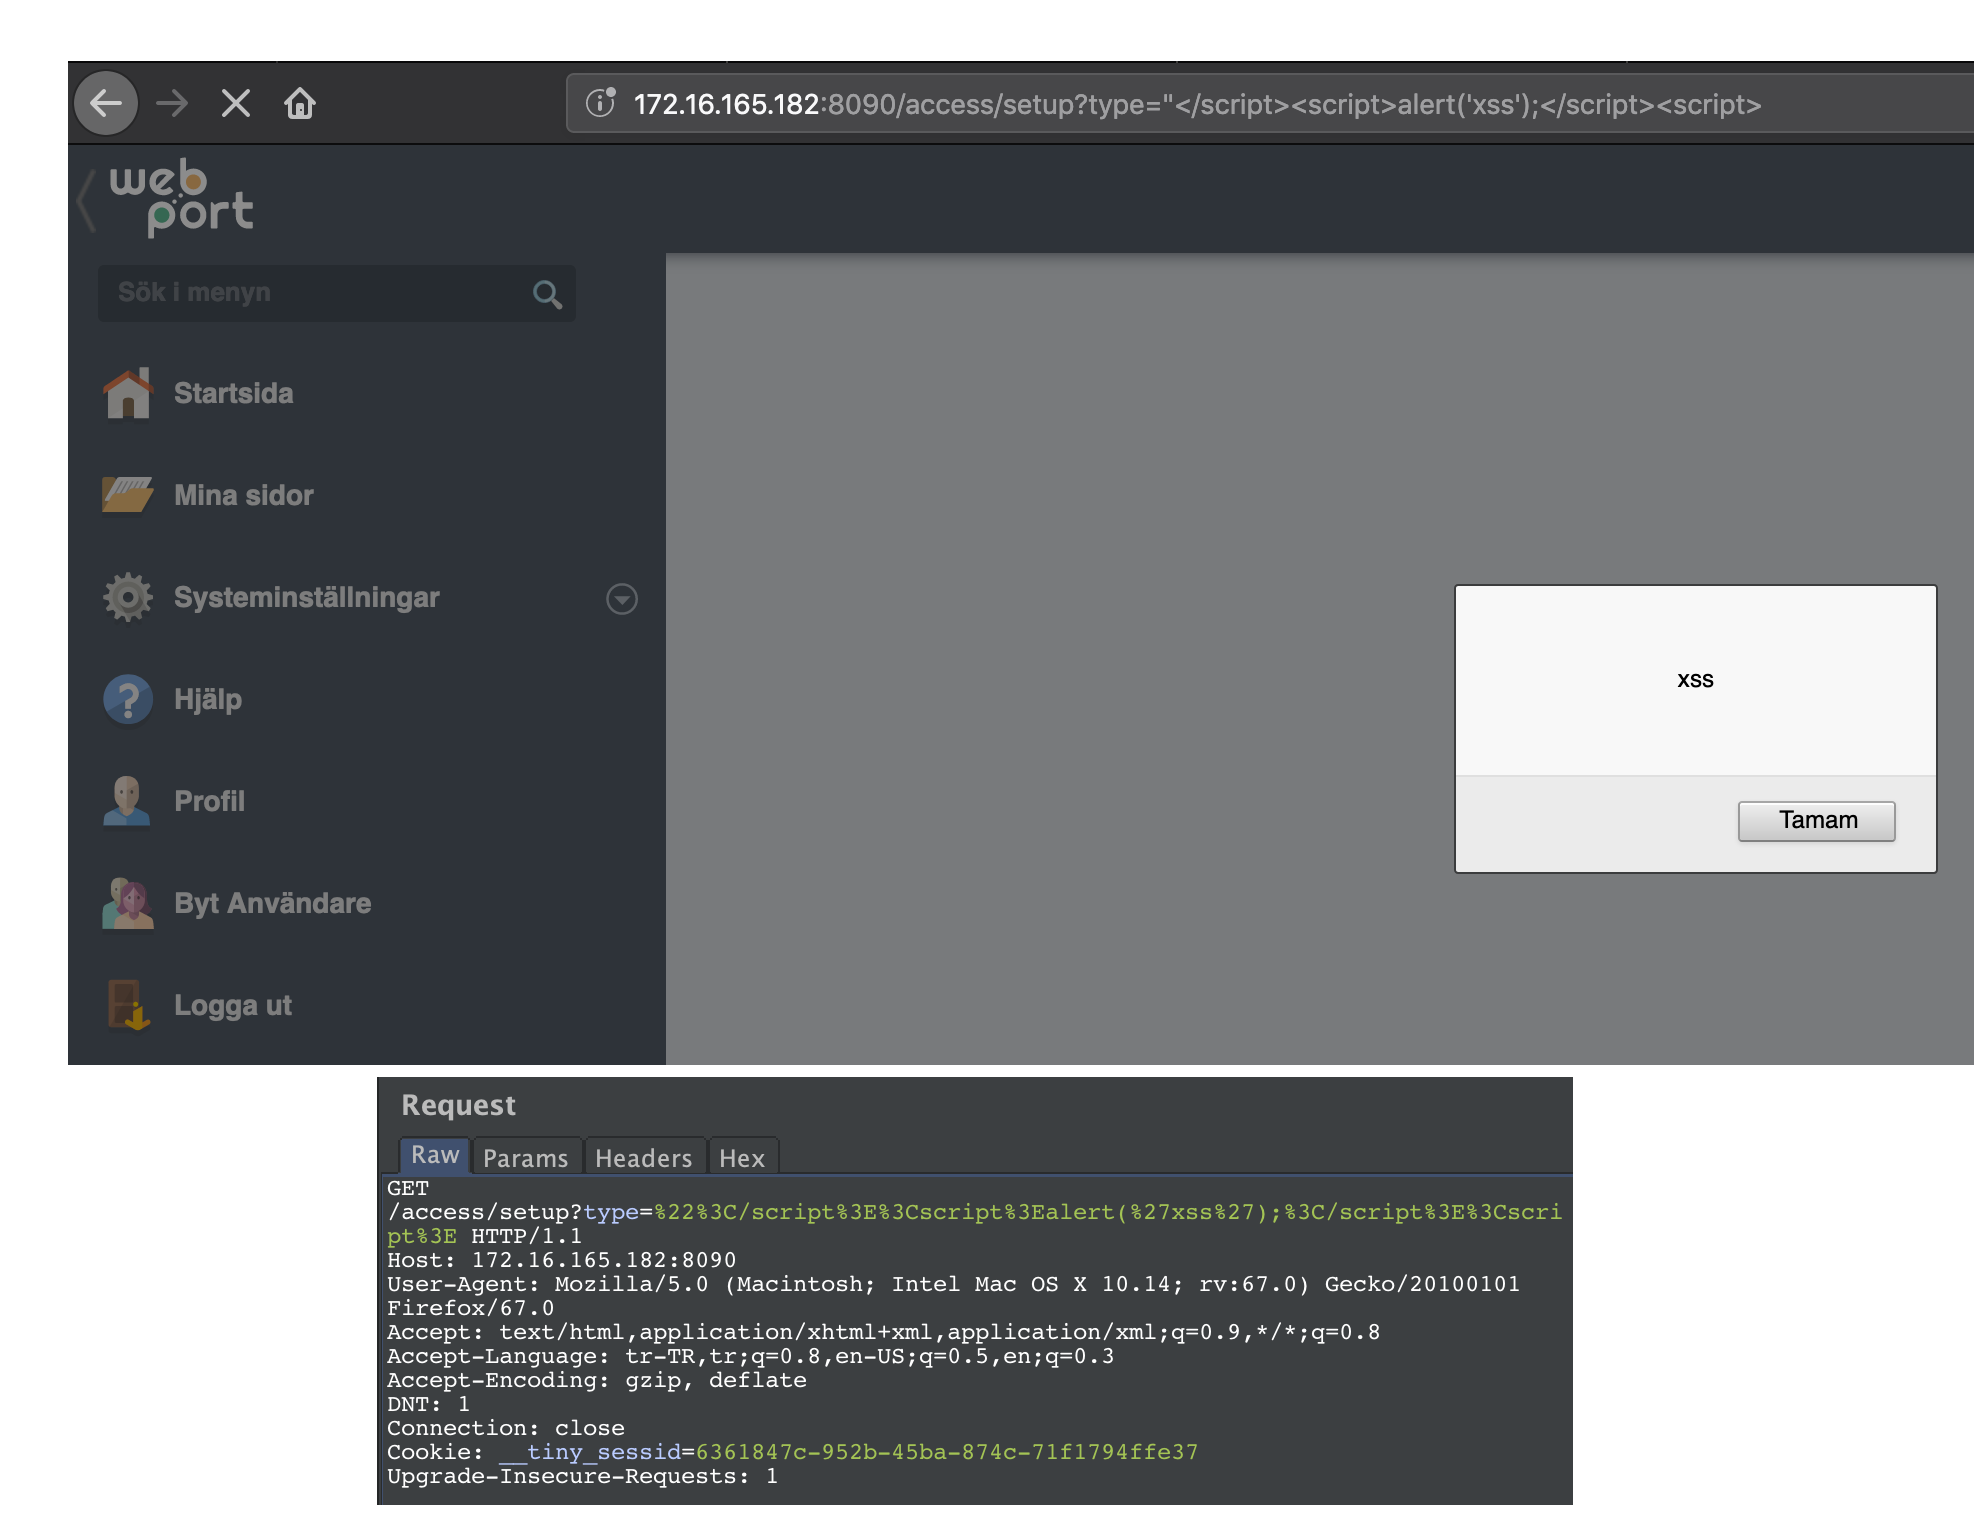 emreovunc/webport-v1.19.1-reflected-xss
CVE-2019-12460|Reflected XSS in WebPort-v1.19.1 impacts users who open a maliciously crafted link or third-party web page.
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…