Massive-Web-Application-Penetration-Testing-Bug-Bounty-Notes

A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…

A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…

The Offensive Manual Web Application Penetration Testing Framework.

Go Web Application Penetration Test

Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…

Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…

Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.

Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…

Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…

Python-based exploit for CVE-2021-45428, targeting a specific web application vulnerability for penetration testing and security assessment.

WAFNinja is a tool which contains two functions to attack Web Application Firewalls.

ADAPT is a tool that performs automated Penetration Testing for WebApps.

Python exploit script for CVE-2022-46169 targeting a specific web application vulnerability. Designed for penetration testers to verify and…

Exploit for CVE-2019-3396 targeting a web application vulnerability. Designed for penetration testing and security assessment of affected systems.

Exploit implementation for CVE-2014-6287, targeting a remote code execution vulnerability in a web application. Provides a proof-of-concept for…

Modified exploit for CVE-2019-15107 with a Perl reverse shell payload. Designed for penetration testing of the targeted web application vulnerability.

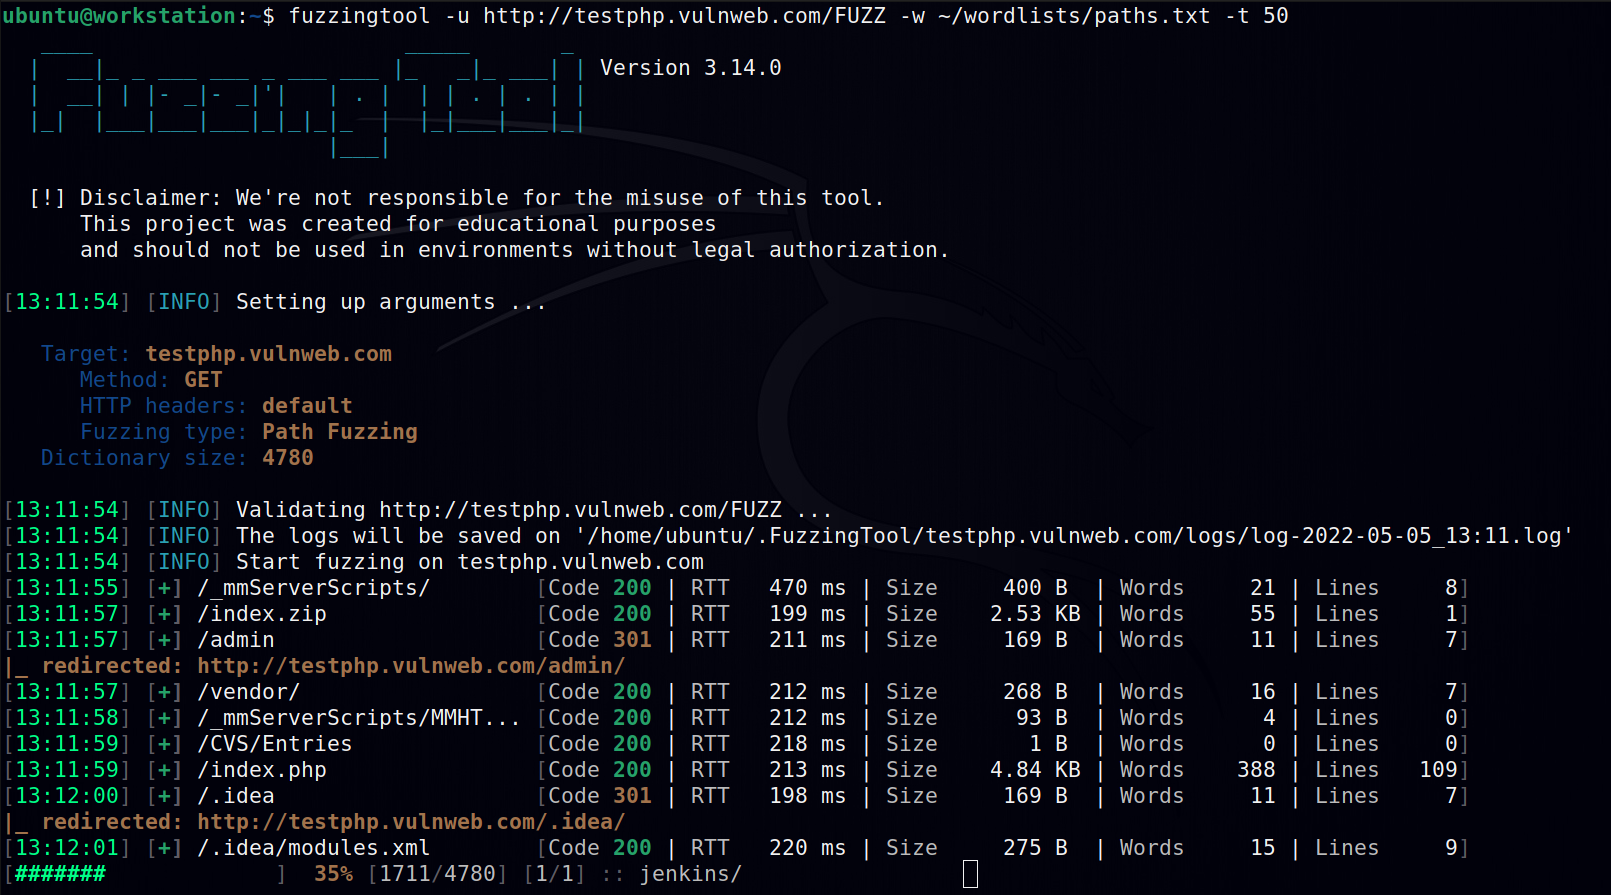
Software for fuzzing, used on web application pentestings.

Exploit script for CVE-2022-29469, a web application vulnerability, providing automated exploitation for penetration testing and security assessment.