
BWASP
 bwasp/bwasp
BoB Web Application Security Project
educationpenetration-testingvulnerability-analysis+3
bwasp/bwaspBoB Web Application Security Project
 jenderal92/cve-2024-10508
This tool scans WordPress sites for vulnerabilities in the "RegistrationMagic" plugin (CVE-2024-10508). It checks for the presence of a specific…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 dzonerzy/gowapt
Go Web Application Penetration Test
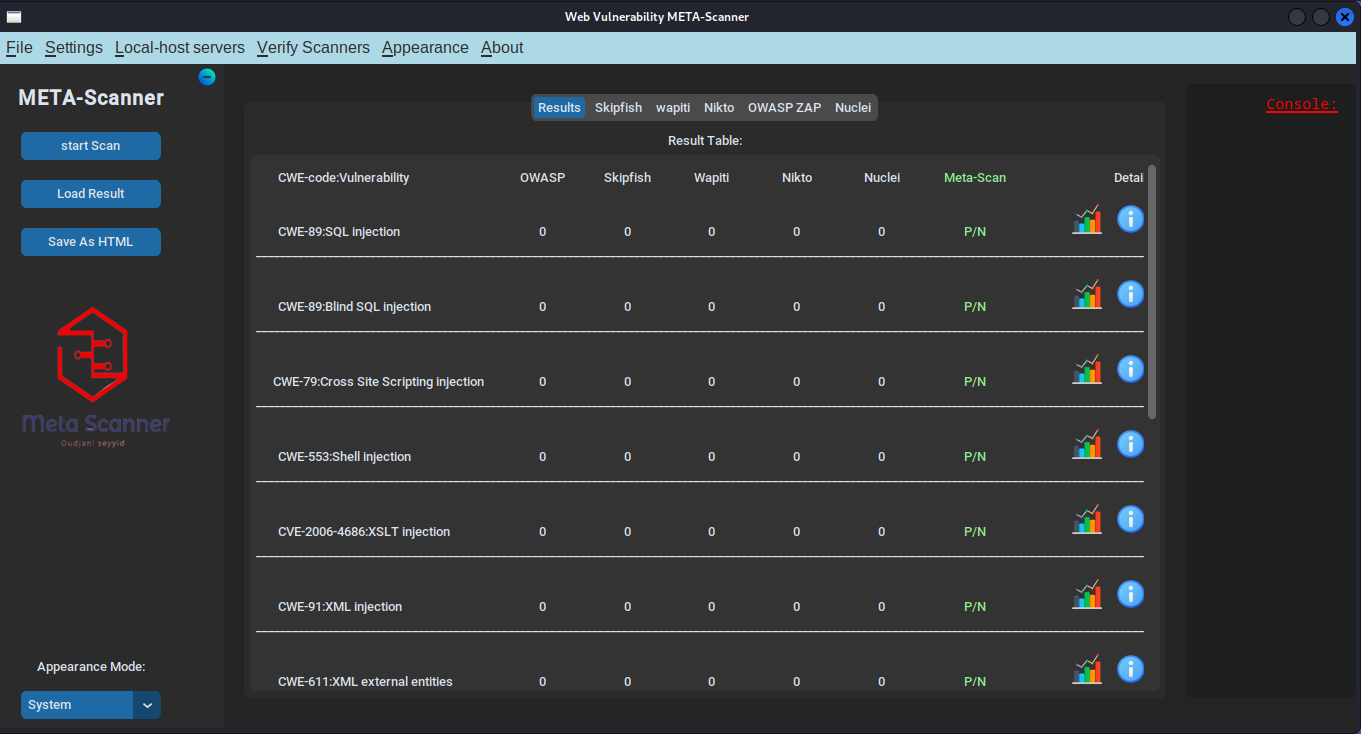 ostesayed/oste-meta-scan
Multi-engine DAST scanner aggregating Nikto, ZAP, Nuclei, SkipFish, and Wapiti for automated web injection vulnerability detection with consolidated…
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 hahwul/xspear
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner