

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 assetnote/node2shell-scanner
High fidelity detection mechanism for node2shell (CVE-2026-111497)
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
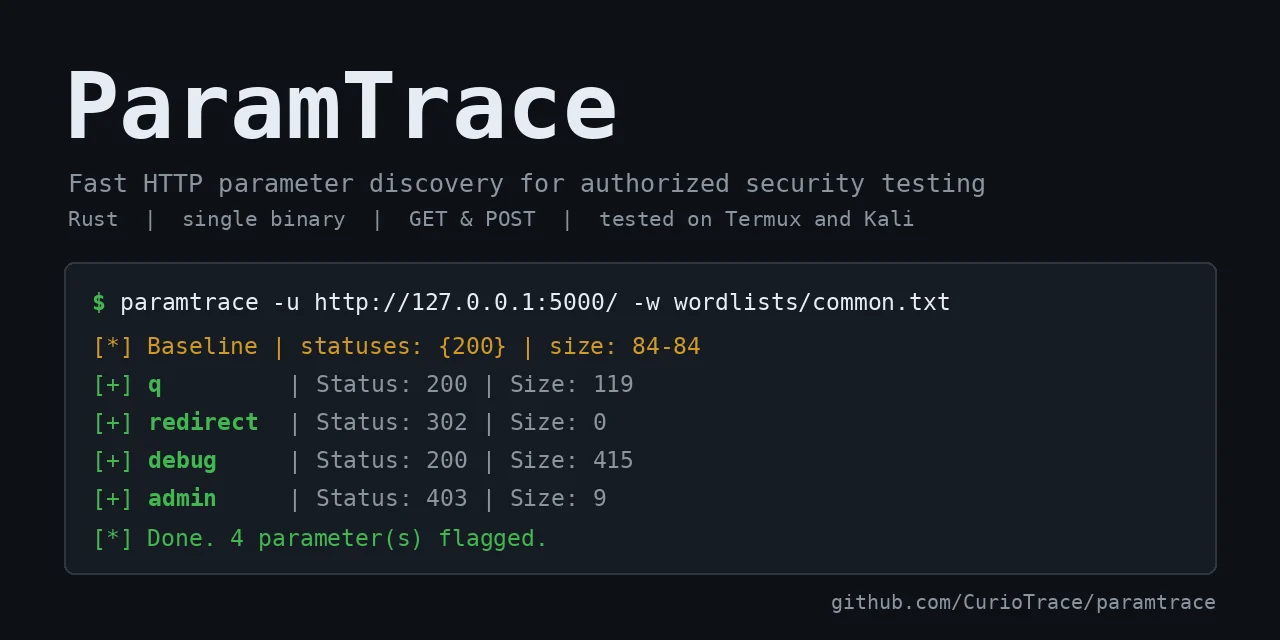 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 shenril/sitadel
Web Application Security Scanner
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 be-keb/cve-2026-12227
Proof-of-concept and technical analysis for CVE-2026-12227, an unauthenticated LFI in the WordPress Visual Composer plugin (<=45.16.0) enabling file…
 fgeek/pyfiscan
Free web-application vulnerability and version scanner
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 pwnvader/cve-2026-17089-poc-pwnvader
Shell PoC for CVE-2026-17089, an unauthenticated reflected XSS in the WordPress Events Manager plugin (<= 7.4.0.1); fingerprints the plugin and tests…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
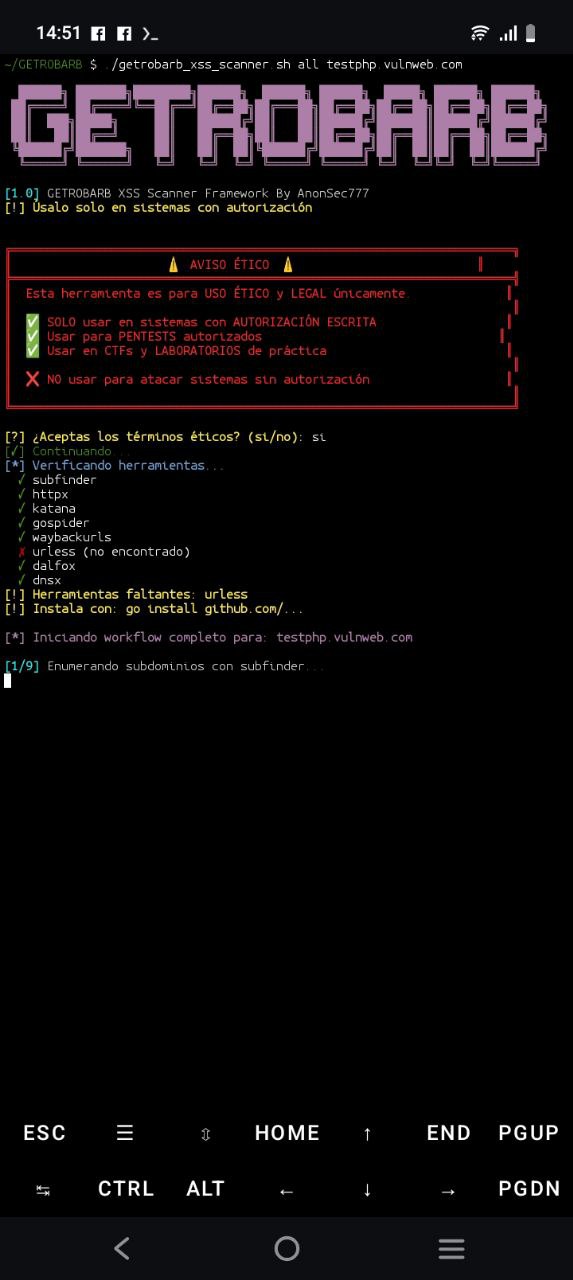 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.