
CVE-2026-123633
 llcforge/cve-2026-123633
Docker-based proof-of-concept for CVE-2026-123633, an nginx HTTP/2 use-after-free triggered by connection exhaustion and RST_STREAM races, with a…
exploitationnetwork-securityvulnerability-analysis+2
llcforge/cve-2026-123633Docker-based proof-of-concept for CVE-2026-123633, an nginx HTTP/2 use-after-free triggered by connection exhaustion and RST_STREAM races, with a…
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
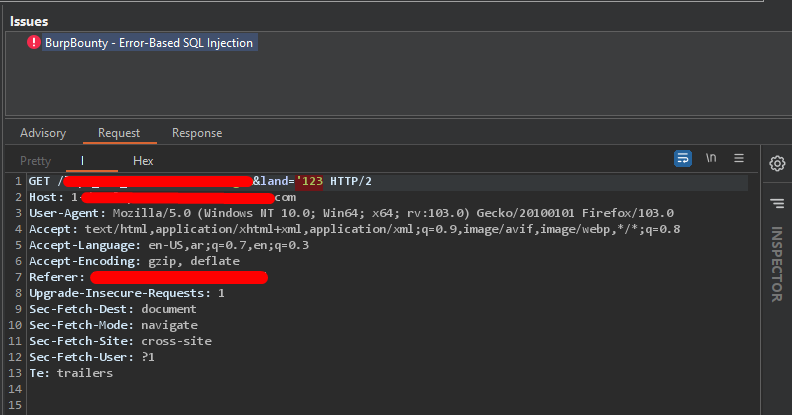 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
 charlie-goldenowl/cve-2026-122006-check
Read-only Bash script that scans Rails projects for CVE-2026-122006, flagging vulnerable activestorage versions, mini_magick variant processing, and…
 r0gfall/cve-2026-88804
Python script that checks Rancher instances for CVE-2026-88804 stored XSS and optionally injects an alert(1) payload to confirm exploitation.
 bimboxh4/cve-2026-21589
Python detection script that sends payloads to Atlassian Jira, Confluence, and Bitbucket instances to identify CVE-2026-21589 arbitrary file read…
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 yaupunal/cve-2025-55182-scanner
CVE-2025-55182-scanner with 2 different method
 rxerium/cve-2025-61882-cve-2025-61884
Detection for CVE-2025-61882 & CVE-2025-61884
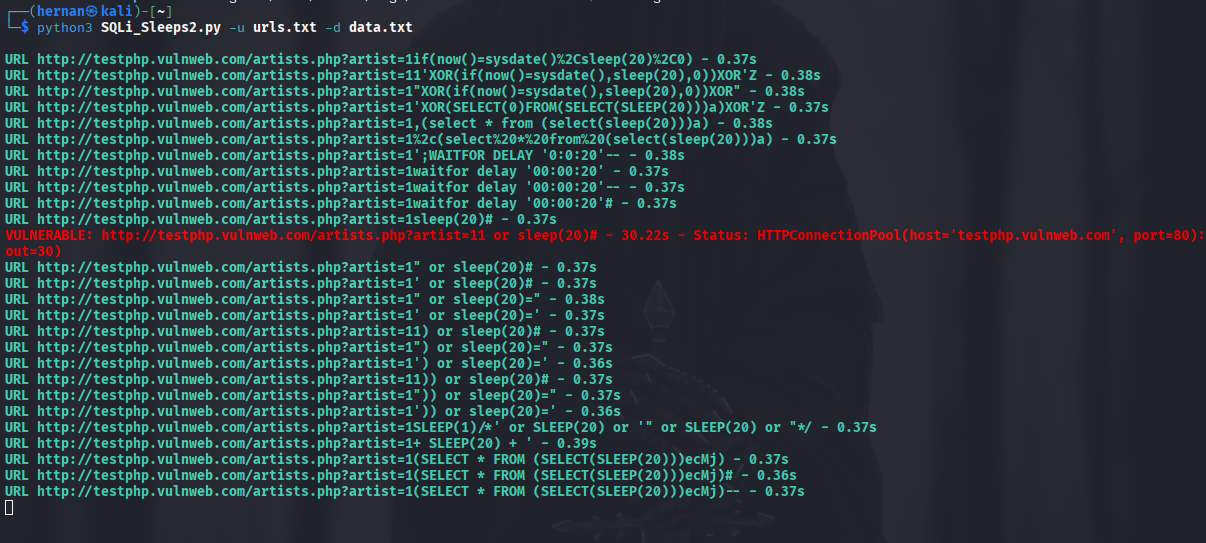 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 z3usx01/cve-2025-0054
Lightweight Python scanner for detecting stored XSS (CVE-2025-0054) in SAP NetWeaver Java. Submits customizable payloads and checks for script…
 sumeet-darekar/cve-2025-30208
mass scan for CVE-2025-30208
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 hxlxmj/cve-2022-3590-wordpress-vulnerability-scanner
This repository contains a Python script that checks WordPress websites for the CVE-2022-3590 vulnerability, which exploits an unauthenticated blind…
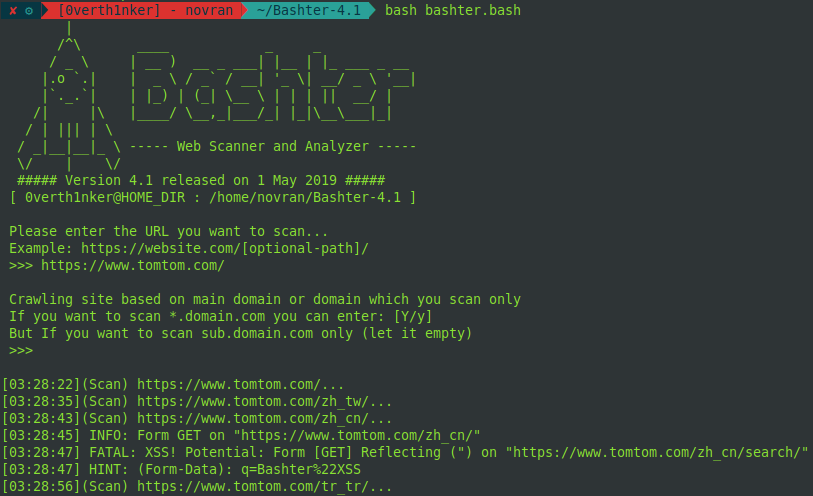 zerobyte-id/bashter
Web Vulnerability Scanner using Shell Script
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading