
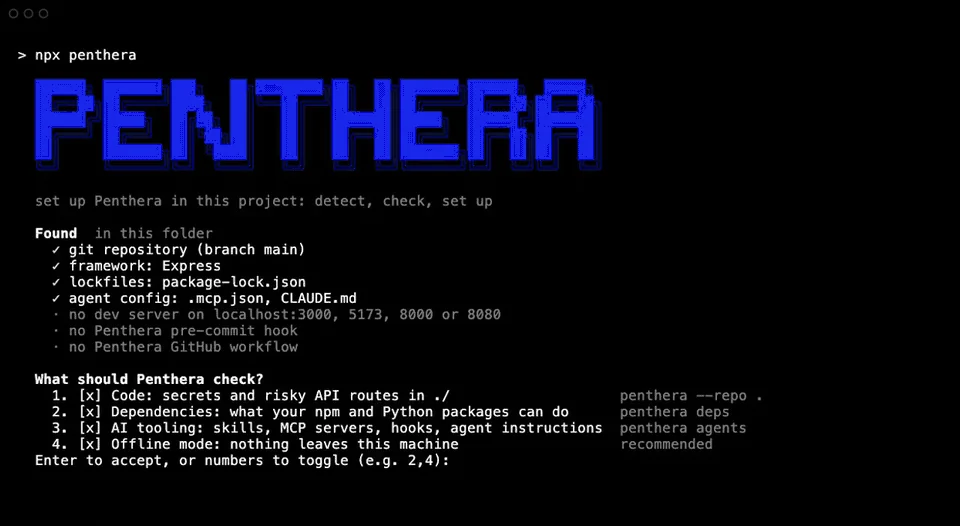
penthera
 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
ai-securitycode-analysisconfiguration-auditing+7
78
danoszz/pentheraOffline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 affolter-engineering/hvt
Rust CLI that probes HTTP methods (including WebDAV and DeltaV verbs) against a target URL to surface verb tampering, access-control bypasses, and…
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 horkimhab/cve-2025-64702-more
Proof-of-concept code and research notes for QPACK/HTTP-3 vulnerabilities (CVE-2025-64702, CVE-2026-12523, CVE-2025-13945) for authorized lab testing.
 assetnote/php2shell-scanner
High fidelity scanner for php2shell (CVE-2026-109618 and CVE-2026-109619)
 oscerd/cve-2026-85315
Runnable proof-of-concept reproducer for CVE-2026-85315, demonstrating camel-grpc consumer exception message disclosure (CWE-209) in Camel Spring…
 oscerd/cve-2026-85260
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85260, demonstrating camel-mllp PHI logging in affected versions and suppression after the…
 oscerd/cve-2026-85300
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85300, demonstrating camel-pqc writing private keys with permissive umask-derived file…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…