
CVE-2026-114509
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
authenticationexploitationinformation-gathering+6
nxploited/cve-2026-114509Laravel TokenGuard authentication bypass through non-string API credentials
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 assetnote/node2shell-scanner
High fidelity detection mechanism for node2shell (CVE-2026-111497)
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
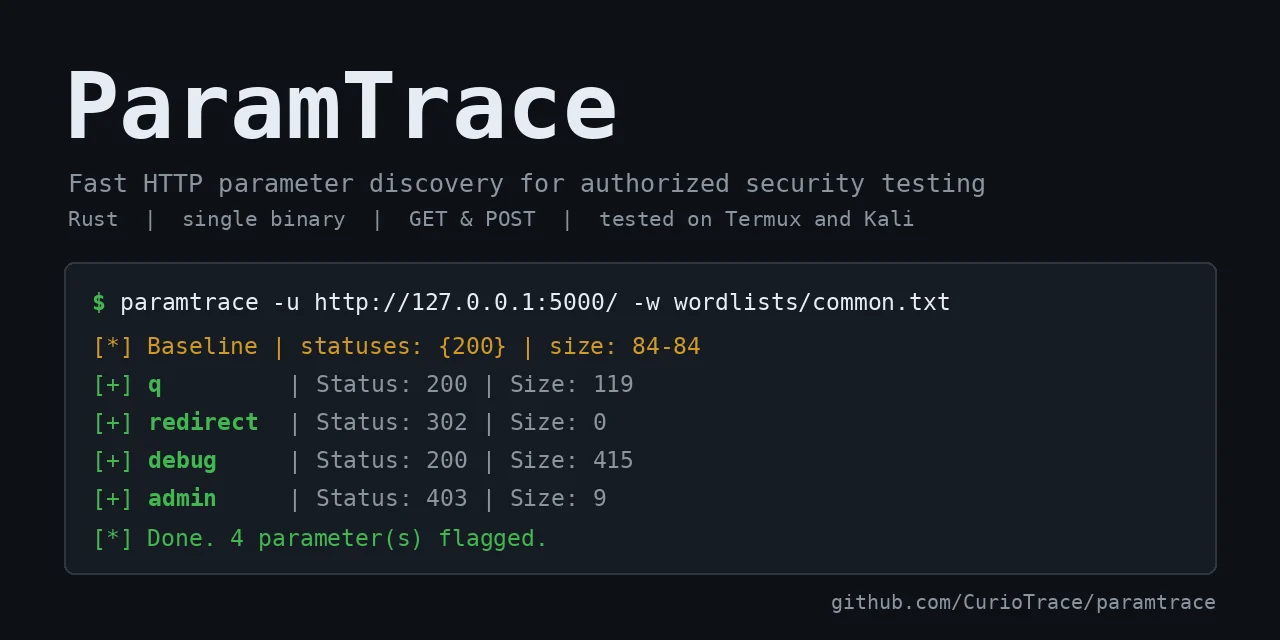 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 watchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589
Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.
 abatsakidis/cve-2026-14281-check
A Windows-friendly, non-destructive Python checker for detecting WordPress installations potentially affected by CVE-2026-14281.
 be-keb/cve-2026-12227
Proof-of-concept and technical analysis for CVE-2026-12227, an unauthenticated LFI in the WordPress Visual Composer plugin (<=45.16.0) enabling file…
 pwnvader/cve-2026-17089-poc-pwnvader
Shell PoC for CVE-2026-17089, an unauthenticated reflected XSS in the WordPress Events Manager plugin (<= 7.4.0.1); fingerprints the plugin and tests…
 flenz00/cve-2026-18110-poc
Python PoC and Nuclei template exploiting CVE-2026-18110, an unauthenticated user enumeration flaw in Concrete CMS 9.0.0-9.5.2 via the user…
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 hex0user/cve-2026-1731
Python scanner that passively fingerprints exposed BeyondTrust Remote Support and Privileged Remote Access services to detect potential CVE-2026-1731…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…