

rcekit
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
command-and-controlexploitationfuzzing+8
27
kabiri-labs/rcekitRCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
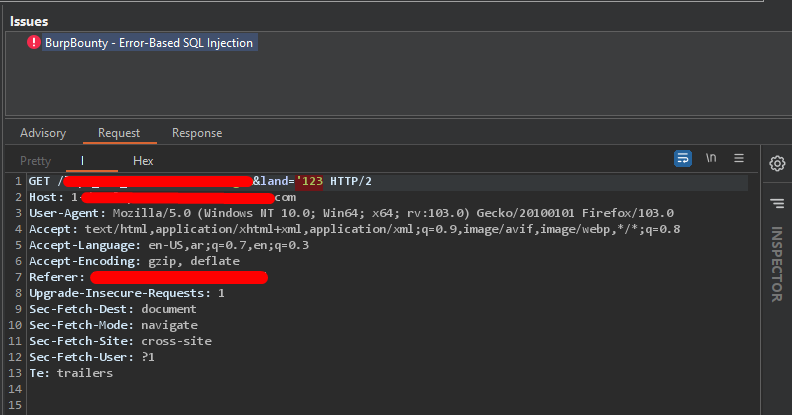 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
 capture0x/xss-loader
Xss Payload Generator ~ Xss Scanner ~ Xss Dork Finder
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
 jenderal92/cve-2026-49049
Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…
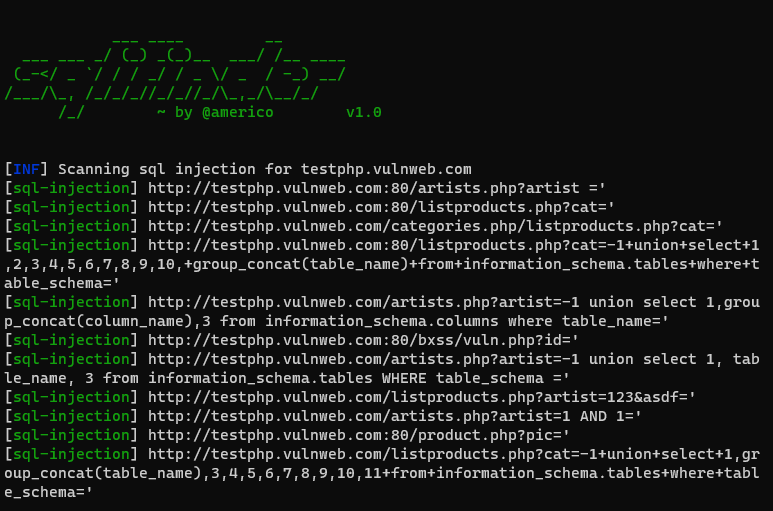 americo/sqlifinder
SQL Injection Vulnerability Scanner made with Python
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 strobelpierre/cve-2026-9082
Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…
 z3usx01/cve-2025-0054
Lightweight Python scanner for detecting stored XSS (CVE-2025-0054) in SAP NetWeaver Java. Submits customizable payloads and checks for script…
 0xshaheen/cve-2025-30208
Scanner for CVE-2025-30208 in Vite Dev Server, supporting single and mass URL scanning with multiple payloads, multi-threading, and vulnerable URL…
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…