

cve-2025-66723
 audiopump/cve-2025-66723
CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
data-exfiltrationexploitationinformation-gathering+3
audiopump/cve-2025-66723CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
 indominusrexes/cve-2025-4322-exploit
Critical CVE-2025-4322 exploit for Firefox on Windows enabling sandbox escape and arbitrary code execution. Includes download link and technical…
 egebalci/cve-2018-8065
Flexense HTTP Server <= 10.6.24 - Denial Of Service Exploit
 zprototype/cve-2023-29808
Reflected cross-site scripting (XSS) proof-of-concept exploit for CVE-2023-29808 targeting the /index.php?map=overview&findme= endpoint in cmaps…
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
 gmh5225/zeropoint
This PowerShell script detects indicators of compromise for CVE-2025-53770 — a critical RCE vulnerability in Microsoft SharePoint. Created by…
 sastraadiwiguna-purpleeliteteaming/dissecting-cve-2026-0628-chromium-extension-privilege-escalation
Technical dissection of CVE-2026-0628, a Chromium WebView privilege escalation vulnerability, including root cause analysis, PoC exploit, detection…
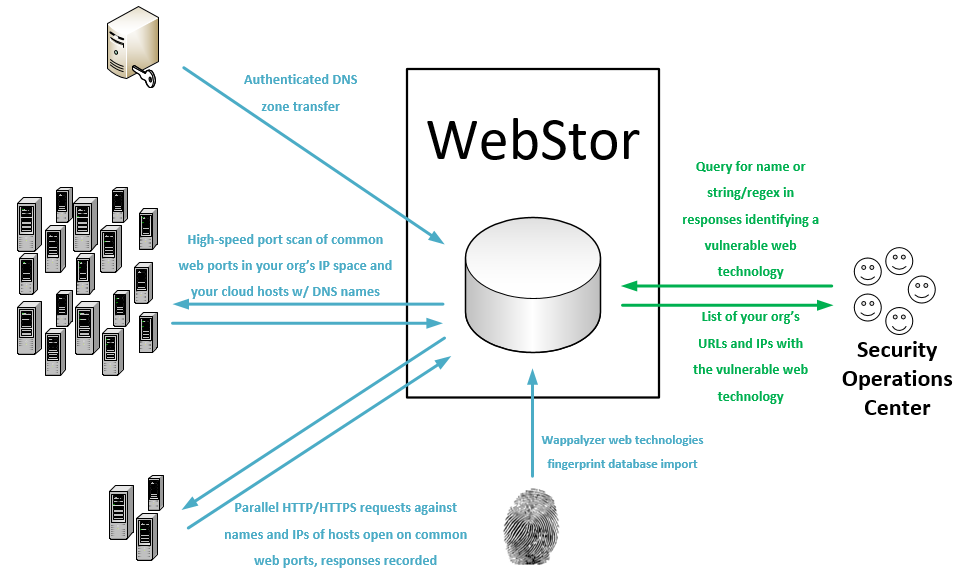 rossgeerlings/webstor
Enumerates all websites across an organization's networks via DNS zone transfers and masscan, stores responses, and enables querying for known…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 davidfortytwo/bluekeep
Python-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 alt3kx/cve-2002-0200
Cyberstop Web Server for Windows 0.1 allows remote attackers to cause a denial of service via an HTTP request for an MS-DOS device name.
 jet-pentest/cve-2021-3130
Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
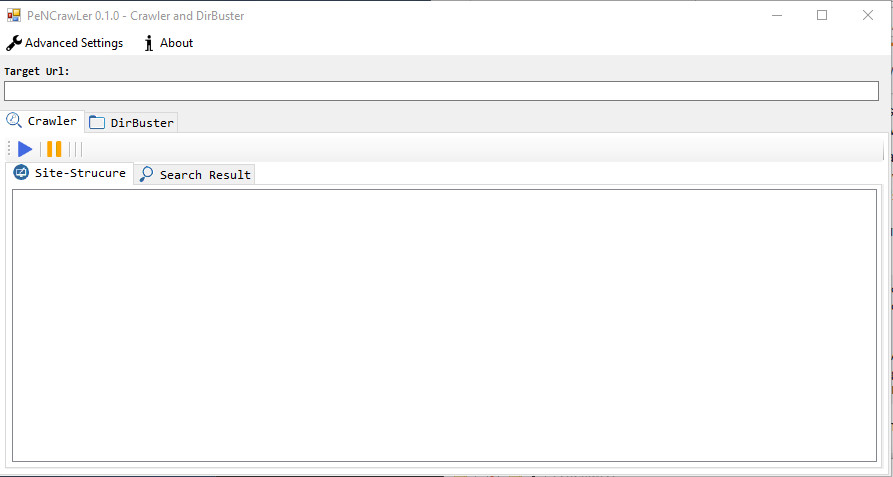 them4hd1/pencrawler
An Advanced Web Crawler and DirBuster
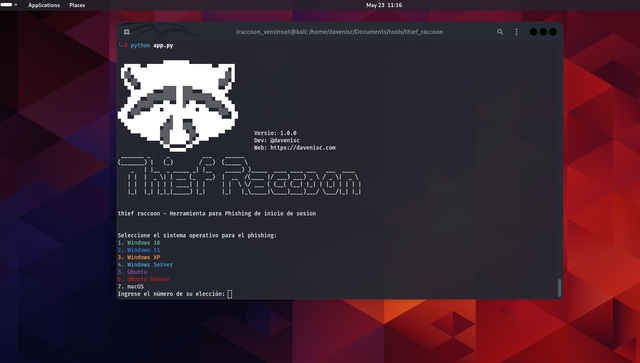 davenisc/thief_raccoon
Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…