
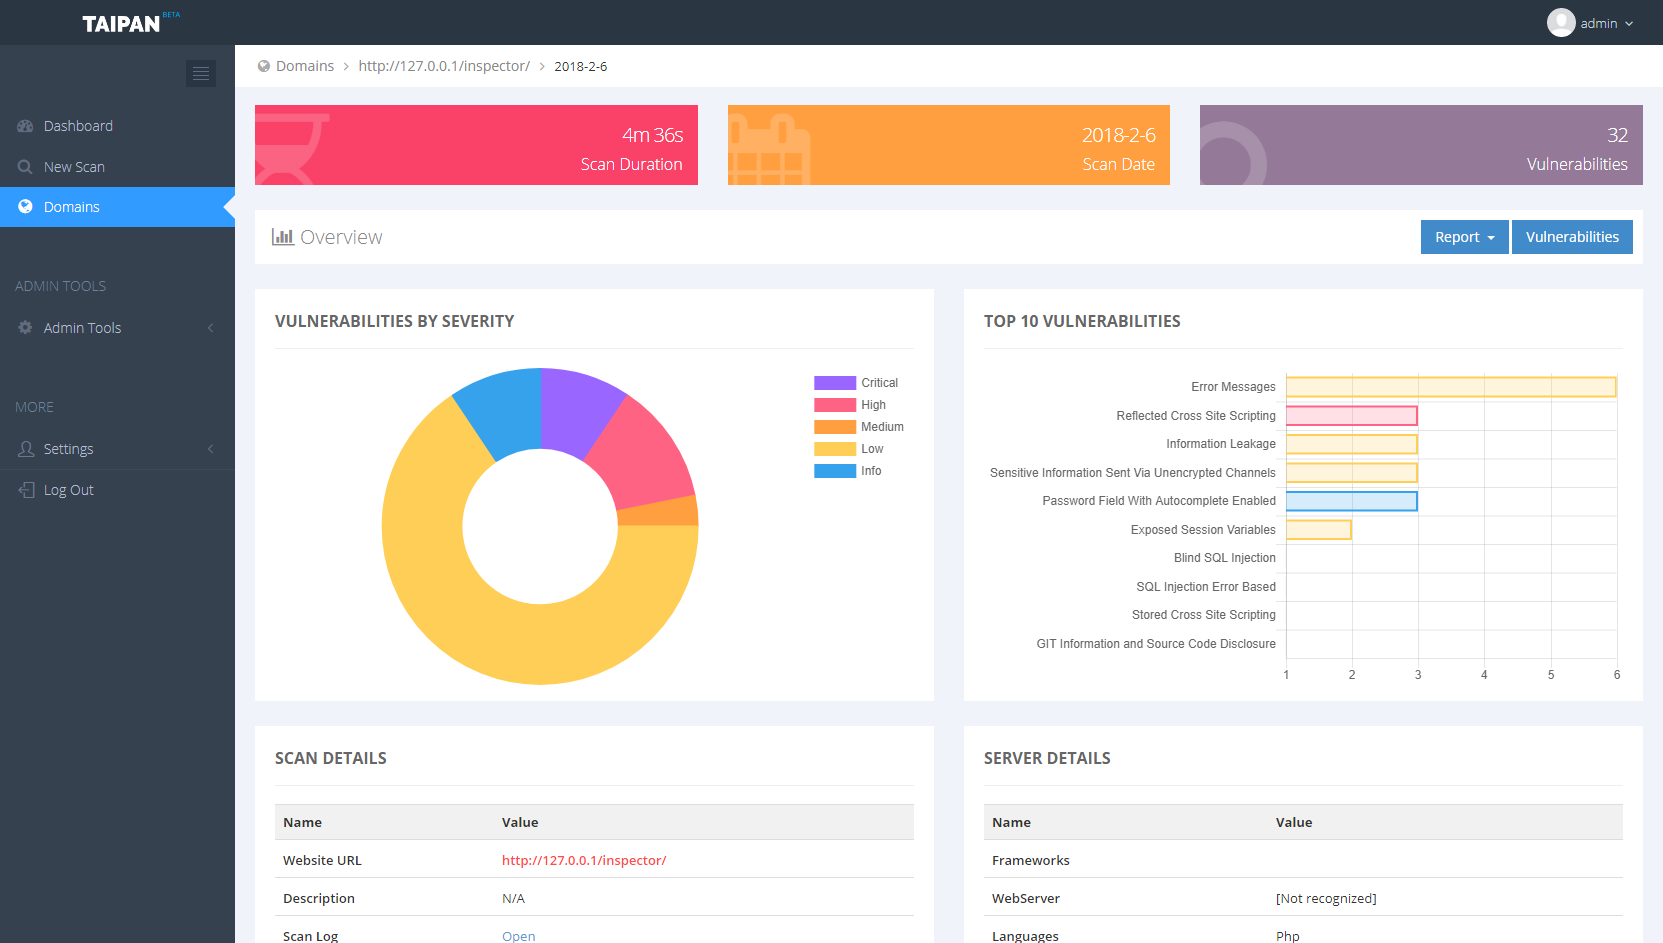
Taipan
 enkomio/taipan
Web application vulnerability scanner
penetration-testingvulnerability-scannersweb-security+1
enkomio/taipanWeb application vulnerability scanner
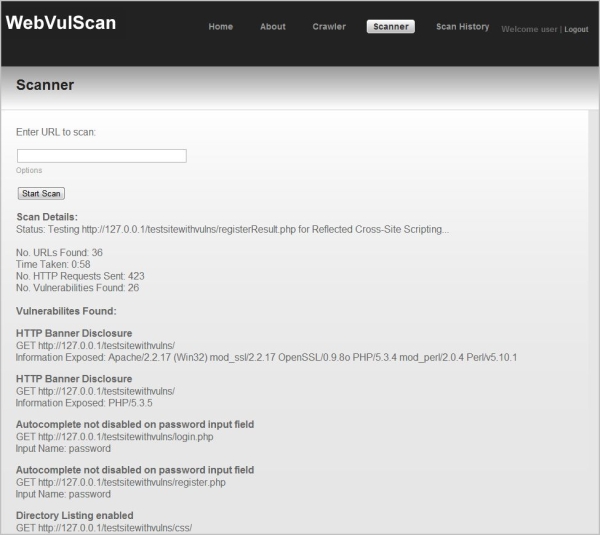 dermotblair/webvulscan
Web Application Vulnerability Scanner.
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
 ulyssessaicha/cve-2023-6875
Proof-of-concept exploit for CVE-2023-6875, demonstrating a web application vulnerability. Includes code and instructions for reproducing the issue.
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
 usernameisunavailable-cell/bili-cracker
Exploit tool leveraging CVE-2026-350234 to obtain bilibili membership privileges, demonstrating web application vulnerability exploitation.
 joojiii/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 in Next.js 15.2.0, demonstrating a specific web application vulnerability for testing and educational…
 fgeek/pyfiscan
Free web-application vulnerability and version scanner
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 brianwrf/nagascan
NagaScan is a distributed passive vulnerability scanner for Web application.
 4chech/cve-2026-41242
Proof-of-concept exploit for CVE-2026-41242 in a Node.js web application, demonstrating the vulnerability and potential impact.
 z3n70/cve-2023-23752
simple program for joomla CVE-2023-23752 scanner for pentesting and educational purpose
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 smarttfoxx/cve-2025-45778
A stored cross-site scripting (XSS) vulnerability in The Language Sloth Web Application v1.0 allows attackers to execute arbitrary javascript or HTML…
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher