
jwtear
 kingsabri/jwtear
Modular command-line tool to parse, create and manipulate JWT tokens for hackers
educationpassword-crackingpenetration-testing+2
kingsabri/jwtearModular command-line tool to parse, create and manipulate JWT tokens for hackers
 iangcarroll/cookiemonster
Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
 noraj/flask-session-cookie-manager
🍪 Flask Session Cookie Decoder/Encoder
 dub-flow/sessionprobe
Multi-threaded web authorization testing tool that evaluates user privileges by checking session token access across a list of URLs, highlighting…
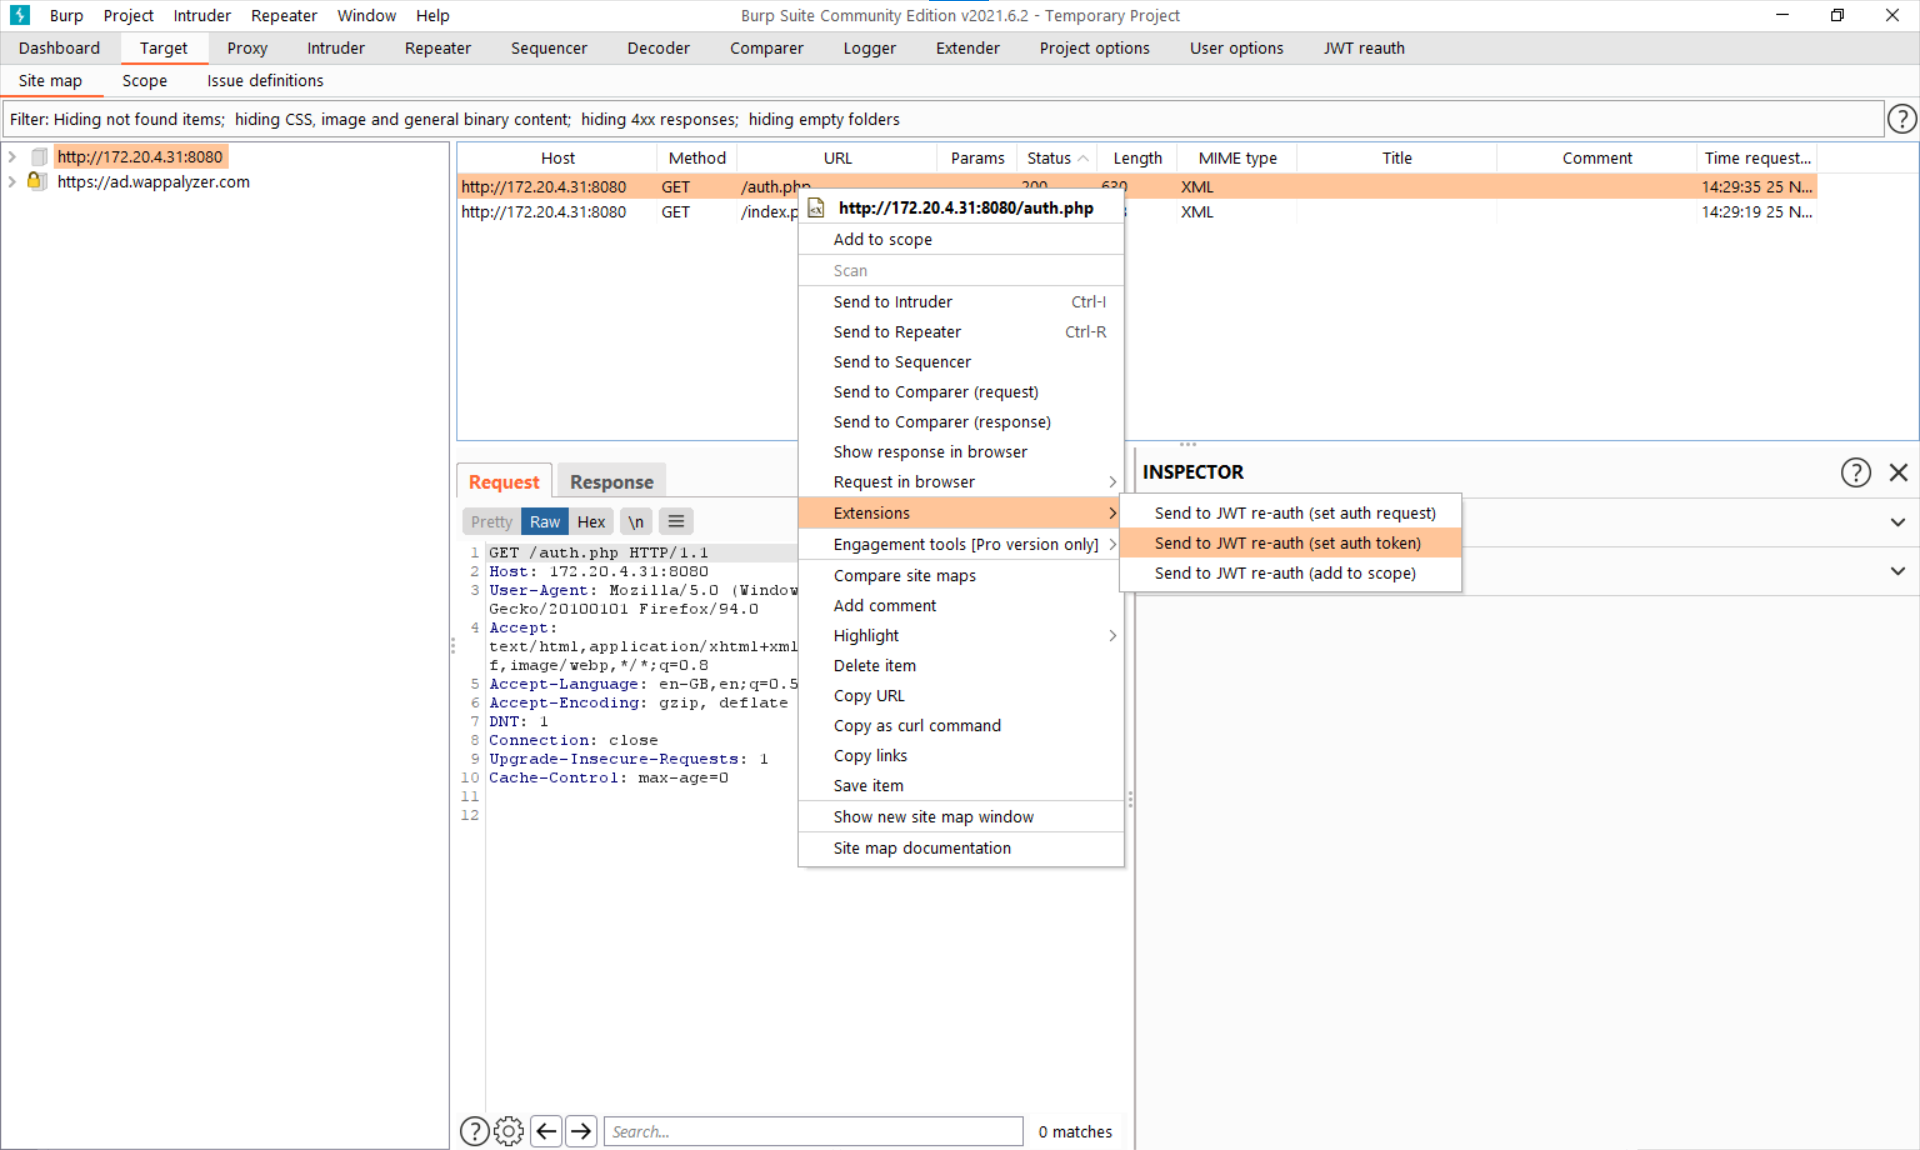 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
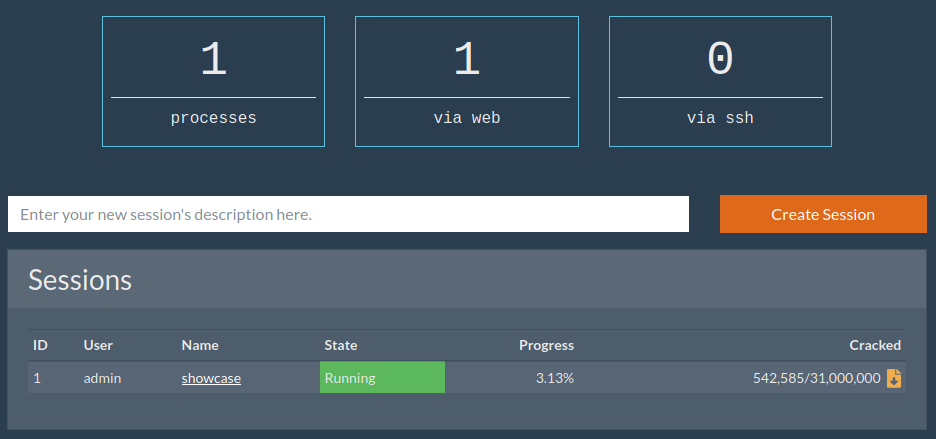 sadreck/crackerjack
Web-based GUI for Hashcat that simplifies password cracking with session management, mask generation, wordlist support, and multi-user access.
 dionach/codeigniterxor
CodeIgniter <=2.1.4 session cookie decryption vulnerability
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 oscarfromnz/instagrammutualfollowerchecker
Checks mutual followers between ig accounts (local hosted, use your own session id)
 ibnuuby/cve-2021-32099
Proof-of-concept exploit for CVE-2021-32099, a SQL injection vulnerability in Pandora FMS, demonstrating session hijacking via crafted UNION query.
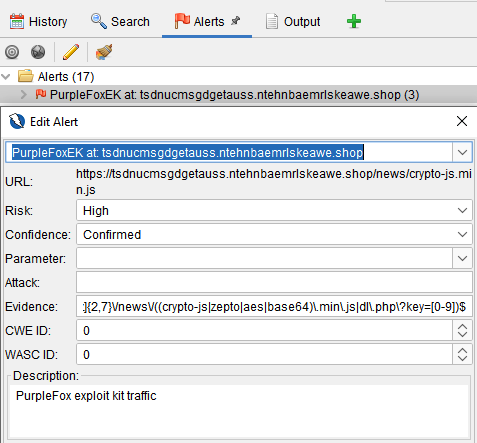 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
 iss4cf0ng/openshell
Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
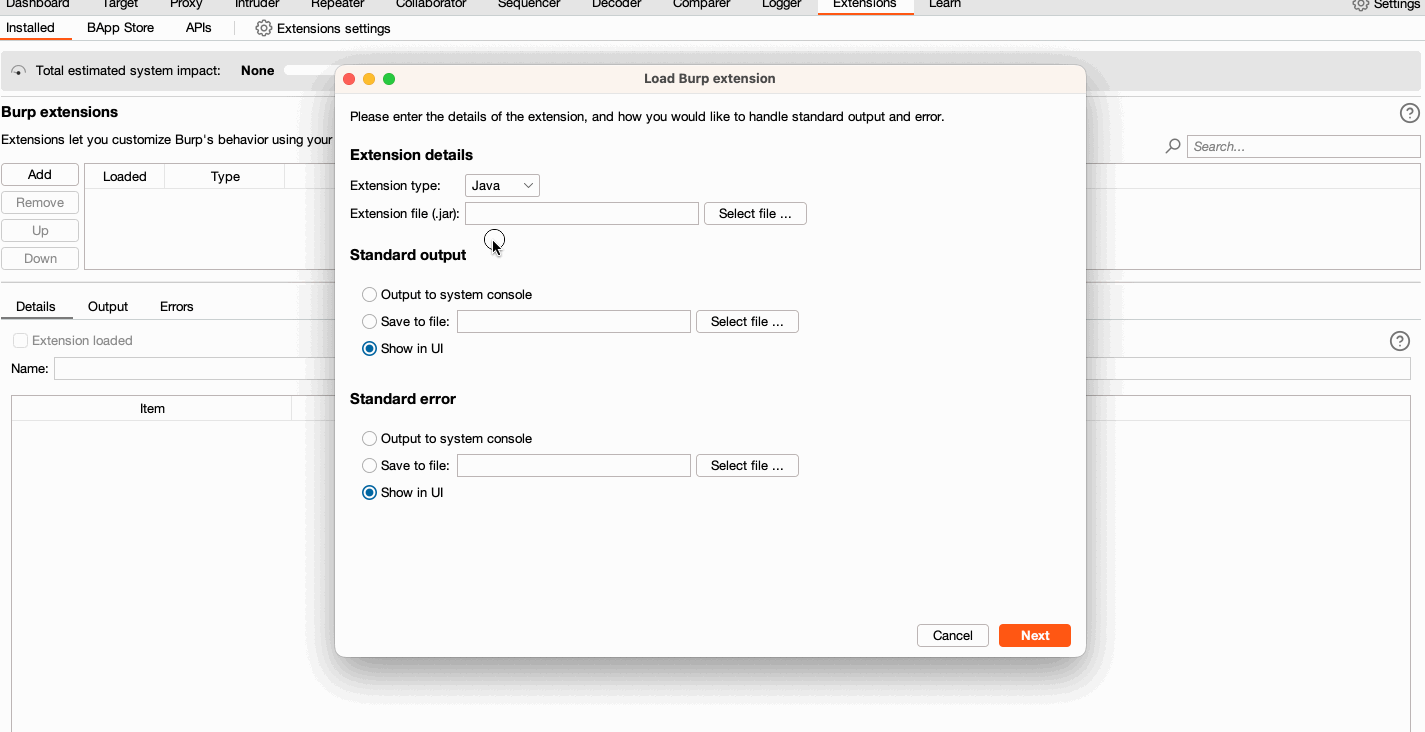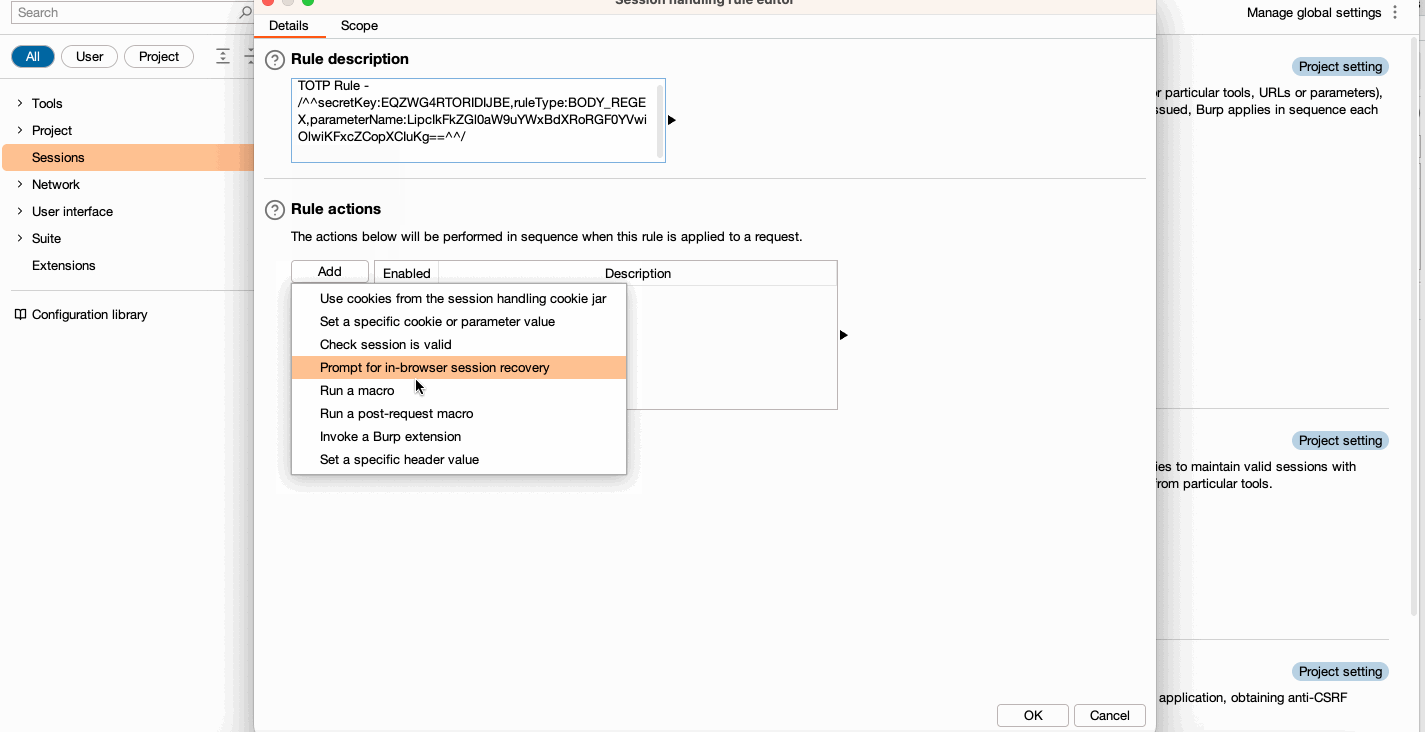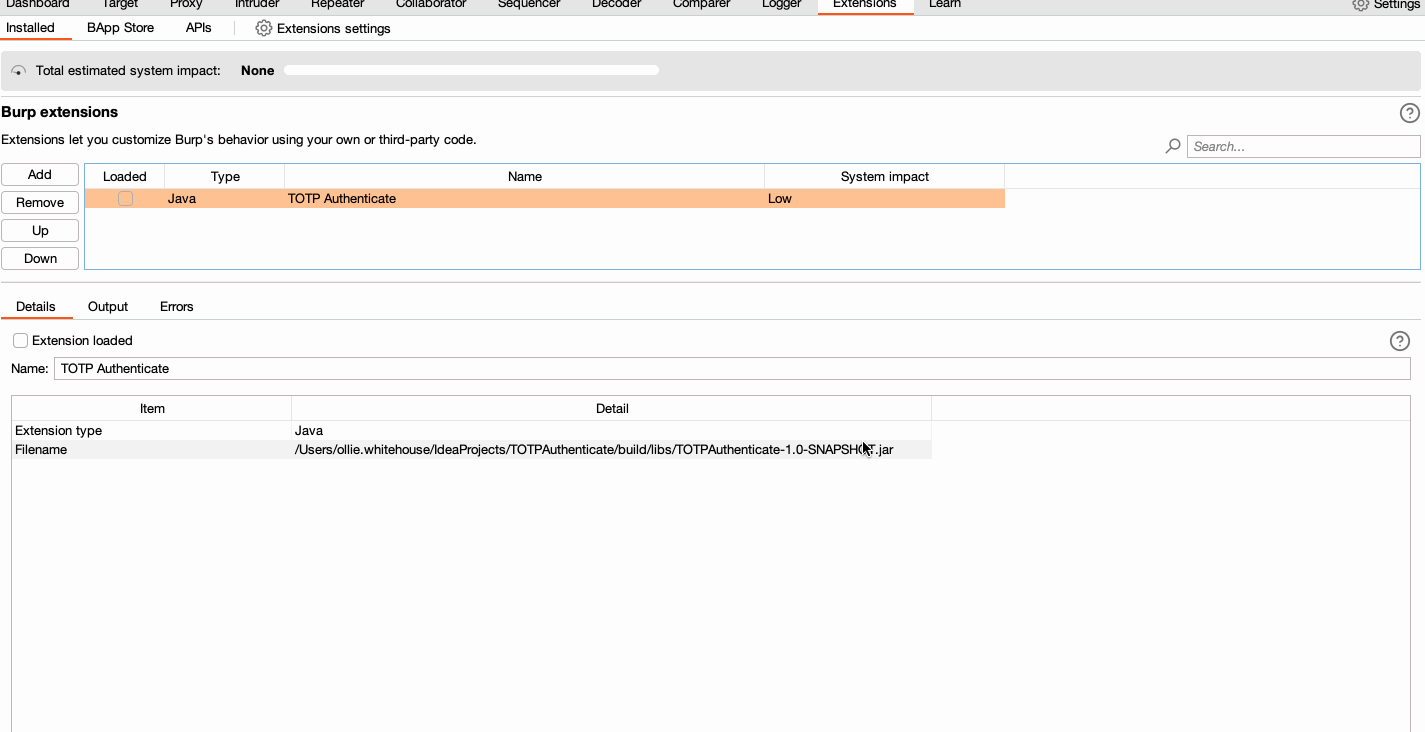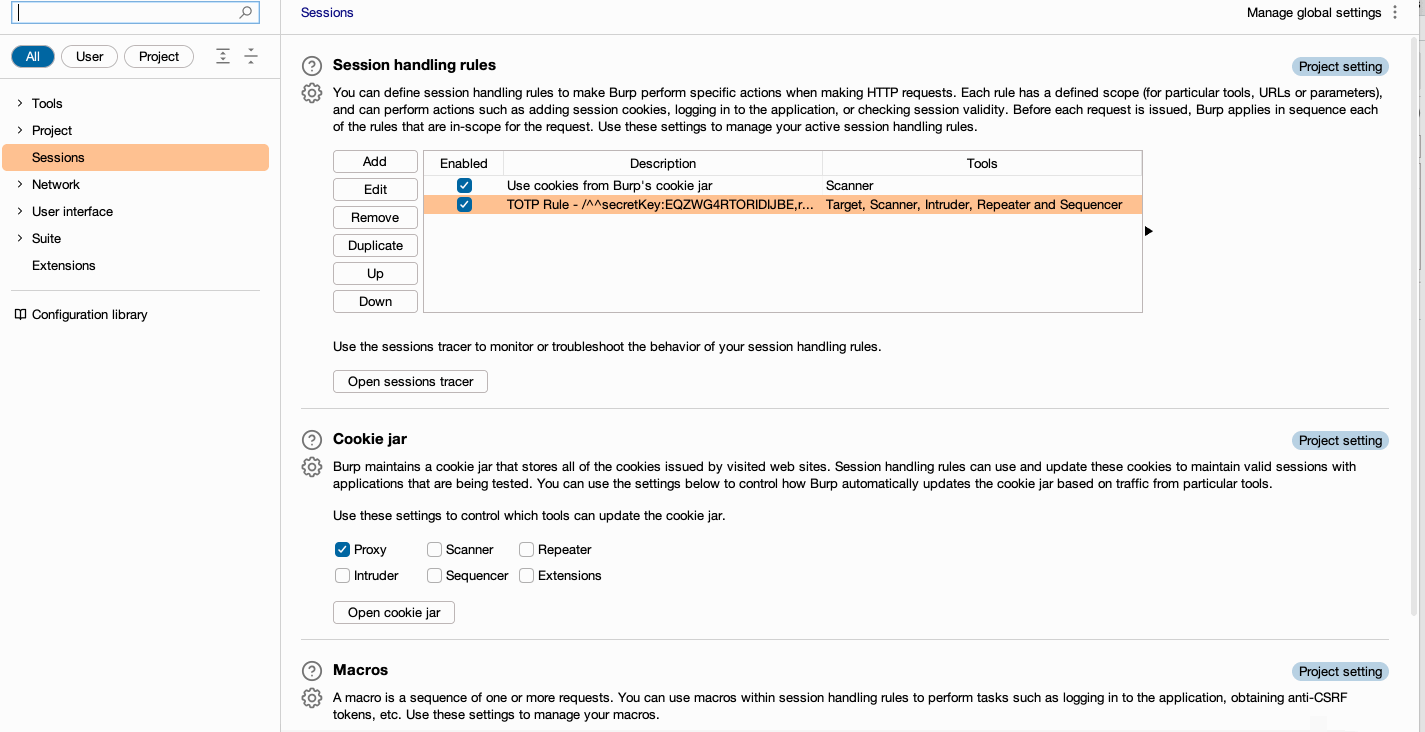 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 horkimhab/cve-2026-19516
Proof-of-concept for CVE-2026-19516, demonstrating session spoofing and SSRF in Grafana MCP. Intended for authorized security research and education…
 zjicmdarkwing/cve-2021-32099
Proof-of-concept exploit for CVE-2021-32099, a SQL injection vulnerability in Pandora FMS, demonstrating session hijacking via crafted HTTP requests.
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…