
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
custom-oscp-tooling preview

custom-oscp-tooling

GitLabwattocyber/custom-oscp-tooling

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

database-securitydns-analysishash-analysis+9
1 month ago
reconftw preview

reconftw

GitHubsix2dez/reconftw

reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…

cloud-securitydns-analysisdns-subdomain-enumeration+11
8.2k8 days ago
coraza preview

coraza

GitHubcorazawaf/coraza

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

api-securityapi-security-testingdefensive-tools+7
3.9k14h 37m ago
coreruleset preview

coreruleset

GitHubcoreruleset/coreruleset

Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
anti-botids-ips-evasionmisconfiguration+4
3.3k1 day ago
globaleaks-whistleblowing-software preview

globaleaks-whistleblowing-software

GitHubglobaleaks/globaleaks-whistleblowing-software

GlobaLeaks is a free and open-source whistleblowing software enabling anyone to easily set up and maintain a secure reporting platform.
defensive-toolsencryption-decryption-toolsprivacy+1
1.5k25 days ago
sitedorks preview

sitedorks

GitHubzarcolio/sitedorks

Search Google/Bing/Ecosia/DuckDuckGo/Yandex/Yahoo for a search term (dork) with a default set of websites, bug bounty programs or custom collection.
dns-subdomain-enumerationinformation-gatheringosint+3
1.1k1 month ago
HopLa preview

HopLa

GitHubsynacktiv/hopla

HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
ai-securityapi-security-testingpayload-generation+3
8376 months ago
PoW-Shield preview

PoW-Shield

GitHubruisiang/pow-shield

Project dedicated to fight Layer 7 DDoS with proof of work, with an additional WAF and controller. Completed with full set of features and…
web-security
4101 year ago
ftw preview

ftw

GitHubcoreruleset/ftw

YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
devsecopspenetration-testingvulnerability-scanners+2
1434 years ago
XIP preview

XIP

GitHubimmunit/xip

XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.

ids-ips-evasioninformation-gatheringpenetration-testing+2
767 years ago
OpenSSL-CCS-Inject-Test preview

OpenSSL-CCS-Inject-Test

GitHubtripwire/openssl-ccs-inject-test

This script is designed for detection of vulnerable servers (CVE-2014-0224.) in a wide range of configurations. It attempts to negotiate using each…

exploitationnetwork-securitypenetration-testing+2
3912 years ago
f5-waf-quick-patch-cve-2021-44228 preview

f5-waf-quick-patch-cve-2021-44228

GitHubirgoncalves/f5-waf-quick-patch-cve-2021-44228

This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode

api-securitycloud-securitydevsecops+3
34 years ago
CRSprober preview

CRSprober

GitHubazurit/crsprober

Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
information-gatheringpenetration-testingvulnerability-analysis+1
710 months ago
Exploit-For-CVE-2026-18963 preview

Exploit-For-CVE-2026-18963

GitHubblackhatexploitation/exploit-for-cve-2026-18963

Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
authenticationexploitationpenetration-testing+3
1 month ago
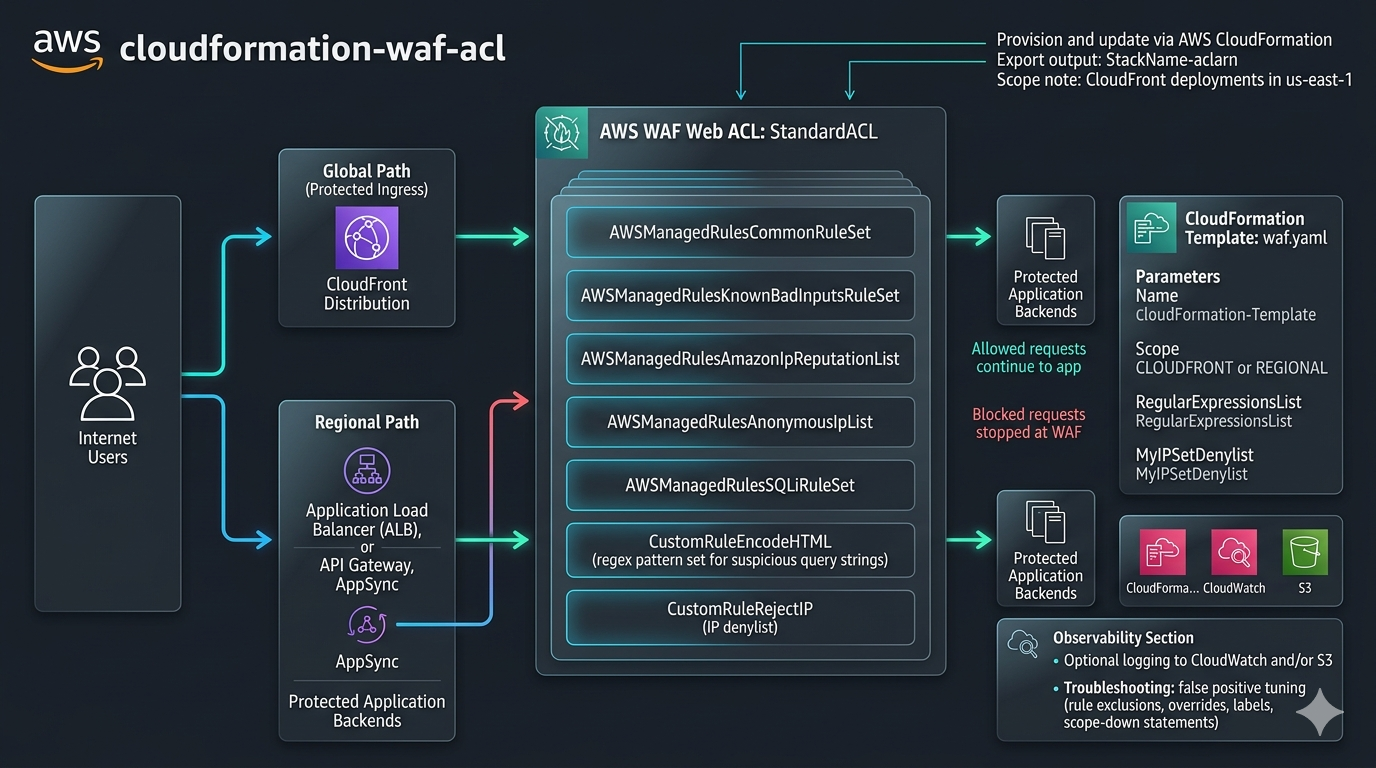
cloudformation-waf-acl preview

cloudformation-waf-acl

GitLabfer1035_aws/cloudformation/cloudformation-waf-acl

An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…
cloud-securityconfiguration-auditingmisconfiguration+2
3 months ago
wvctf preview

wvctf

GitHubsyn-4ck/wvctf

WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…

ctfeducationlabs-practice+3
12 years ago
Lab_Reportlab preview

Lab_Reportlab

GitHubonion2203/lab_reportlab

This lab was set up to test CVE-2023-33733

educationexploitationlabs-practice+2
12 years ago
CVE-2023-30212-POC-DOCKER-FILE preview

CVE-2023-30212-POC-DOCKER-FILE

GitHubrishipatidar/cve-2023-30212-poc-docker-file

This repository provides a Docker container for simulating the CVE-2023-30212 vulnerability, allowing you to practice and understand its impact. It…

educationexploitationlabs-practice+3
13 years ago
Previous123Next