
METATRON
 sooryathejas/metatron
AI-powered penetration testing assistant using local LLM on linux (Parrot OS)
ai-securityeducationexploitation+5
sooryathejas/metatronAI-powered penetration testing assistant using local LLM on linux (Parrot OS)
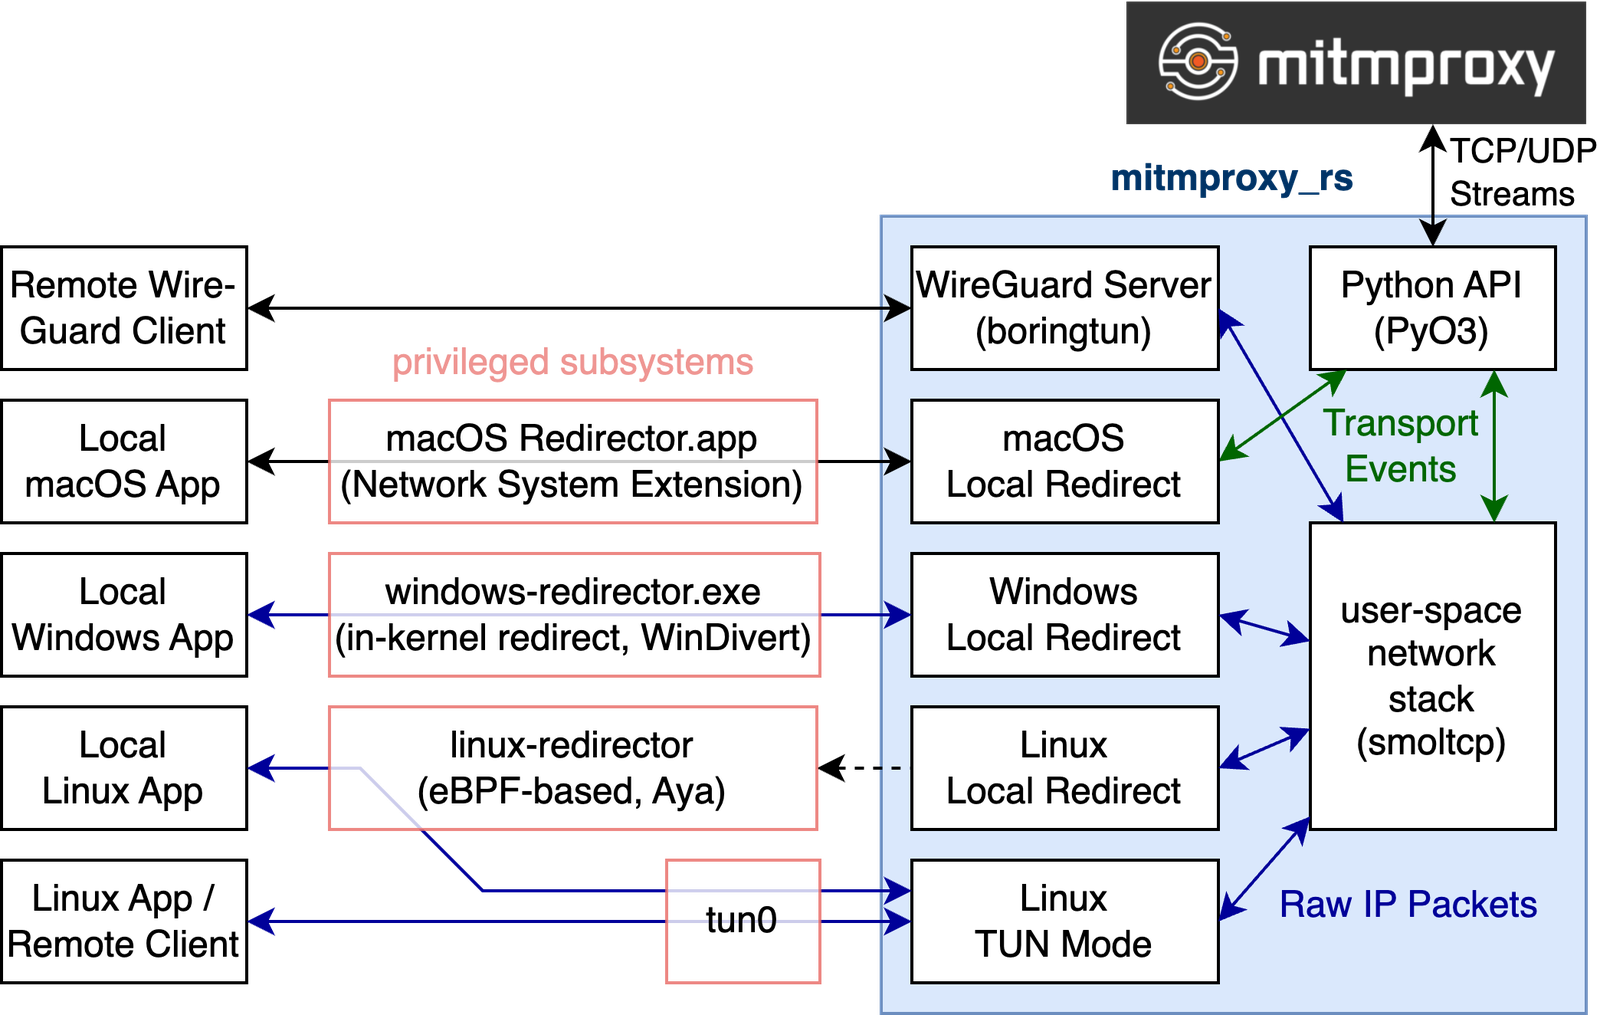 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 al1ex/cve-2020-9470
Wing FTP Server 6.2.5 - Privilege Escalation
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
 defaultnamehere/cookie_crimes
Read local Chrome cookies without root or decrypting
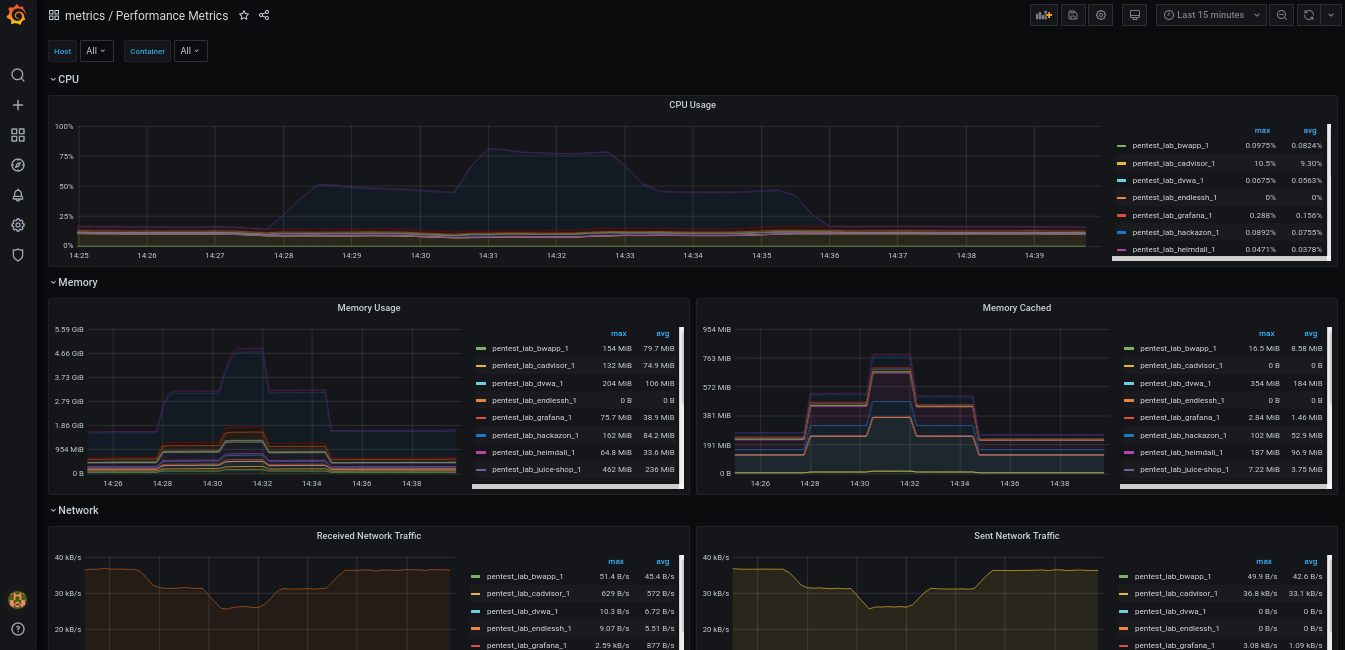 oliverwiegers/pentest_lab
Local penetration testing lab using docker-compose.
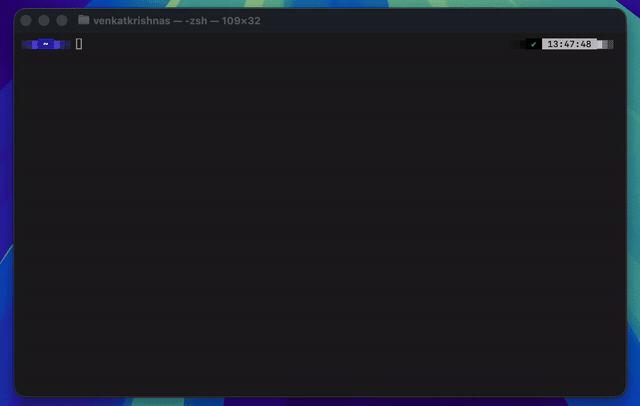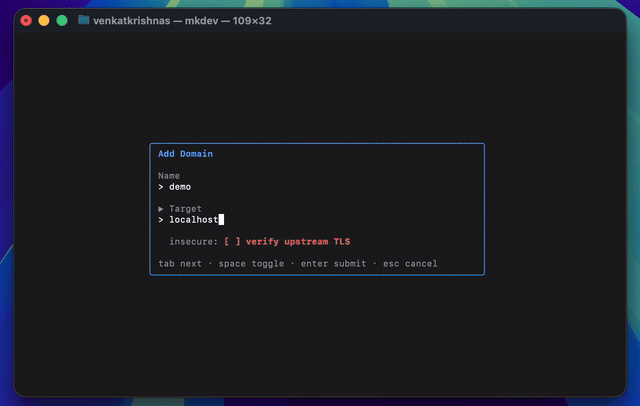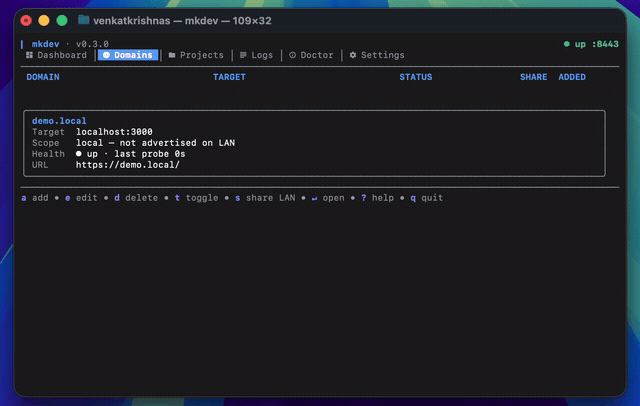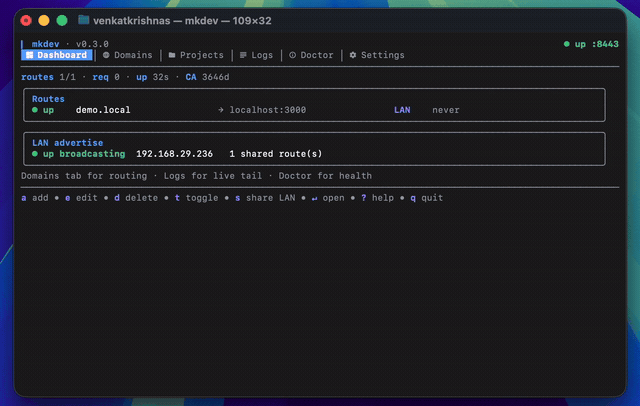 venkatkrishna07/mkdev
Trusted localhost HTTPS — local CA, /etc/hosts, mDNS LAN sharing, reverse proxy. Maps https://name.local → localhost:port
 llamakko/cve-2015-7214
Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
 mega-starmie/tomcat-cve-2025-24813-lab
Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.
 byezero/nginx-cve-2026-42945-check
Local read-only scanner for CVE-2026-42945 (NGINX Rift) that checks NGINX, OpenResty, and Tengine instances for vulnerable rewrite configurations…
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 u1tr0nex/cve-2026-40072-ssrf-lab
Hands-on lab for CVE-2026-40072 — SSRF vulnerability in web3.py via CCIP Read (EIP-3668)