
cve-2024-32002-poc
 joaoleonello/cve-2024-32002-poc
Proof of Concept for CVE-2024-32002: Git submodule path injection vulnerability.
educationexploitationpenetration-testing+3
joaoleonello/cve-2024-32002-pocProof of Concept for CVE-2024-32002: Git submodule path injection vulnerability.
 davtur19/dotgit
An extension for checking if .git is exposed in visited websites
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
 10cks/cve-2024-32002-poc
Proof-of-concept exploit for CVE-2024-32002, a Git remote code execution vulnerability triggered when cloning a malicious repository.
 10cks/cve-2024-32002-submod
Proof-of-concept exploit for CVE-2024-32002, a Git submodule remote code execution vulnerability, demonstrating malicious submodule-based clone…
 tsy244/cve-2024-32002-git-rce-father-poc
Proof-of-concept exploit for CVE-2024-32002, a Git remote code execution vulnerability, demonstrating exploitation techniques for security research…
 aitorcastel/poc_cve-2024-32002_submodule
Proof-of-concept demonstrating exploitation of CVE-2024-32002, a Git submodule vulnerability, for security research and testing.
 wadewfsssss/cve-2024-32004
Proof-of-concept exploit for CVE-2024-32004, a Git remote code execution vulnerability, demonstrating exploitation via a malicious upload-pack filter.
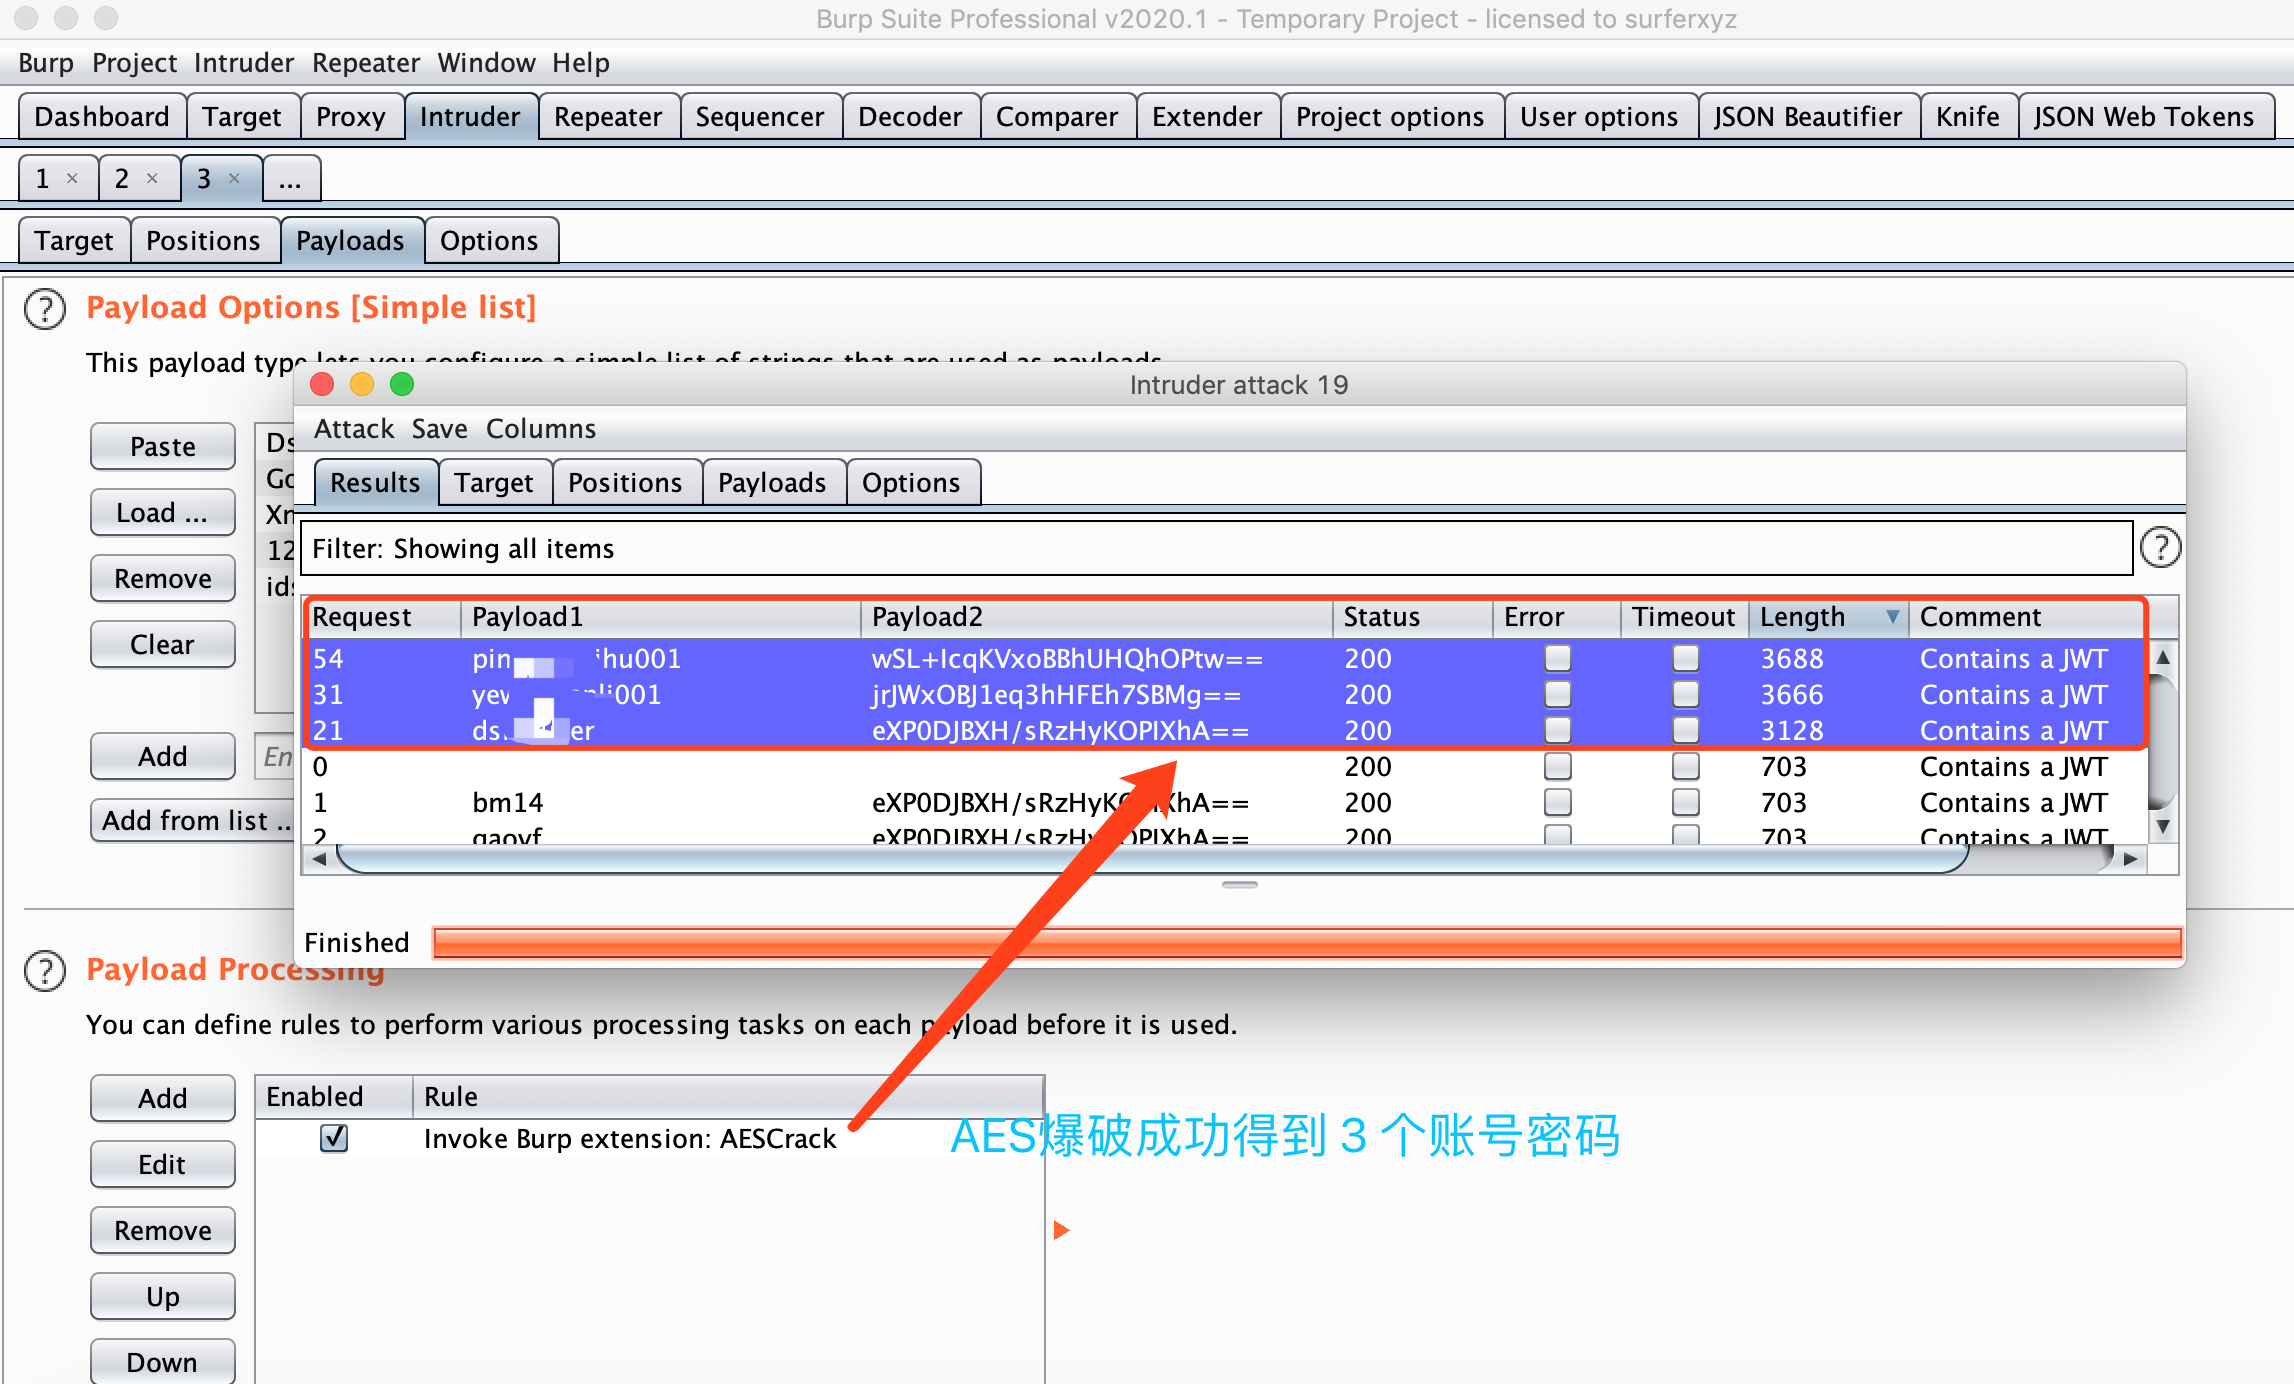 jas502n/burp_aes_plugin
Burpsuite Plugin For AES Crack
 jasalurah/creating-a-vulnerable-docker-environment-cve-2023-30212-
Docker-based vulnerable environment for practicing CVE-2023-30212 exploitation, featuring an OURPHP web app with a reflected XSS vulnerability for…
 dsnezhkov/octohook
Git Web Hook Tunnel for C2
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
 masamuneee/cve-2024-32002-poc
PoC for CVE-2024-32002: RCE via malicious git submodule hooks on case-insensitive filesystems
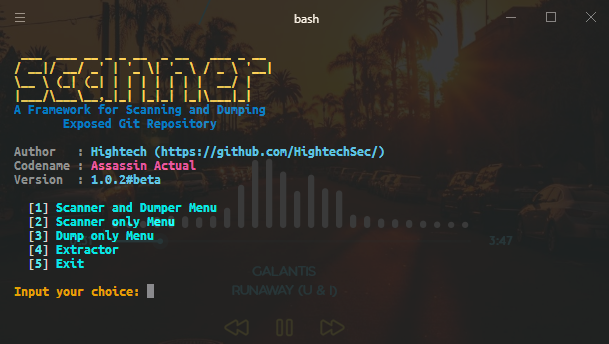 hightechsec/git-scanner
A tool for bug hunting or pentesting for targeting websites that have open .git repositories available in public
 jakob-pennington/cve-2024-32002-submodule-aw
A submodule to demonstrate CVE-2024-32002. Demonstrates arbitrary write into .git.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 ssst0n3/docker-cve-2022-39253-poc
Proof-of-concept exploit for CVE-2022-39253 demonstrating Docker container escape via malicious Git repository build, enabling host file system read…