
Wildfire
 defineid/wildfire
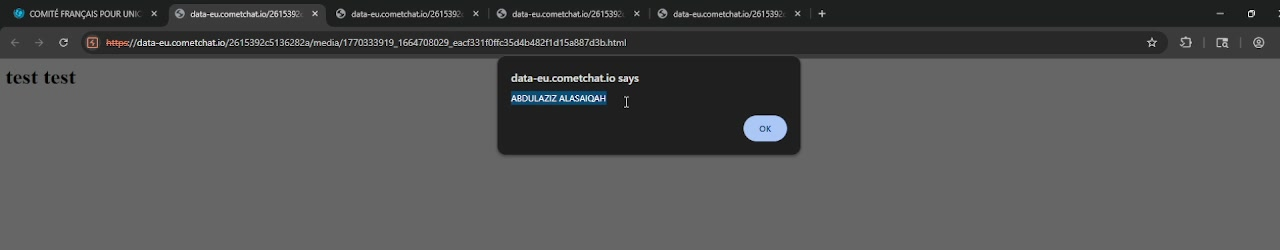
CVE-2026-39154, Stored XSS in CometChat JS SDK
api-securityexploitationpayload-development+4
defineid/wildfireCVE-2026-39154, Stored XSS in CometChat JS SDK
 hisxo/jspector
A simple Burp Suite extension to crawl JavaScript (JS) files in passive mode and display the results directly on the issues
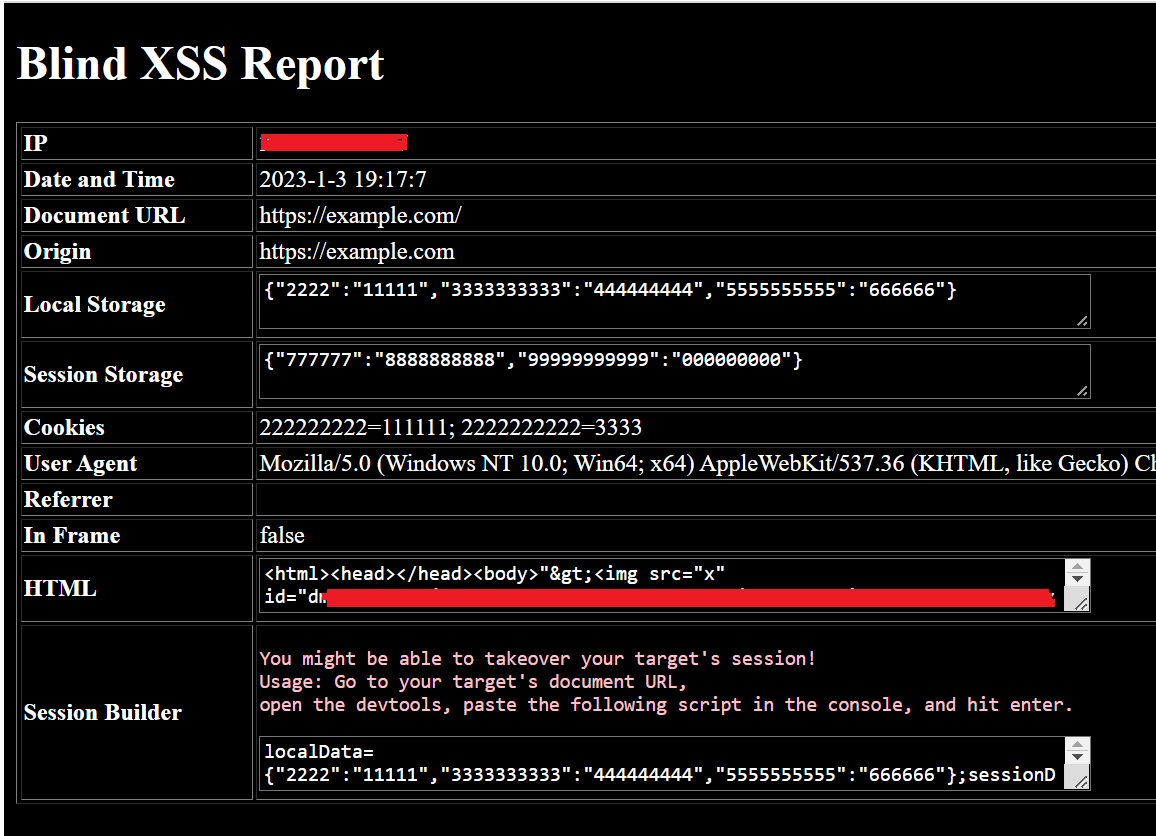 seifelsallamy/xssfire
A standalone Blind XSS Script.
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…
 brosck/mantra
「🔑」A tool used to hunt down API key leaks in JS files and pages
 sirbugs/endext
Extracts all possible endpoints, URLs, and paths from JavaScript files using customizable regex patterns for web application reconnaissance and API…
 bigzooooz/cve-2022-31298
Haraj Script 3.7 - Authenticated Stored XSS
 sohelyousef/js-secret-hunter
Automated Python scanner to detect hardcoded secrets (Private Keys, API Tokens) in client-side JavaScript files.
 anomalousvectors/cve-2024-4367-poc
POC for PDF JS' CVE-2024-4367 vuln
 spamscanner/url-regex-safe
Regular expression matching for URL's. Maintained, safe, and browser-friendly version of url-regex. Resolves CVE-2020-7661 for Node.js servers.
 dosx-dev/websafecompiler
A powerfull websites compiler/obfuscator for optimization or intellectual property protection purposes.
 9pings/cve-2022-24999
"qs" prototype poisoning vulnerability ( CVE-2022-24999 )
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
 powerscript/getdatareport
Get information client with getdatareport (Plugin)
 omidsec/cve-2018-6389
PoC Exploit CVE-2018-6389
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
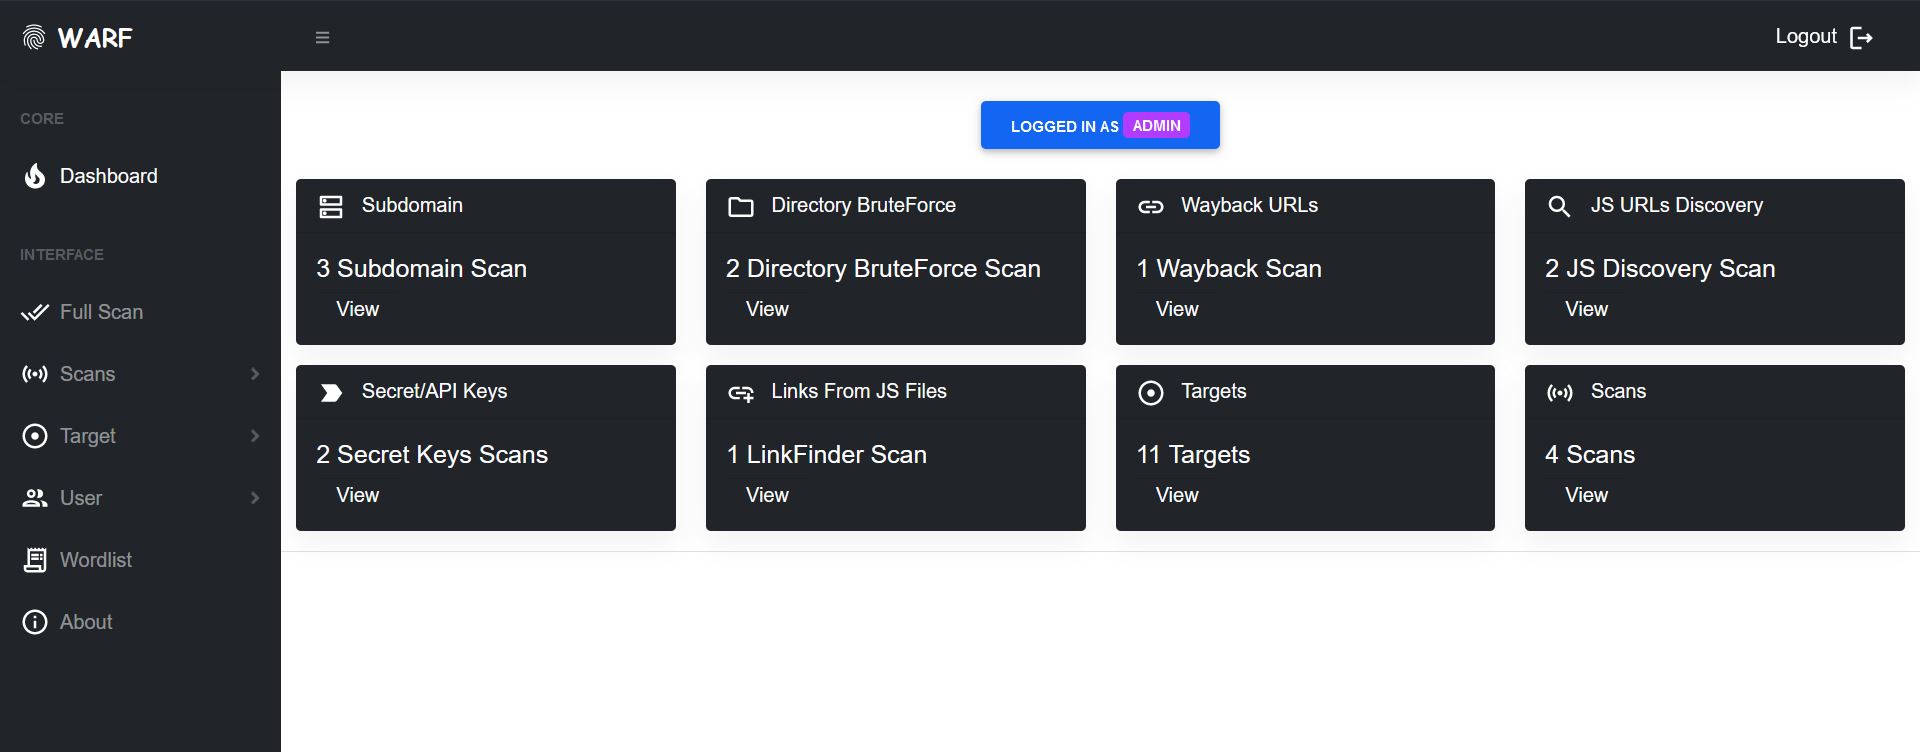 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…