
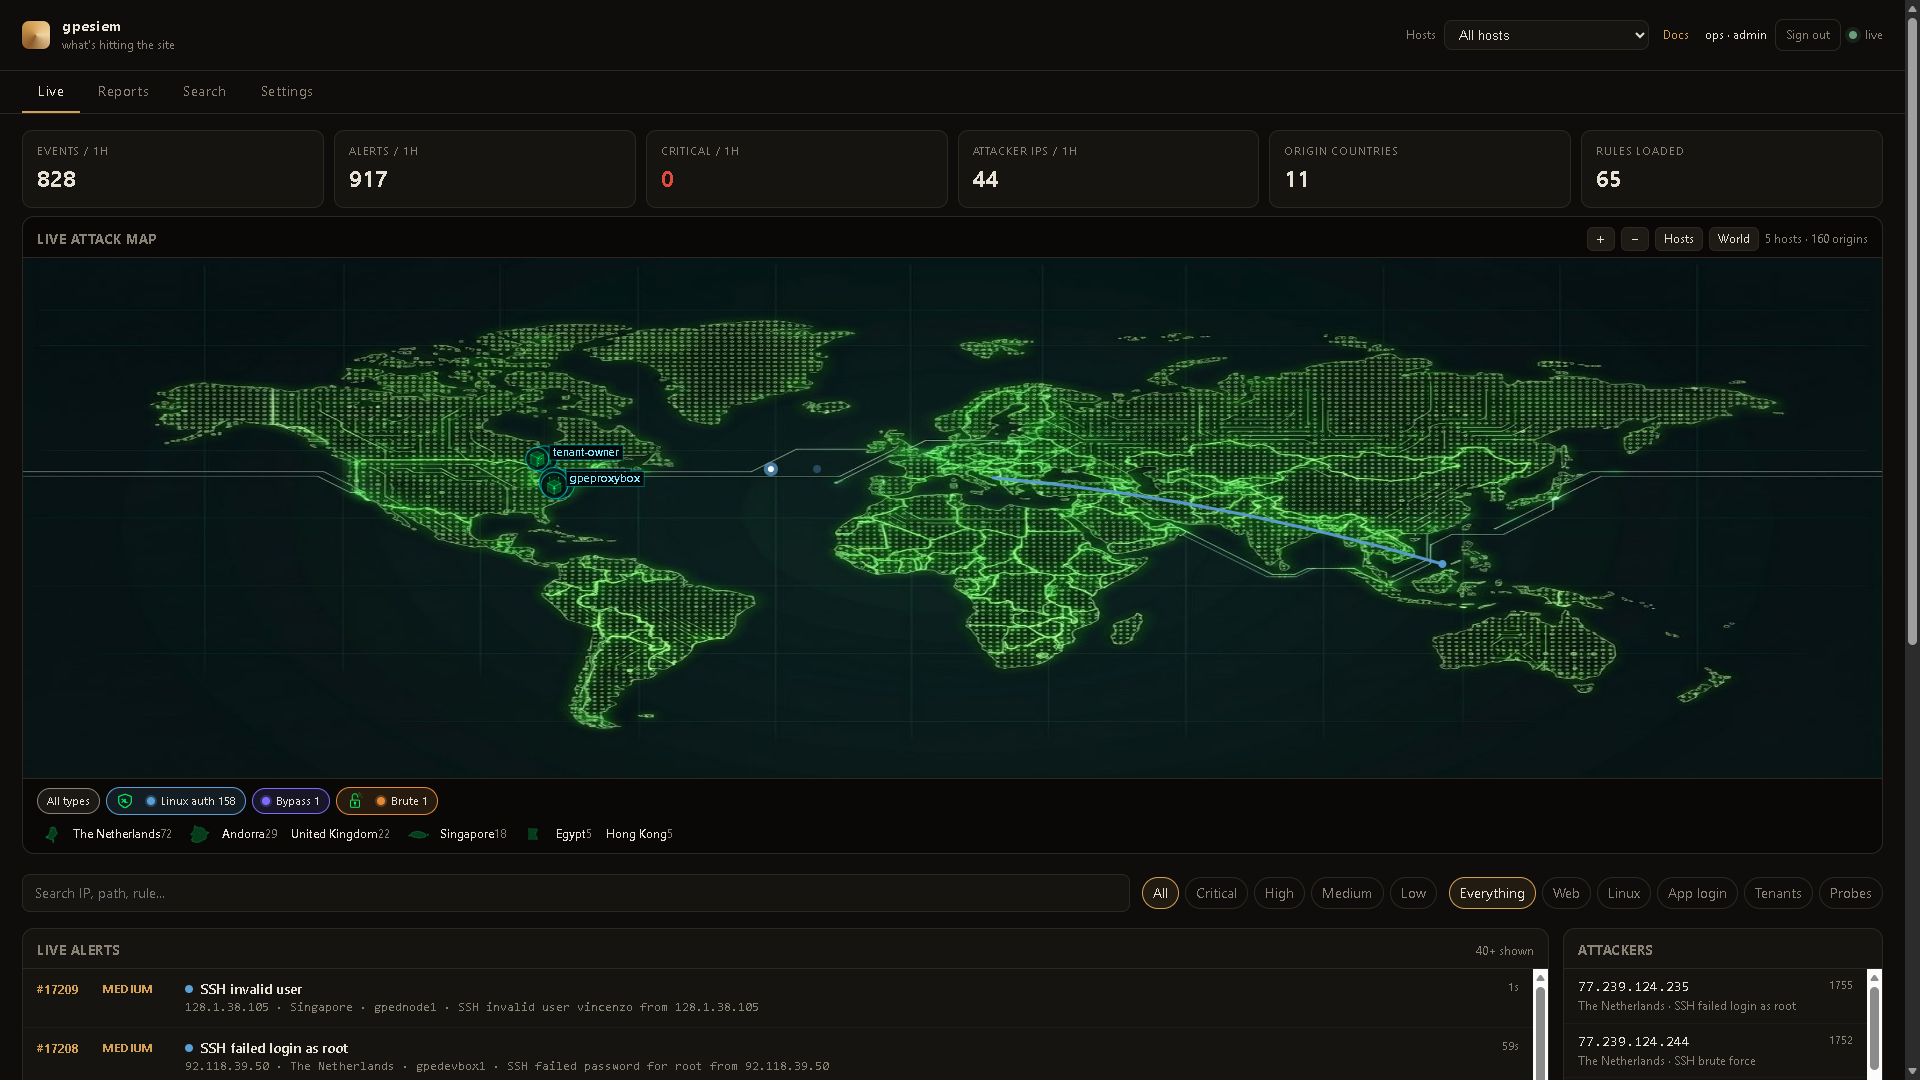
GPEWebDefender
 theretardedelon/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
anomaly-detectiondefensive-toolsintrusion-detection+2
2
theretardedelon/gpewebdefenderLightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 rverton/webanalyze
Port of Wappalyzer (uncovers technologies used on websites) to automate mass scanning.

 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 projectdiscovery/wappalyzergo
A high performance go implementation of Wappalyzer Technology Detection Library
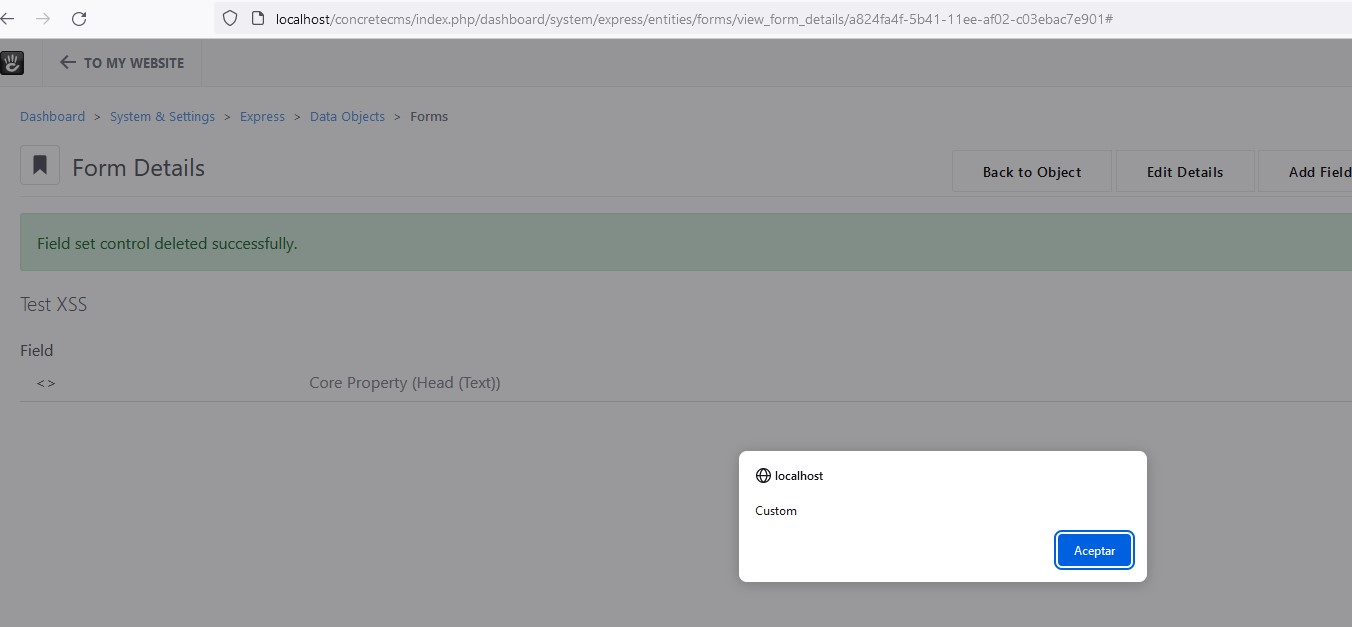 sromanhu/cve-2023-44761_concretecms-stored-xss---forms
Cross Site Scripting vulnerability in ConcreteCMS v.9.2.1 allows a local attacker to execute arbitrary code via a crafted script to the Form of the…
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 xm1k3/cent
Community edition nuclei templates, a simple tool that allows you to organize all the Nuclei templates offered by the community in one place
 alexbakker/log4shell-tools
Tool that runs a test to check whether one of your applications is affected by the recent vulnerabilities in log4j: CVE-2021-44228 and CVE-2021-45046
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 saied25/fix-react2shell-next
🔧 Fix vulnerable versions in Next.js and React RSC apps with one command to secure against CVE-2025-66478. Improve your app's safety effortlessly.
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
 leonardobg/cve-2023-36146
Proof-of-concept for authenticated stored cross-site scripting (XSS) vulnerability in Multilaser RE 170 router firmware 2.2.6733, with reproduction…
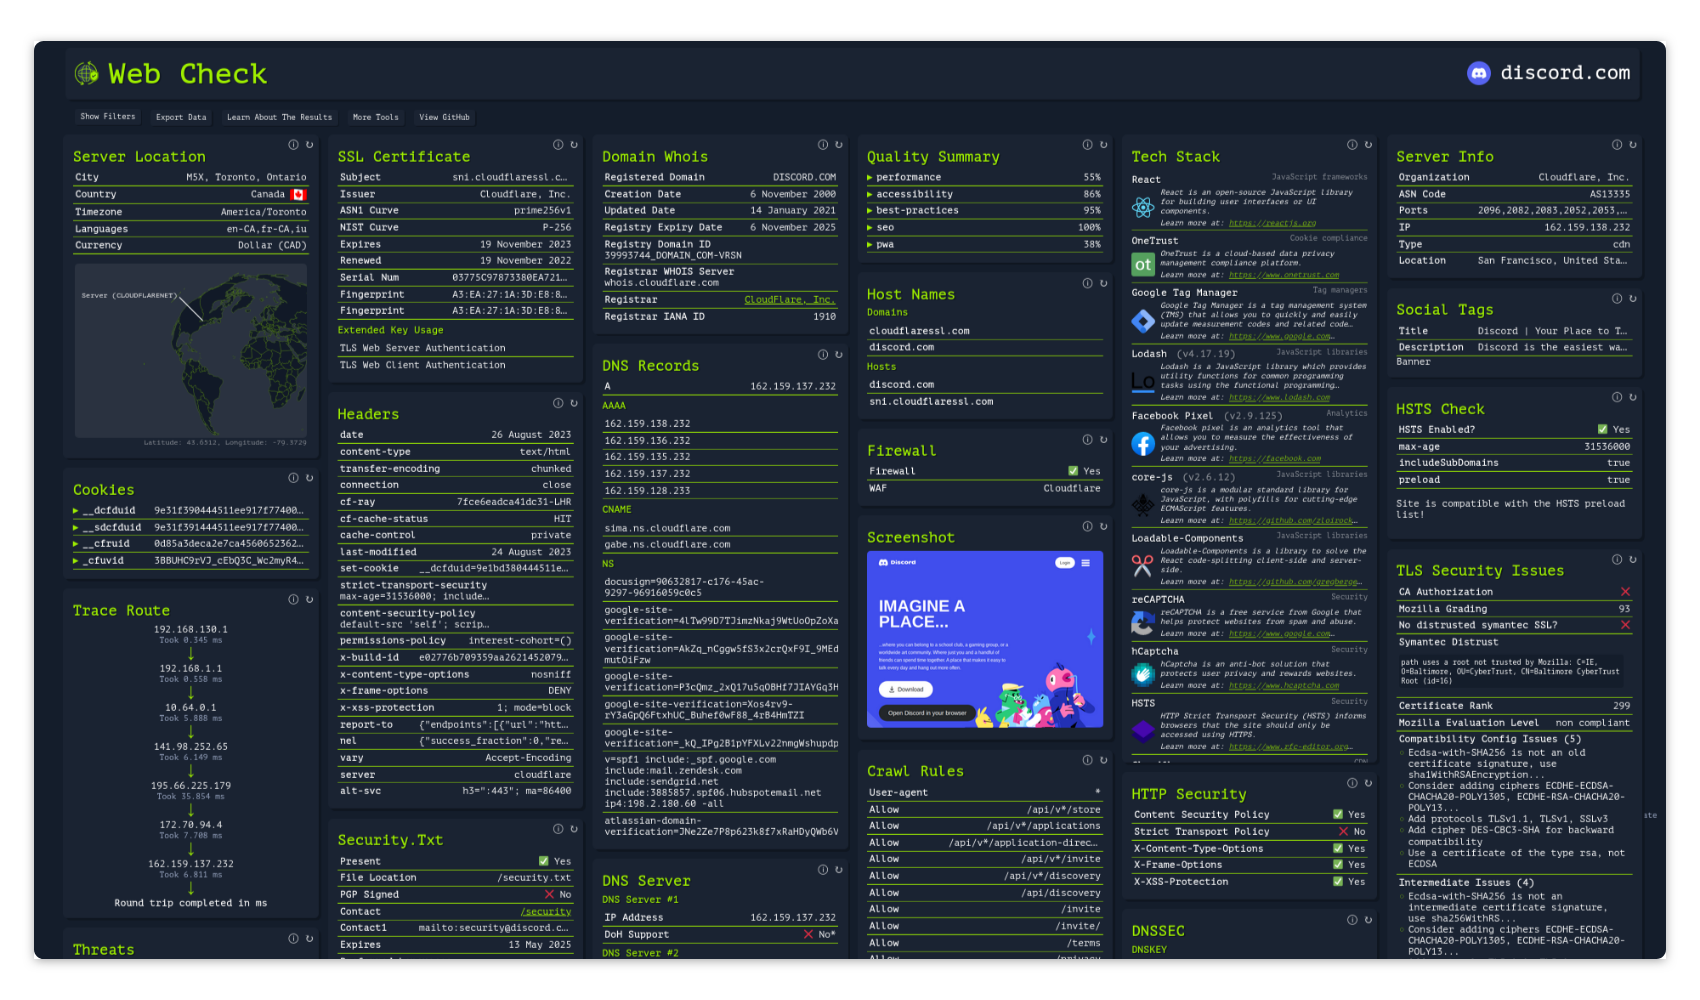 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…