
HSTP
 cagataycali/hstp
Application-layer protocol framework for trust-based, end-to-end encrypted communication across heterogeneous networks, enabling uniform service…
cryptographynetwork-securityutilities-frameworks+1
155
cagataycali/hstpApplication-layer protocol framework for trust-based, end-to-end encrypted communication across heterogeneous networks, enabling uniform service…
 tam-k592/cve-2024-40725-cve-2024-40898
CVE-2024-40725 and CVE-2024-40898, affecting Apache HTTP Server versions 2.4.0 through 2.4.61. These flaws pose significant risks to web servers…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 0xdevrel/easyscan
Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…
 defparam/haptyc
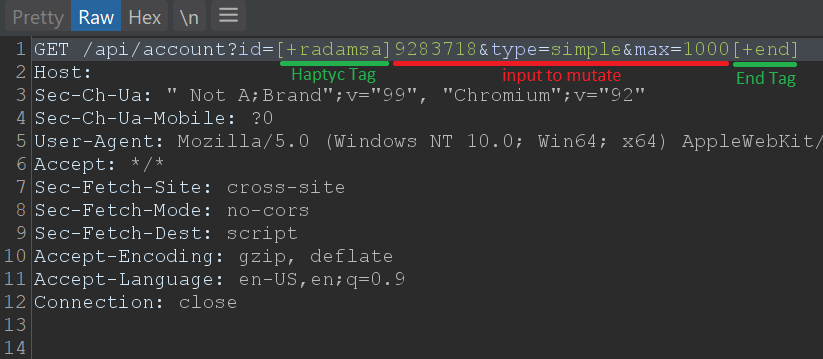
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 mrmtwoj/apache-vulnerability-testing
Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…
 thehackersbrain/cve-2021-41773
Python exploit for Apache HTTP Server 2.4.49 path traversal and remote code execution (CVE-2021-41773), enabling LFI and RCE on vulnerable servers.
 zer-far/spurt
HTTP stress testing tool that can overload web servers.
 nccgroup/vulnerabledotnethttpremoting
Example Vulnerable .NET HTTP Remoting
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
 portswigger/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
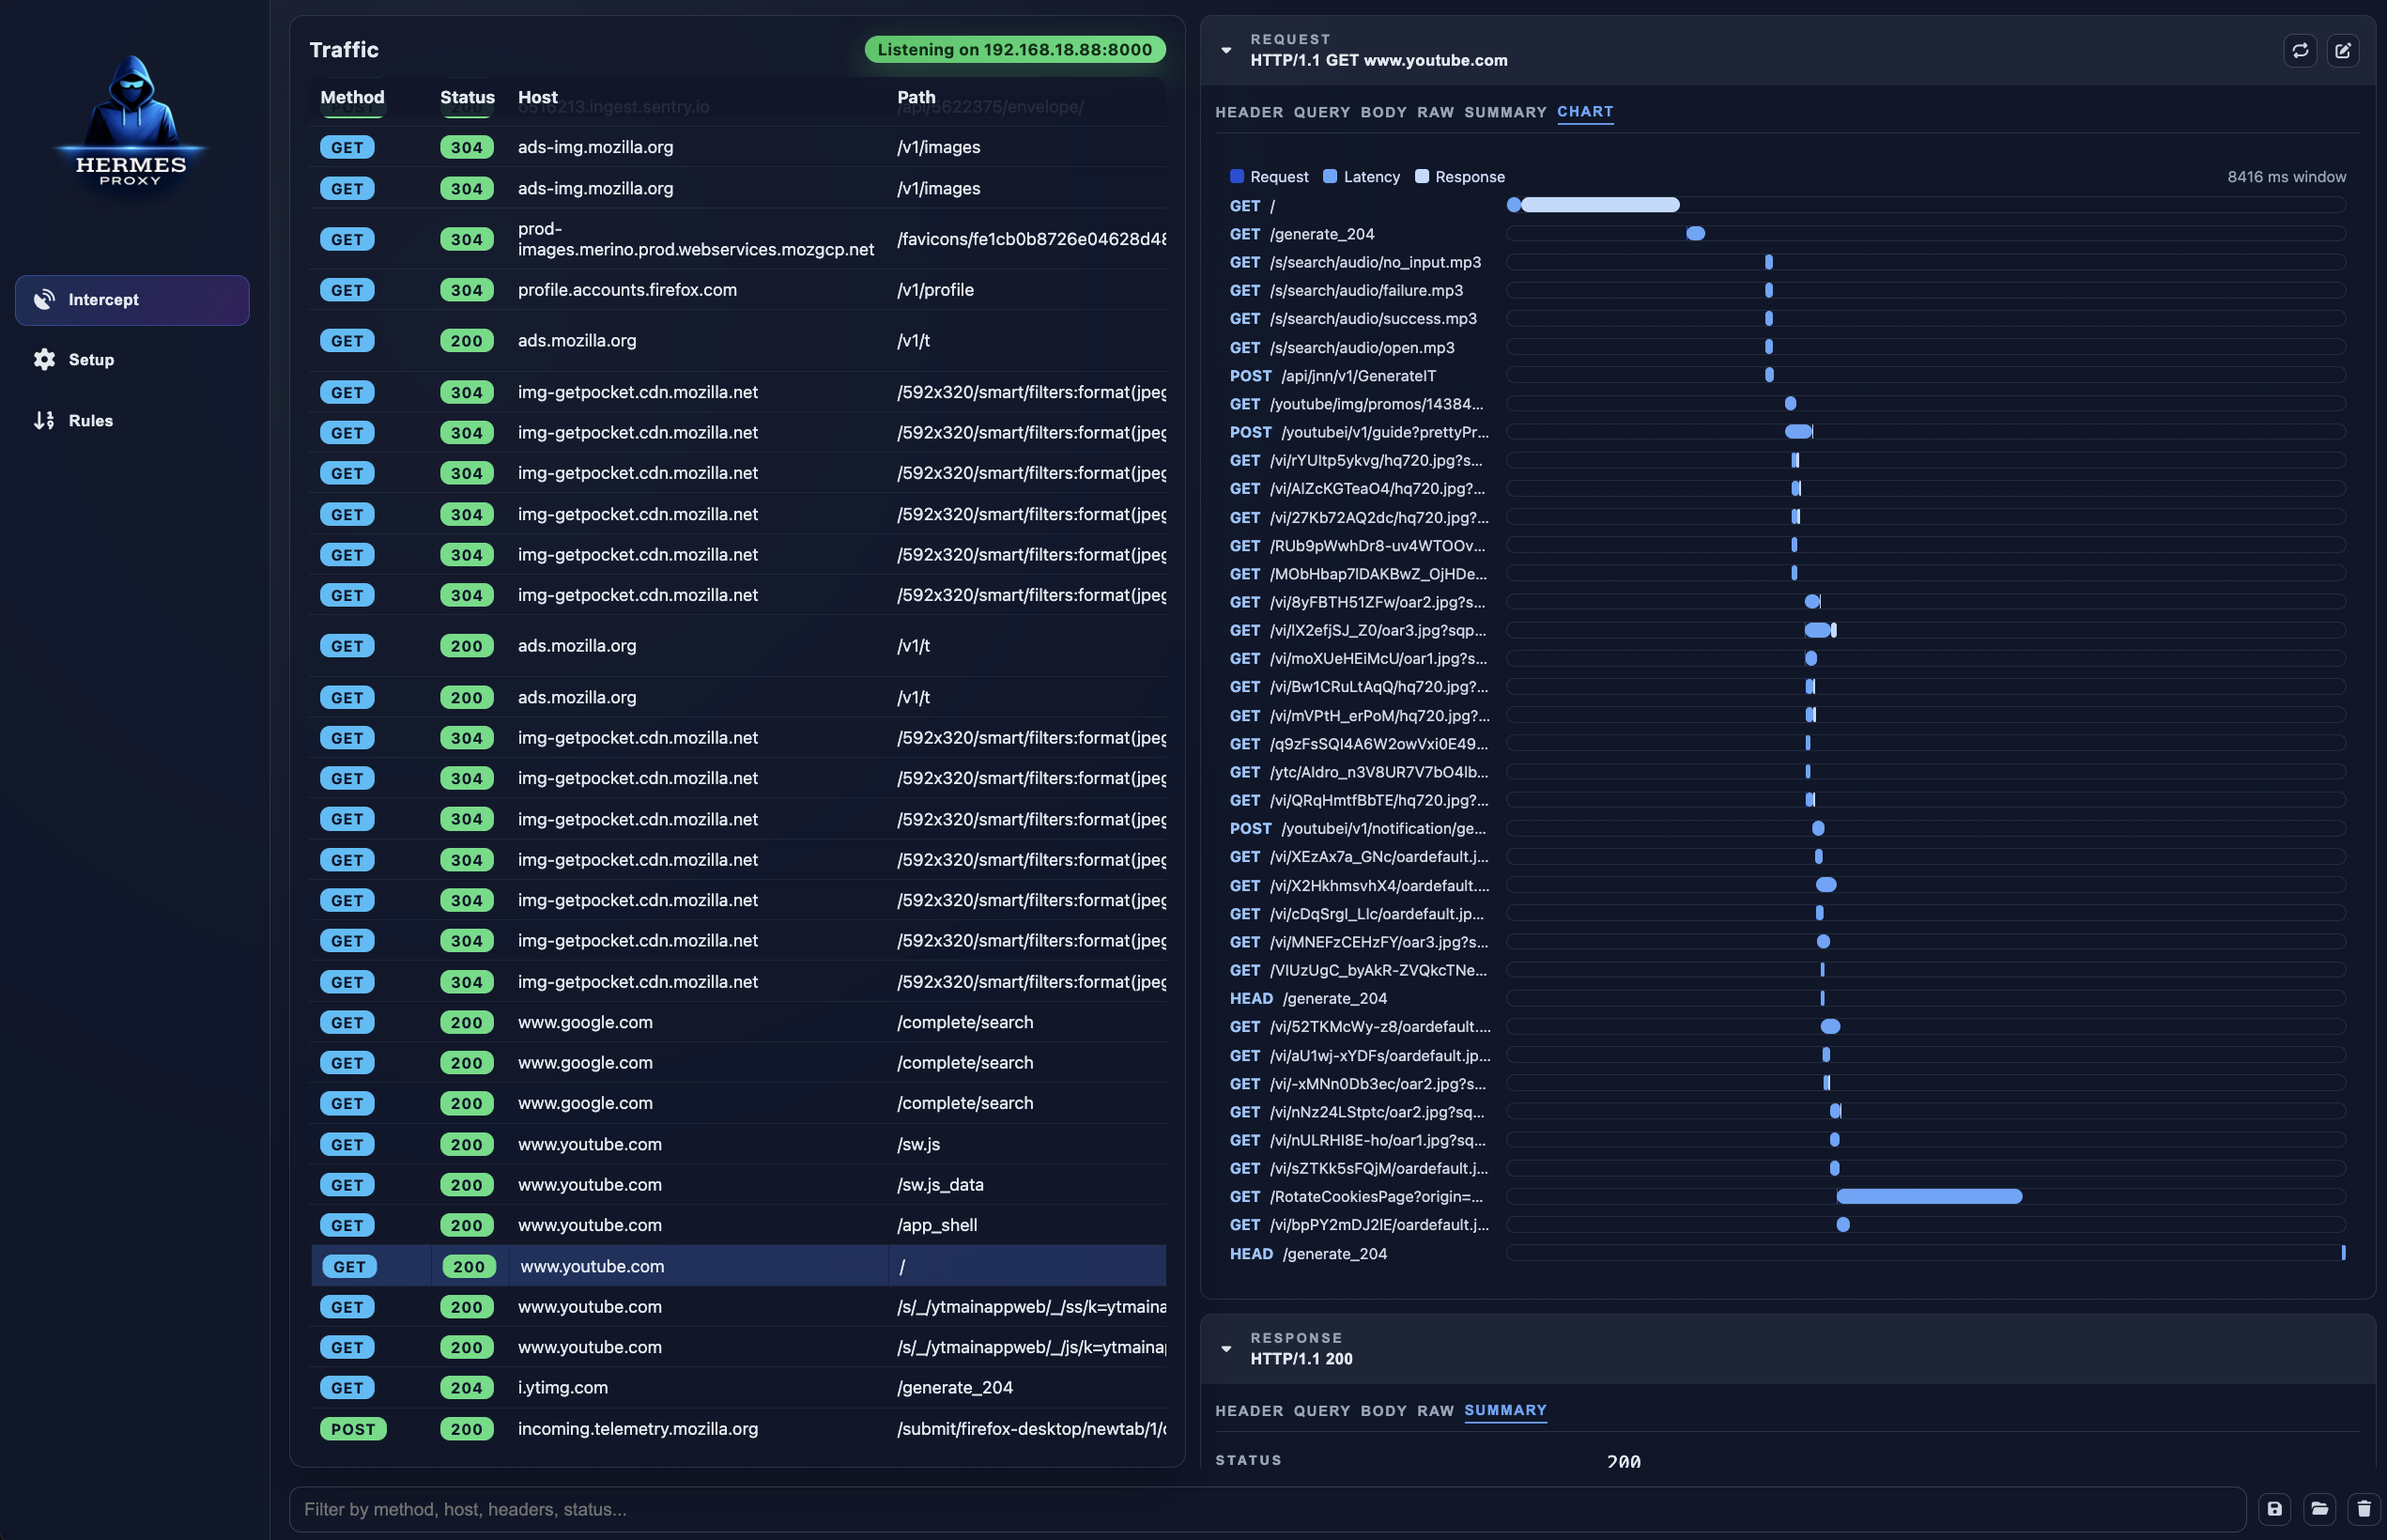 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 pownjs/cdb
Automate common Chrome Debug Protocol tasks to help debug web applications from the command-line and actively monitor and intercept HTTP requests and…
 black-scorp10/url-status-checker
Async Python CLI tool for bulk URL status checking with color-coded HTTP response categorization, IP tracking, and redirect following for web service…
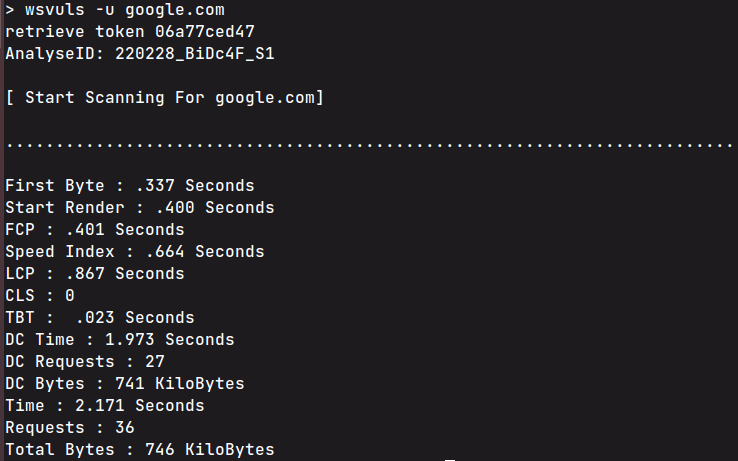 anouarbensaad/wsvuls
CLI website vulnerability scanner that detects outdated server software, insecure HTTP headers, and extracts Cloudflare IP/port data with performance…
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…