

wafw00f
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
crawlerdynamic-code-analysisinformation-gathering+6
6.6k
enablesecurity/wafw00fAutomated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
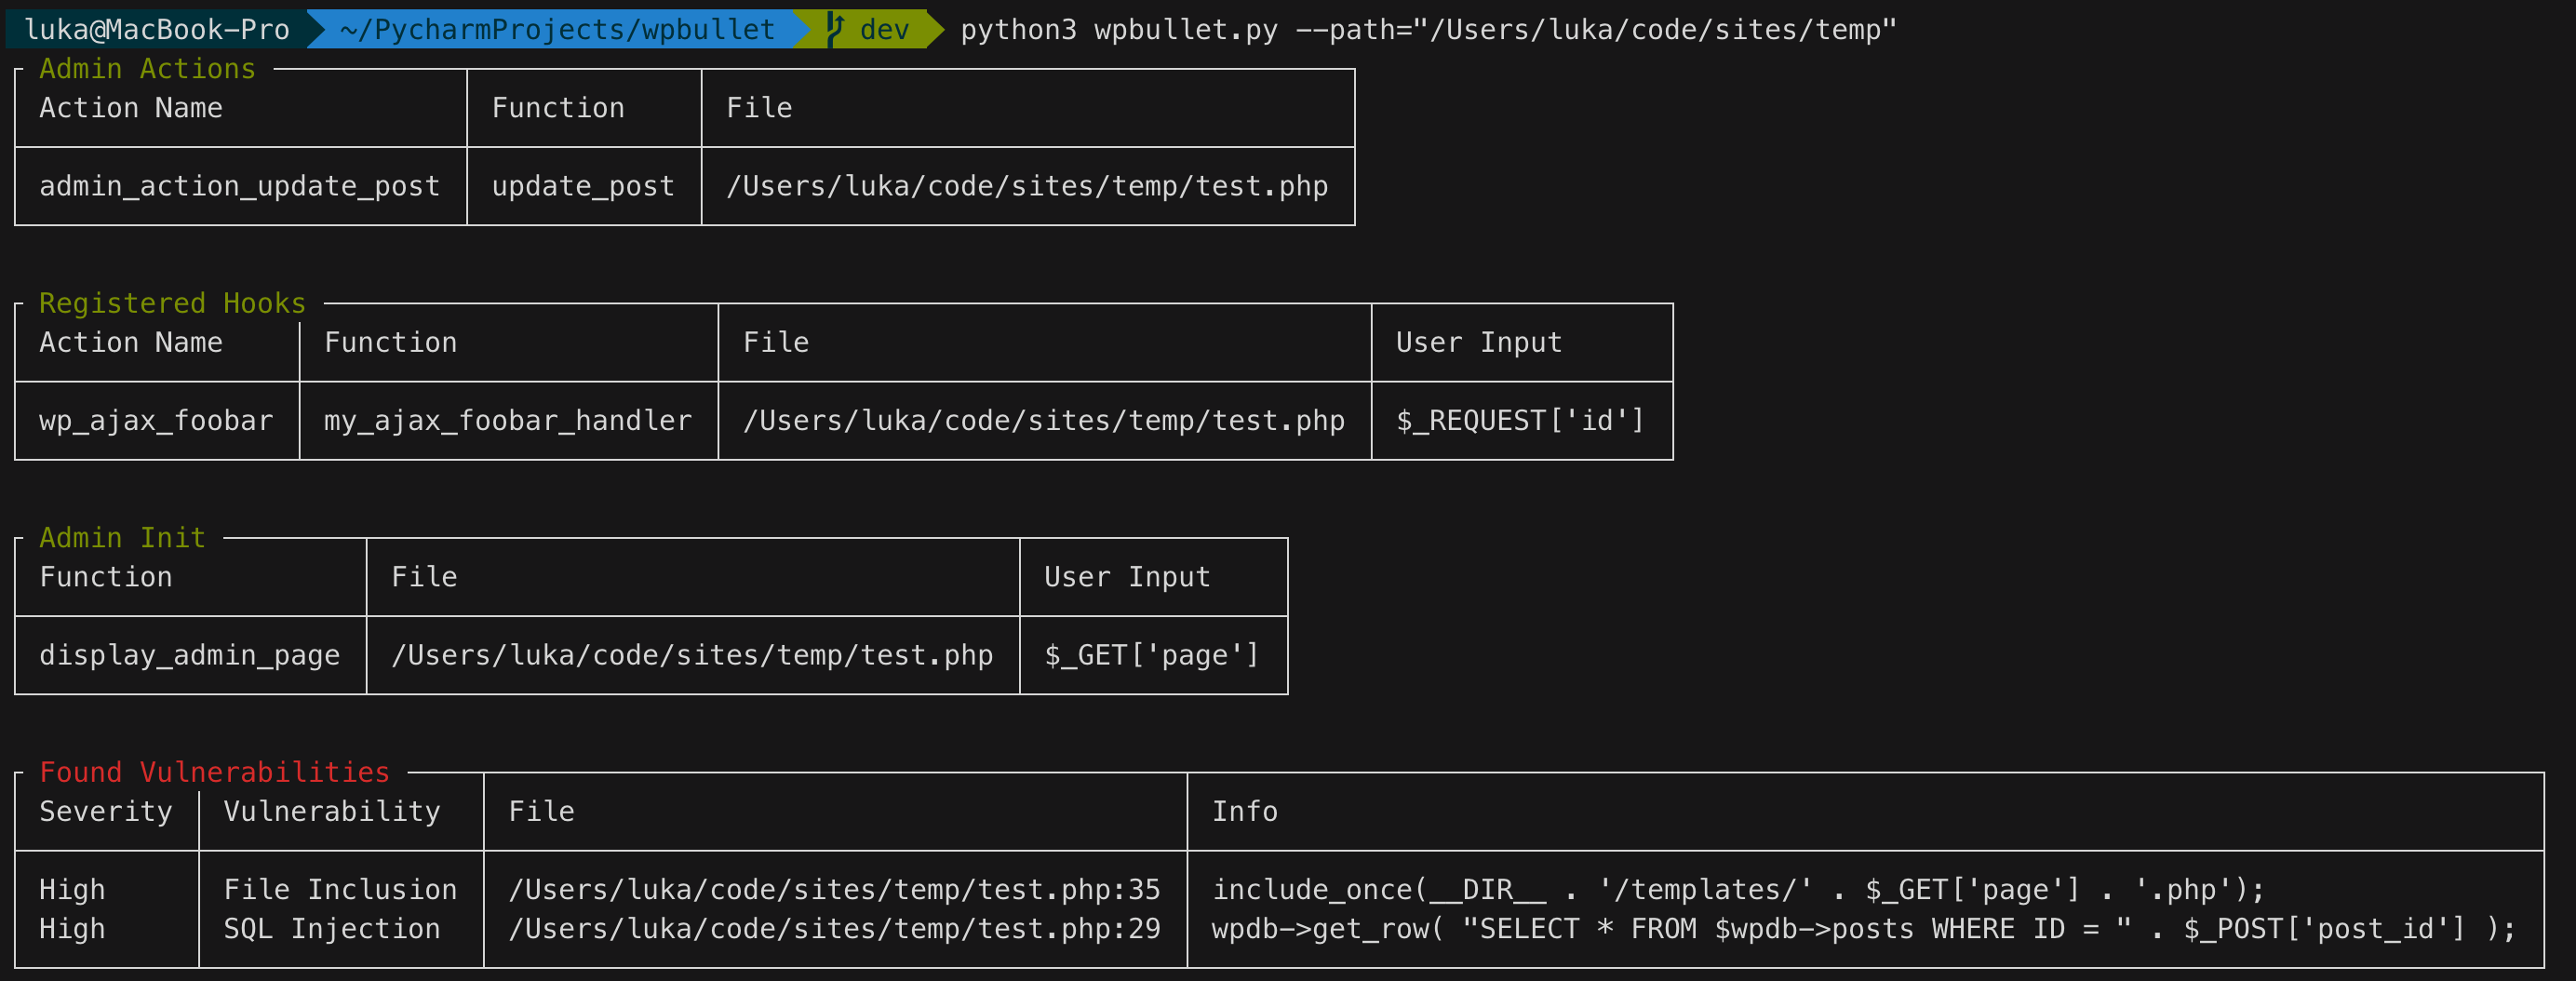 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
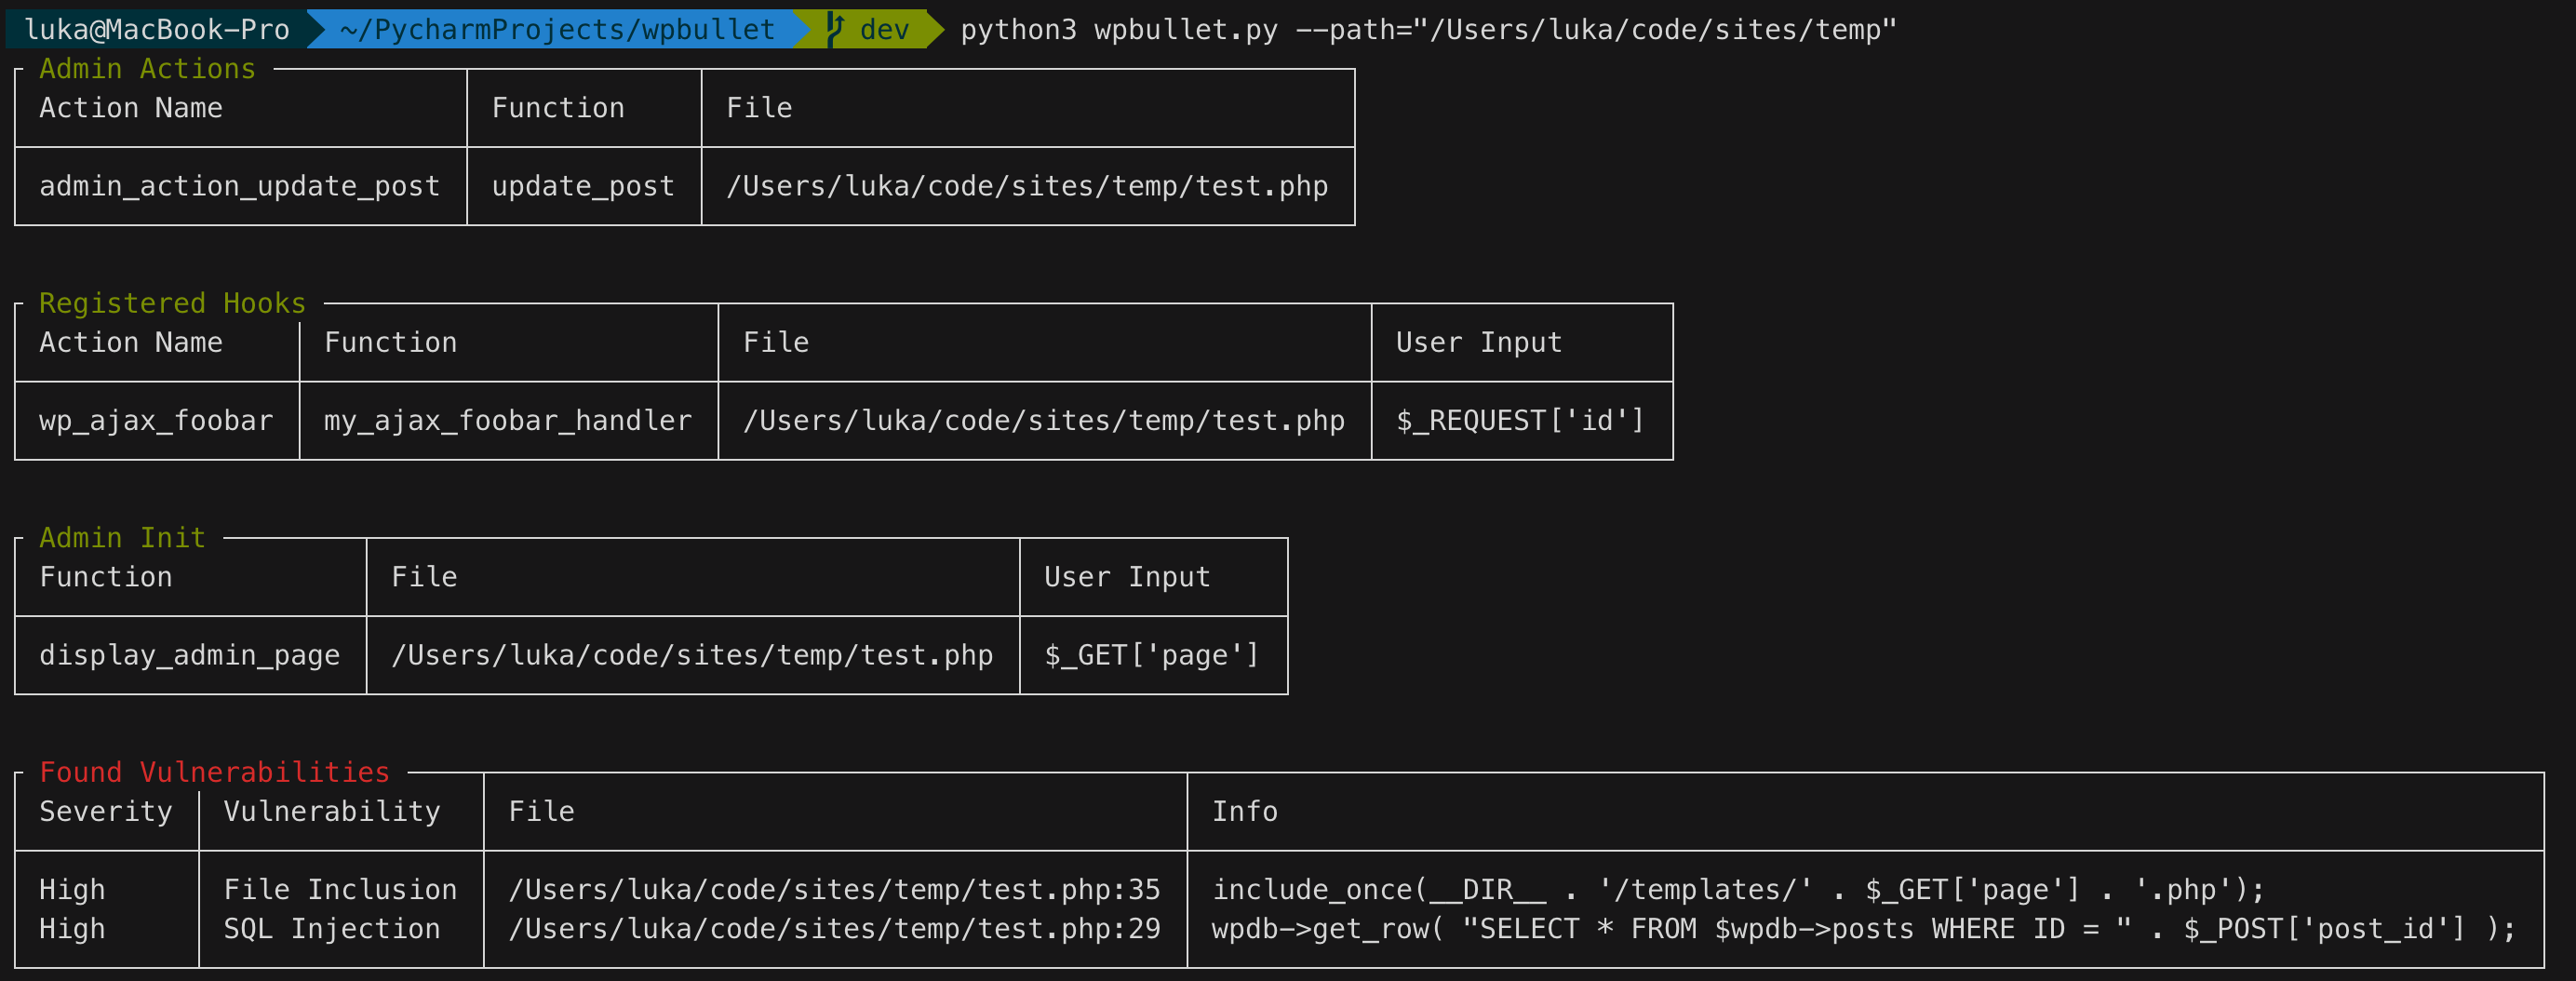 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
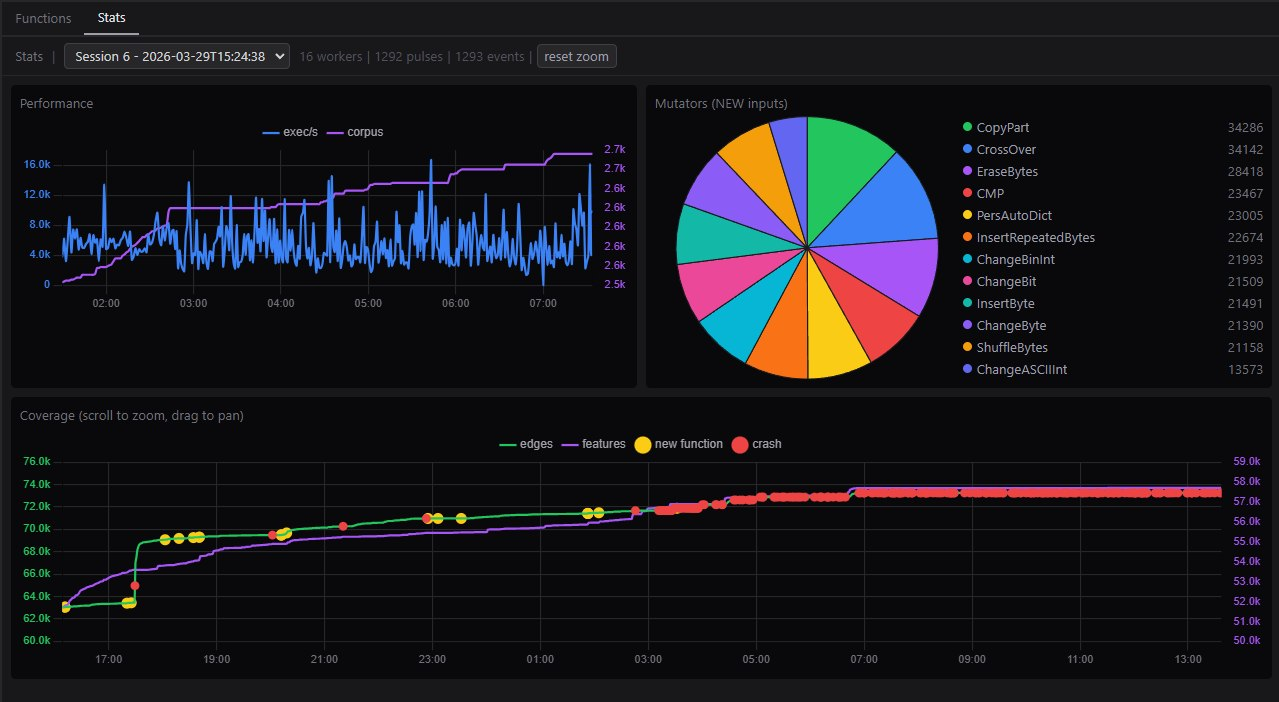 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 ntfargo/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0