

AutoRepeater
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
api-security-testingauthentication-authorizationpenetration-testing+4
895
nccgroup/autorepeaterAutomated HTTP Request Repeating With Burp Suite
 omriher/captipper
Malicious HTTP traffic explorer
 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
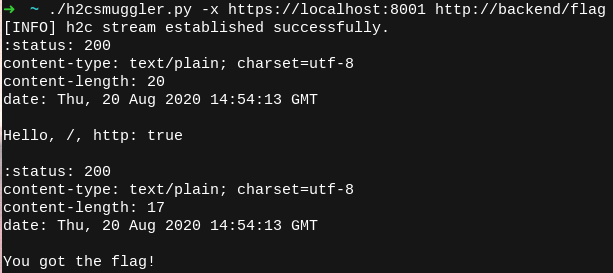 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
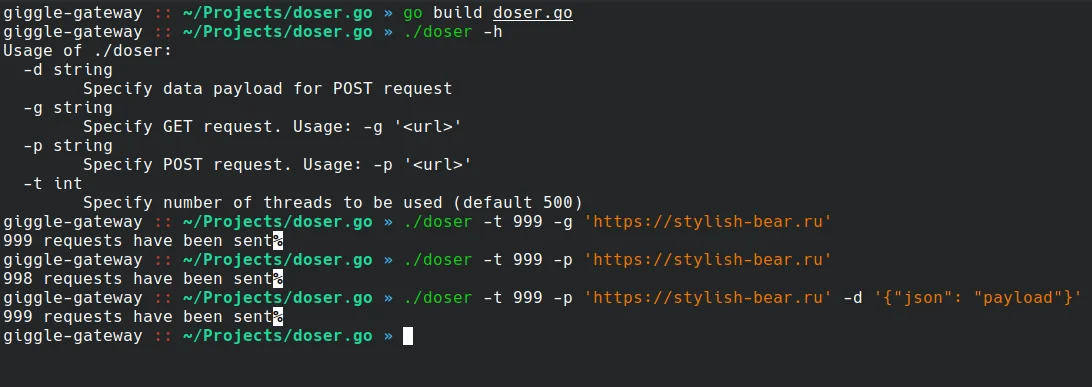 quitten/doser.go
DoS tool for HTTP requests (inspired by hulk but has more functionalities)
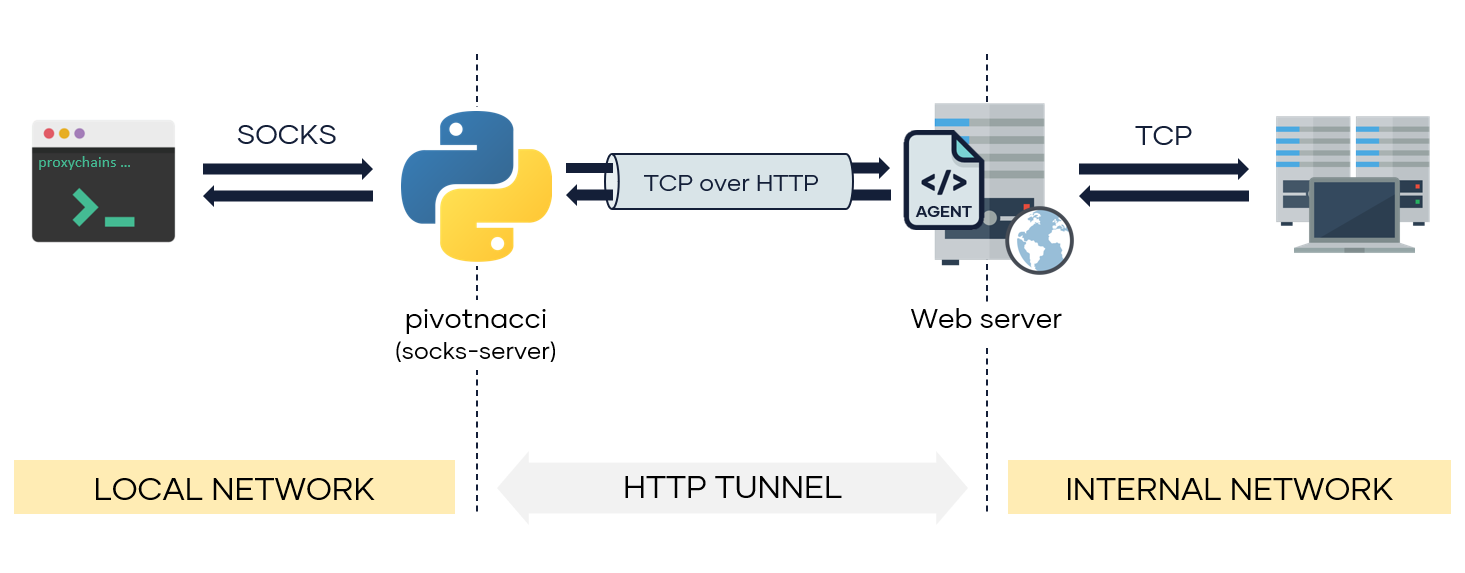 blackarrowsec/pivotnacci
A tool to make socks connections through HTTP agents
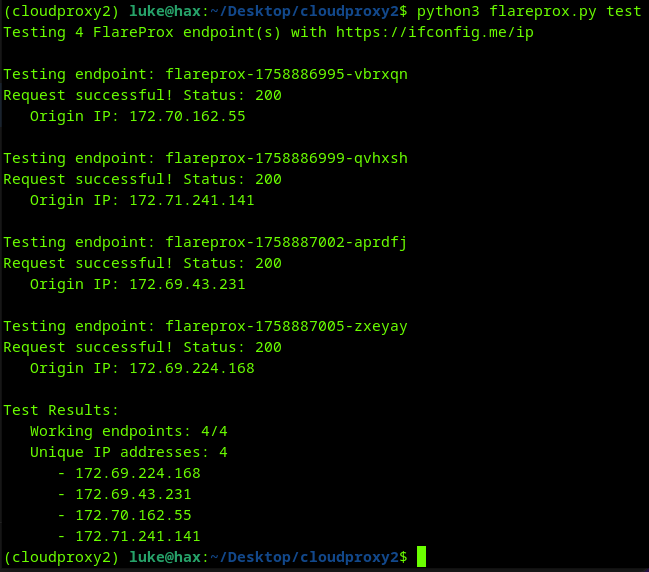 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 zz-socmap/cve-2022-21907
HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 riramar/hsecscan
A security scanner for HTTP response headers.
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 dhmosfunk/cve-2023-25690-poc
CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…
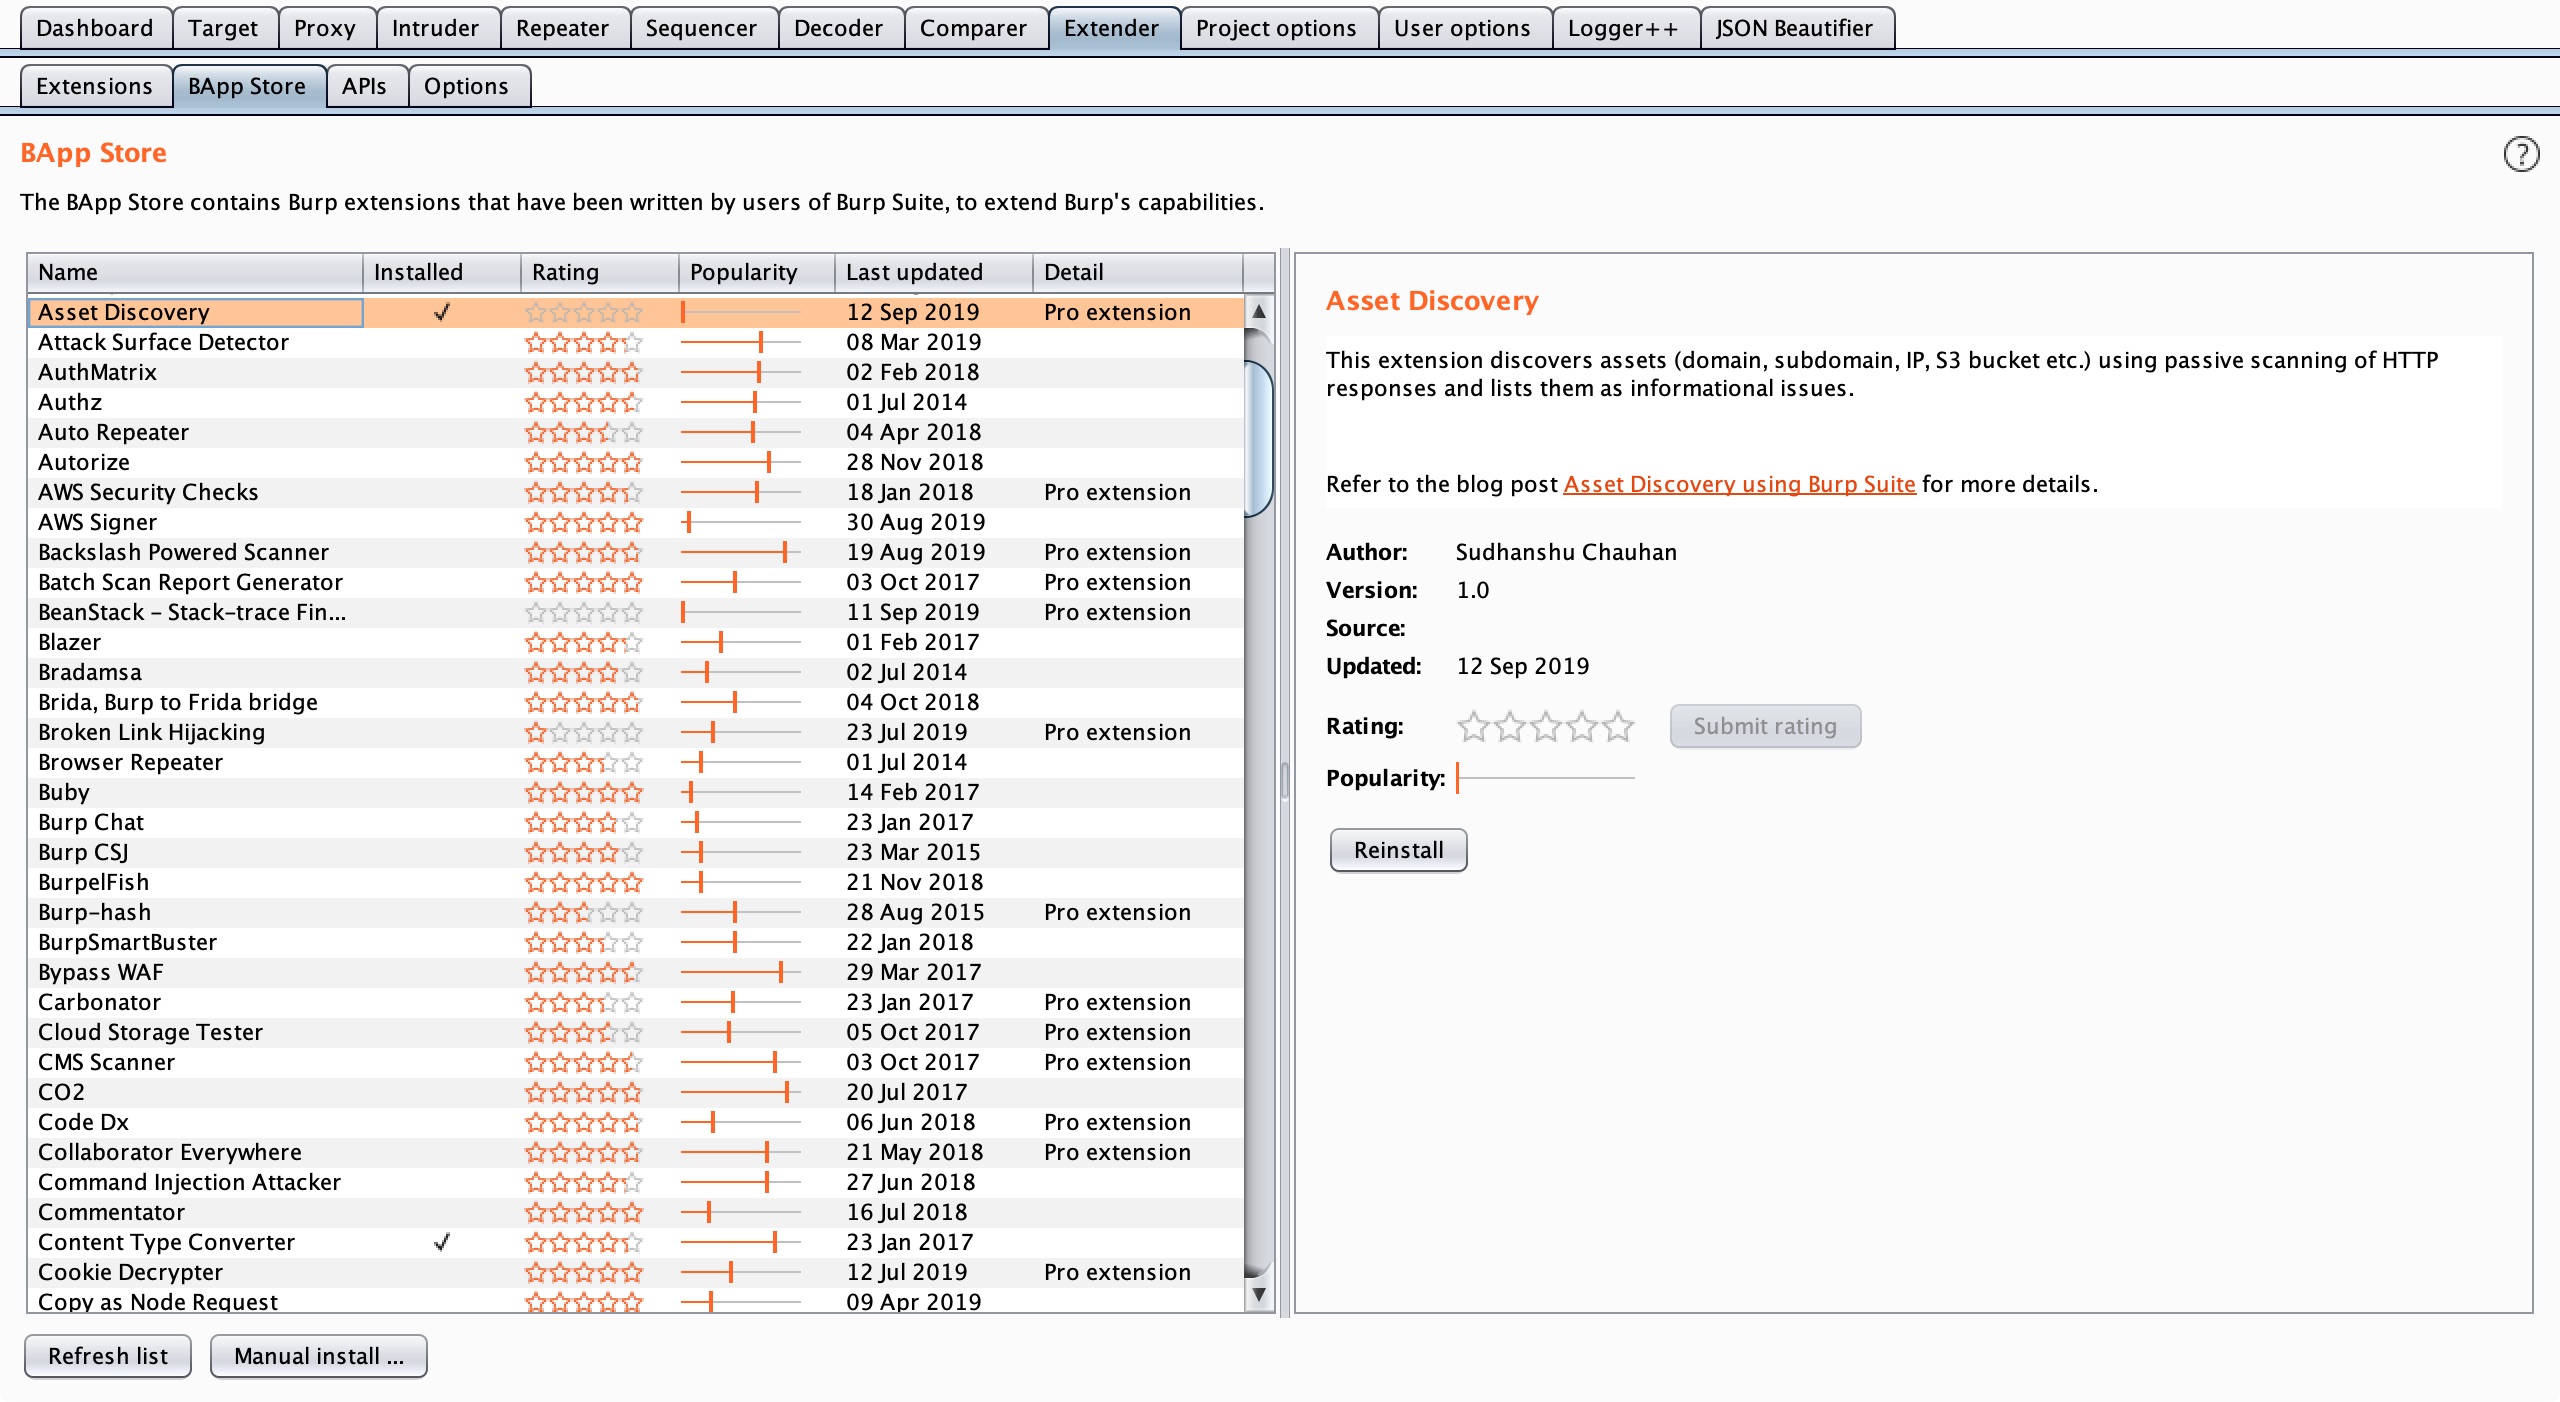 redhuntlabs/burpsuite-asset_discover
Burp Suite extension to discover assets from HTTP response.
 assetnote/surf
Filters host lists to identify viable SSRF candidates by probing HTTP reachability and resolving internal/external IPs, bypassing traditional…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.