
bunkerweb
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
anti-botcloud-securitycontainer-security+6
10.9k
bunkerity/bunkerweb🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
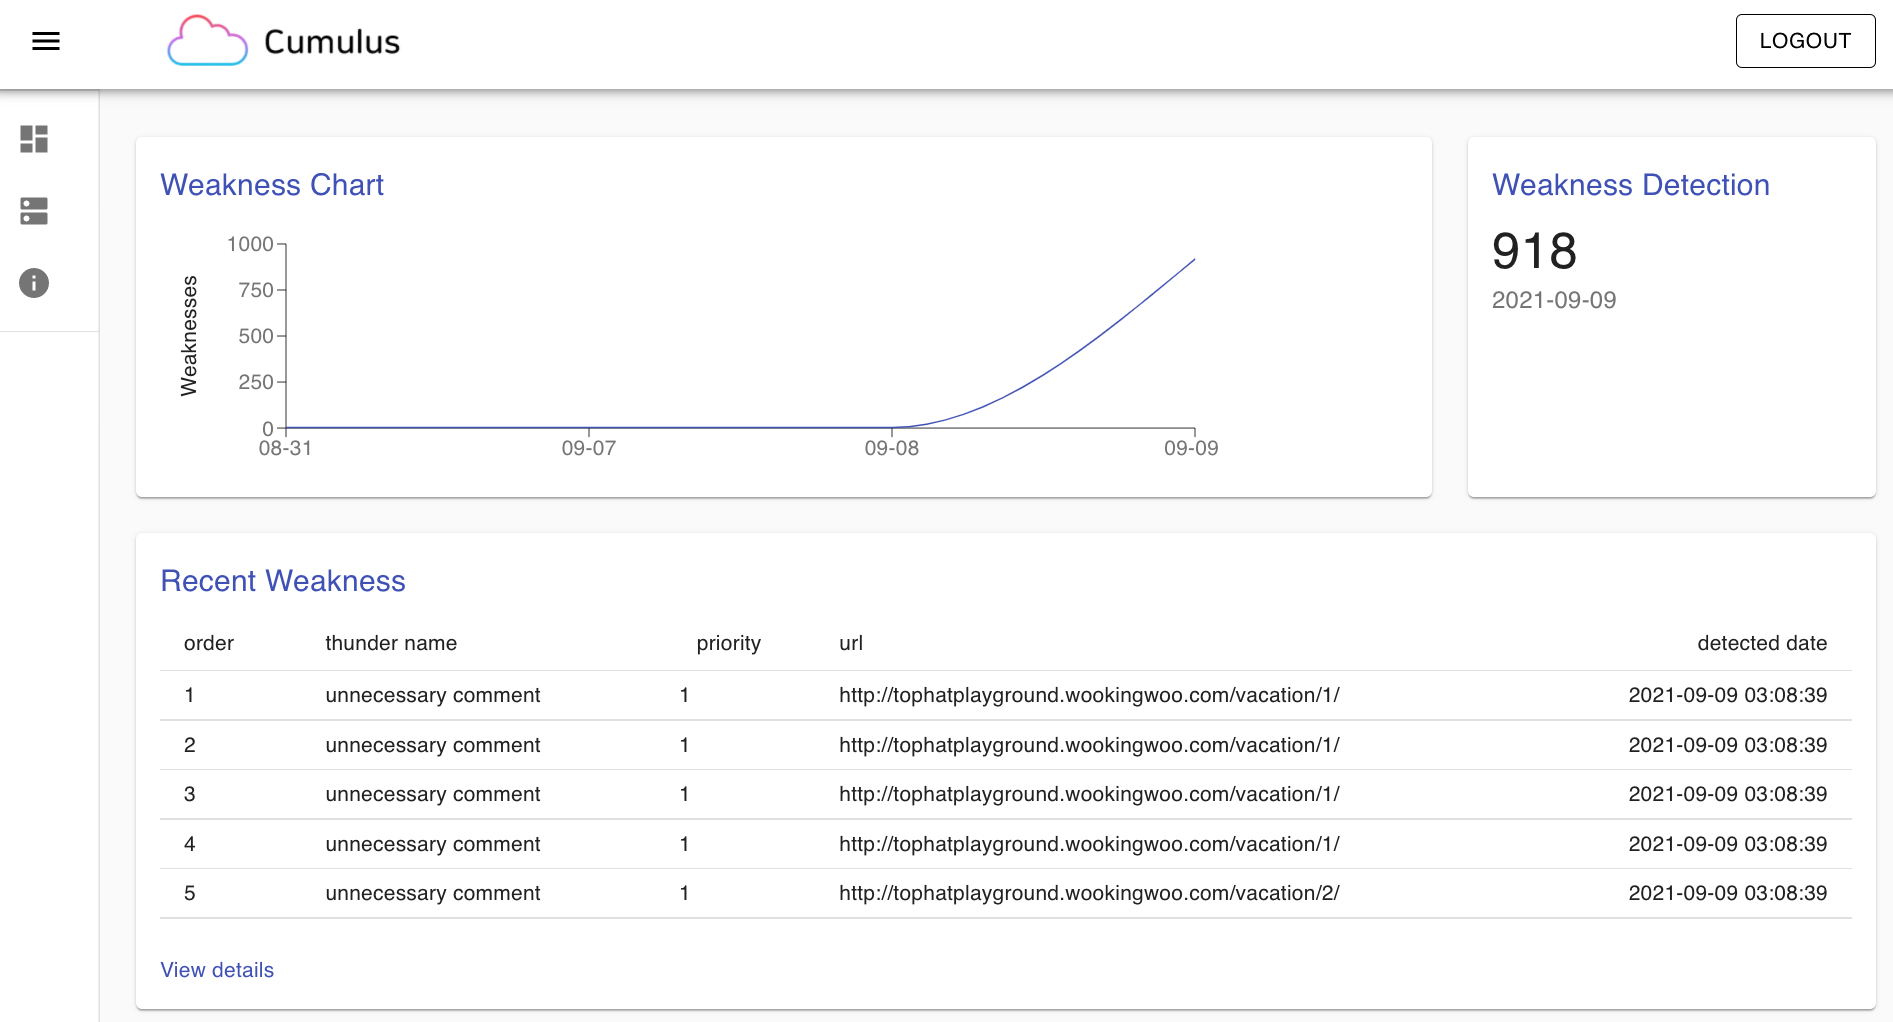 tophat-cloud/cumulus
Real-time web application weakness monitoring SDK and scanner. Detects XSS, SQL injection, sensitive payloads, and code vulnerabilities via dynamic…
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
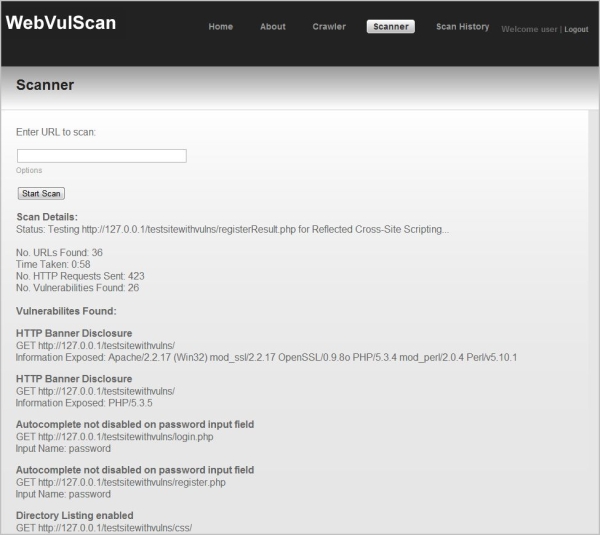 dermotblair/webvulscan
Web Application Vulnerability Scanner.
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 an5i/cve-2025-64446-fortiweb-exploit
Security research tool for detecting and testing CVE-2025-64446 (FortiWeb Path Traversal RCE vulnerability)
 rohan-pt/cve-2025-26054
CVE-2025-26054
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 kuzushiki/cve-2025-29927-test
Test application for CVE-2025-29927, designed for security study groups to demonstrate and verify the web vulnerability in a controlled environment.
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 deepankarkumar1/cve-2025-55182_vulnerable-application
Intentionally vulnerable React Server Components lab for studying CVE-2025-55182. Provides a safe environment for security researchers, developers,…
 nccgroup/tracy
A tool designed to assist with finding all sinks and sources of a web application and display these results in a digestible manner.
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…
 ruisiang/pow-shield
Project dedicated to fight Layer 7 DDoS with proof of work, with an additional WAF and controller. Completed with full set of features and…
 evilsocket/altair
Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…