Ruby-On-Rails-Path-Traversal-Vulnerability-CVE-2018-3760-

Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…

Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

CVE-2024-38475 exploitation & scanning tool with Mullvad VPN rotation

Anti-Anti-Automation Framework

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

Python SQL injection framework

A free and open source command-line shell and scripting language designed especially for security testing

nginx CVE scanner + RCE exploit framework (CVE-2026-42945 + 16 others)

Orchestration component of purpleteam


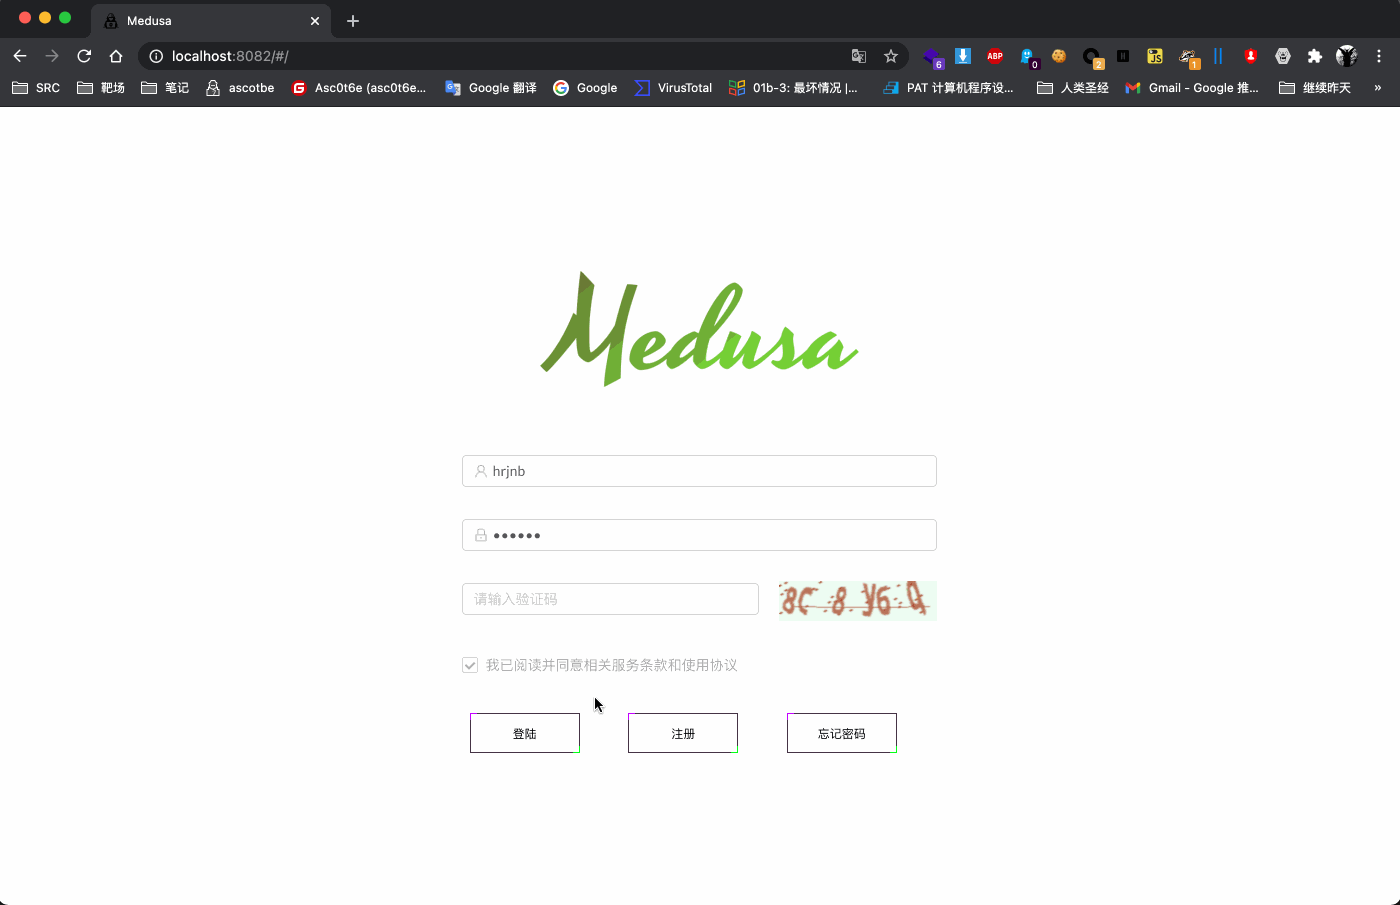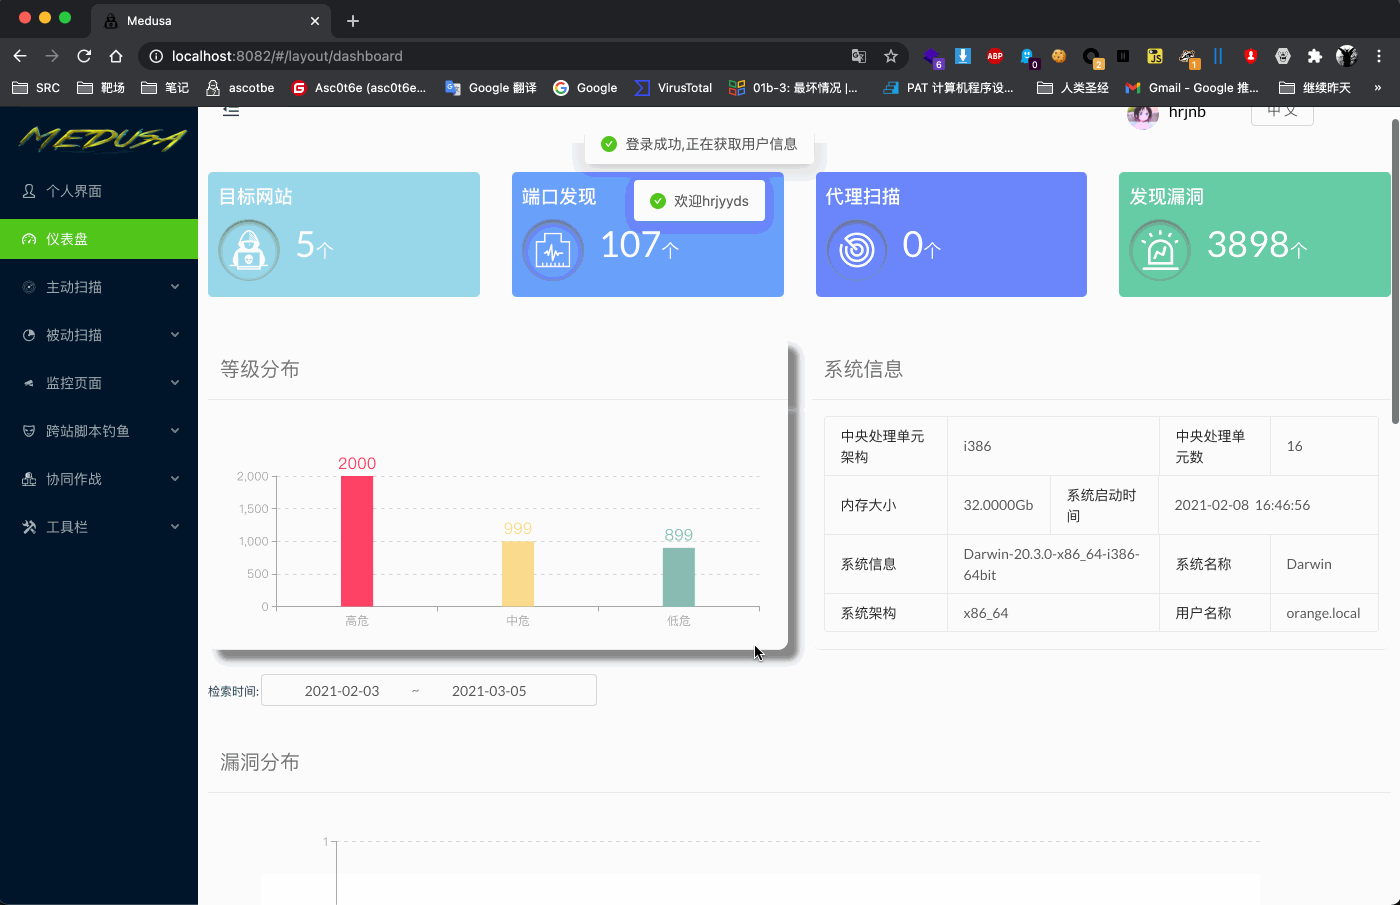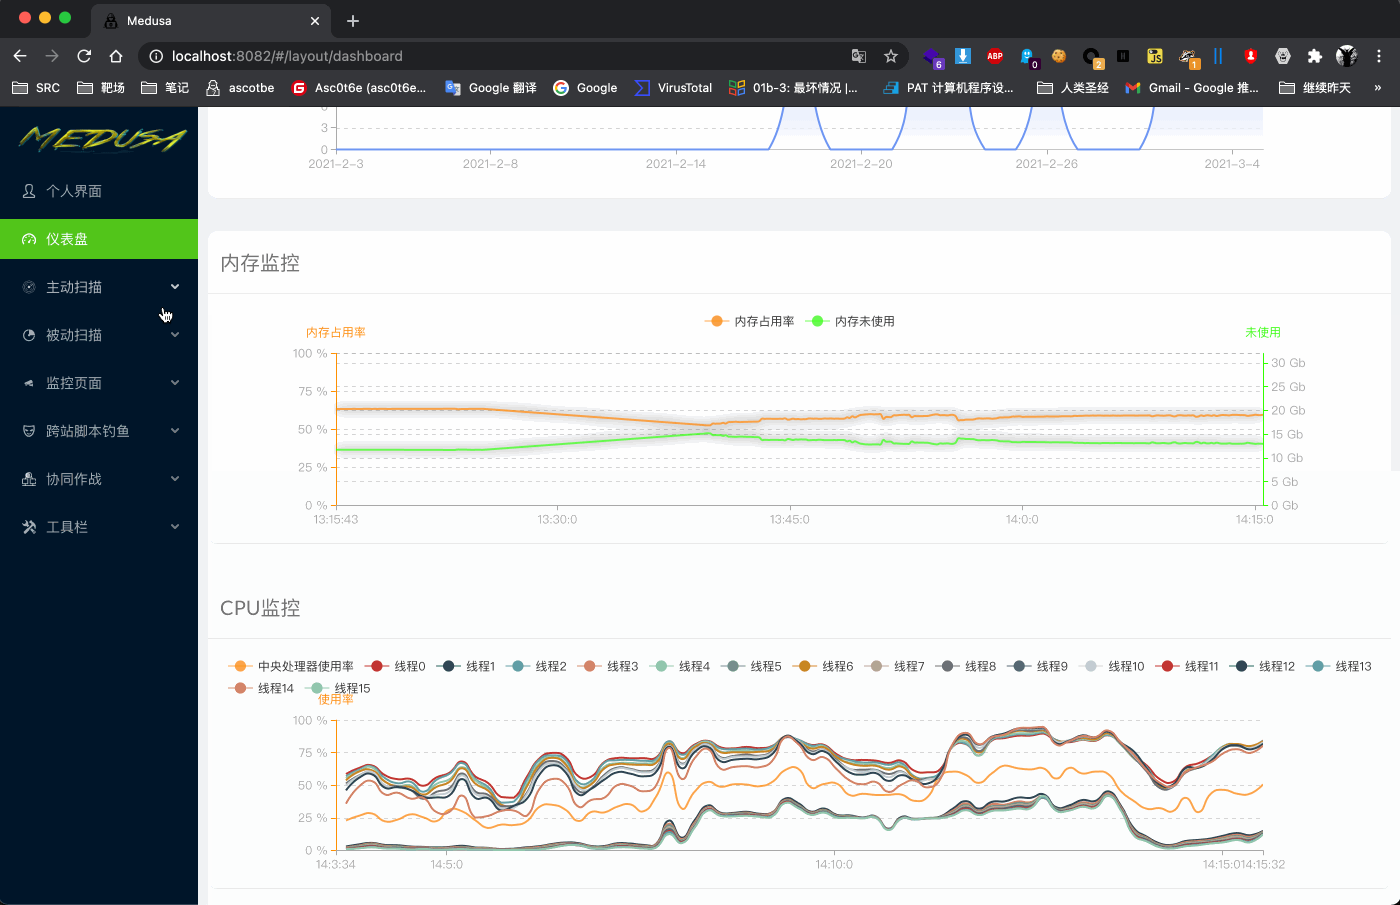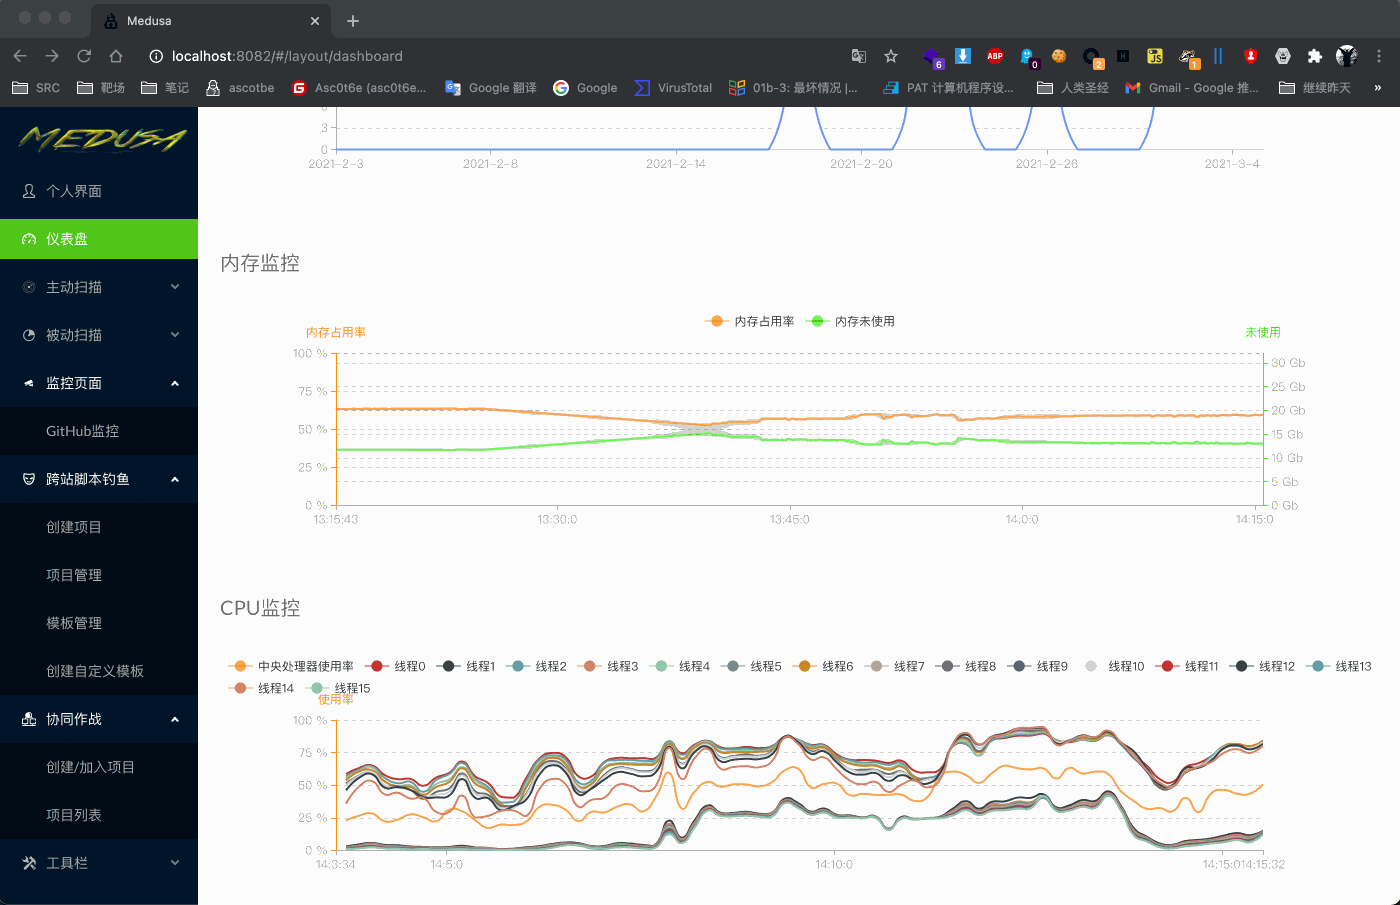
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中

Malicious HTTP traffic explorer

POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC

A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.

PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…

WordPress wp2shell pre-auth RCE exploit kit (CVE-2026-63030 + CVE-2026-60137)

WordPress Core Unauthenticated RCE (CVE-2026-63030, CVE-2026-60137)

Open-source pentesting management and automation platform by Salesforce Product Security